
ProcessInjection
 3xpl01tc0d3r/processinjection
This program is designed to demonstrate various process injection techniques
binary-exploitationeducationencryption-decryption-tools+5
1.3k
3xpl01tc0d3r/processinjectionThis program is designed to demonstrate various process injection techniques
 safebreach-labs/pinjectra
Pinjectra is a C/C++ OOP-like library that implements Process Injection techniques (with focus on Windows 10 64-bit)
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 secrary/injectproc
InjectProc - Process Injection Techniques [This project is not maintained anymore]
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
 chompie1337/windows_lpe_afd_cve-2023-21768
Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…
 kkent030315/evil-mhyprot-cli
A PoC for Mhyprot2.sys vulnerable driver that allowing read/write memory in kernel/user via unprivileged user process.
 orinimron123/cve-2026-40369-exploit
Full exploit code for CVE-2026-40369 - A Windows kernel arbitrary write vulnerability that allows browser sandbox escape from all browsers render…
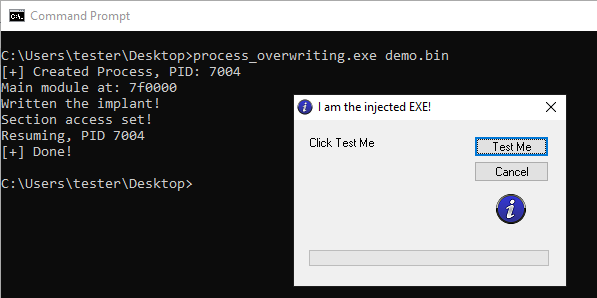 hasherezade/process_overwriting
PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.
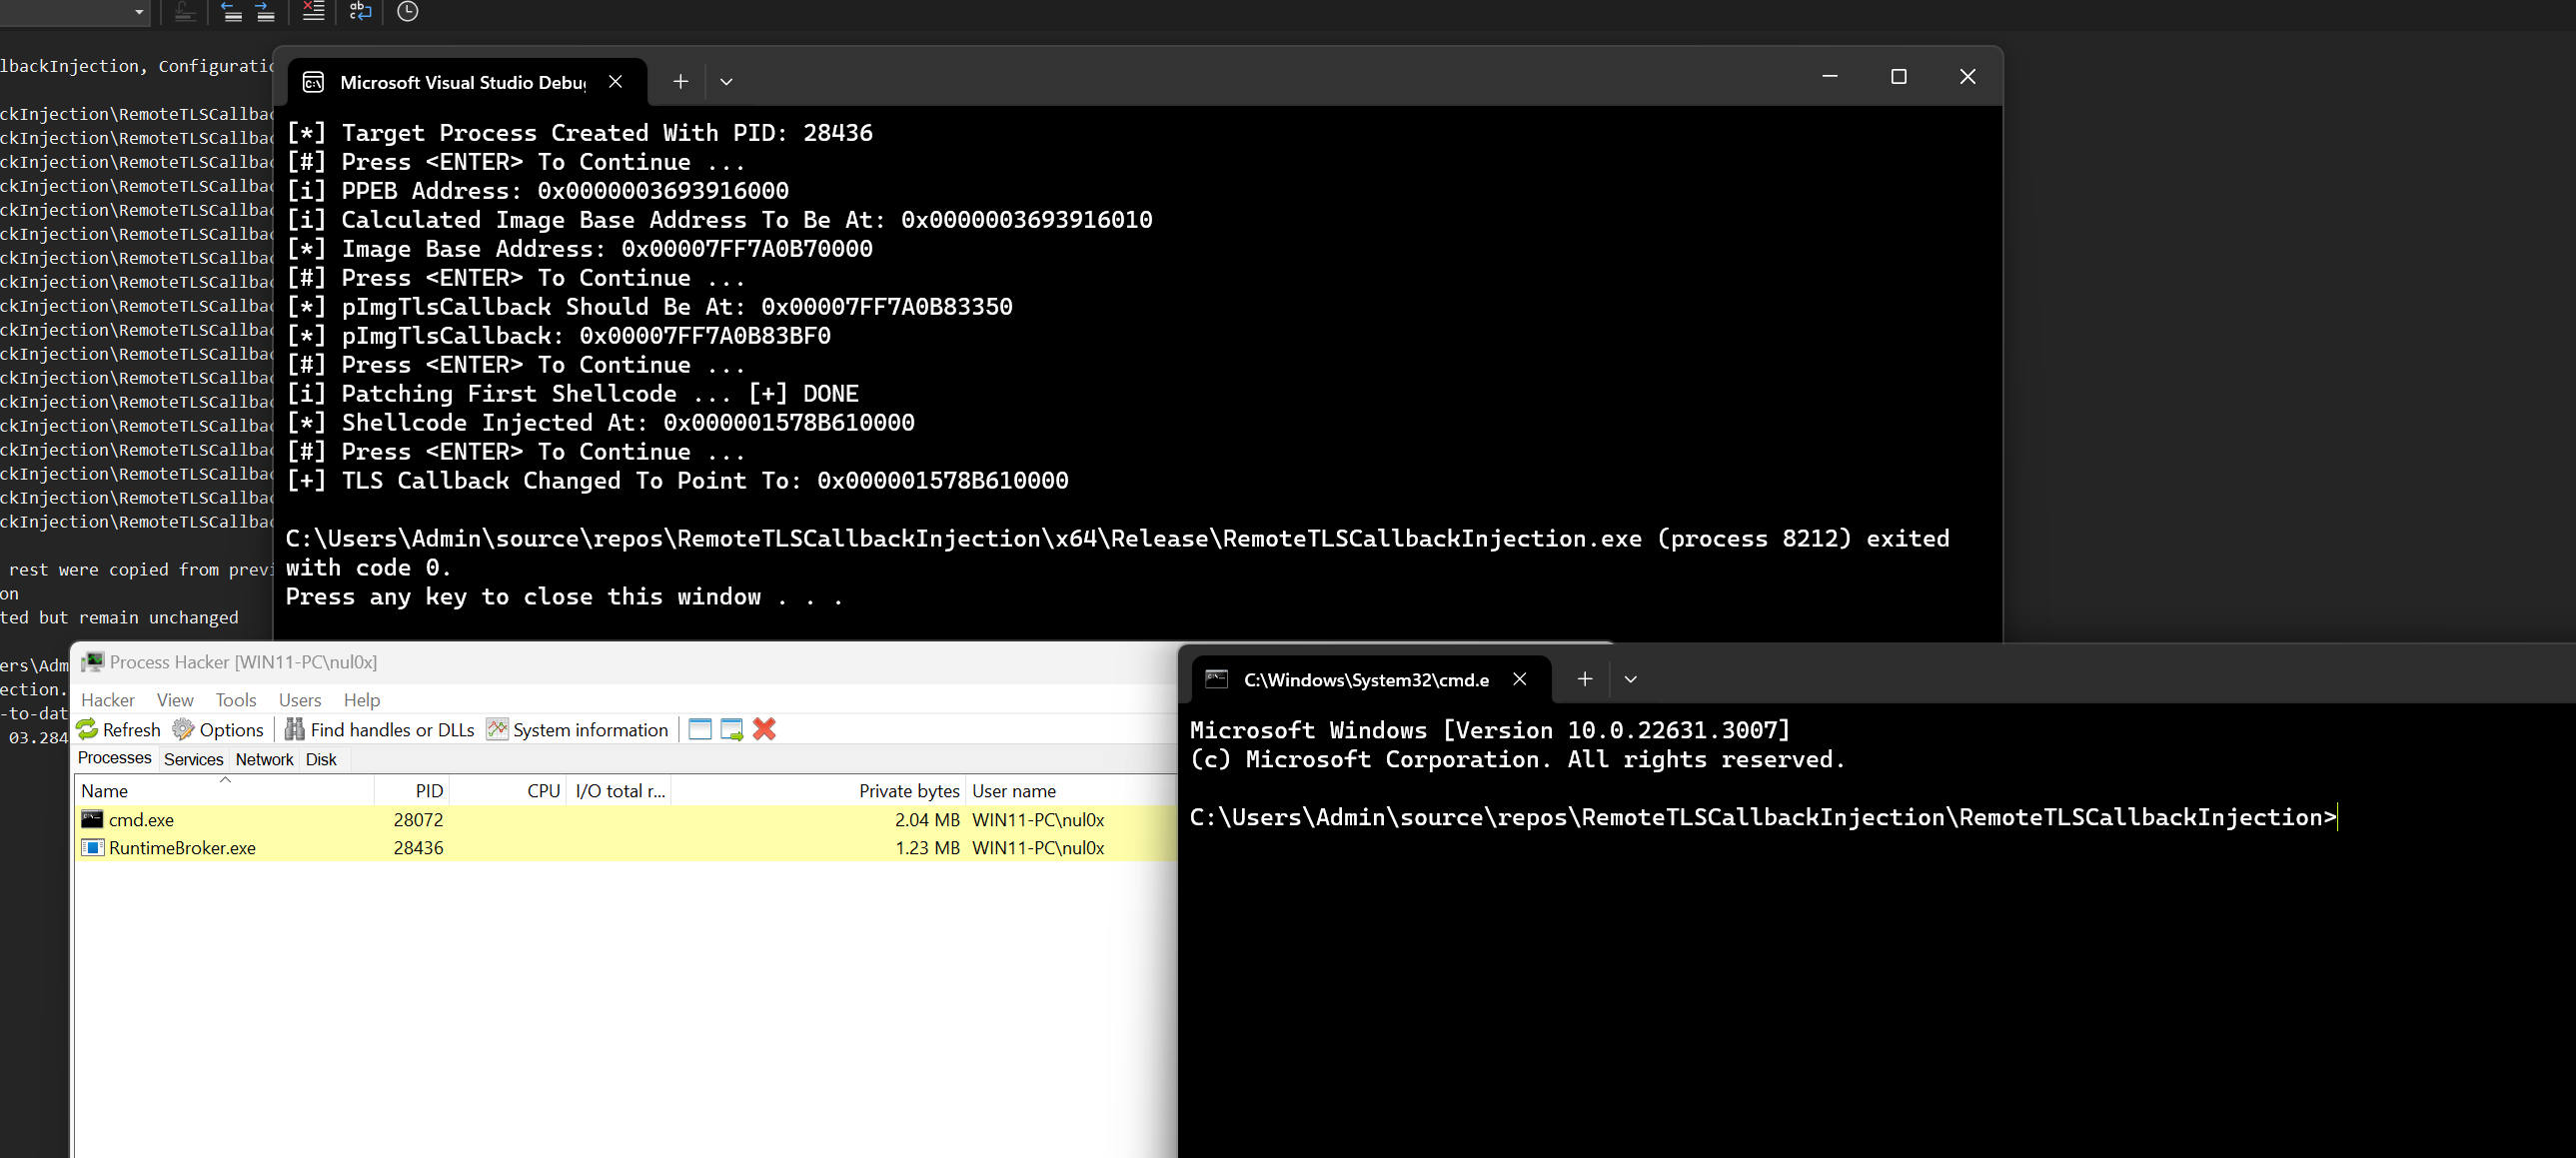 maldev-academy/remotetlscallbackinjection
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process
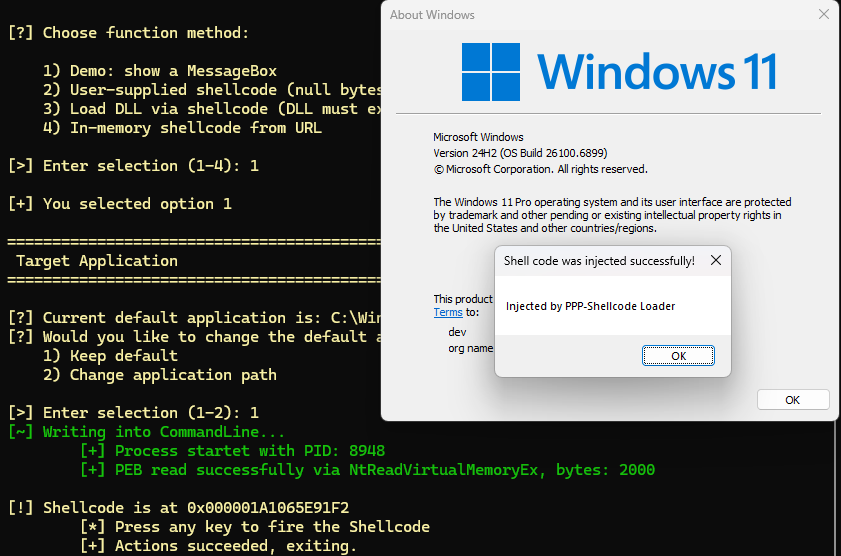 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
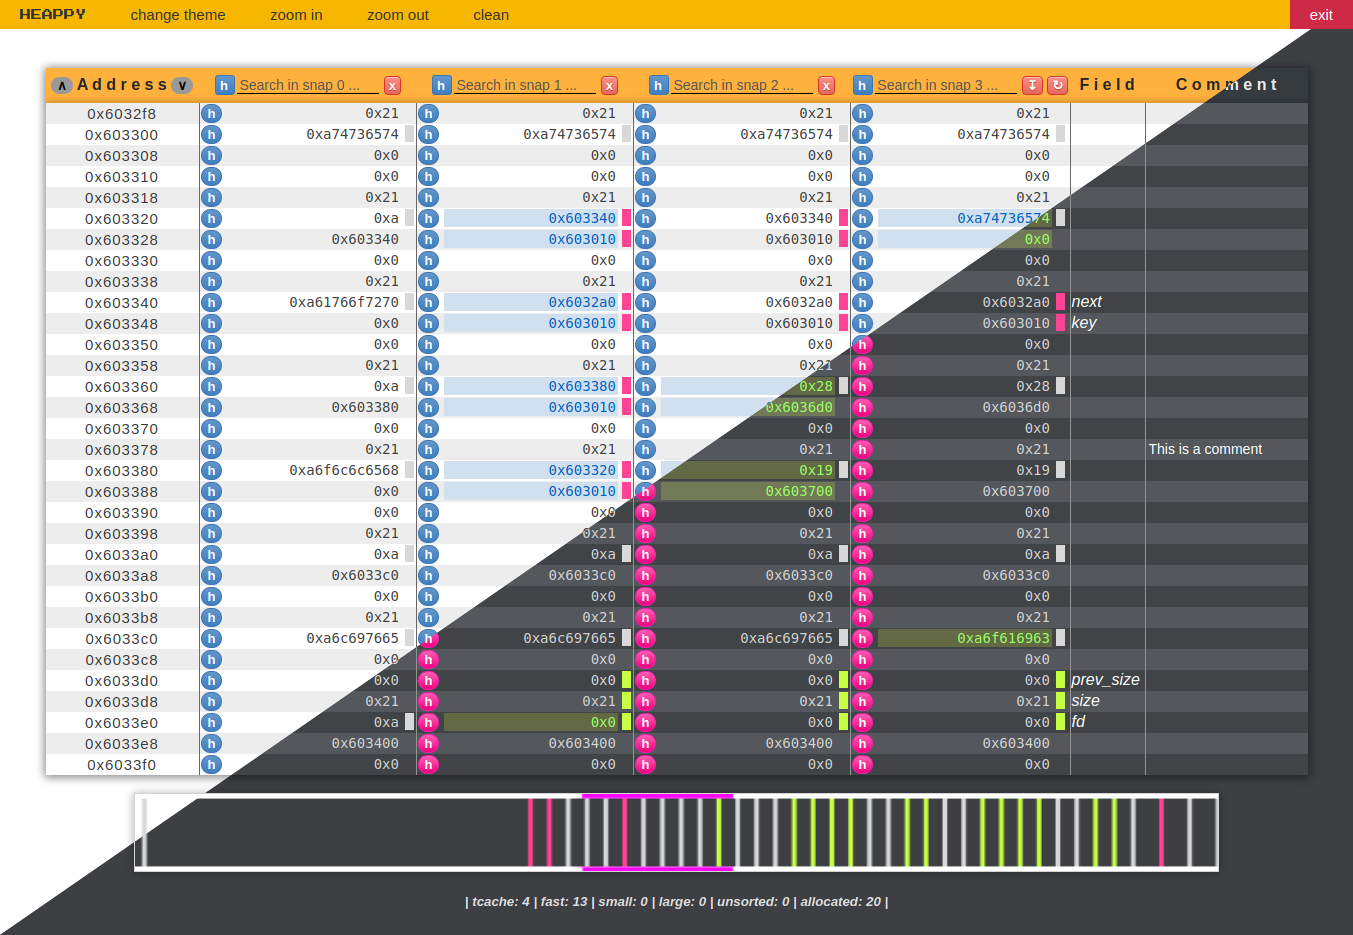 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face:
 po6ix/poc-for-cve-2023-41993
Proof-of-concept exploit for CVE-2023-41993, a WebKit JIT type confusion in Safari. Provides addrof/fakeobj primitives via heap manipulation and…
 chompie1337/windows_mskssrv_lpe_cve-2023-36802
Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…
 rootkitsmm-zz/win10pcap-exploit
Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )
 canyie/transitionplayer
CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…