
cve-2026-31431
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
binary-exploitationcloud-securitycontainer-security+7
2
nisec-eric/cve-2026-31431Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 zhanghangorg/cve-2026-31431
Detector and proof-of-concept for a Linux kernel page-cache write vulnerability (CVE-2026-31431) in algif_aead, including a non-destructive scanner…
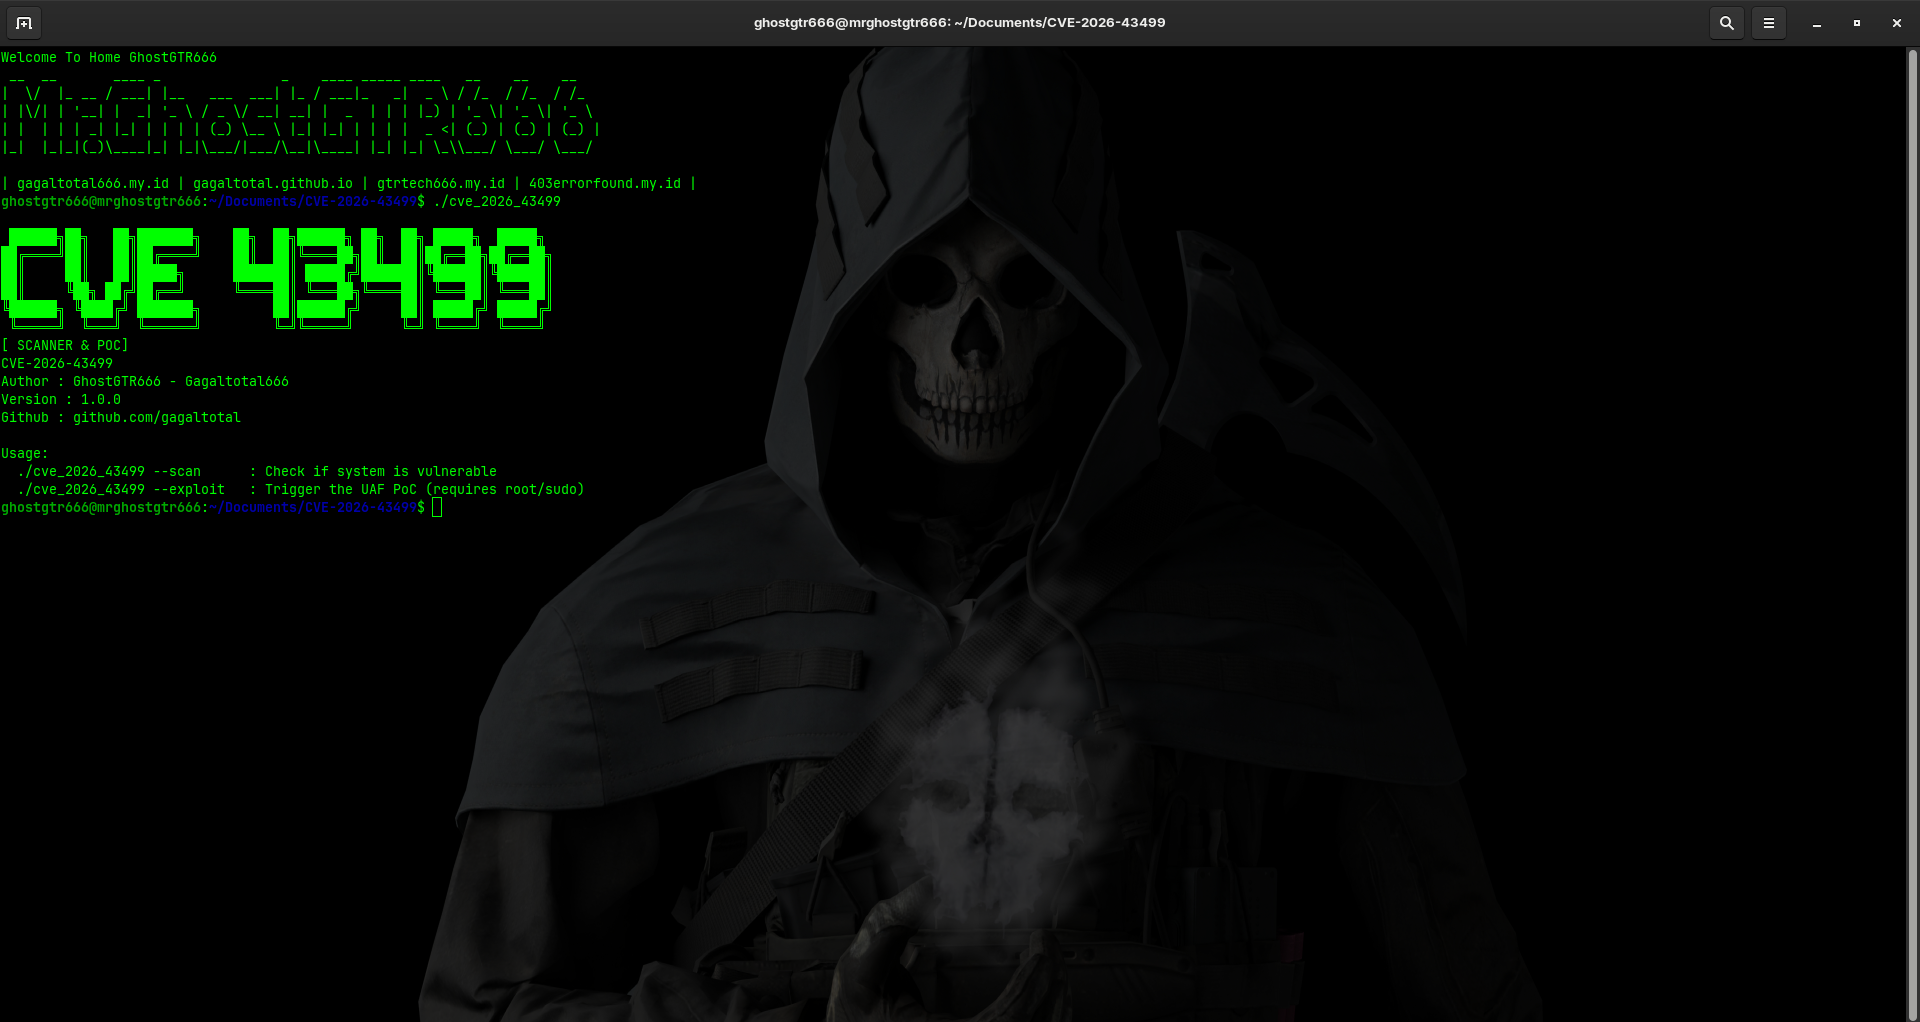 gagaltotal/cve-2026-43499-poc-scanner
CVE-2026-43499 PoC Scanner
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 rvzsec/cve-2024-2961
CVE-2024–2961 Security Issue Mitigation Script
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38427
CVE-2026-38427 — Integer Wraparound → Heap Buffer Overflow in Tasmota fetch_jpg() uint16_t (Tasmota <= 15.3.0.3)
 galois17/cve-2017-12149-playground
Containerized JBoss AS 6.1.0 research lab for demonstrating Java Deserialization (CVE-2017-12149) and JBoss Seam EL Injection vulnerabilities with…

 xkaneiki/rtty_cve-2025-56708-cve-2025-56709
CVE-2025-56708&CVE-2025-56709漏洞详解
 sneakynachos/cve-2026-2796-and-cve-2026-2768-escape-the-wasm-box
Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…
 sunqiz/cve-2010-3333-reproduction
CVE-2010-3333复现
 aaroncaiii/cve-2020-0796-poc
CVE-2020-0796-POC
 alexisahmed/cve-2022-0847-dirtypipe-exploits
A collection of exploits and documentation that can be used to exploit the Linux Dirty Pipe vulnerability.
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 elttam/publications
Offensive security research hub aggregating original vulnerability advisories, CVE proof-of-concept exploits, conference talks, and internal tooling…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…