
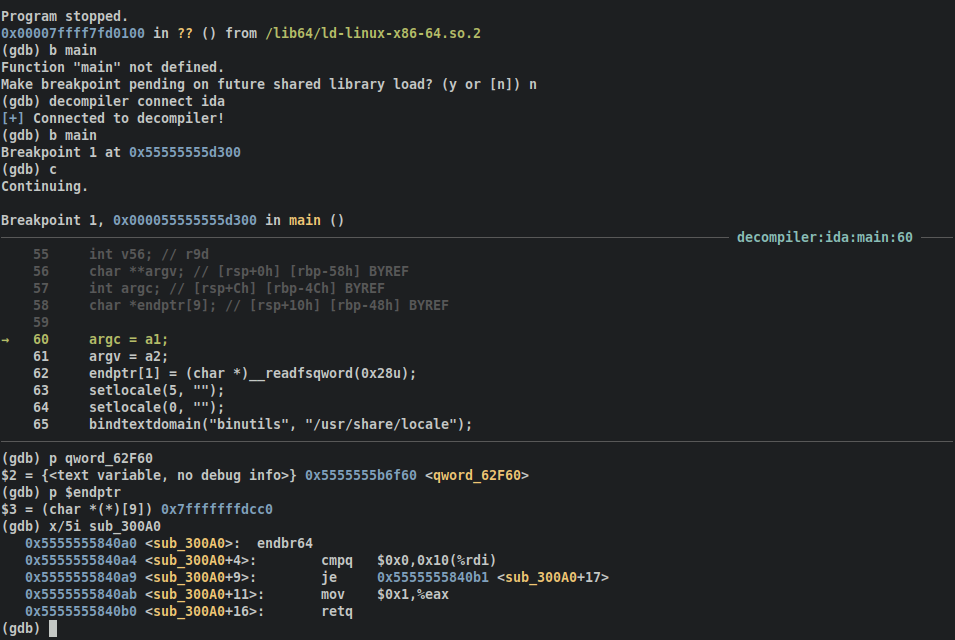
decomp2dbg
 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
binary-analysisbinary-exploitationdebuggers+3
mahaloz/decomp2dbgA plugin to introduce interactive symbols into your debugger from your decompiler
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 llvmparty/striga
Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…
 gamesarchive/cve-2025-48543
Proof-of-concept exploit for CVE-2025-48543, written in C++. Demonstrates exploitation of a specific vulnerability for security testing and research…
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 haile01/perl_spreadsheet_excel_rce_poc
POC for RCE vulnerability in ParseExcel library, and ParseXLSX too, as a depending library
 nccgroup/rustproofing-linux
Educational examples porting Linux kernel vulnerabilities to Rust, featuring intentionally vulnerable code and exploits for learning kernel security…
 h3st4k3r/cve-2025-30065
Java-based research harness for studying CVE-2025-30065, an RCE vulnerability in Apache Parquet via Avro schema deserialization, intended for…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 gmh5225/cve-2022-35737
Proof-of-concept exploit code and technical analysis for CVE-2022-35737, an integer overflow in SQLite3's sqlite3_str_vappendf function enabling…
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 kai6u/tribell_edge_sandbox_escape
Tribell Edge Sandbox Escape - PoCs of Edge's legacy vulnerabilities BadgeUpdateManager / TileFlyoutUpdateManager / ToastNotificationManager to…
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 piyush-bhor/cve-2024-11393
Technical Details and Exploit for CVE-2024-11393
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…