
cheat-engine-undetectable
 gmh5225/cheat-engine-undetectable
Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
binary-exploitationeducationexploitation+3
gmh5225/cheat-engine-undetectableAcademic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 madexploits/cve-2026-46300
CVE-2026-43284 - CVE-2026-43500 - CVE-2026-46300 Variant of dirtyfrag exploit
 fomovet/cve-2025-29384
POC for CVE-2025-29384
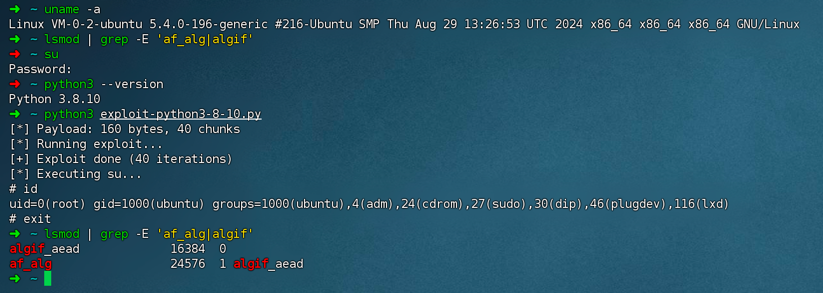 y5neko/copy-fail-cve-2026-31431-universal
Multi-language implementation and compatibility with older versions of Python.
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 joehquak/mi8e5-unlocker-by-cve-2026-43499
Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English
 rasetsuu/vmprotect-research
Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 droidvoider/dirtycow-replacer
CVE-2016-5195 dirtycow by timwr automated multi file patch tool
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)