

kurasagi
 neomaster831/kurasagi
Windows 11 24H2-25H2 Runtime PatchGuard Bypass
adversarial-attackbinary-exploitationeducation+4
neomaster831/kurasagiWindows 11 24H2-25H2 Runtime PatchGuard Bypass
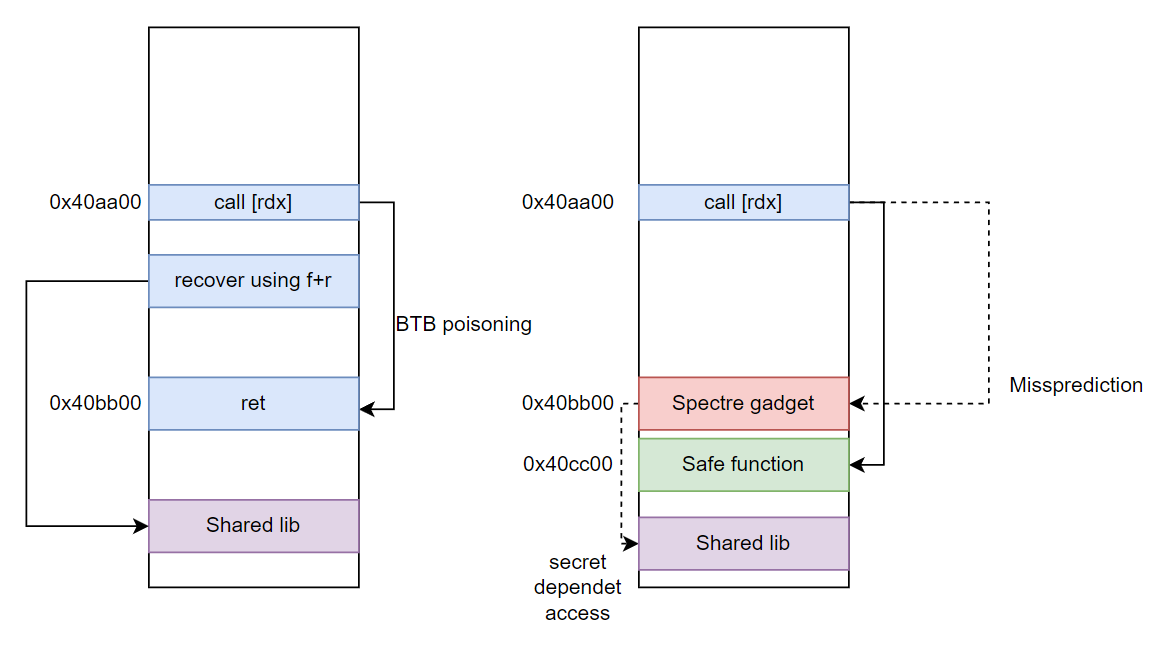 es0j/execaslr-ekoparty
Proof-of-concept exploit that bypasses ASLR on Intel CPUs by abusing branch target buffer and speculative execution to leak randomized addresses via…
 spiralbl0ck/rowhammer-exploit
RowHammer Based-Exploit
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
 aaryanbhujang/cve-2024-3660-poc
A PoC for CVE-2024-3660. Arbitrary Code Execution in Keras.
 inertfluid/sk-cve-2026-26030-lab
Ethical, network-isolated Docker lab reproducing CVE-2026-26030 — Semantic Kernel in-memory vector store filter eval() RCE (patched in 1.39.4)
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
 chamsbouzaiene/ai-vuln-rediscovery-nginx-cve-2026-42945
Reproducible AI-assisted vulnerability rediscovery of CVE-2026-42945 in nginx, including technical analysis, PoC trigger, and patch validation for…
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
 cyhe50/cve-2025-32434-poc
Proof-of-concept exploit for CVE-2025-32434, a pickle deserialization vulnerability in PyTorch's weights_only mode, demonstrating malicious tar file…
 1numak1/cve-2025-31337
CVE-2025-31337 Security Advisory - Critical Buffer Overflow in AI Chatbot Framework
 rooobeam/pickle-deserialization-exploit-in-transformers
This study analyzes Python pickle deserialization vulnerabilities, focusing on CVE-2024-3568 in Hugging Face Transformers' TFAutoModel. We reproduce…