

My-Presentation-Slides
 orangetw/my-presentation-slides
Collections of Orange Tsai's public presentation slides.
binary-exploitationctfcurated-resources+5
orangetw/my-presentation-slidesCollections of Orange Tsai's public presentation slides.
 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 sec-sys/cve-2026-42945-reverse-shell-poc
Python RCE PoC with reverse-shell listener for CVE-2026-42945 (NGINX Rift)
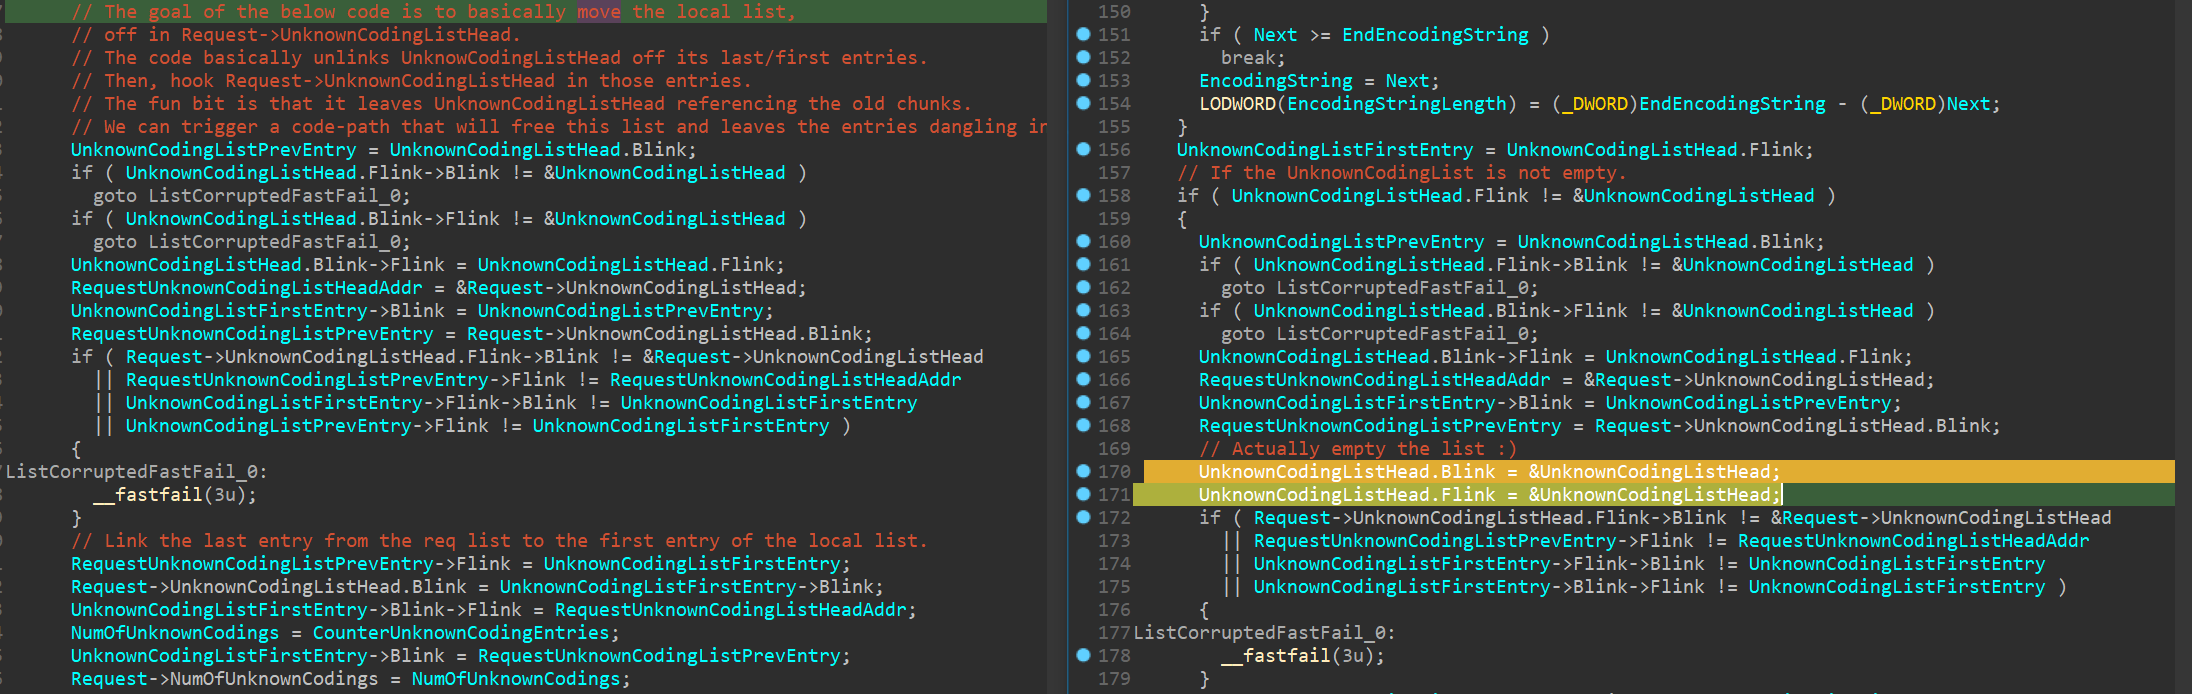 0vercl0k/cve-2021-31166
Proof of concept for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely.
 ianxtianxt/cve-2015-7501
Educational lab for understanding Java deserialization vulnerabilities with PoC exploits for JBoss CVEs, gadget chain analysis, and a vulnerable HTTP…
 fatmo666/cve-2023-38545-libcurl-socks5-heap-buffer-overflow
Proof-of-concept exploit for CVE-2023-38545, a heap buffer overflow in libcurl's SOCKS5 proxy handshake triggered via a malicious HTTP 301 redirect…
 secforce/cve-2021-37748
Exploit code for CVE-2021-37748 targeting Grandstream HT801 ATA, demonstrating remote code execution via crafted HTTP requests.
 sak110/cve-2025-69219
Proof-of-concept exploit for CVE-2025-69219, demonstrating remote code execution in Apache Airflow Providers HTTP via unsafe pickle deserialization.…
 12lie20/cve-2026-23918-test
This repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
 oscerd/cve-2026-40859
Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)
 aratane/cve-2026-42945
A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
 debajyoti0-0/cve-2026-27654-poc
Proof-of-Concept and technical analysis for CVE-2026-27654, a heap-based buffer overflow vulnerability in the NGINX HTTP WebDAV module, including…
 lipeozyy/cve-2017-14980_syncbreeze_10.0.28_bof
Proof-of-concept buffer overflow exploit for Sync Breeze Enterprise v10.0.28 (CVE-2017-14980). Sends crafted HTTP POST payload to overwrite EIP and…
 jeanback1/cve-2019-0211-exploit
Local privilege escalation exploit for CVE-2019-0211 targeting Apache HTTP Server 2.4.17-2.4.38 with mod_php. Uses UAF in PHP to corrupt Apache…
 themalwareguardian/cve-2020-13768
Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 d0rb/cve-2024-4323
Critical heap buffer overflow vulnerability in the handle_trace_request and parse_trace_request functions of the Fluent Bit HTTP server.