

NotEnough
 caoweiquan322/notenough
This tool calculates tricky canonical huffman histogram for CVE-2023-4863.
binary-exploitationexploitationfuzzing+3
252 years ago
caoweiquan322/notenoughThis tool calculates tricky canonical huffman histogram for CVE-2023-4863.
 benschlueter/cve-2021-33624
Proof of Concept for CVE-2021-33624
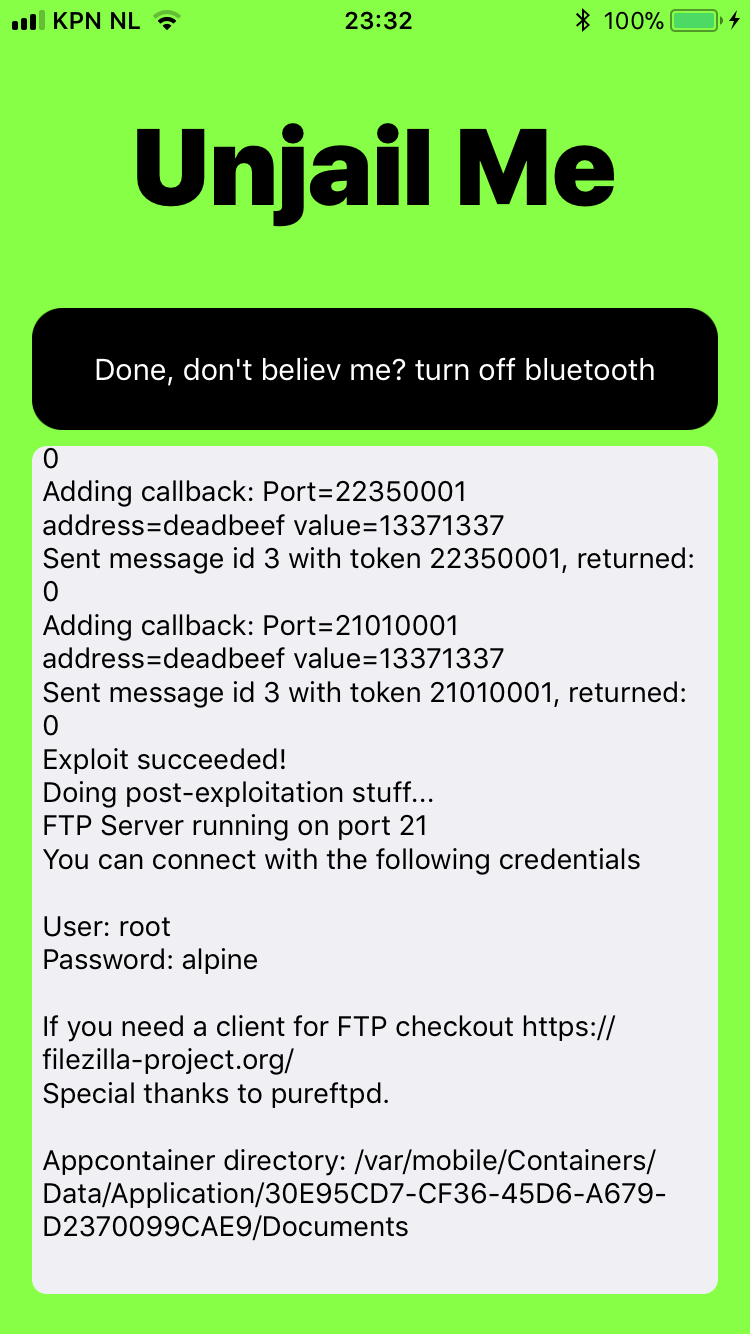 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 downwithup/cve-2018-16712
PoC Code for CVE-2018-16712 (exploit by MmMapIoSpace)
 downwithup/cve-2018-15499
PoC code for CVE-2018-15499 (exploit race condition for BSoD)
 downwithup/cve-2018-16711
PoC code for CVE-2018-16711 (exploit by wrmsr)
 downwithup/cve-2018-18714
PoC Code for CVE-2018-18714 (exploit by stack overflow)
 downwithup/cve-2018-18026
PoC Code for CVE-2018-18026 (exploit by stack overflow)
 sornphut/overlayfs---cve-2021-3493
Technical analysis of CVE-2021-3493, an Ubuntu OverlayFS local privilege escalation vulnerability, including root cause explanation and affected…
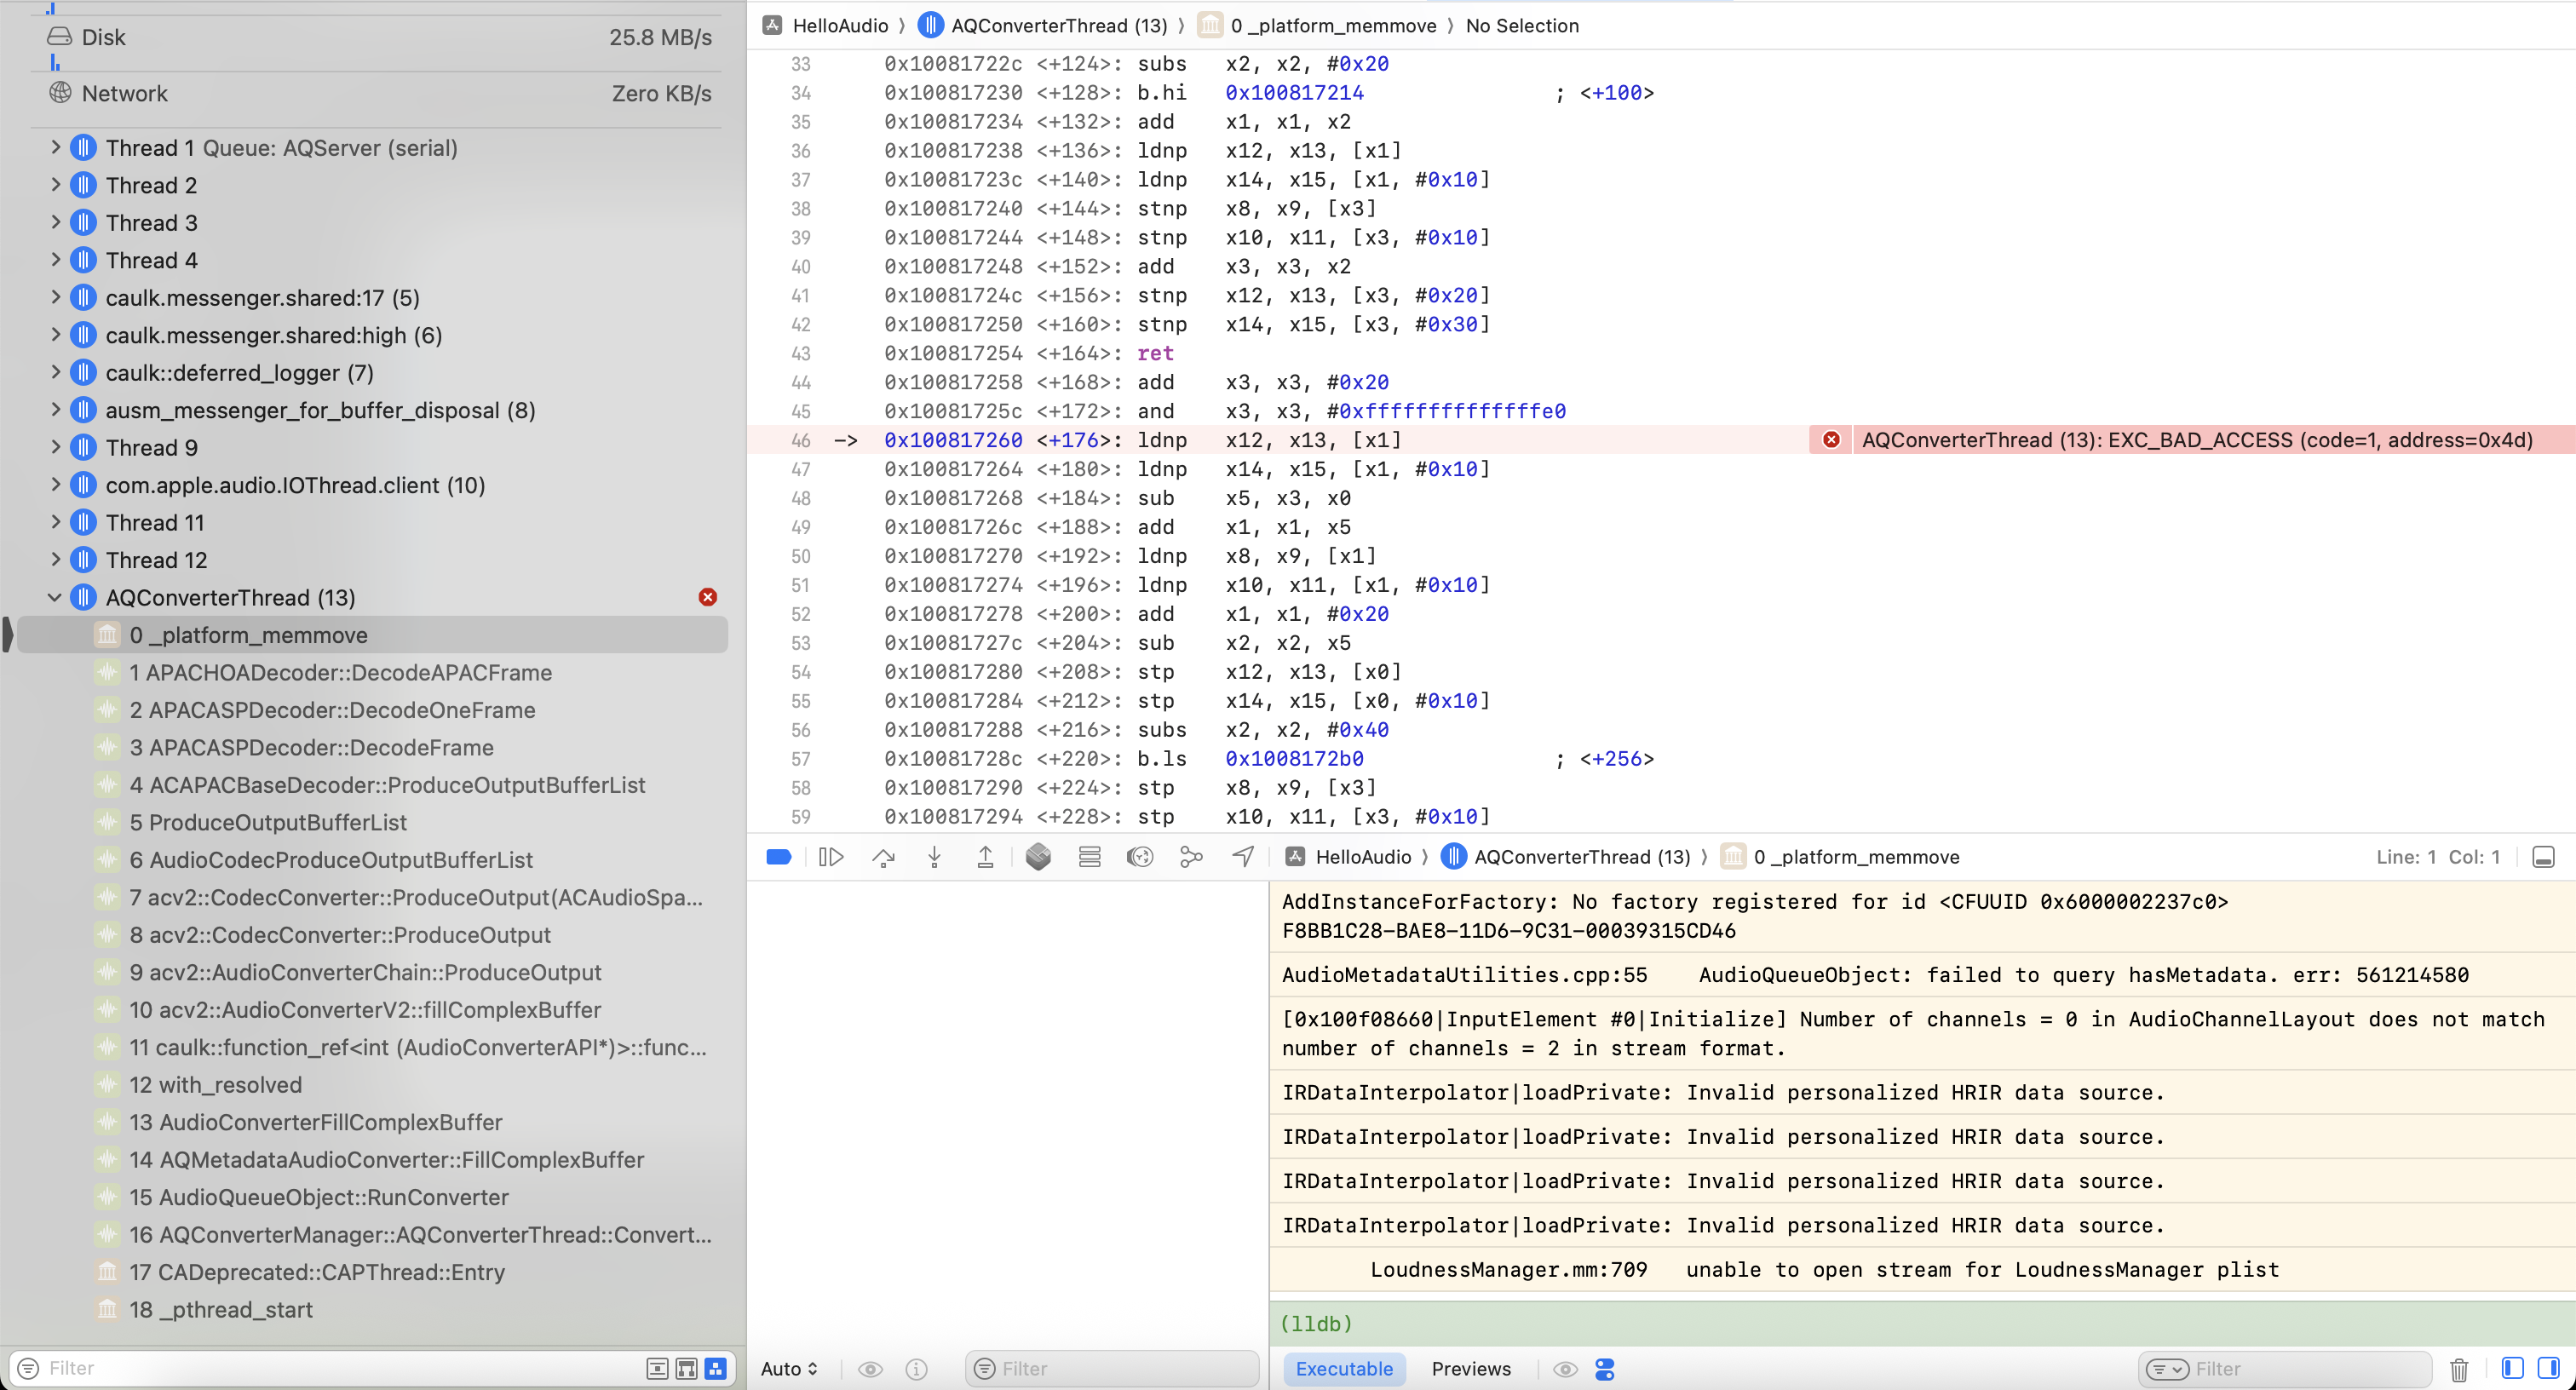 zhuowei/apple-positional-audio-codec-invalid-header
CVE-2025-31200 - @Noahhw46 figured it out
 homjxi0e/cve-2017-8641_chakra_js_globalobject
There is a classic heap overflow when eval a string which large enough in Chakra! This issue can be reproduced steadly in uptodate Edge in Win10 WIP.…
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 xyjl-ly/cve-2021-22555-exploit
CVE-2021-22555 Exploit
 dukptkey/cve-2020-9273
Analysis and exploitation of an use-after-free in ProFTPd
 0xcyberstan/cve-2026-53360-poc
PoC for CVE-2026-53360: guest-triggered heap out-of-bounds read/write in KVM SEV-SNP Page State Change (PSC) handling.
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 pwndorei/cve-2024-22532
Proof-of-concept exploit for CVE-2024-22532: heap-based buffer overflow in XnView Classic 2.51.5 and NConvert 7.163 via crafted .xwd file, enabling…
 0linear/cve-2026-62958
Proof-of-concept for CVE-2026-62958: crafts a malformed ELF to trigger an out-of-bounds read in Libriscv and crash the sandbox with SIGSEGV.