
cve-2013-2094
 realtalk/cve-2013-2094
original cve-2013-2094 exploit and a rewritten version for educational purposes
binary-exploitationeducationexploitation+2
91
realtalk/cve-2013-2094original cve-2013-2094 exploit and a rewritten version for educational purposes
 k3vinlusec/r7000_httpd_bof_cve-2020-15416
Walkthrough of CVE-2020-15416 buffer overflow exploit for Netgear R7000 router, including QEMU user-mode debugging environment setup and detailed…
 albocoder/cve-2022-27666-exploits
There are 2 exploitation methods that exploit CVE-2022-27666. For more info on how to use these code bases please check my blog.
 mistymntncop/cve-2024-5274
Exploit for CVE-2024-5274, a Chrome V8 DCHECK bytecode mismatch vulnerability that provides out-of-bounds read/write primitives for browser…
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…
 askyeye/cve-2022-21894-payload
Example payload for CVE-2022-21894
 infiniteloopers/cve-2019-11932
Technical write-up and exploit code for CVE-2019-11932, a double-free vulnerability in WhatsApp for Android that leads to remote code execution via a…
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
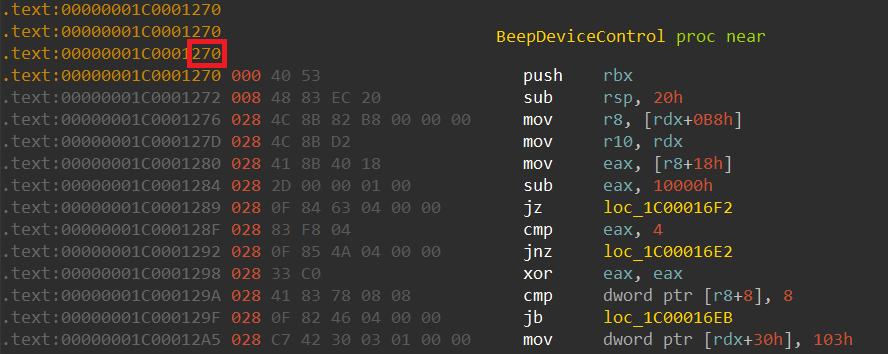 stong/cve-2020-15368
CVE-2020-15368, aka "How to exploit a vulnerable driver"
 wpengfei/cve-2016-6516-exploit
An demonstration of how to exploit double-fetch vulnerability CVE-2016-6516
 spiralbl0ck/linux-kernel-infoleak-6.12.-leveraged-to-do-cross-container-info-leak.-
POC shows how to leak postgresql stuff cause hugefile sub-system. Based on https://x.com/spendergrsec/status/1993794163880718700?s=20
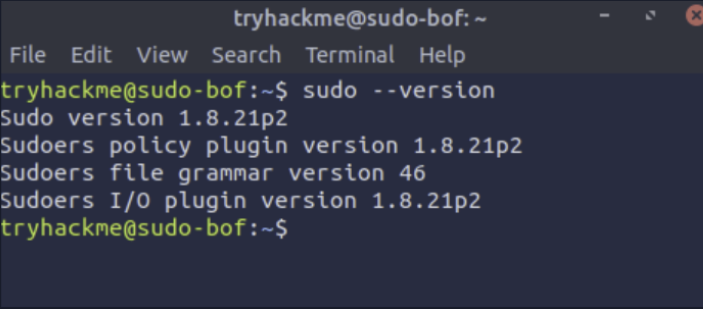 devteam6rabbit/cve-2019-18634-writeup
analysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits
 joeymeech/cve-2022-0847-exploit-implementation
Using CVE-2022-0847, "Dirty Pipe Exploit", to pop a reverse bash shell for arbitrary code execution on a foreign machine.
 0xirongoat/dirty-pipe
Implementation of Max Kellermann's exploit for CVE-2022-0847
 aesophor/cve-2019-18634
My n-day exploit for CVE-2019-18634 (local privilege escalation)
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
 fuzzrf/openbsd_ov1
OpenBSD remote overflow