
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
57 results
QuestStack preview

QuestStack

GitHubstarseed12345/queststack

Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
android-securitybinary-exploitationembedded-systems-security+5
205
28 days ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
binary-exploitationexploitationmalware-analysis+6
1269 months ago
K50G-POCOF4GT-CVE-2026-43499-PoC preview

K50G-POCOF4GT-CVE-2026-43499-PoC

GitHubcxyofficial/k50g-pocof4gt-cve-2026-43499-poc

Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
android-securitybinary-exploitationexploitation+5
23 days ago
CTF-CVE-2022-0847 preview

CTF-CVE-2022-0847

GitHubjustinye377/ctf-cve-2022-0847

CTF challenge deploying CVE-2022-0847 (Dirty Pipe) exploit to overwrite read-only files. Includes setup scripts, hints, and verification for kernel…
binary-exploitationctfeducation+3
1 year ago
DbgNexum preview

DbgNexum

GitHubdis0rder0x00/dbgnexum

Shellcode injection using the Windows Debugging API
binary-exploitationexploitationpayload-development+6
1818 months ago
CVE-2026-66804-CrossDevice-LPE preview

CVE-2026-66804-CrossDevice-LPE

GitHubdavidcarliez/cve-2026-66804-crossdevice-lpe

Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…

binary-exploitationexploitationprivilege-escalation+1
141 month ago
Windows-X64-RAT preview

Windows-X64-RAT

GitHubmaorbuskila/windows-x64-rat

Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…
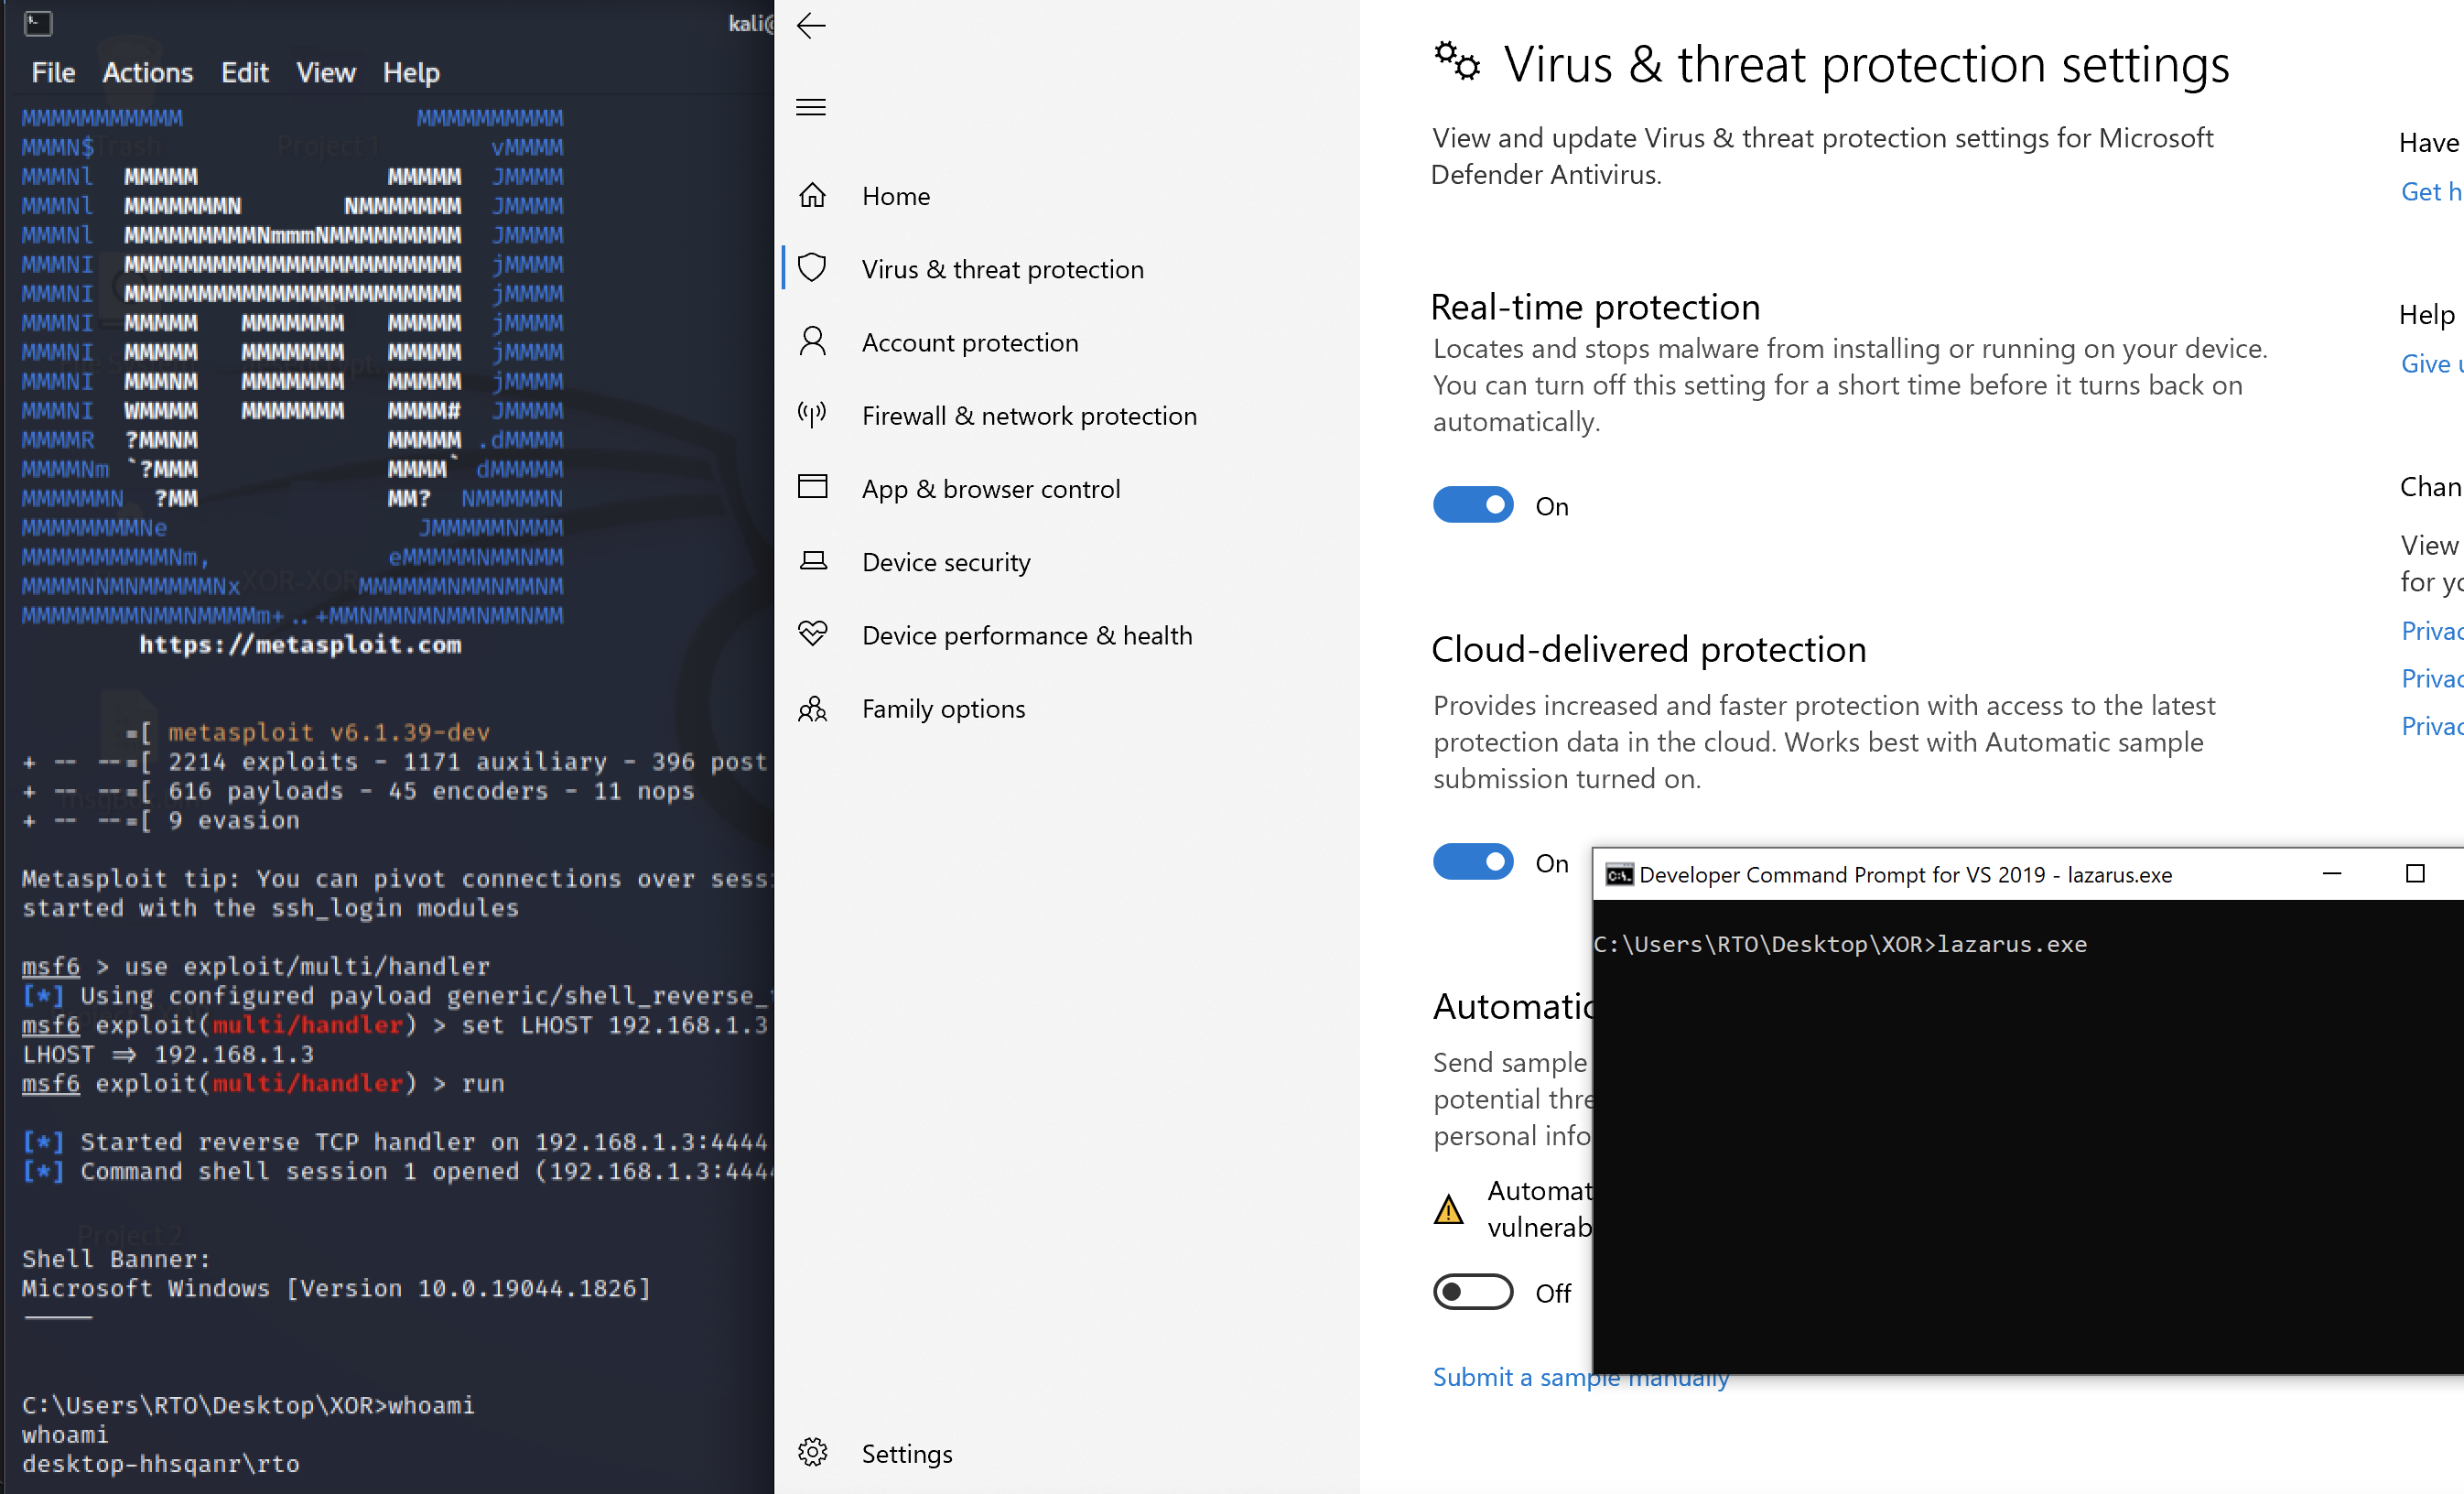
binary-exploitationcommand-and-controleducation+5
22 years ago
FUD-UUID-Shellcode preview

FUD-UUID-Shellcode

GitHubbl4ckm1rror/fud-uuid-shellcode

C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
binary-exploitationdefensive-toolsexploitation+6
3343 years ago
CVE-2023-28252 preview

CVE-2023-28252

GitHubfortra/cve-2023-28252

Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…

binary-exploitationdebuggersexploitation+4
1843 years ago
CVE-2021-21551 preview

CVE-2021-21551

GitHubluke0x90/cve-2021-21551

Proof-of-concept exploit for CVE-2021-21551: Windows local privilege escalation via Dell dbutil_2_3.sys driver. Implements read/write primitives,…
binary-exploitationexploitationprivilege-escalation+1
1 year ago
CLFS preview

CLFS

GitHubbyt3n33dl3/clfs

it's a CVE-2023-28252 (Patched), but feel free to use it for check any outdated software or reseach

binary-exploitationeducationexploitation+2
62 years ago
prefetch-tool preview

prefetch-tool

GitHubexploits-forsale/prefetch-tool

Windows KASLR bypass using prefetch side-channel
binary-exploitationexploitationinformation-gathering+4
2132 years ago
Windows_MSKSSRV_LPE_CVE-2023-36802 preview

Windows_MSKSSRV_LPE_CVE-2023-36802

GitHubchompie1337/windows_mskssrv_lpe_cve-2023-36802

Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…

binary-exploitationexploitationexploit-frameworks+3
1642 years ago
CVE-2019-0708-Exploit preview

CVE-2019-0708-Exploit

GitHubrockmelodies/cve-2019-0708-exploit

Using CVE-2019-0708 to Locally Promote Privileges in Windows 10 System

binary-exploitationexploitationprivilege-escalation+1
317 years ago
CVE-2026-20841-PoC preview

CVE-2026-20841-PoC

GitHub404godd/cve-2026-20841-poc

🛠 Demonstrate remote code execution in Windows Notepad versions below 11.2510 using the CVE-2026-20841 proof of concept.

binary-exploitationeducationexploitation+2
6 days ago
CVE-2020-17057 preview

CVE-2020-17057

GitHublsw29475/cve-2020-17057

Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.
binary-exploitationexploitationmemory-forensics+1
25 years ago
IoRingReadWritePrimitive preview

IoRingReadWritePrimitive

GitHubyardenshafir/ioringreadwriteprimitive

Post exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
binary-exploitationexploitationpenetration-testing+3
2584 years ago
LdrShuffle preview

LdrShuffle

GitHubrwxstoned/ldrshuffle

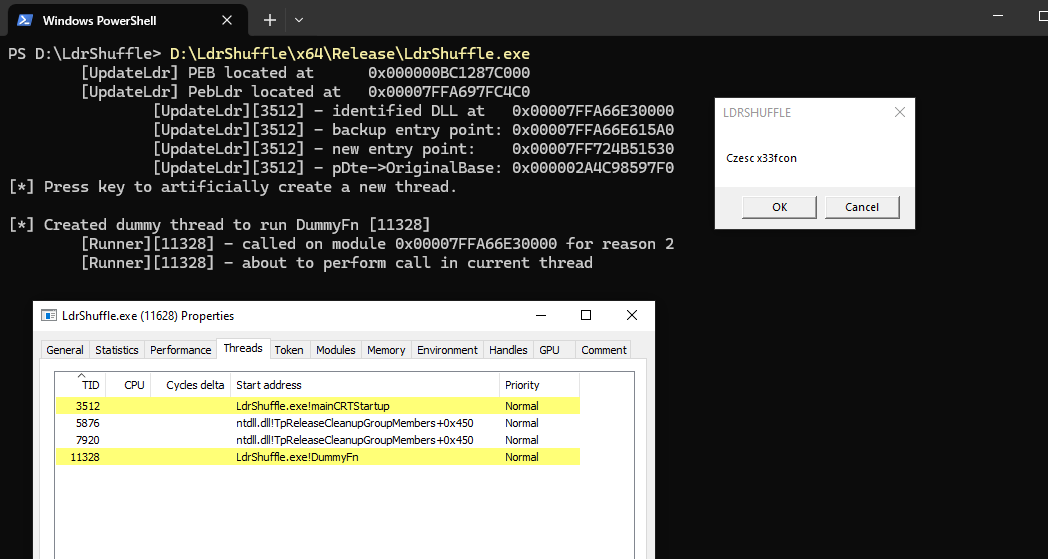
Code execution/injection technique using DLL PEB module structure manipulation

binary-exploitationcode-analysisexploitation+6
2871 year ago
Previous1234Next