
CVE-2026-23918-test
 12lie20/cve-2026-23918-test
This repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
binary-exploitationexploitationfuzzing+3
4
12lie20/cve-2026-23918-testThis repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
 oscerd/cve-2026-40473
Reproducer for CVE-2026-40473: Apache Camel camel-mina MinaConverter.toObjectInput unsafe deserialization (RCE over TCP/UDP)
 oscerd/cve-2026-40048
Reproducer for CVE-2026-40048: Apache Camel camel-pqc FileBasedKeyLifecycleManager unsafe deserialization (RCE)
 oscerd/cve-2026-43865
Reproducer for CVE-2026-43865 — Apache Camel camel-hazelcast default-configured instance unsafe Java deserialization (RCE)
 oscerd/cve-2026-43867
Reproducer for CVE-2026-43867 — Apache Camel camel-pqc AwsSecretsManagerKeyLifecycleManager unsafe key-metadata deserialization (RCE)
 oscerd/cve-2026-40858
Reproducer for CVE-2026-40858 — Apache Camel camel-infinispan remote aggregation repository unsafe deserialization (RCE)
 oscerd/cve-2026-27172
Reproducer for CVE-2026-27172: Apache Camel camel-consul ConsulRegistry Java deserialization (RCE)
 oscerd/cve-2026-40859
Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)
 iss4cf0ng/cve-2026-31431-linux-copy-fail
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.
 gagaltotal/cve-2026-43499-poc-scanner
CVE-2026-43499 PoC Scanner
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 sammwyy/copyfail-rs
Copy Fail exploit (CVE-2026-31431) but in Rust.
 alihzsec/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux local privilege escalation vulnerability, demonstrating kernel exploitation for educational and…
 wzhdgithub/ghostlock
CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…
 k4ntux/cowslip
xfs kernel LPE (CVE-2026-64600), disclosed by Qualys on 22 July 2026
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
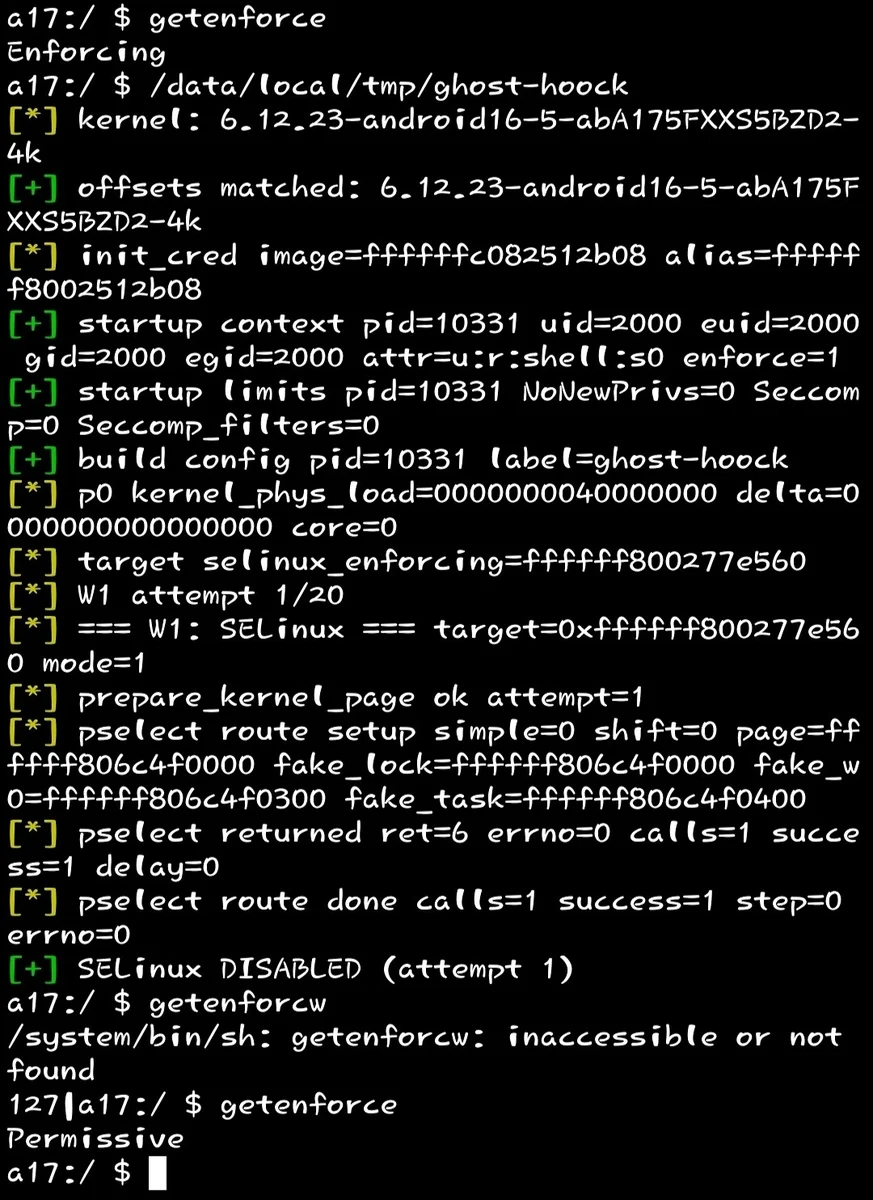 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 razureink/cve-2026-21509-office_security_bypass_reproduction
CVE Reproduction: cve-2026-21509-office_security_bypass_reproduction