
GLUFS
 diego-altf4/glufs
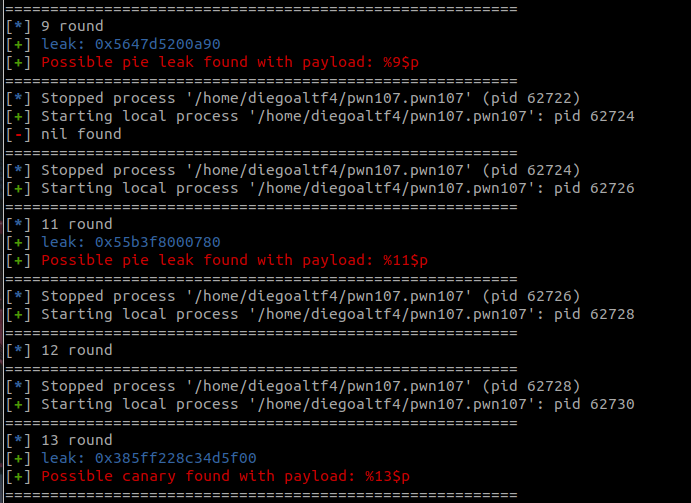
Automated format string vulnerability exploitation tool for discovering stack, PIE, and canary leaks with flag search capability via %s or %p…
binary-exploitationexploitationfuzzing+1
27
diego-altf4/glufsAutomated format string vulnerability exploitation tool for discovering stack, PIE, and canary leaks with flag search capability via %s or %p…
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 shams-ul-mehmood/cve-2021-3156-project
Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…
 dointisme/cve-2020-8597
Demonstration of CVE-2020-8597: a buffer overflow in pppd's EAP handler, with exploit analysis, stack canary bypass discussion, and memory map…
 x-stp/cves-2025-11187_15467_69418
OpenSSL pocs: PKCS#12 stack overflow, CMS IV overflow, OCB infoleak [partial chain]