
CVE-2022-22077
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
binary-exploitationcommand-and-controleducation+5
7
grisuno/cve-2022-22077BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 safebreach-labs/pinjectra
Pinjectra is a C/C++ OOP-like library that implements Process Injection techniques (with focus on Windows 10 64-bit)
 monoxgas/koppeling
Adaptive DLL hijacking / dynamic export forwarding
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
 star-sg/cve
A collection of proof-of-concept exploit scripts written by the STAR Labs team for various CVEs that they discovered or found by others.
 zgzhang/cve-2024-6387-poc
a signal handler race condition in OpenSSH's server (sshd)
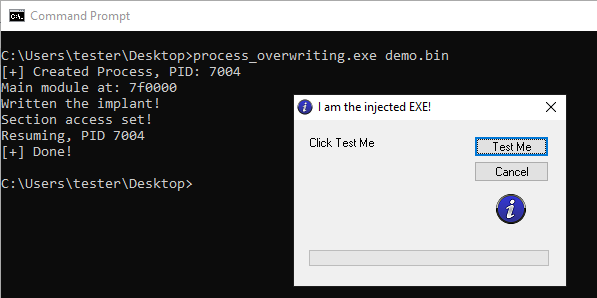 hasherezade/process_overwriting
PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.
 maherazzouzi/cve-2022-37706-lpe-exploit
A reliable exploit + write-up to elevate privileges to root. (Tested on Ubuntu 22.04)
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
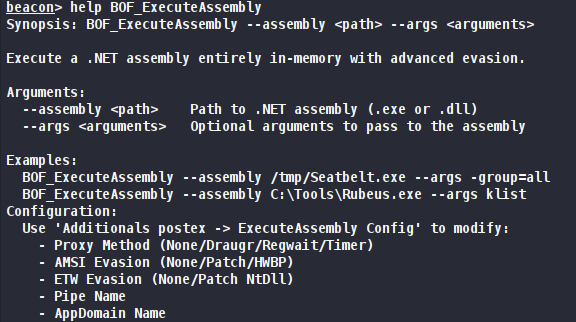 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132