
CVE-2017-0038-EXP-C-JS
 k0keoyo/cve-2017-0038-exp-c-js
C and JavaScript exploit for CVE-2017-0038, demonstrating memory corruption exploitation with debug-based memory leak observation.
binary-exploitationdebuggersexploitation+2
6
k0keoyo/cve-2017-0038-exp-c-jsC and JavaScript exploit for CVE-2017-0038, demonstrating memory corruption exploitation with debug-based memory leak observation.
 crihexe/v8-poc-cve-2026-5865
Minimal JavaScript proof-of-concept for V8 engine vulnerability CVE-2026-5865, with scripts to patch and calibrate the exploit for d8.
 pwntoday/cve-2025-6554
Proof-of-concept exploit for a V8 JavaScript engine vulnerability (CVE-2025-6554) demonstrating a TDZ bypass that leaks 'The Hole' sentinel, enabling…
 shaikusaf/external_v8_aosp10_r33_cve-2020-0240
Research repository for CVE-2020-0240 in V8 JavaScript engine, providing source code and analysis for vulnerability understanding and exploitation.
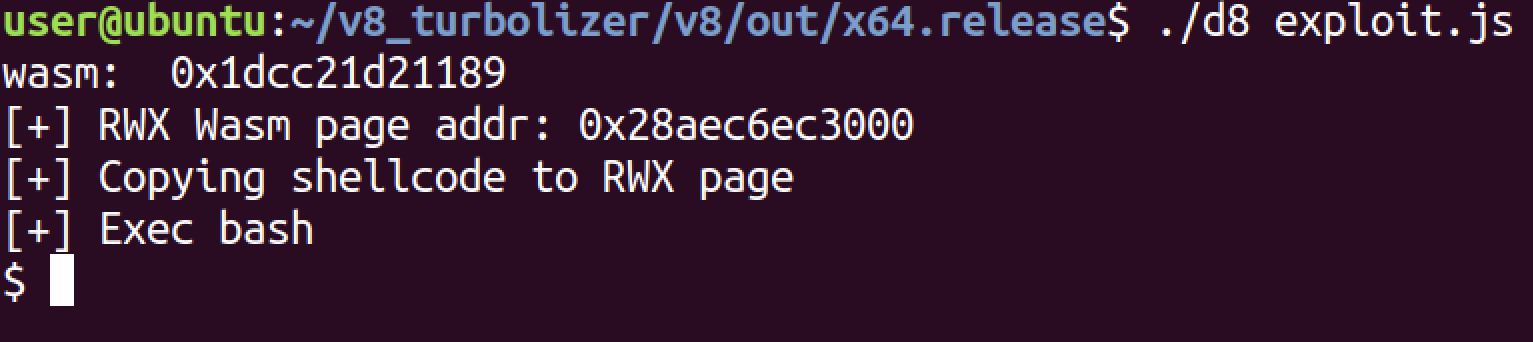 habooblab/cve-2019-13764
Full exploit for CVE-2019-13764 targeting V8 JavaScript engine on Linux, with root cause analysis and proof-of-concept code from Haboob Research Team.
 ghostn4444/poc-cve-2025-6554
Proof-of-concept exploit for CVE-2025-6554, a V8 JavaScript engine vulnerability allowing unauthorized access to uninitialized 'Hole' values via…
 peterpan0927/tfc-chrome-v8-bug-cve-2021-38001-poc
Proof-of-concept exploit for CVE-2021-38001, a Chrome V8 JavaScript engine vulnerability. Demonstrates exploitation via d8 shell with a malicious…
 maldiohead/tfc-chrome-v8-bug-cve-2021-38001-poc
Proof-of-concept exploit for CVE-2021-38001, a Chrome V8 JavaScript engine vulnerability, demonstrating remote code execution via crafted .mjs files.
 ppwwiinn/cve-2026-2763-poc
Proof-of-concept exploit for CVE-2026-2763, a use-after-free in Mozilla's JavaScript engine, demonstrating a constrained 1-bit write primitive…
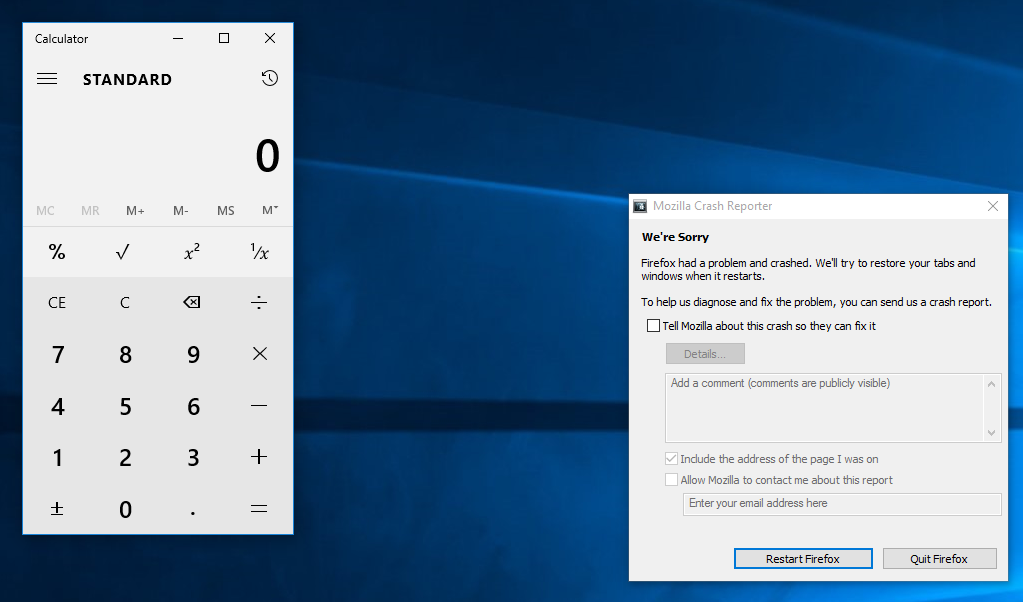 soham23/firefox-rce-nssmil
Educational standalone JavaScript implementation of the public exploit for CVE-2016-9079 (Firefox Use-After-Free), adapted from the original…
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.
 dexsemon/cve-2026-27495
Proof-of-concept exploit and lab environment for CVE-2026-27495
 trinadh465/external_v8_aosp10_r33_cve-2021-0393
A patched version of the V8 JavaScript engine addressing CVE-2021-0393, providing a secure baseline for Android 10 R33 builds.
 alalng/cve-2022-44789
Proof-of-concept exploit and writeup for CVE-2022-44789, a heap buffer overflow in MuJS JavaScript interpreter, including vulnerable version and…
 jaf0rk/cve-2026-14431
Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 sneakynachos/cve-2026-2796-escape-wasm-by-using-wasm
PoC exploit chain for CVE-2026-2796: SpiderMonkey WebAssembly sandbox escape (signature type confusion -> arbitrary R/W -> RCE)
 sneakynachos/cve-2026-2764-but-with-wasm
Proof-of-concept exploit chain for Firefox JIT CVE-2026-2764, chaining JIT miscompilation and use-after-free into arbitrary read/write and WASM…