

CVE-2023-25136
 malvika-thakur/cve-2023-25136
OpenSSH Pre-Auth Double Free CVE-2023-25136 – Writeup and Proof-of-Concept
binary-exploitationeducationexploitation+3
3
malvika-thakur/cve-2023-25136OpenSSH Pre-Auth Double Free CVE-2023-25136 – Writeup and Proof-of-Concept
 imv7/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387, a remote code execution vulnerability. Provides a targeted exploitation tool for security testing and…
 diego-altf4/pwnctftool
Automated ret2win exploit tool for CTF challenges. Finds stack offset, generates payloads, supports remote exploitation, and attaches GDB for…
 fortra/cve-2022-30136
Windows Network File System Remote exploit for CVE-2022-30136
 acrono/cve-2024-6387-poc
32-bit PoC for CVE-2024-6387 — mirror of the original 7etsuo/cve-2024-6387-poc
 lflare/cve-2024-6387-poc
MIRROR of the original 32-bit PoC for CVE-2024-6387 "regreSSHion" by 7etsuo/cve-2024-6387-poc
 websecnl/cve-2022-26809
Remote Code Execution Exploit in the RPC Library
 kkirsche/cve-2004-2271
Python exploit for Minishare 1.4.1 remote buffer overflow (CVE-2004-2271) with proof-of-concept demonstration.
 ieee0824/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117, a Git remote code execution vulnerability that executes ifconfig on successful exploitation.
 cybermads/cve-2011-2523
Python exploit for vsftpd 2.3.4 backdoor vulnerability (CVE-2011-2523) that opens a shell on port 6200 when a smiley is sent in the USER parameter.
 doaso/cve-2023-42115
Remote code execution exploit for Exim AUTH out-of-bounds write vulnerability (CVE-2023-42115). No authentication required; includes build and usage…
 wdfcc/cve-2019-0708
Proof-of-concept crash exploit for CVE-2019-0708 (BlueKeep), targeting a remote code execution vulnerability in Windows RDP service.
 thecybermind/w48crash
PoC code for vulnerability in webmod v0.48. Originally written in 2007, assigned CVE-2007-1260.
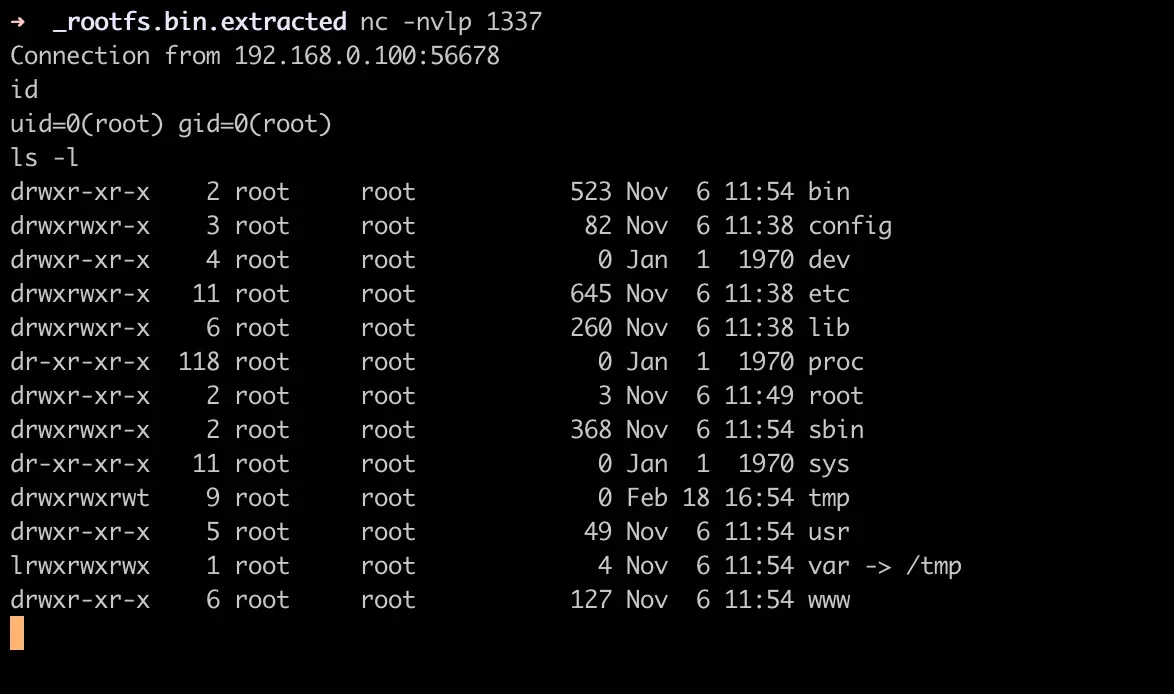 ii4gsp/cve-2026-1457
Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…
 writegsqword/cve-2024-39840-poc
Proof-of-concept exploit for CVE-2024-39840, a remote code execution vulnerability in Factorio 1.1.86. Adapted from a detailed writeup, demonstrating…
 throwawayaccount12312312/precompiled-cve-2018-10933
Precompiled exploit for CVE-2018-10933 targeting LibSSH servers. Enables unauthorized remote access via a server-side authentication bypass…
 war4uthor/cve-2009-4660
CVE-2009-4660 - BigAnt Server 2.52 'USV' Remote Buffer Overflow Vulnerability. Tested on Windows XP Professional SP3.
 cyberdesu/remote-buffer-overflow-cve-2003-0172
Python-based remote buffer overflow exploit targeting CVE-2003-0172. Accepts host and port arguments to deliver a payload for penetration testing and…