s26-m1q-ghostlock-selinux

GhostLock CVE-2026-43499 research for Galaxy S26 (SM-S942U1/m1q): SELinux Permissive achieved, KASLR + tracefs port, uid=0 boundary documented

GhostLock CVE-2026-43499 research for Galaxy S26 (SM-S942U1/m1q): SELinux Permissive achieved, KASLR + tracefs port, uid=0 boundary documented

Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.

A Proof of concept scenario for exploitation of CVE2021-38297 GO WASM buffer-overflow

A core dump debugging murder mystery.

CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port

Proof-of-concept exploit for CVE-2021-28476, a Microsoft Hyper-V vmswitch vulnerability allowing attacker-controlled pointer dereference and…

Proof-of-concept exploit for CVE-2023-38545, a heap buffer overflow in libcurl's SOCKS5 proxy handshake triggered via a malicious HTTP 301 redirect…

Remote buffer overflow exploit for D-Link DIR-619L router (CVE-2024-9570) targeting the formEasySetTimezone function for penetration testing and…

CHARON — pre-built PoC for CVE-2026-46333 (Linux ptrace mm==NULL fd theft)

Chrome V8 exploit for CVE-2019-5825 targeting version 73.0.3683.86 with --no-sandbox. Includes proof-of-concept code and integration with Metasploit…

Productization efforts of CVE-2020-11179 Adreno-Qualcomm-GPU bug, original poc by Ben Hawkes of P0

CVE-2019-5700

PoC exploit chain for CVE-2026-2796: SpiderMonkey WebAssembly sandbox escape (signature type confusion -> arbitrary R/W -> RCE)

Proof-of-concept exploit for CVE-2026-8461, generating a crafted AVI file that triggers a crash in unpatched ffmpeg versions.

POC for CVE-2026-23416 (linux kernel 6.17 – linux kernel 7 rc5) - vulnerability discovered by Antonius

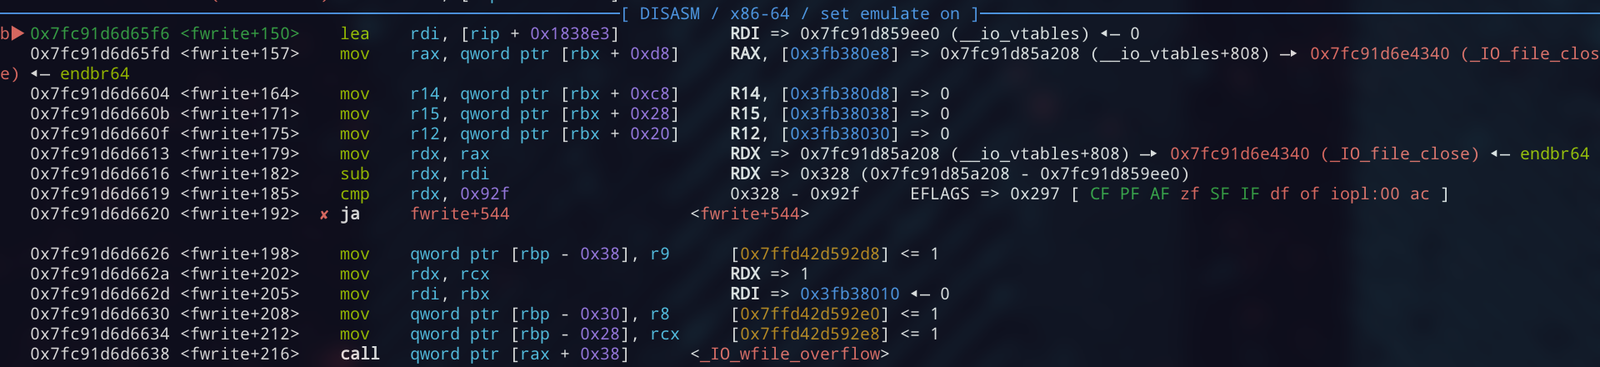
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…

Demo-ing CVE-2017-1000253 in a container

CVE-2026-41089