
CVE-2026-25243
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).
binary-exploitationexploitationmemory-forensics+5
13
dinosn/cve-2026-25243CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).
 jmousqueton/cve-2023-21716
POC : CVE-2023-21716 Microsoft Word RTF Font Table Heap Corruption
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 bytev0rtex/cve-2026-64788
Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…
 marsel-marsel/cve-2022-45770
LPE exploit via windows driver
 fusiondrive/cve-2026-43499-s24u
CVE-2026-43499 research port for Galaxy S24 Ultra SM-S928U1 DZF2 (COMPLETED)
 otsmane-ahmed/cve-2025-29384-poc
Proof-of-concept exploit for CVE-2025-29384, a critical stack-based buffer overflow in Tenda AC9 routers. Includes Python and Metasploit modules for…
 horizon3ai/cve-2026-22200
CVE-2026-22200: Arbitrary file read + CNEXT RCE in osTicket
 lunbun/cve-2025-55188
Proof-of-concept exploit for CVE-2025-55188 demonstrating arbitrary file write in 7-Zip via symlink path traversal, with escalation to arbitrary code…
 gabriel-lacorte/cve-2025-7771
Arbitrary Function Call Exploit using the ThrottleStop driver
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 szymonh/inspector-gadget
CVE-2021-39685 Description and sample exploit for Linux USB Gadget overflow vulnerability
 cssxn/cve-2020-17136
Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability
 reaizuguo/vivo_iqoo_neo_9_root_research_on_cve-2025-21479
iQOO Neo9 (PD2338C) 免解锁 Caps-Root 工具** — 基于 CVE-2025-21479 (Adreno GPU SDS) 的任意物理写提权方案

 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
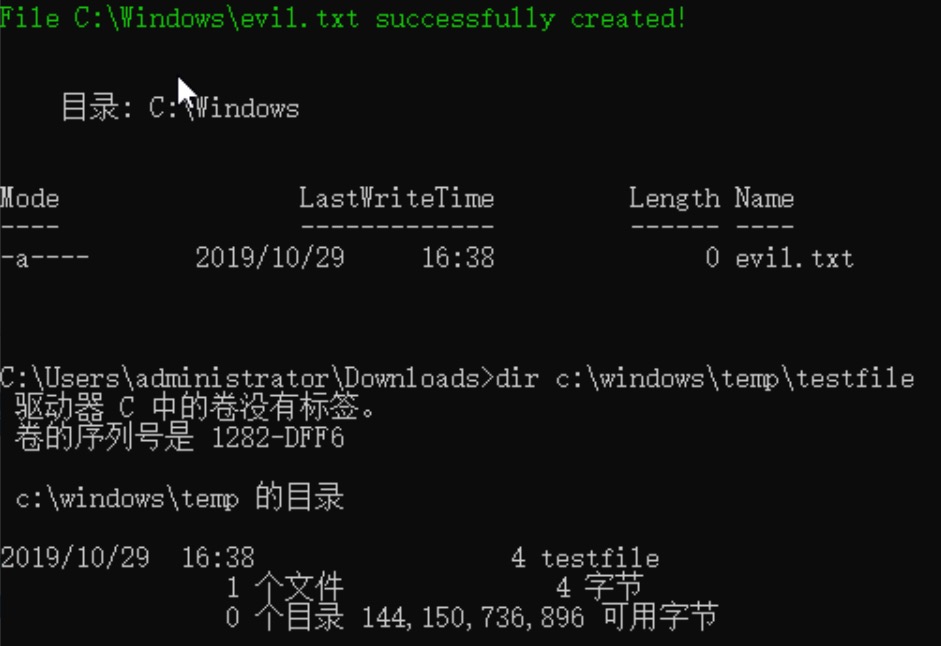 mayter/cve-2019-1315
Proof-of-concept PowerShell exploit for CVE-2019-1315, a Windows Error Reporting Manager arbitrary file move elevation of privilege vulnerability,…