
CVE-2022-48565-POC
 einstein2150/cve-2022-48565-poc
A proof-of-concept for CVE-2022-48565 - python plistlib XML deserialisation attack
binary-exploitationeducationexploitation+3
3
einstein2150/cve-2022-48565-pocA proof-of-concept for CVE-2022-48565 - python plistlib XML deserialisation attack
 tna0y/cve-2018-1000802-poc
Python CVE-2018-1000802 Proof-of-Concept
 umu618/cve-2024-21338
Fork of https://github.com/hakaioffsec/CVE-2024-21338
 madexploits/cve-2025-40271
CVE-2025-40271 Modifed By MadEploits
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 sprushed/cve-2022-30292
Technical documentation and analysis of CVE-2022-30292, a heap-based buffer overflow in Squirrel 3.2 leading to denial of service, sandbox escape,…
 halcy0nic/cve-2022-36234
Proof of concept for CVE-2022-36234
 k0n9-log/cve-2023-6931
CVE-2023-6931 kernel panic PoC
 hi0u/poc-cve-2024-12227
# CVE-2024-12227 - NTIOLib_X64.sys DoS PoC
 animeprincess420/cve-2025-4517-poc
CVE‑2025‑4517 Proof‑of‑Concept Script
 sexyshoelessgodofwar/cve-2025-47256
Stack overflow in LibXMP
 citizen13x/cve-2021-43229
CVE-2021-43229 Walkthrough
 mein-0/cve-2026-29923
Proof-of-concept for CVE-2026-29923, a local privilege escalation in pstrip64.sys kernel driver. Demonstrates physical memory read/write primitive…
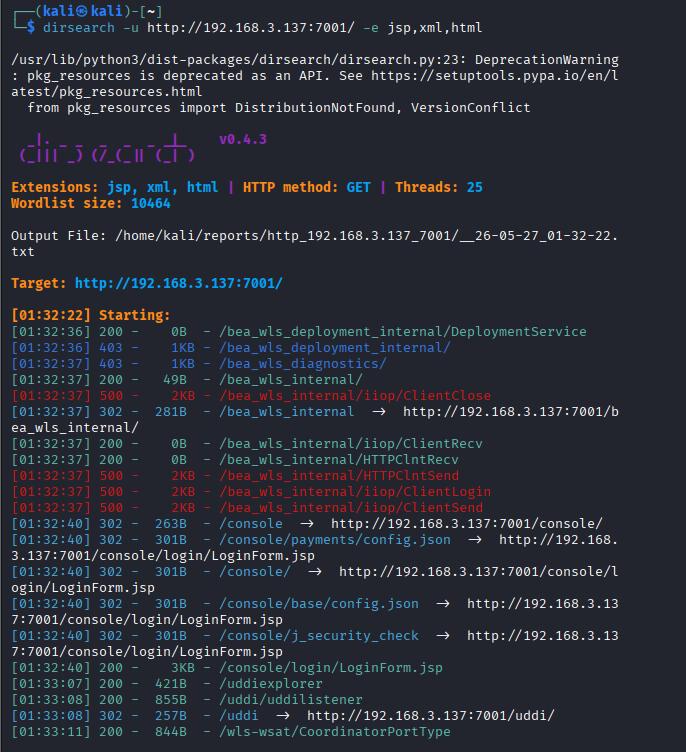 dungsocool/cve-2017-10271
Step-by-step lab guide for exploiting CVE-2017-10271 (WebLogic XMLDecoder deserialization RCE) with manual payload construction, blind RCE bypass,…
 0linear/cve-2026-62958
Proof-of-concept for CVE-2026-62958: crafts a malformed ELF to trigger an out-of-bounds read in Libriscv and crash the sandbox with SIGSEGV.
 nonameuserosint-hue/fragnesia-go
A Go implementation of fragnesia (CVE-2026-46300)