

pwnfest2016
 secmob/pwnfest2016
full exploit of pwnfest2016, slide and full text of syscan2017
binary-exploitationexploitationpapers-research+1
164
secmob/pwnfest2016full exploit of pwnfest2016, slide and full text of syscan2017
 hackerschoice/team-teso
Historical archive of exploit code and tools from TESO, including remote exploits, DDoS agents, and development utilities for educational security…
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 kangtastic/cve-2019-2215
Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
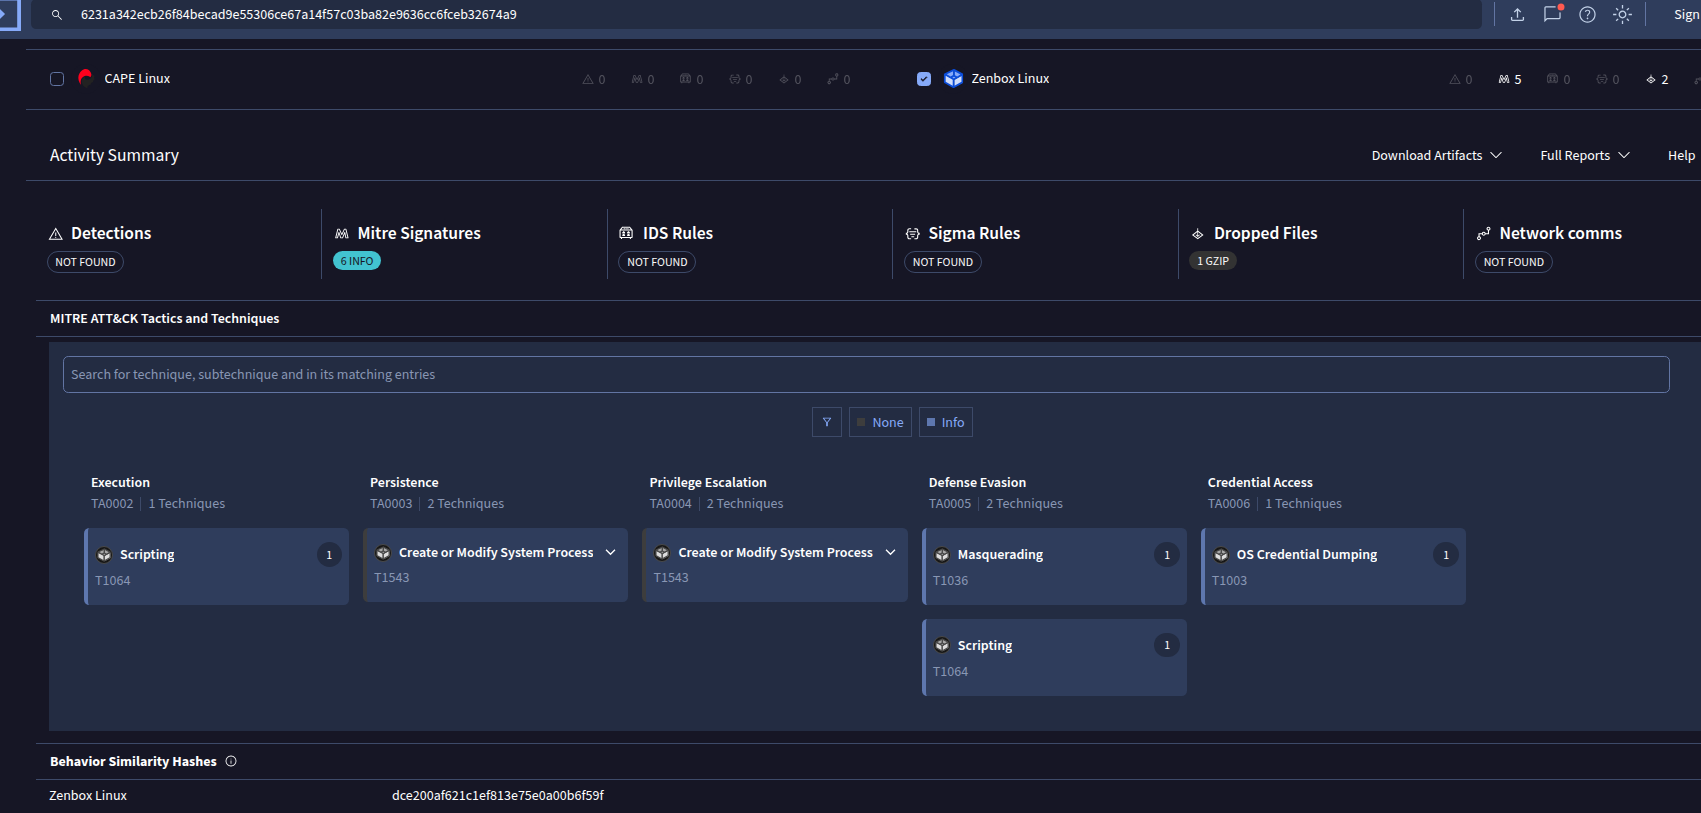 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 alephsecurity/initroot
Motorola Untethered Jailbreak: Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 kkent030315/cve-2022-42046
Proof-of-concept exploit for CVE-2022-42046 demonstrating local privilege escalation via direct kernel object manipulation of EPROCESS Protection and…
 nccgroup/libslub
Python library for examining Linux kernel SLUB heap allocations and structures within GDB, enabling deeper understanding of kernel heap internals for…
 g4sp4rcs/cve-2026-42980-poc
Public exploit and research material for CVE-2026-42980, a Windows kernel WMI integer-underflow vulnerability enabling local privilege escalation to…
 irql/cve-2021-31728
Public proof-of-concept for CVE-2021-31727 and CVE-2021-31728 demonstrating unrestricted disk read/write and arbitrary ring 0 code execution in…
 abdsec/cve-2016-0801
C-based proof-of-concept exploit for CVE-2016-0801, demonstrating a specific vulnerability in Android components for security research and testing.