
CVE-2023-21716
 xnuvers007/cve-2023-21716
RTF Crash POC Python 3.11 Windows 10
binary-exploitationexploitationpayload-generation+2
463 years ago
xnuvers007/cve-2023-21716RTF Crash POC Python 3.11 Windows 10
 hexx0r/cve-2016-0051
Proof-of-concept exploit for CVE-2016-0051 (MS16-016) achieving local privilege escalation to SYSTEM on Windows 7, with compiled binaries and…
 plazmaz/cve-2019-18634
A functional exploit for CVE-2019-18634, a BSS overflow in sudo's pwfeedback feature that allows for for privesc
 flowerwind/autogeneratexalanpayload
cve-2022-34169 延伸出的Jdk Xalan的payload自动生成工具,可根据不同的Jdk生成出其所对应的xslt文件
 spiralbl0ck/chrome-v8-rce-cve-2021-38003
CVE-2021-38003 exploits extracted from https://twitter.com/WhichbufferArda/status/1609604183535284224
 siberas/cve-2016-3309_reloaded
Exploits for the win32kfull!bFill vulnerability on Win10 x64 RS2 using Bitmap or Palette techniques
 0xeb-bp/cve-2020-1015
PoC for CVE-2020-1015
 mbanyamer/cve-2025-30397---windows-server-2025-jscript-rce-use-after-free-
Remote Code Execution via Use-After-Free in JScript.dll (CVE-2025-30397)
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 zer0t0/cve-2025-56383-proof-of-concept
CVE-2025-56383-Proof-of-Concept
 thoxy67/zig-pe
Reflective PE loader written in Zig. Loads and executes native and .NET PE files directly from memory.
 kristal-g/cve-2021-40449_poc
Exploit for CVE-2021-40449
 maxpl0it/cve-2019-17026-exploit
An exploit for CVE-2019-17026. It pops xcalc and was tested on Ubuntu (x64).
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 sam-b/cve-2014-4113
Trigger and exploit code for CVE-2014-4113
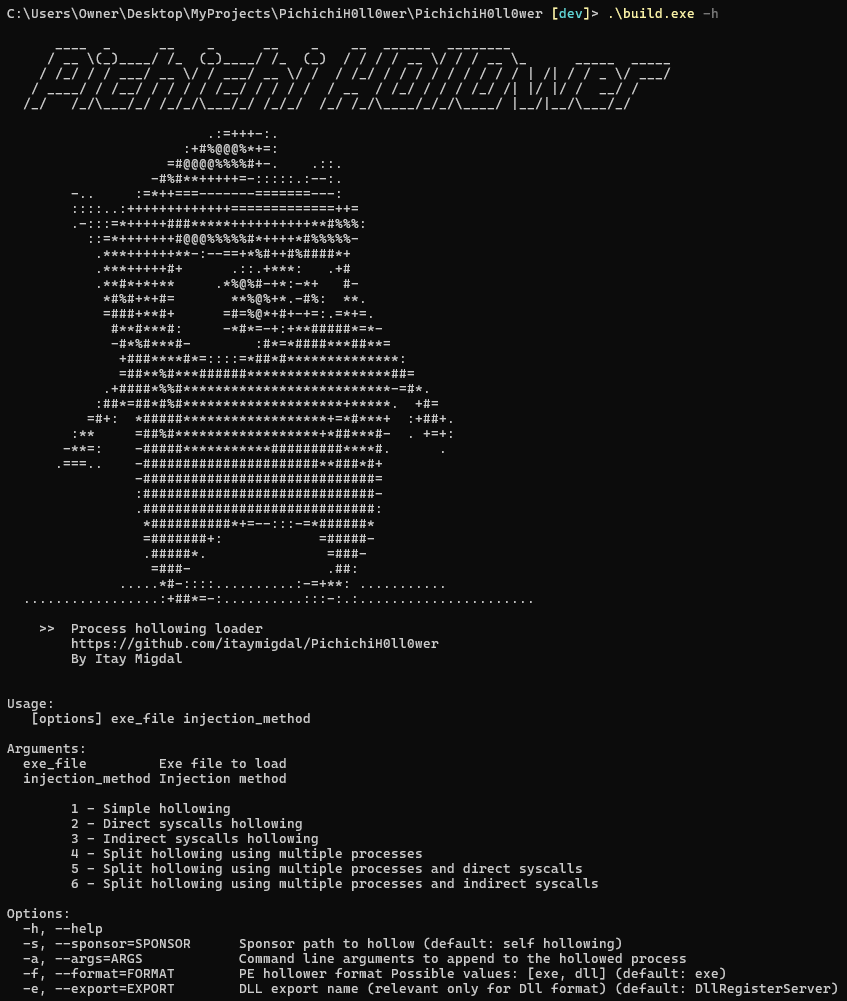 itaymigdal/pichichih0ll0wer
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
 sfewer-r7/cve-2025-0282
PoC for CVE-2025-0282: A remote unauthenticated stack based buffer overflow affecting Ivanti Connect Secure, Ivanti Policy Secure, and Ivanti Neurons…
 panyu6325/cve-2015-1805
Proof-of-concept exploit for CVE-2015-1805, a Linux kernel vulnerability enabling local privilege escalation via a race condition in the pipe buffer…