cve-2024-27130-poc
CVE-2024-27130是影响QNAP网络附加存储(NAS)设备的一个严重漏洞。该漏洞源于QTS操作系统中share.cgi脚本的No_Support_ACL函数中不安全地使用strcpy函数,导致堆栈缓冲区溢出。攻击者可以利用此漏洞,通过精心构造的请求在目标系统上执行任意代码,进而完全控制受影…

CVE-2024-27130是影响QNAP网络附加存储(NAS)设备的一个严重漏洞。该漏洞源于QTS操作系统中share.cgi脚本的No_Support_ACL函数中不安全地使用strcpy函数,导致堆栈缓冲区溢出。攻击者可以利用此漏洞,通过精心构造的请求在目标系统上执行任意代码,进而完全控制受影…

Precompiled exploit for CVE-2018-10933 targeting LibSSH servers. Enables unauthorized remote access via a server-side authentication bypass…

CVE-2009-4660 - BigAnt Server 2.52 'USV' Remote Buffer Overflow Vulnerability. Tested on Windows XP Professional SP3.

CVE-2003-0264 SLMail5.5_RemoteBufferOverflow

Bypass for Symantec Endpoint Protection's Client User Interface Password

Exploit for CVE-2024-6387 targeting a signal handler race condition in OpenSSH sshd on glibc-based Linux systems, enabling remote code execution as…

CVE-2024-38077-POC

Variant of hackerhouse-opensource/cve-2018-10933

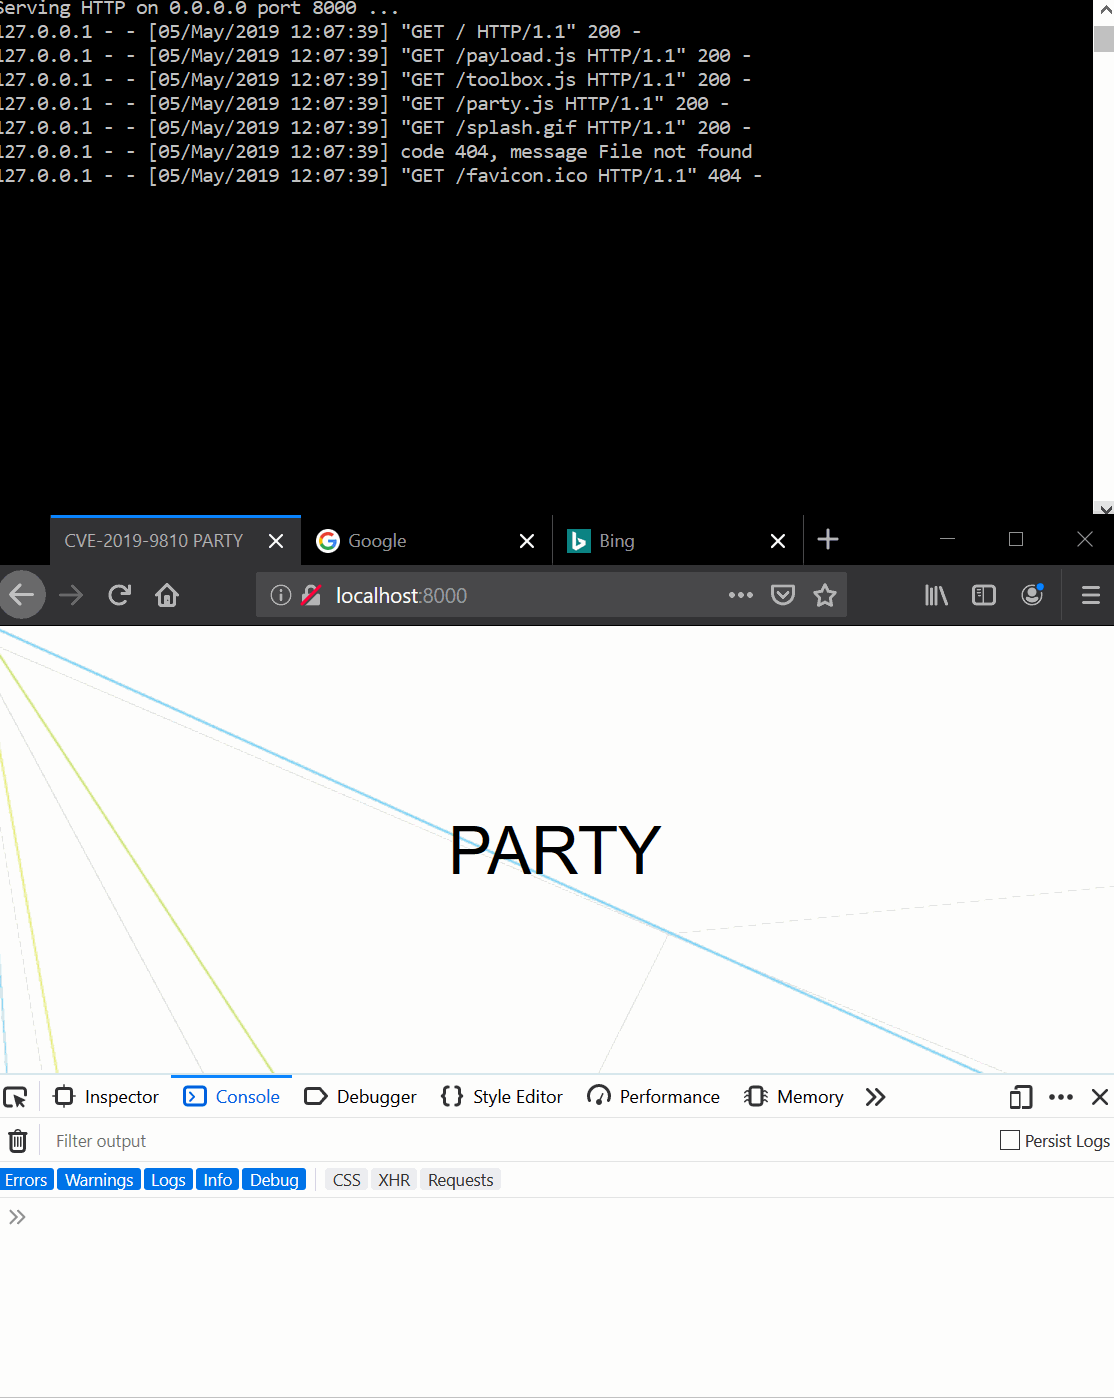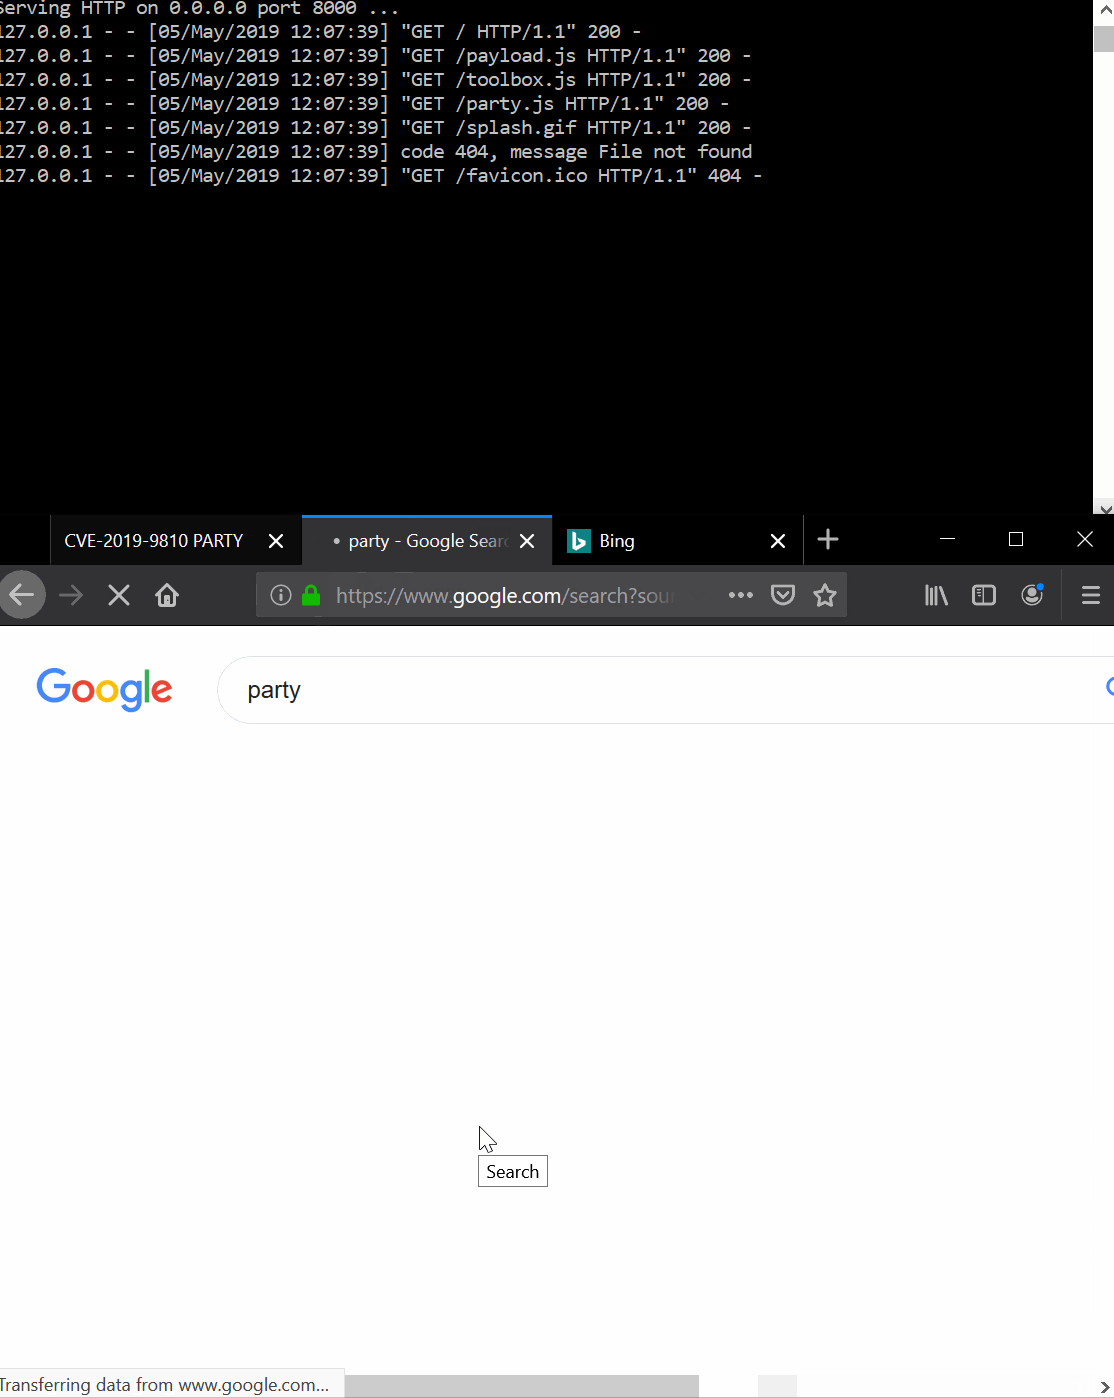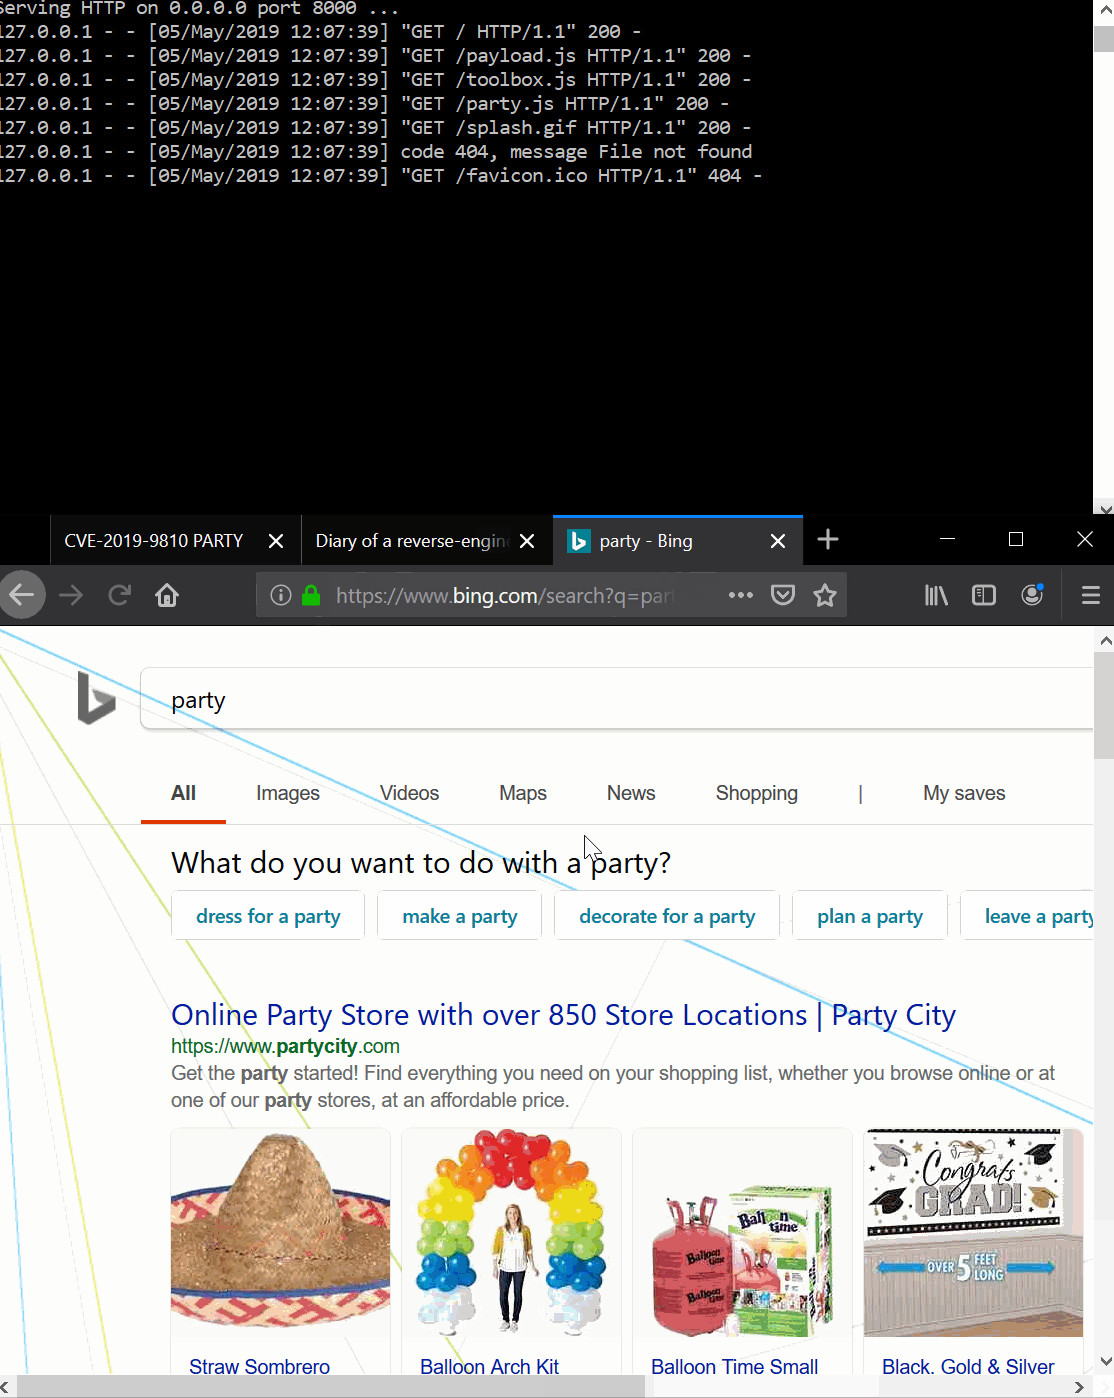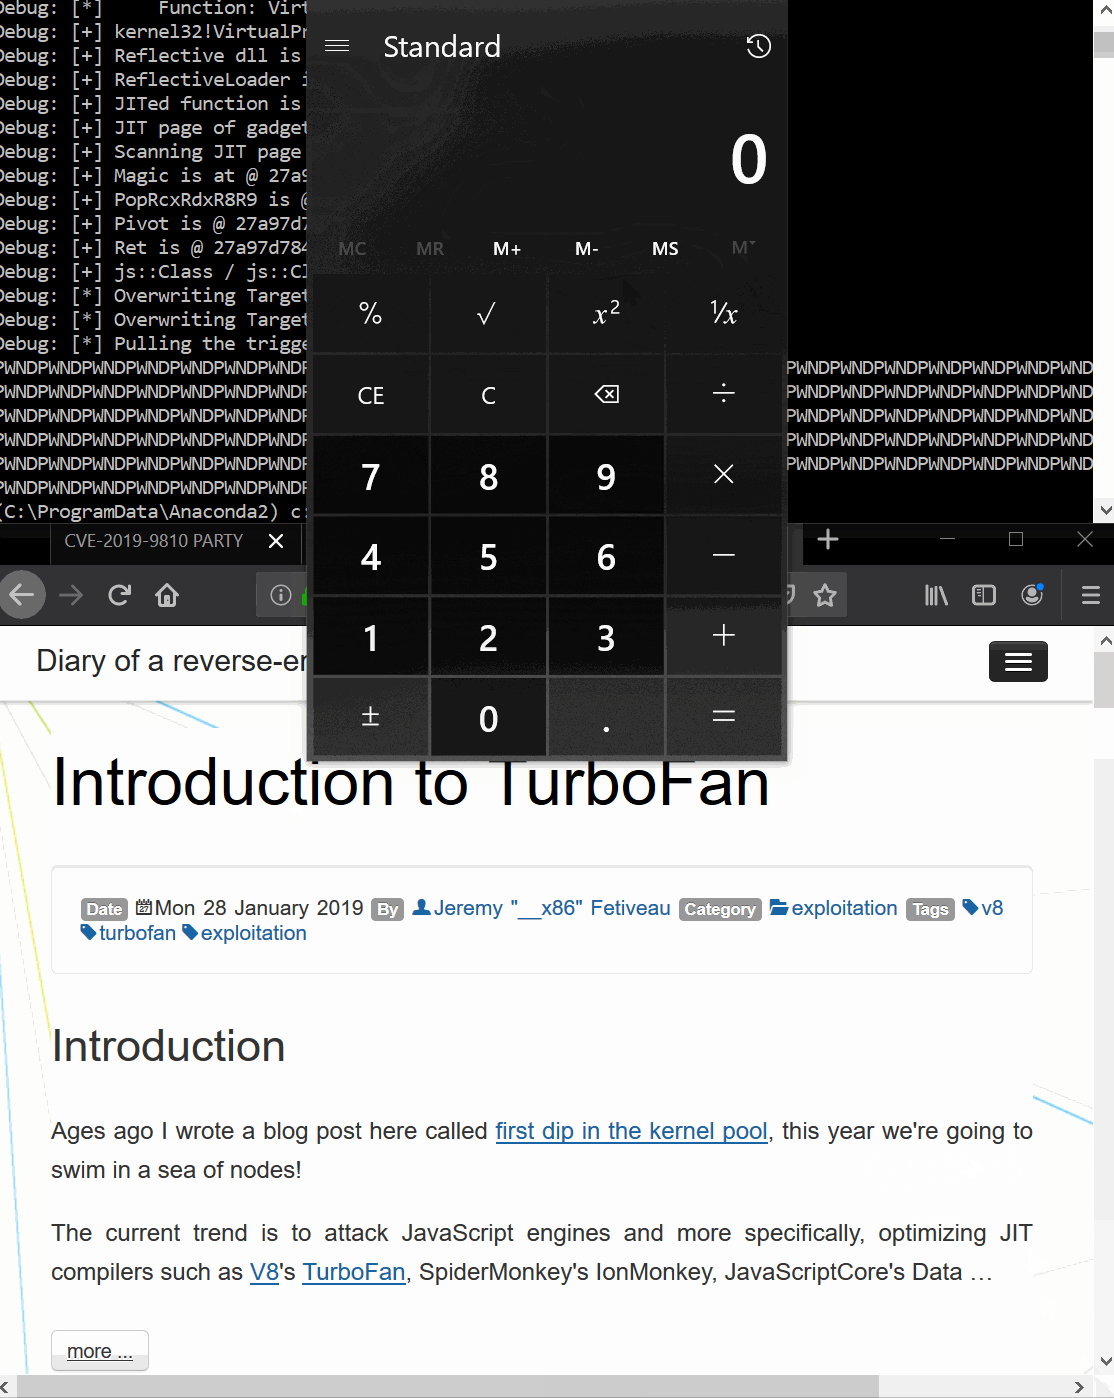
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.

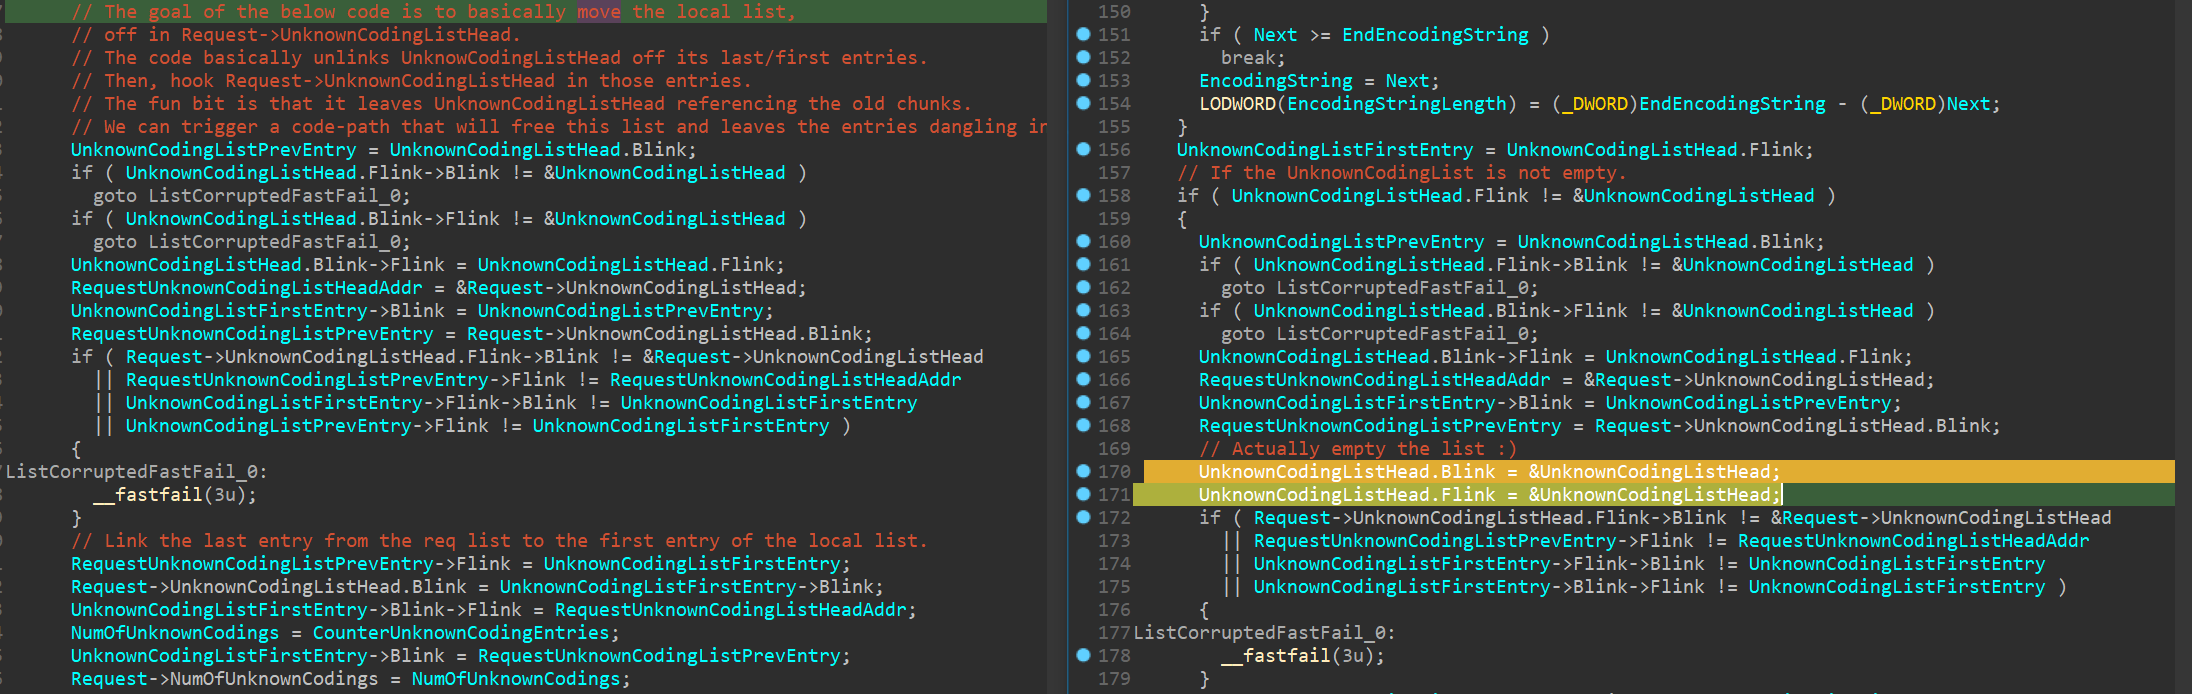
Proof of concept for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely.