
CVE-2022-23967
 maherazzouzi/cve-2022-23967
TightVNC Vulnerability.
binary-exploitationexploitationremote-access-tool+1
16
maherazzouzi/cve-2022-23967TightVNC Vulnerability.
 kn32/cve-2024-46483
Pre-Authentication Heap Overflow in Xlight SFTP server <= 3.9.4.2
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…
 freax13/cve-2024-21978-poc
Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
 ieee0824/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117, a Git remote code execution vulnerability that executes ifconfig on successful exploitation.
 razureink/cve-2024-38077-madlicense_reproduction
CVE Reproduction: cve-2024-38077-madlicense_reproduction
 thanawee321/cve-2024-38063
Vulnerability CVE-2024-38063
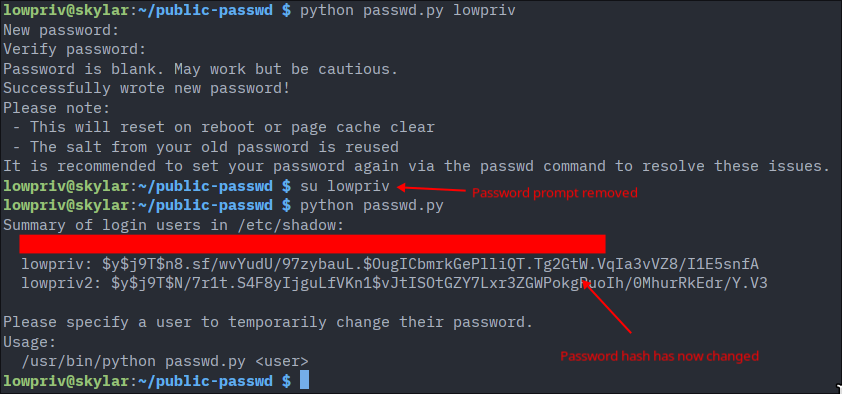 st4rburn/public-passwd
Use CVE-2026-46333 and CVE-2026-31431 to change any user's password.
 doaso/cve-2023-42115
Remote code execution exploit for Exim AUTH out-of-bounds write vulnerability (CVE-2023-42115). No authentication required; includes build and usage…
 zjw88282740/cve-2019-0708-win7
 wdfcc/cve-2019-0708
Proof-of-concept crash exploit for CVE-2019-0708 (BlueKeep), targeting a remote code execution vulnerability in Windows RDP service.
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
 teamtopkarl/cve-2025-32433
Erlang/OTP SSH 远程代码执行漏洞
 thecybermind/w48crash
PoC code for vulnerability in webmod v0.48. Originally written in 2007, assigned CVE-2007-1260.
 7etsuo/cve-2024-6387-poc
a signal handler race condition in OpenSSH's server (sshd)
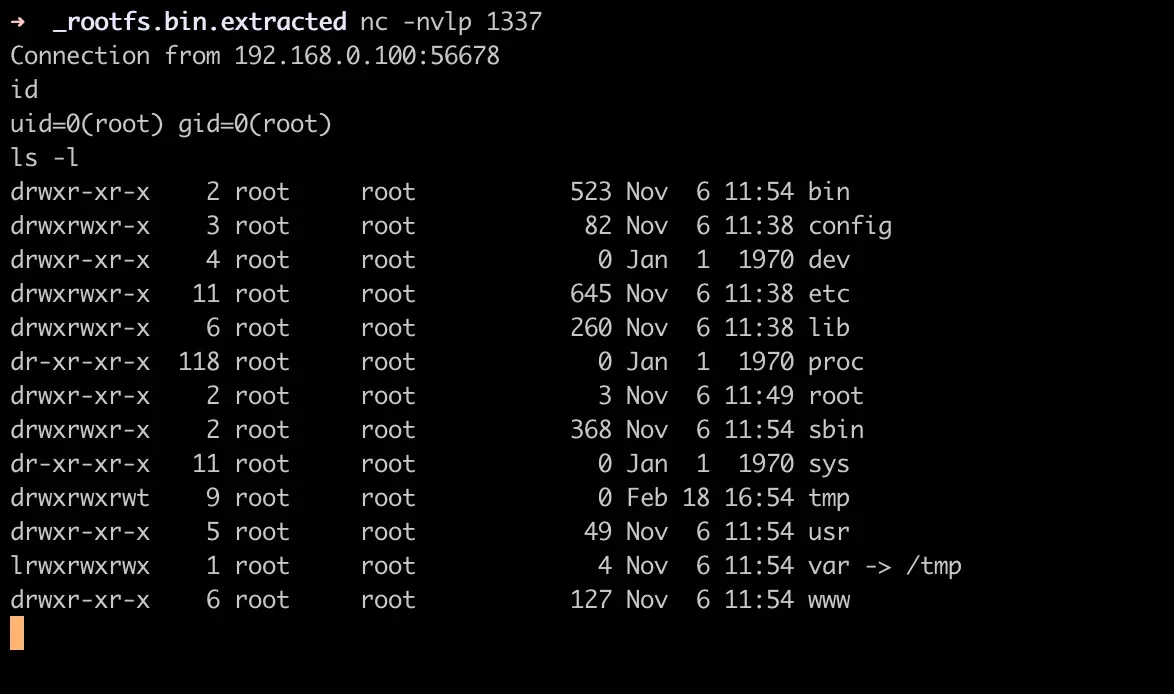 ii4gsp/cve-2026-1457
Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…
 writegsqword/cve-2024-39840-poc
Proof-of-concept exploit for CVE-2024-39840, a remote code execution vulnerability in Factorio 1.1.86. Adapted from a detailed writeup, demonstrating…