
CVE-2018-3252
 go-spider/cve-2018-3252
Exploit for CVE-2018-3252 targeting WebLogic deserialization vulnerability. Includes payload generation with ysoserial and a Python proof-of-concept…
binary-exploitationexploit-frameworkspayload-development+3
18
go-spider/cve-2018-3252Exploit for CVE-2018-3252 targeting WebLogic deserialization vulnerability. Includes payload generation with ysoserial and a Python proof-of-concept…
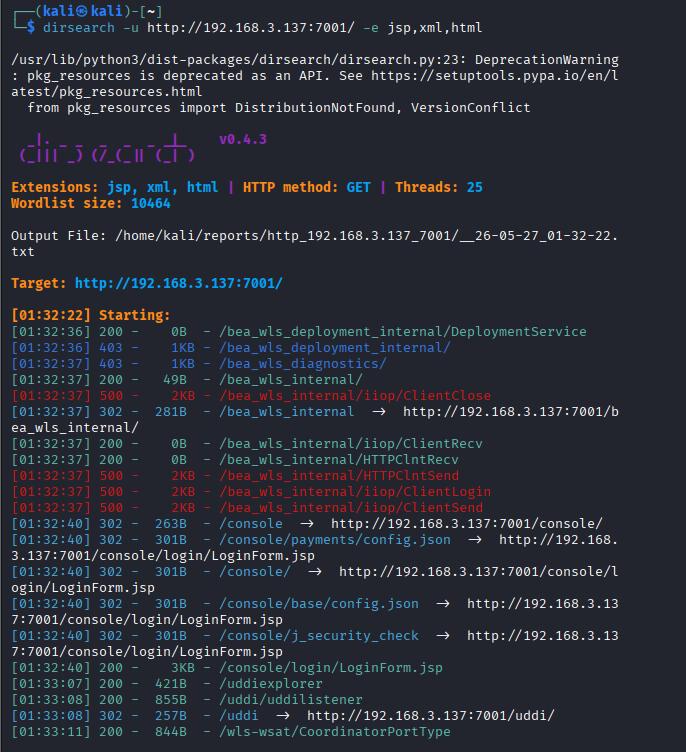 dungsocool/cve-2017-10271
Step-by-step lab guide for exploiting CVE-2017-10271 (WebLogic XMLDecoder deserialization RCE) with manual payload construction, blind RCE bypass,…
 simoesctt/ctt-apple-silicon-refraction
webkit_refraction.js (The 33-Layer WebGL Payload) This JavaScript payload uses the \alpha constant to create a high-frequency "Memory Shiver." It…
 foxoman/cve-2024-24576-poc---nim
Proof-of-concept demonstrating command injection (BatBadBut) vulnerability in Nim on Windows, with payload testing across execProcess and…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
 kitsuneshade/winrar-exploit-tool---rust-edition
A high-performance, memory-safe implementation of the WinRAR CVE-2025-8088 exploit tool, rewritten in Rust for better reliability and performance.