android-kernel-exploitation

Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.

Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.

Deobfuscation via optimization with usage of LLVM IR and parsing assembly.

Exploit for CVE-2022-20452, privilege escalation on Android from installed app to system app (or another app) via LazyValue using Parcel after…

A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks

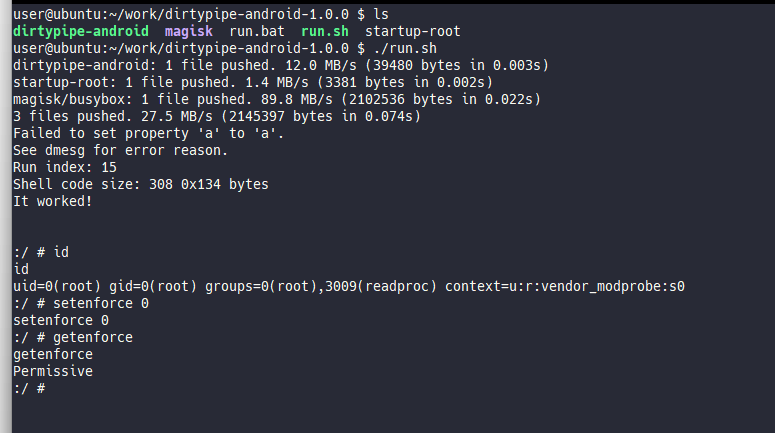
Dirty Pipe root exploit for Android (Pixel 6)

Android 14 kernel exploit for Pixel7/8 Pro

A PoC application demonstrating the power of an Android kernel arbitrary R/W.

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…

Exploits for Android Binder bug CVE-2020-0041

CVE-2026-43499 Implementation for 6.12.23-android16-5-g75e9b1c7ae7c-abogki463945075-4k

A Nim implementation of reflective PE-Loading from memory

metame is a metamorphic code engine for arbitrary executables

Patching ROP-encoded shellcodes into PEs

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.

Proof-of-concept exploit for CVE-2015-3636 targeting 32-bit Android OS kernel privilege escalation.

Collections of my POCs for android vendor CVEs

Bad Spin: Android Binder Privilege Escalation Exploit (CVE-2022-20421)

Android kernel exploit for CVE-2025-38352, previously exploited in-the-wild. Targets vulnerable x86_64 Linux kernels v5.10.x.