CVE-2026-31431-old-python

Provides a ctypes wrapper for the splice syscall to enable exploitation of CVE-2026-31431 on Python versions below 3.10, tested on Python 3.7.3.

Provides a ctypes wrapper for the splice syscall to enable exploitation of CVE-2026-31431 on Python versions below 3.10, tested on Python 3.7.3.

fork of worawit/CVE-2021-3156 exploit_nss.py modified to work with ifconfig instead of the ip command

Proof of concept with the academic purpose to understand the Buffer Overflow vulnerability using as background the CVE-2019-11395

Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…

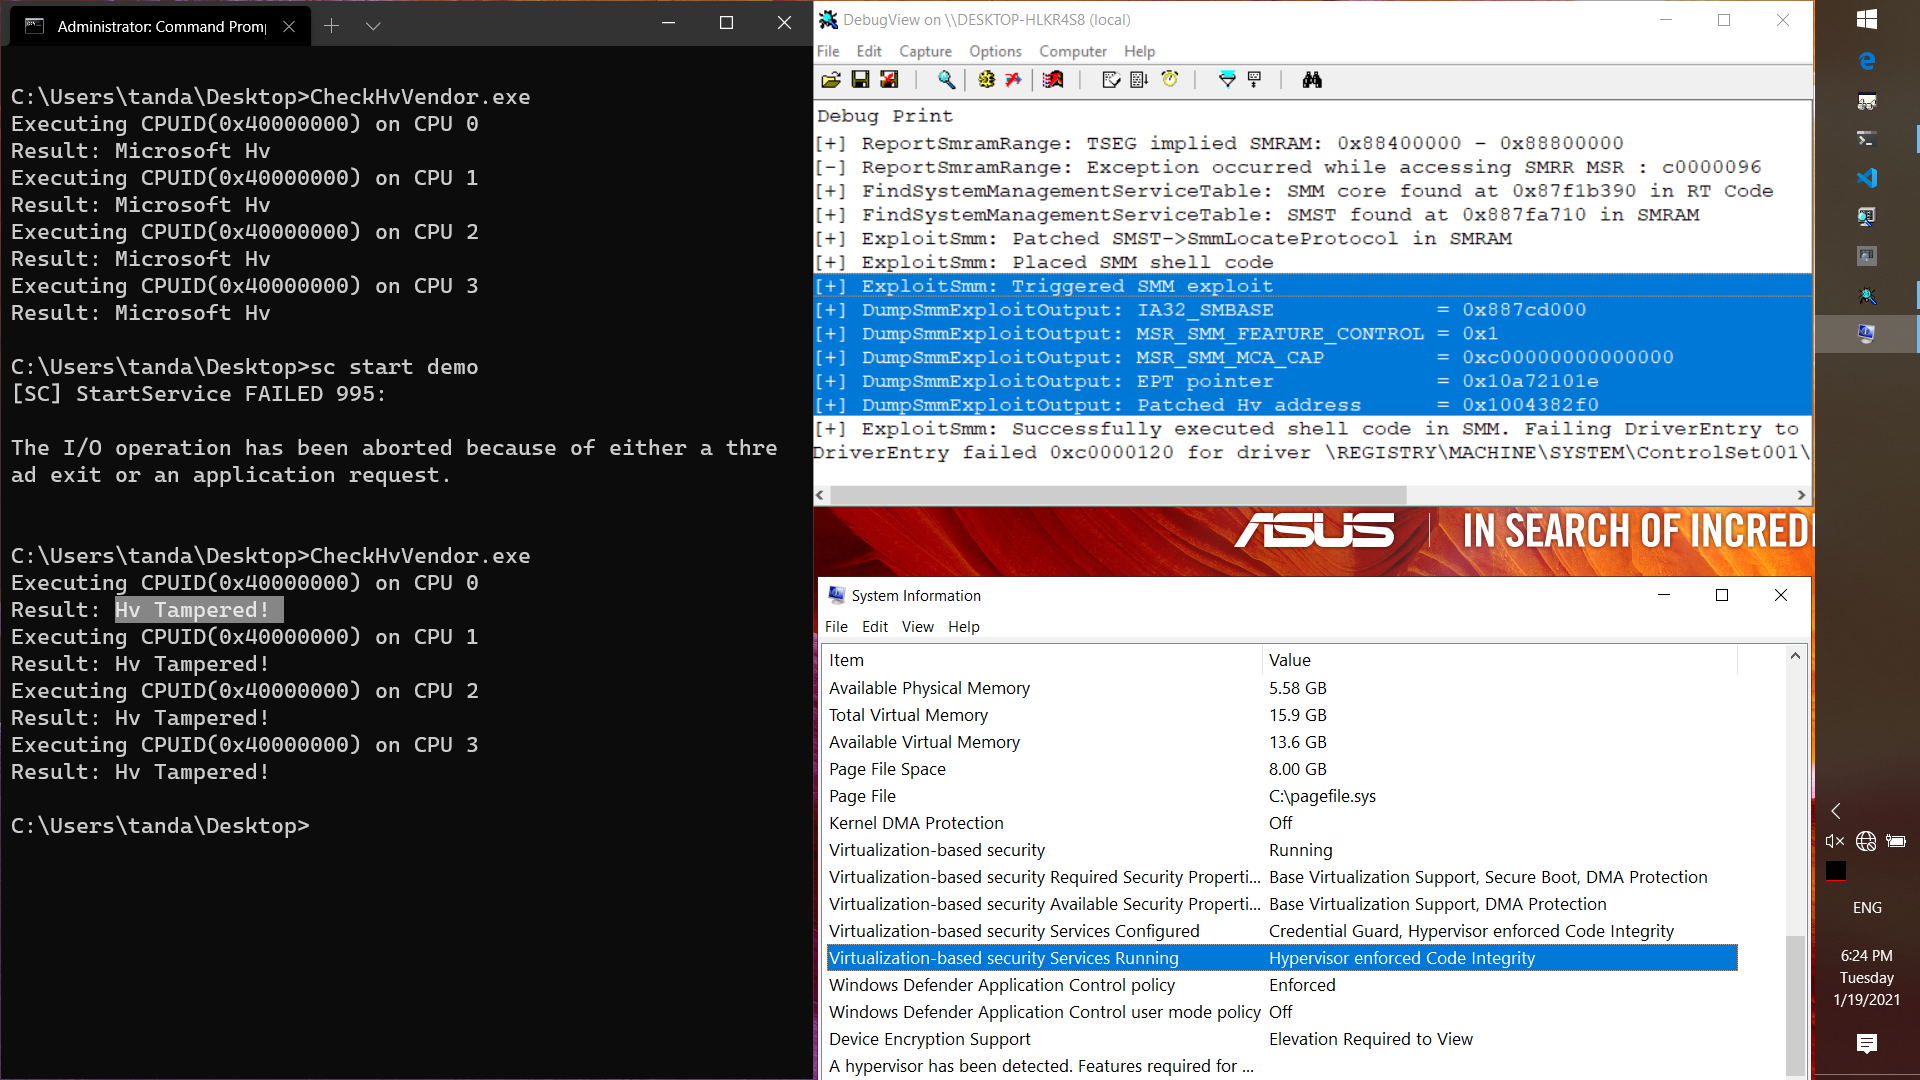
The report and the exploit of CVE-2021-26943, the kernel-to-SMM local privilege escalation vulnerability in ASUS UX360CA BIOS version 303.

CVE-2017-13868: Information leak of uninitialized kernel heap data in XNU.

Step-by-step walkthrough for exploiting CVE-2015-1328 (OverlayFS) to escalate privileges from a low-privileged user to root on Ubuntu 14.04. Includes…

A Bash-based privilege escalation exploit targeting the `below` system performance monitoring tool. This refurbished exploit leverages a symlink…

PoC exploit for CVE-2025-47917: Use-After-Free in mbedTLS leading to remote code execution.

Stack-based buffer overflow in the server in IBM Tivoli Storage Manager FastBack 6.1 before 6.1.12 allows remote attackers to cause a denial of…

Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.

CVE-2026-2766, but with wasm

CVE-2026-5281 (Chrome Dawn WebGPU UAF) analysis, lab validation tools, and reproducible environment for vulnerable vs patched builds.

baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability

C-based tool exploiting the vulnerable wsftprm.sys kernel driver to terminate protected EDR/AV processes on Windows, including PPL processes, via…

Proof of concept code in C# to exploit the WinRAR ACE file extraction path (CVE-2018-20250).

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.

Exploiting CVE-2016-4657 to JailBreak the Nintendo Switch