Windows-Kernel-Exploitation

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks

Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…

exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House

PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…

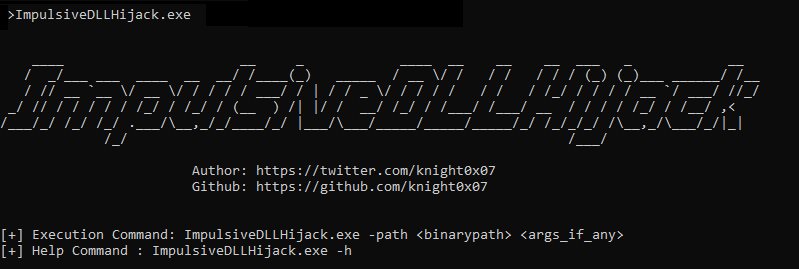
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

Curated collection of iOS kernel and userland exploit PoCs and writeups for in-the-wild and researched CVEs, including binary-diffed vulnerability…

Slides and conference talks from security research covering Windows, virtualization, web, and blockchain exploit techniques, presented at Black Hat,…

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…

Proof-of-concept exploit for CVE-2020-0787, a Windows privilege escalation vulnerability. Supports all Windows versions for security research and…

Python exploit for CVE-2015-1538-1 targeting Stagefright's 'stsc' MP4 atom integer overflow to achieve remote code execution and a reverse shell on…

Nim-based assembly packer and shellcode loader for opsec & profit

Collection of proof-of-concept exploits and technical analyses for high-impact CVEs, covering browser memory corruption, TCP/IP RCE, and web…

IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…

Exploits and Security Tools Framework 2.0.1

CVE-2016-5195 (Dirty COW) exploit that modifies /etc/passwd to escalate privileges and spawn a root shell on vulnerable Linux kernels.

Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…

A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++