
CVE-2025-56799
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
binary-exploitationexploitationmalware-analysis+3
1
shinycolumn/cve-2025-56799OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
 nasawyer7/iobitmalwarefighterdll
(0 day) CVE-2026-37333 LPE I found in IObit Malware Fighter v. 13.2.0.
 osmancanvural/cve-2026-21436
Proof-of-concept exploit for CVE-2026-21436, demonstrating path traversal in Solus OS eopkg package manager allowing arbitrary file write during…
 rajauzairabdullah/cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a remote code execution vulnerability in Windows Notepad, demonstrating file-based trigger and execution…
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
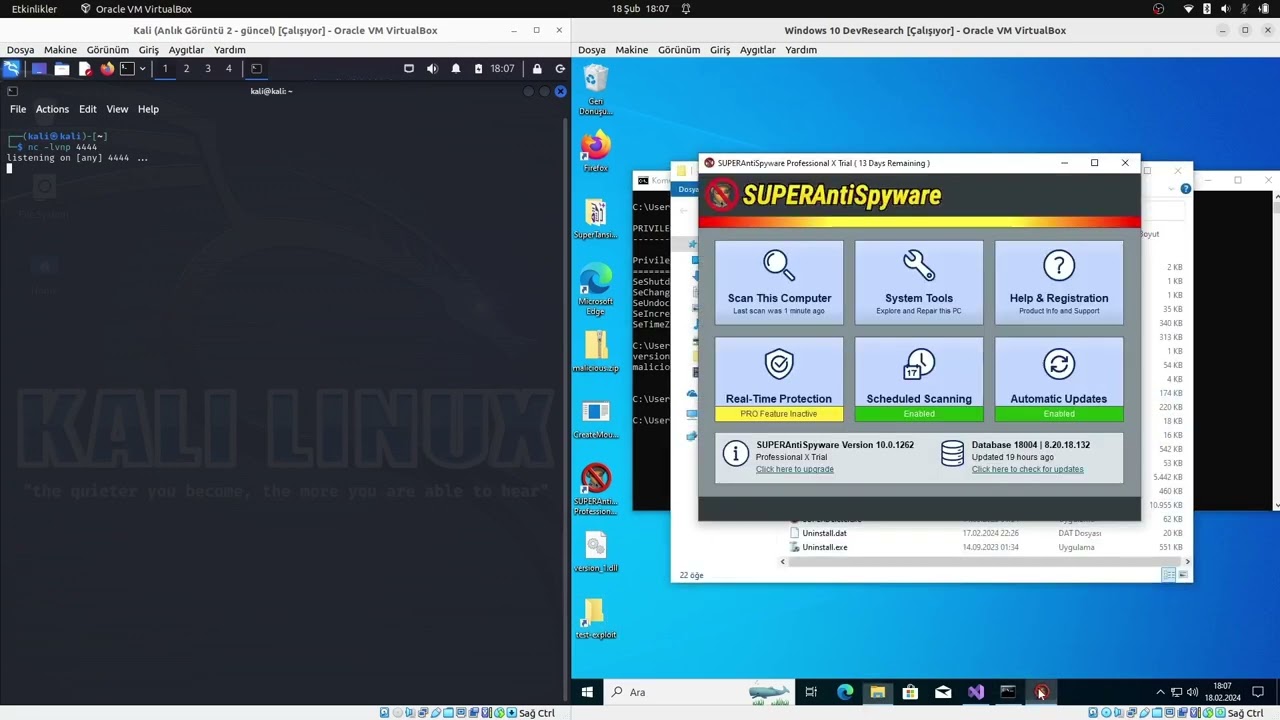 secunnix/cve-2024-27518
SUPERAntiSpyware Professional X <=10.0.1264 LPE Vulnerability PoC
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
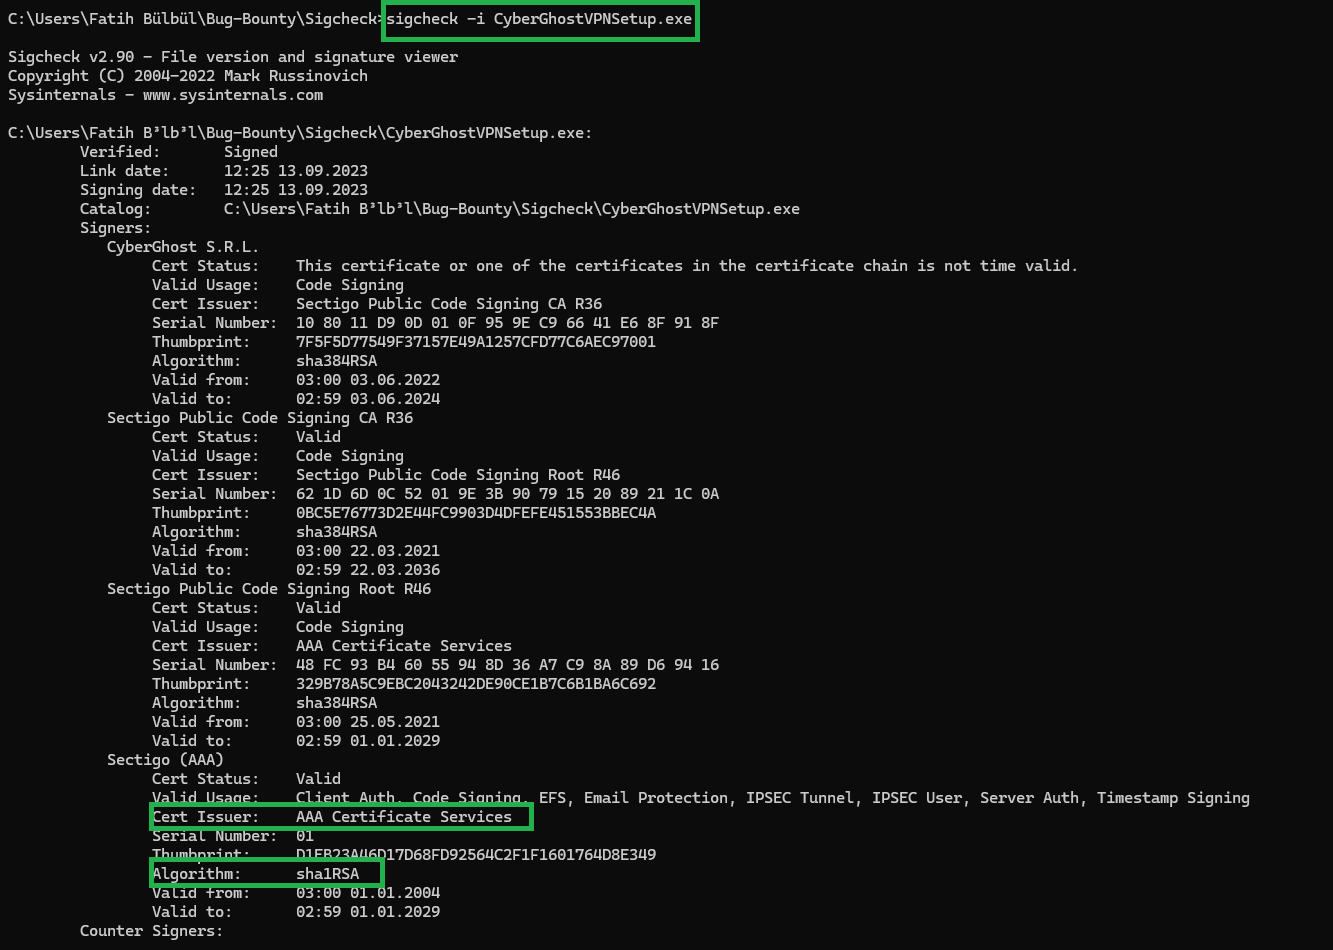 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.
 pixelofapicture/001-malware-analysis-cve-2017-11882
Malware Analysis CVE-2017-11882
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…