
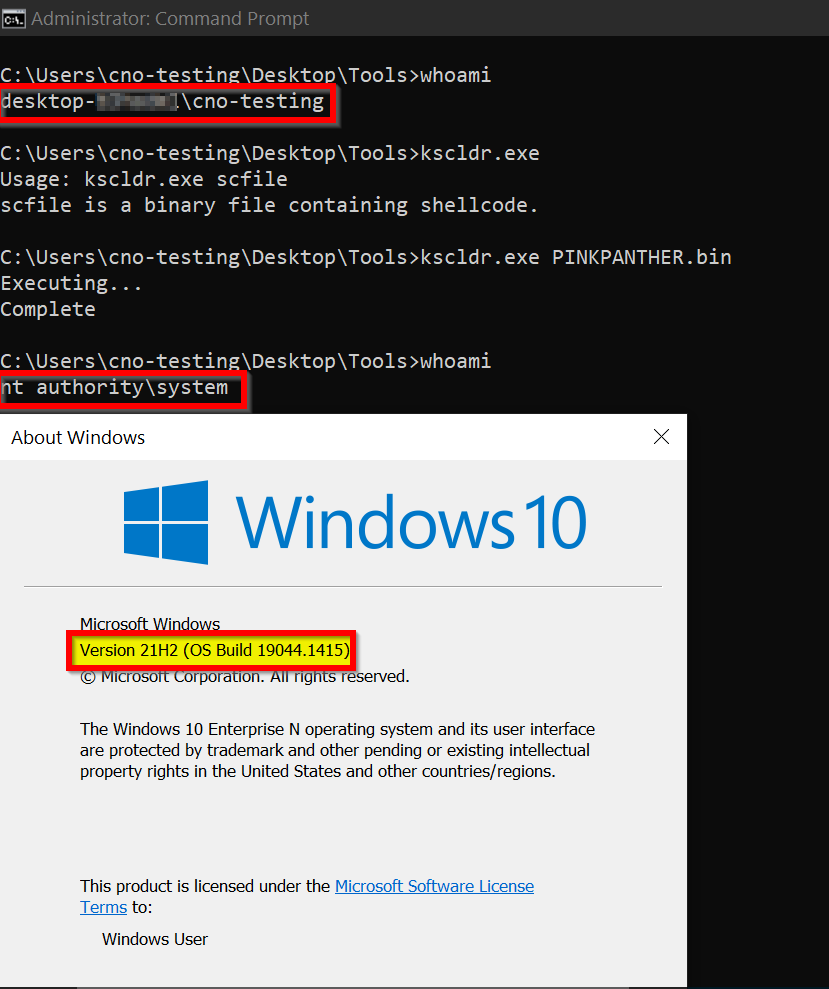
PINKPANTHER
 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
binary-exploitationpayload-developmentpost-exploitation+2
516
winterknife/pinkpantherWindows x64 handcrafted token stealing kernel-mode shellcode
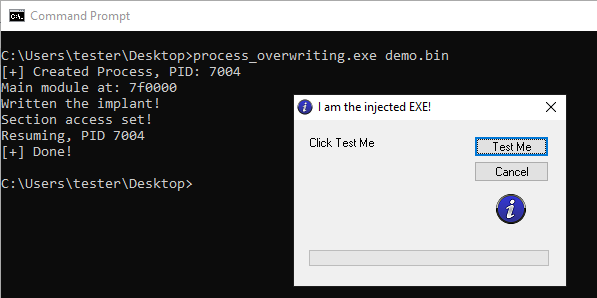 hasherezade/process_overwriting
PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.
 hacksysteam/cve-2023-21608
Proof-of-concept exploit for CVE-2023-21608, a Use-After-Free vulnerability in Adobe Acrobat Reader enabling remote code execution via crafted PDF…
 cryptogenic/ps4-6.20-webkit-code-execution-exploit
A WebKit exploit using CVE-2018-4441 to obtain RCE on PS4 6.20.
 vlad902/hacking-team-windows-kernel-lpe
Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
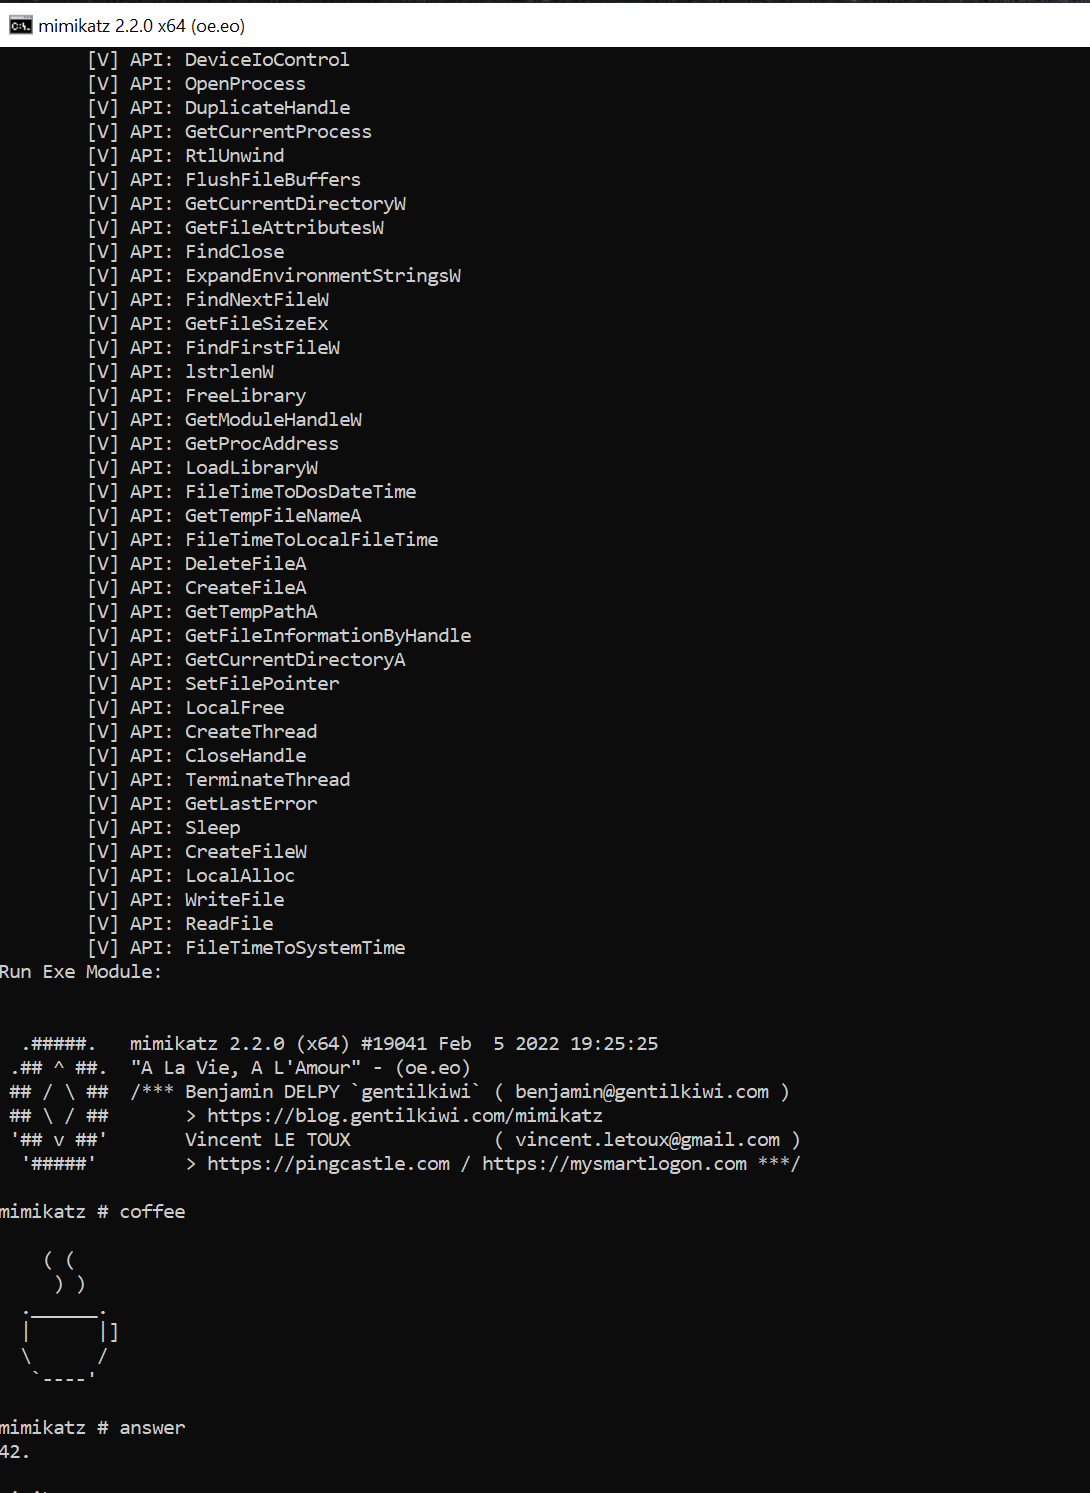 s3cur3th1ssh1t/nim-runpe
A Nim implementation of reflective PE-Loading from memory
 voidsec/exploit-development
Exploit Development - Weaponized Exploit and Proof of Concepts (PoC)
 maxpl0it/cve-2020-0674-exploit
This is an exploit for CVE-2020-0674 that runs on the x64 version of IE 8, 9, 10, and 11 on Windows 7.
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 po6ix/poc-for-cve-2023-41993
Proof-of-concept exploit for CVE-2023-41993, a WebKit JIT type confusion in Safari. Provides addrof/fakeobj primitives via heap manipulation and…
 anvbis/chrome_v8_ndays
Chrome V8 n-day exploits that I've written.
 hatriot/shellme
simple shellcode generator
 secmob/badkernel
Full exploit of CVE-2016-6754(BadKernel) and slide of SyScan360 2016
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 saelo/cve-2018-4233
Exploit for CVE-2018-4233, a WebKit JIT optimization bug used during Pwn2Own 2018
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API