
CVE-2026-31431
 rvzsec/cve-2026-31431
PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros…
binary-exploitationeducationexploitation+4
4
rvzsec/cve-2026-31431PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros…
 neuschaefer/cve-2016-0728-testbed
A testbed for CVE-2016-0728, a refcount leak/overflow bug in Linux
 ysanatomic/cve-2022-1015
A write-up and LPE PoC of an OOB read and write vulnerability in the Linux Kernel.
 noambouillet/cve-2026-3888
Linux LPE via snap-confine + systemd-tmpfiles, explained in depth
 squirre17/hbp-attack-demo
Linux kernel hbp exploit method demo. (i.e. the degradation version of CVE-2022-42703)
 desertdemons/cve-2025-6018-6019
CVE-2025-6018 CVE-2025-6019 PoC Exploit - Local Privilege Escalation in openSUSE/SUSE Linux Enterprise 15 - PAM bypass + udisks2 XFS race condition…
 chenaotian/cve-2022-25636
Detailed technical analysis and exploit write-up for CVE-2022-25636, a Linux kernel netfilter heap overflow vulnerability enabling local privilege…
 tukru/cve-2021-22555
This repo hosts TUKRU's Linux Privilege Escalation exploit (CVE-2021-22555). It demonstrates gaining root privileges via a vulnerability. Tested on…
 askyeye/cve-2023-0045
PoC and write-up for CVE-2023-0045: bypasses Linux prctl/seccomp Spectre-BTI mitigations using BTB poisoning and Flush+Reload to leak process secrets.
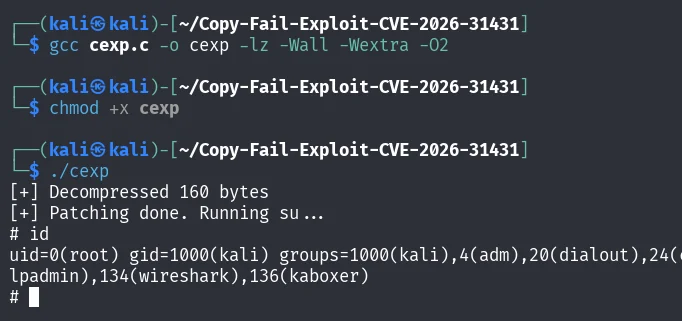 beatbeast007/linux-copyfail-c-version-cve-2026-31431
Clean C implementation of the Copy Fail Linux local privilege escalation exploit (CVE-2026-31431). Uses AF_ALG and splice to overwrite page cache of…
 bytereaper77/dirty-pipe
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…
 dcheng69/cve-2022-0185-case-study
Educational case study and exploit development walkthrough for CVE-2022-0185, a Linux kernel heap-based buffer overflow enabling local privilege…
 lutfifakee-project/cve-2026-31431
CVE-2026-31431 - Linux Kernel Page Cache Vulnerability
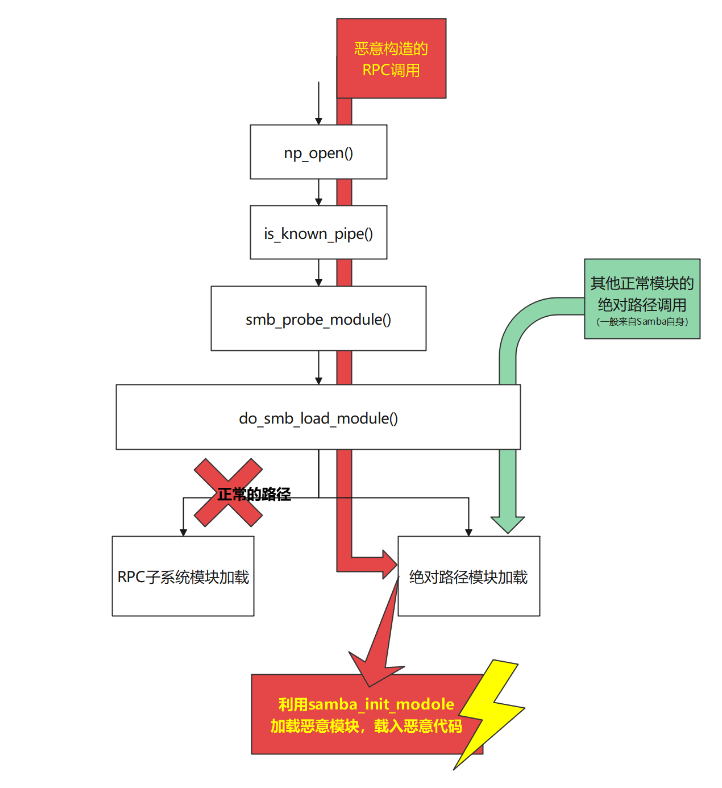 i-rinka/bit-eternalblue-for-macos_linux
Exploit CVE-2017-7494 for Net Security course final Assignment. This would reveal the vulnerability of services that run in administrative priority…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 povzayd/cve-2026-31431
Python exploit demonstrating an in‑memory AF_ALG‑based kernel vulnerability on certain Linux kernels.
 0xfuffm3/cve-2026-31635-dirtydecrypt
Linux kernel local privilege escalation exploit for CVE-2026-31635 that corrupts page cache via RxRPC in-place decryption, overwrites read-only…
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…