CVE-2019-5096-GoAhead-Web-Server-Dos-Exploit

Python exploit for CVE-2019-5096, a use-after-free vulnerability in GoAhead web server's upload handler, causing denial of service via double-free.

Python exploit for CVE-2019-5096, a use-after-free vulnerability in GoAhead web server's upload handler, causing denial of service via double-free.

This is a minimal, educational simulation that demonstrates the _impact_ class of a management-plane parsing RCE (inspired by CVE-2025-20265). It…

Exploit for CVE-2017-7529, a remote integer overflow vulnerability in Nginx, enabling denial of service or potential code execution.

Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…

POC for RCE vulnerability in ParseExcel library, and ParseXLSX too, as a depending library

Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.

Proof-of-concept exploit for CVE-2025-55188 demonstrating arbitrary file write in 7-Zip via symlink path traversal, with escalation to arbitrary code…

Proof-of-concept exploit for CVE-2026-14382, a high-severity ANGLE vulnerability in Chromium, with 32-bit and AArch64 PoCs achieving program counter…

Proof-of-concept exploit for CVE-2016-9079 targeting Firefox on Ubuntu x64, demonstrating a use-after-free vulnerability in the SVG animation…

Unauthenticated RCE exploit for Fantec MWiD25-DS

Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…

Proof-of-concept exploit for CVE-2026-85046 in Chrome 152.0.7977.75, demonstrating type confusion in sort() to achieve arbitrary code execution via a…

Demonstrates a local code execution exploit for Foxit PDF Reader via XFA-based PDFs, with step-by-step attack reproduction and extension to related…

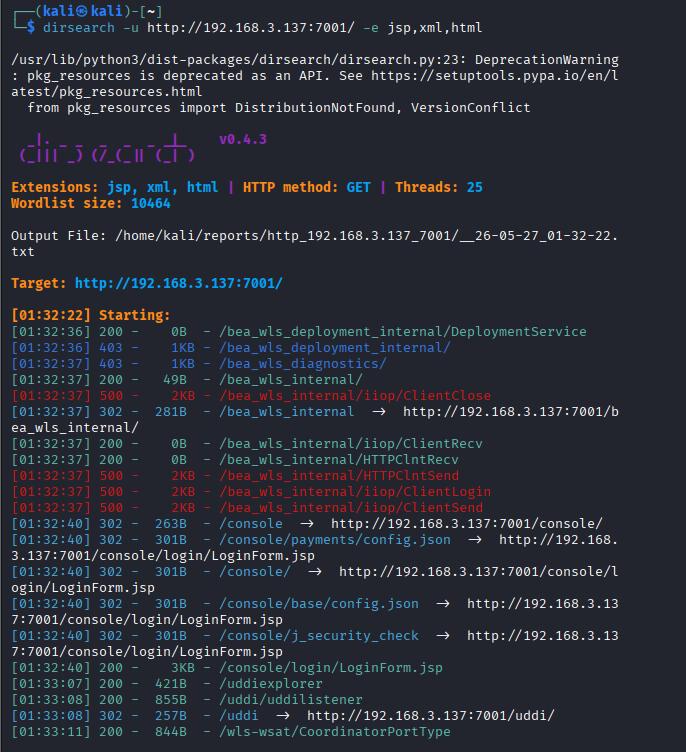
Step-by-step lab guide for exploiting CVE-2017-10271 (WebLogic XMLDecoder deserialization RCE) with manual payload construction, blind RCE bypass,…

Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…

Pre-authentication Remote Code Execution exploit for TP-Link Omada ER605 router via DDNS client daemon (cmxddnsd)

Proof-of-concept remote code execution exploit for Safari 11.0.3 on macOS 10.13.3, leveraging a WebAssembly section vulnerability with heap spray and…

Proof-of-concept exploit for a buffer overflow vulnerability in Tenda AC8v4 router firmware (V16.03.34.09) via the SetNetControlList endpoint,…