
patching
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
binary-analysisbinary-exploitationdebuggers+8
1.3k
gaasedelen/patchingAn Interactive Binary Patching Plugin for IDA Pro
 kitsuneshade/winrar-exploit-tool---rust-edition
A high-performance, memory-safe implementation of the WinRAR CVE-2025-8088 exploit tool, rewritten in Rust for better reliability and performance.
 dennisdgr/cve-2026-31431-poc
An adapted version of the copy fail exploit to use parameters instead of dropping you into a root shell
 jaychouzzk/cve-2019-1388
Proof-of-concept exploit for CVE-2019-1388, a Windows UAC bypass privilege escalation vulnerability. Demonstrates exploitation of the Windows…
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 fortra/cve-2024-6769
Technical writeup and PoC for CVE-2024-6769, chaining DLL hijacking with activation cache poisoning to escalate from medium to high integrity on…
 synacktiv/windows_kernel_shadow_stack
Proof of concepts demonstrating some aspects of the Windows kernel shadow stack mitigation.
 dgndrn/cve-2023-4590
Proof-of-concept exploit for a SEH buffer overflow vulnerability (CVE-2023-4590) in Frhed hex editor v1.6.0. Generates a malicious payload file to…
 swiftloke/fusee-toy
Implementation of CVE-2018-6242 (AKA Fusée Gelée, AKA shofel2)
 realtalk/cve-2013-2094
original cve-2013-2094 exploit and a rewritten version for educational purposes
 secmob/cve-2015-6612
Proof-of-concept exploit for Android CVE-2015-6612, demonstrating a privilege escalation vulnerability with a working PoC for security research and…
 karazajac/charon
CHARON — pre-built PoC for CVE-2026-46333 (Linux ptrace mm==NULL fd theft)
 george0papasotiriou/cve-2026-11105-stack-buffer-overflow-in-custom-base64-decoder
CVE-2026-11105 PoC demonstrating a stack buffer overflow in a custom Base64 decoder; crafted oversized input overwrites stack memory and enables…
 henryisnotavailable/cve-2025-27581
Exploit scripts for CVE-2025-27581
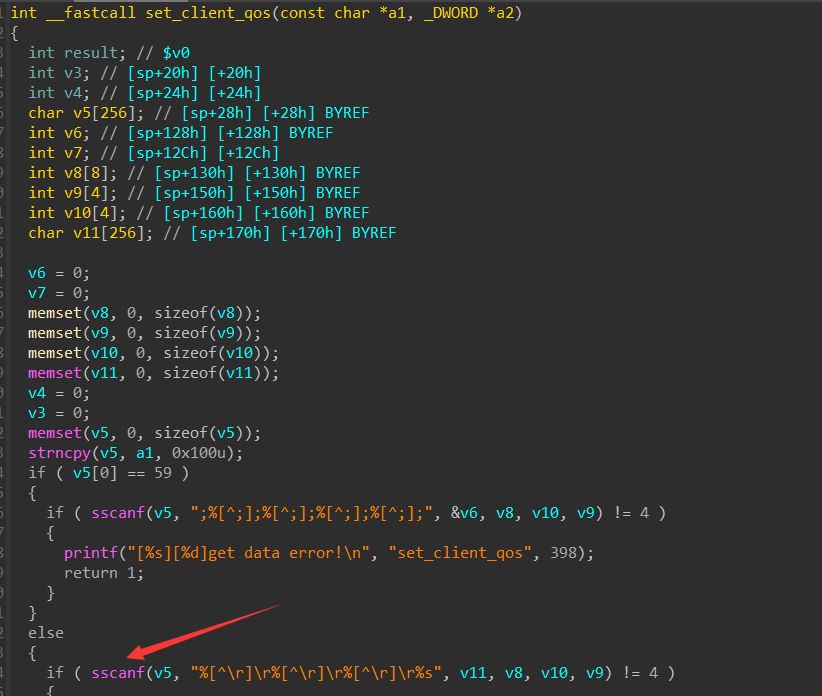 zt20xx/cve-2023-48194
Proof-of-concept exploit for a buffer overflow vulnerability in Tenda AC8v4 router firmware (V16.03.34.09) via the SetNetControlList endpoint,…
 hacker625/cve-2024-22752
EaseUS MobiMover 6.0.5 Build 21620 - Insecure Files and Folders Permissions
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 t3rabyt3-zz/cve-2018-9958--exploit
This vulnerability allows remote attackers to execute arbitrary code on vulnerable installations of Foxit Reader 9.0.1.1049. User interaction is…