
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
600 results
CVE-2024-38063 preview

CVE-2024-38063

GitHubynwarcs/cve-2024-38063

poc for CVE-2024-38063 (RCE in tcpip.sys)
binary-exploitationexploitationfuzzing+3
6892 years ago
Labtainers preview

Labtainers

GitHubmfthomps/labtainers

Labtainers: A Docker-based cyber lab framework
binary-exploitationcryptographyctf+9
3161 month ago
Pixel_GPU_Exploit preview

Pixel_GPU_Exploit

GitHub0x36/pixel_gpu_exploit

Android 14 kernel exploit for Pixel7/8 Pro
android-securitybinary-exploitationeducation+4
5642 years ago
exploits preview

exploits

GitHubhackerhouse-opensource/exploits

exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
binary-exploitationcurated-resourcesembedded-systems-security+7
4708 months ago
shadow preview

shadow

GitHubcensus/shadow

jemalloc heap exploitation framework

binary-exploitationdebuggersexploitation+2
4704 years ago
VMInjector preview

VMInjector

GitHubhzphreak/vminjector

DLL Injection tool to unlock guest VMs
authentication-authorizationbinary-exploitationexploitation+4
23813 years ago
FUD-UUID-Shellcode preview

FUD-UUID-Shellcode

GitHubbl4ckm1rror/fud-uuid-shellcode

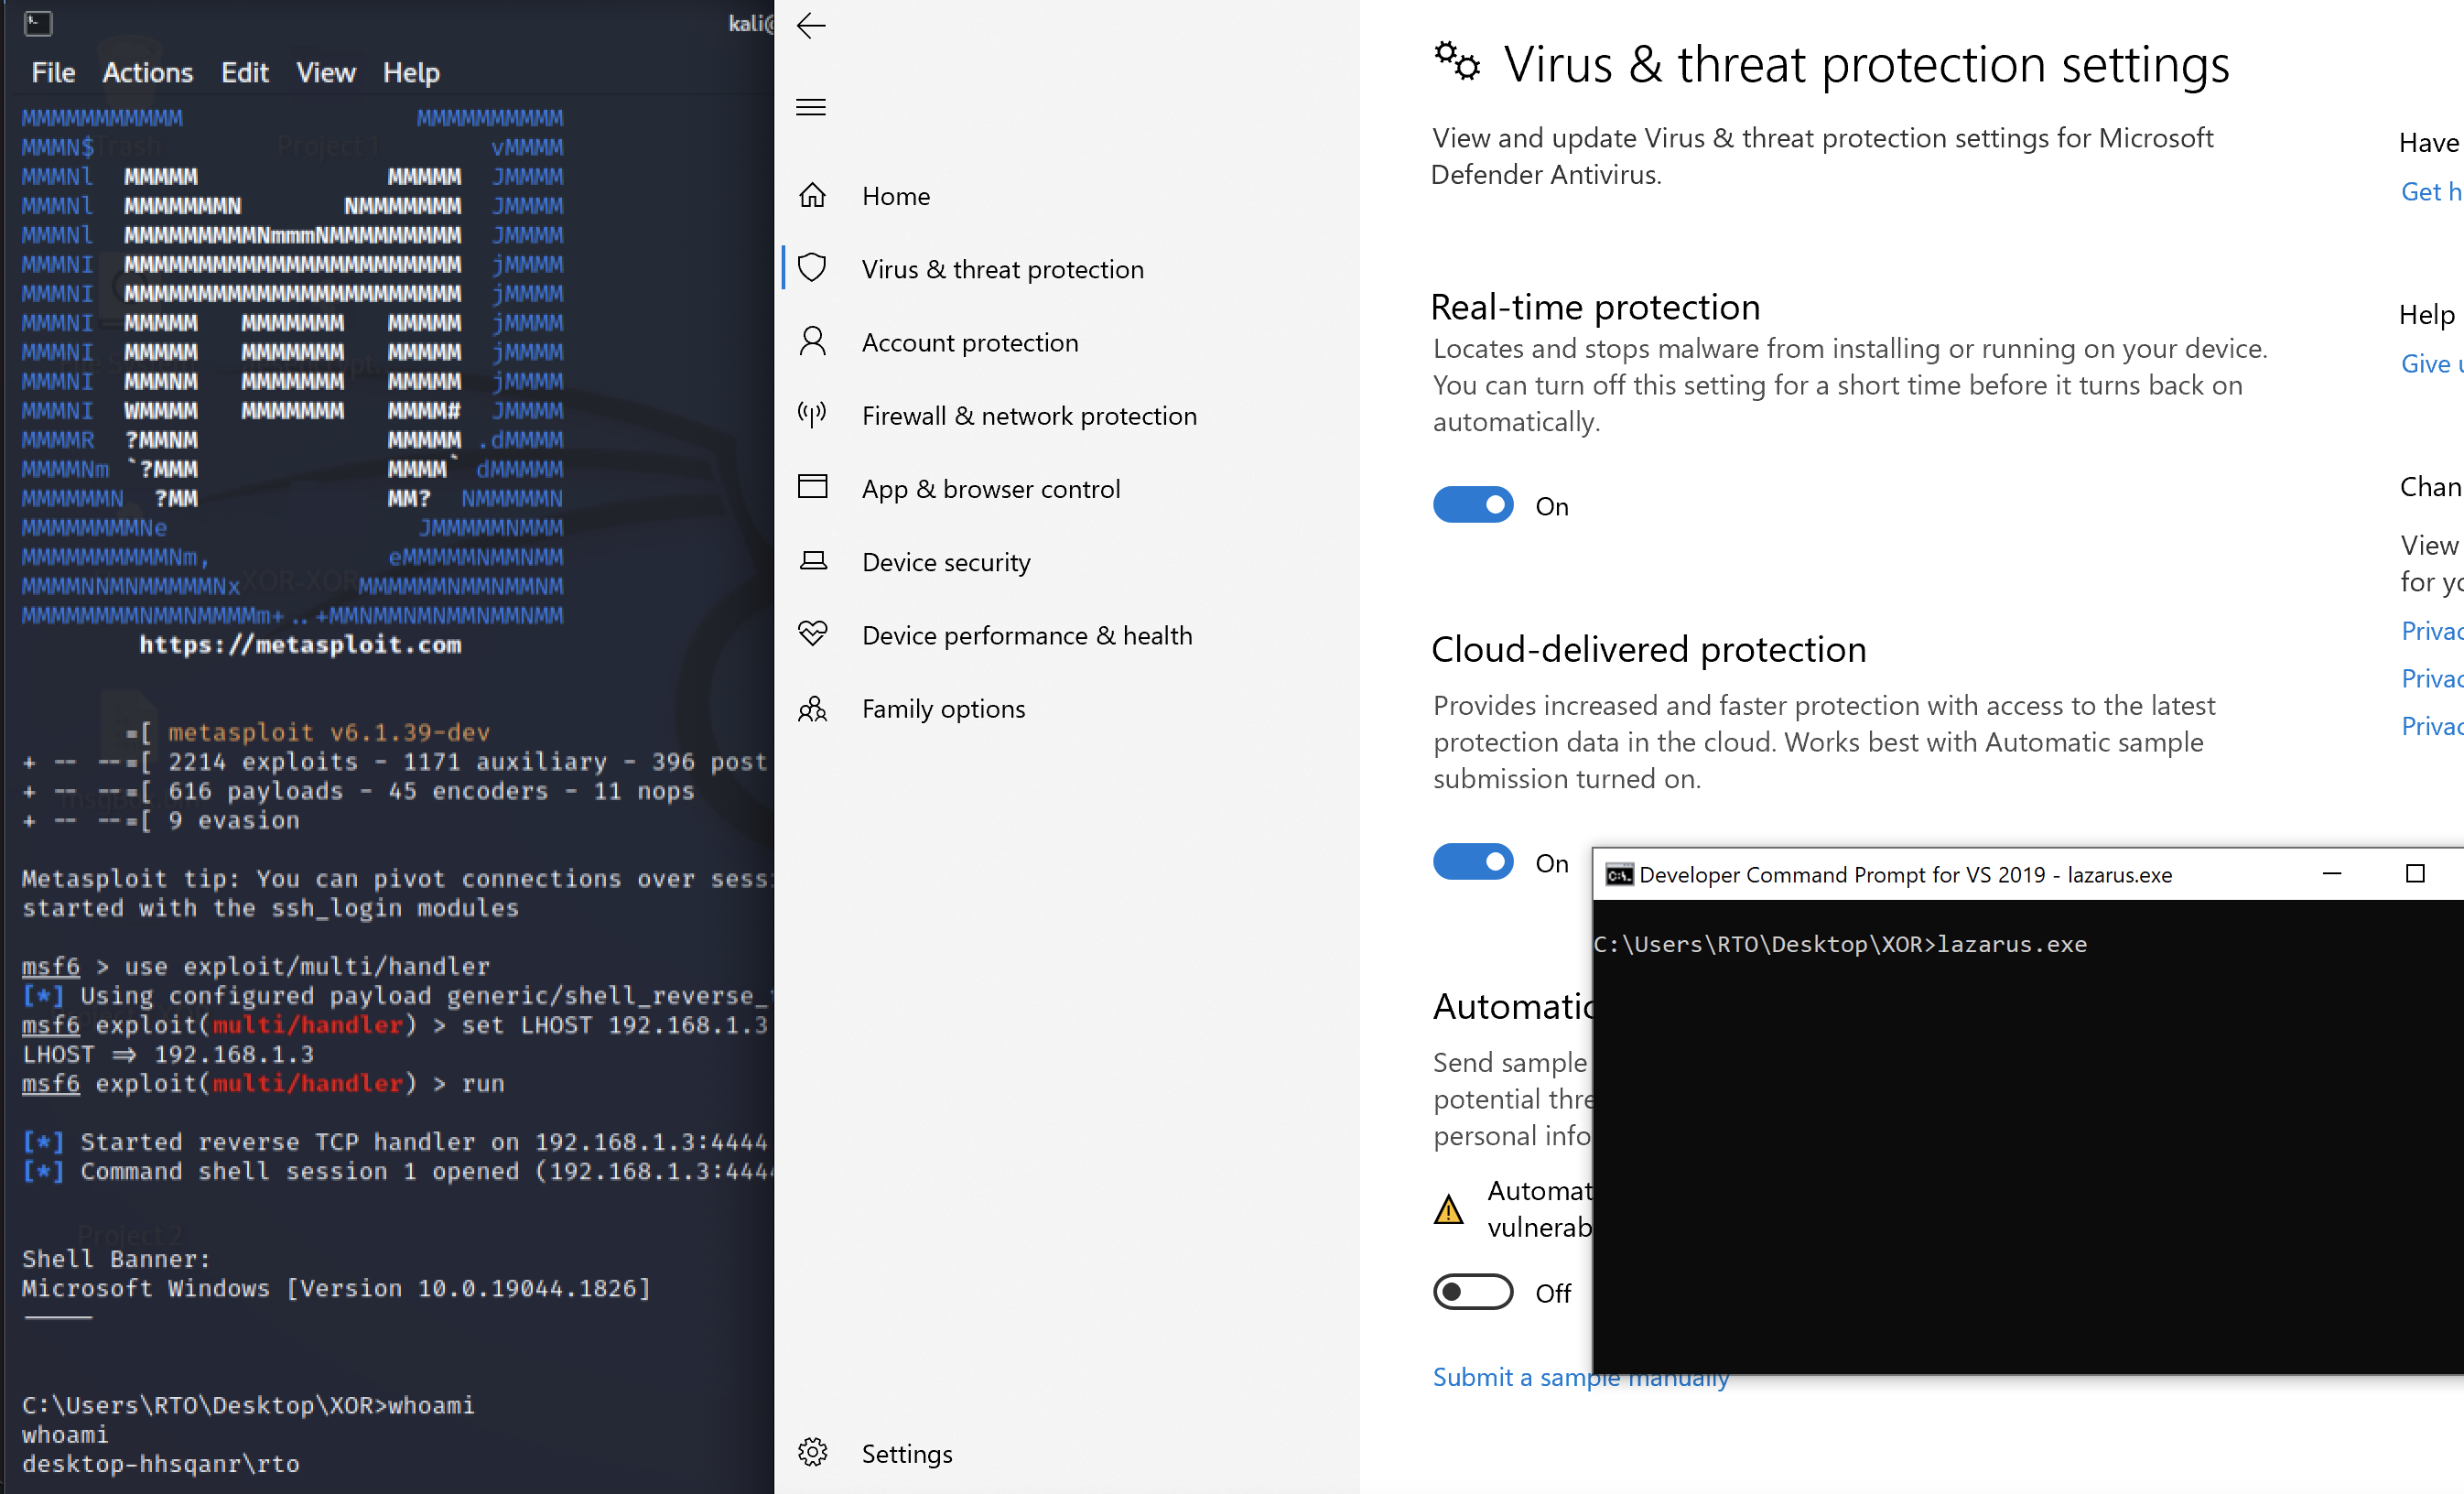
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
binary-exploitationdefensive-toolsexploitation+6
3333 years ago
collateral-damage preview

collateral-damage

GitHubexploits-forsale/collateral-damage

Kernel exploit for Xbox SystemOS using CVE-2024-30088
binary-exploitationexploitationhardware-iot-security+3
5301 year ago
CVE-2026-41089 preview

CVE-2026-41089

GitHub0xabcd01/cve-2026-41089

CVE-2026-41089 PoC — Netlogon CLDAP stack buffer overflow (CVSS 9.8 CRITICAL)
binary-exploitationeducationexploitation+2
2334 months ago
GhostKatz preview

GhostKatz

GitHubrainbowdynamix/ghostkatz

Dump LSASS via physical memory read primitives in vulnerable kernel drivers
binary-exploitationexploitationmemory-forensics+4
3438 months ago
RansomLord preview

RansomLord

GitHubmalvuln/ransomlord

RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
binary-exploitationdefensive-toolsexploitation+4
5151 year ago
MorphAES preview

MorphAES

GitHubcryptolok/morphaes

IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
binary-exploitationexploitationids-ips-evasion+4
3254 years ago
PageTableInjection preview

PageTableInjection

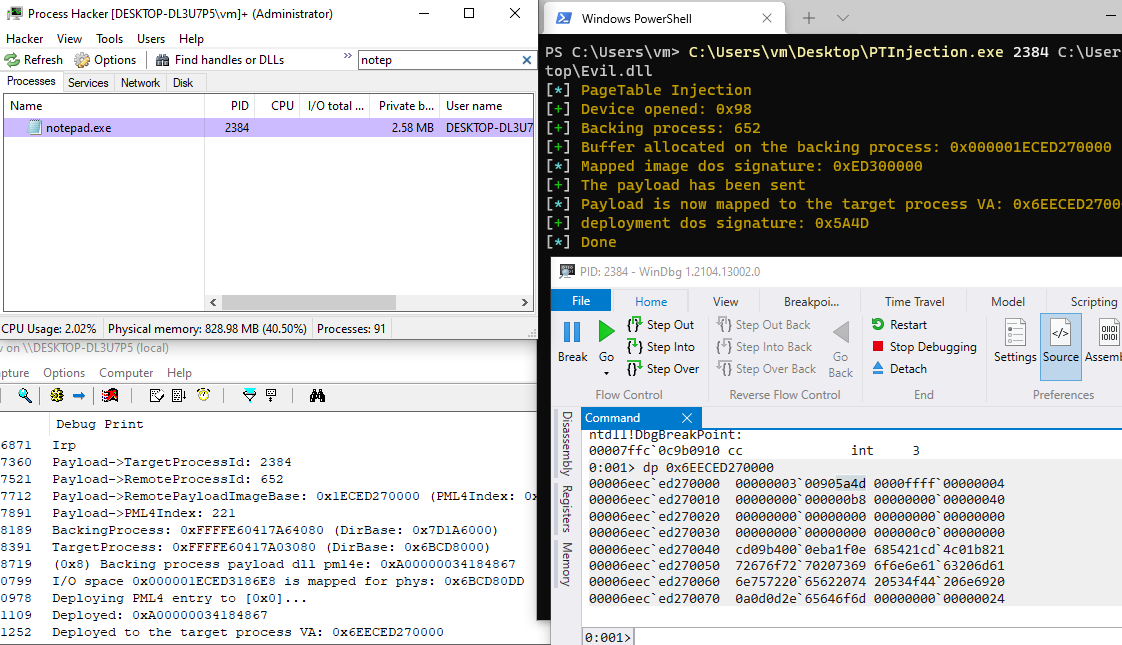
GitHubkkent030315/pagetableinjection

Code Injection, Inject malicious payload via pagetables pml4.
binary-exploitationexploitationmemory-forensics
2485 years ago
CVE-2018-17182 preview

CVE-2018-17182

GitHubjas502n/cve-2018-17182

Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…
binary-exploitationexploitationmemory-forensics+2
1308 years ago
LdrShuffle preview

LdrShuffle

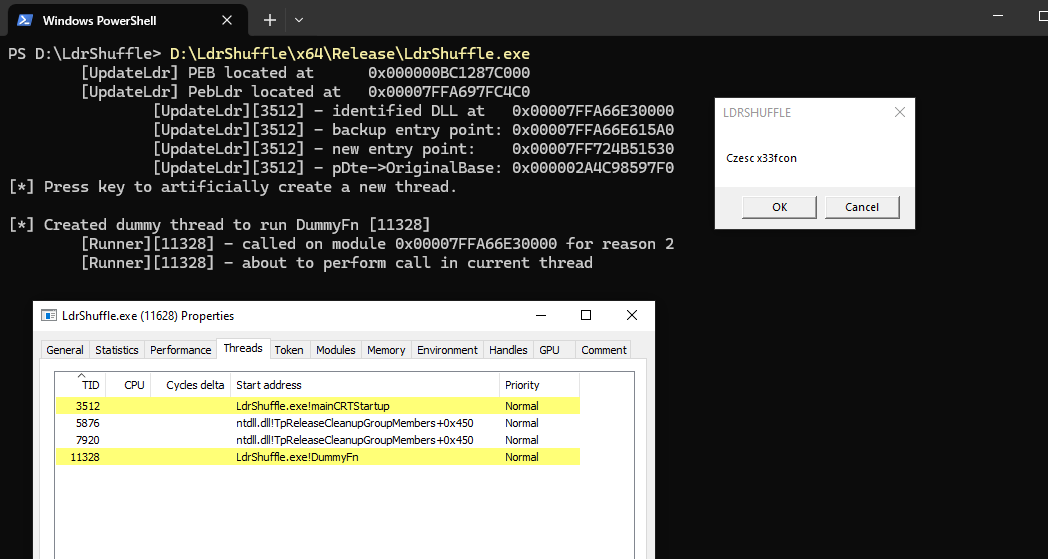
GitHubrwxstoned/ldrshuffle

Code execution/injection technique using DLL PEB module structure manipulation
binary-exploitationcode-analysisexploitation+6
2931 year ago
CVE-2022-37969 preview

CVE-2022-37969

GitHubfortra/cve-2022-37969

Proof-of-concept exploit for CVE-2022-37969, a Windows Common Log File System driver local privilege escalation. Demonstrates heap spray, token…
binary-exploitationexploitationmemory-forensics+2
1343 years ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

binary-exploitationexploitationlateral-movement+7
2191 month ago
ROPInjector preview

ROPInjector

GitHubgpoulios/ropinjector

Patching ROP-encoded shellcodes into PEs

binary-analysisbinary-exploitationexploitation+7
1878 years ago
Previous1…345…34Next