

CVE-2018-4878
 mdsecactivebreach/cve-2018-4878
Proof-of-concept exploit for CVE-2018-4878, a Use-After-Free vulnerability in Adobe Flash Player 32-bit, providing a ByteArray object for process…
binary-exploitationexploitationmalware-analysis+3
23
mdsecactivebreach/cve-2018-4878Proof-of-concept exploit for CVE-2018-4878, a Use-After-Free vulnerability in Adobe Flash Player 32-bit, providing a ByteArray object for process…
 brianwrf/cve-2017-4878-samples
CVE-2017-4878 Samples - http://blog.talosintelligence.com/2018/02/group-123-goes-wild.html
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
 lan1oc/cve-2023-34312-exp
Reproduction of CVE-2023-34312 using two malicious DLL files to exploit QQ and TIM messaging applications for security research and testing.
 xm0kht4r/cve-2025-7771
A simple PoC demonstrating the vulnerability in the ThrottleStop.sys driver, showcasing arbitrary physical memory read and write capabilities, as…
 simoesctt/ctt-microsoft-office-ole-manifold-bypass-cve-2026-21509
Exploit for CVE-2026-21509, a Microsoft Office OLE validation bypass using a speculative race-condition technique to evade AMSI/EDR and achieve code…
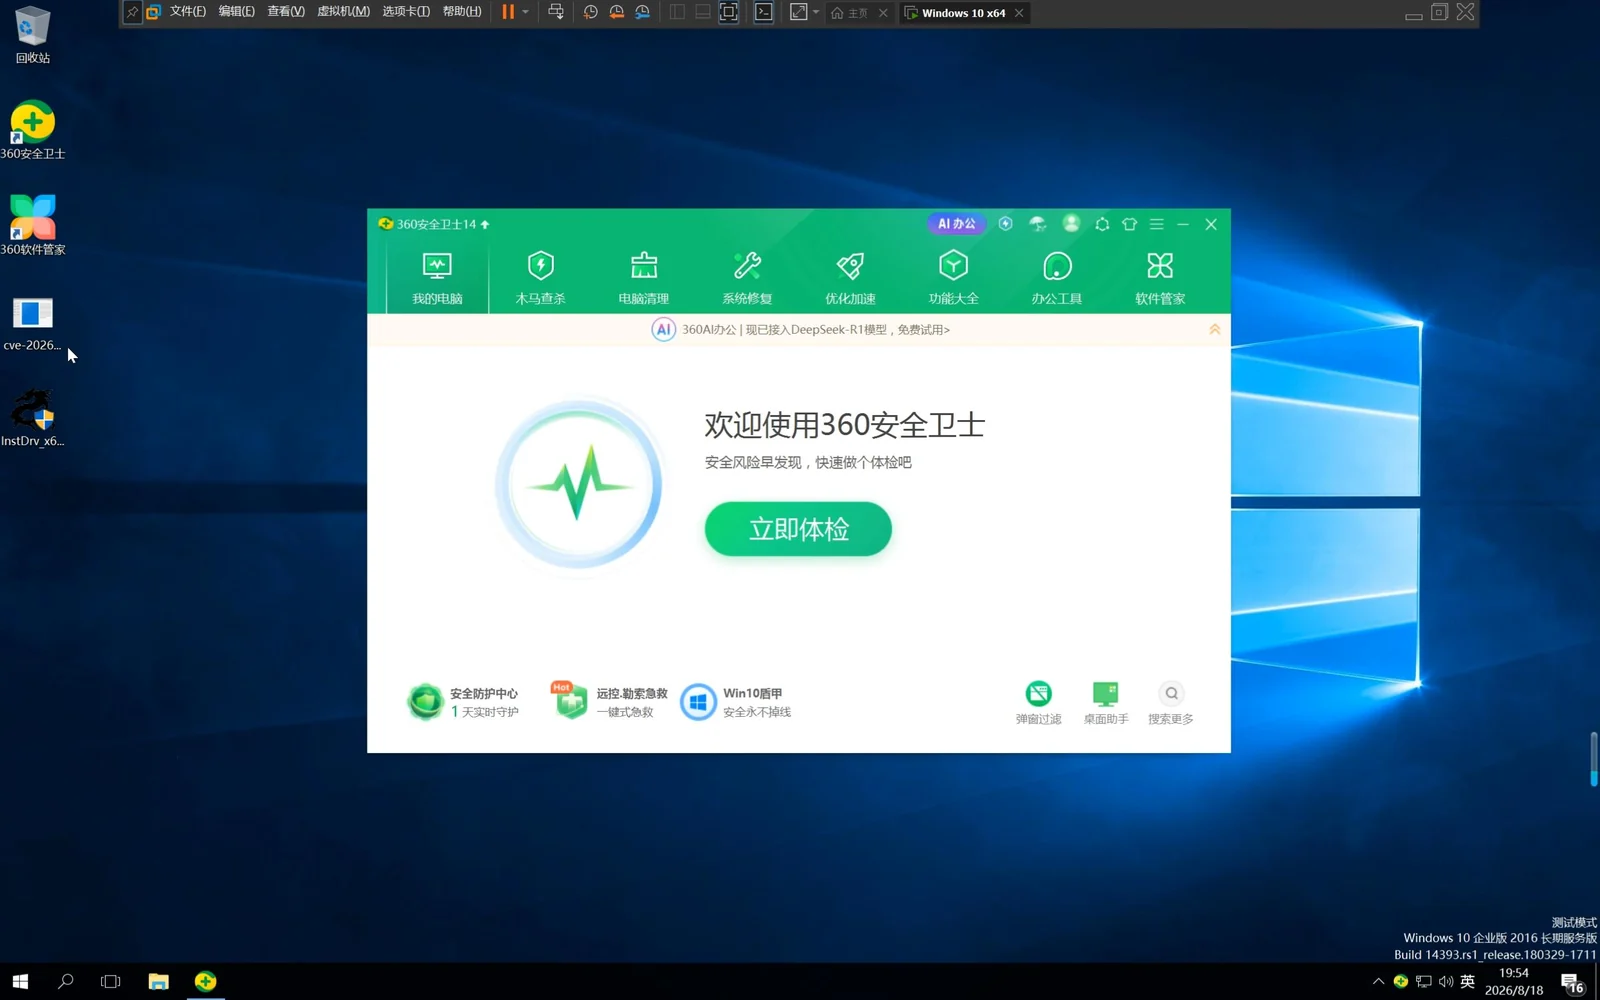 gongchuang1089/edrkiller
Use cve-2026-36425 killer edr,360 can killer
 pexlexity/winrar-cve-2025-8088-path-traversal-poc
Proof-of-Concept for CVE-2025-8088 vulnerability in WinRAR (path traversal via ADS)
 sexyshoelessgodofwar/cve-2025-47256
Stack overflow in LibXMP
 alex-acero-security/cve-2025-20260-poc
Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…
 nasawyer7/iobitmalwarefighterdll
(0 day) CVE-2026-37333 LPE I found in IObit Malware Fighter v. 13.2.0.
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
 rajauzairabdullah/cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a remote code execution vulnerability in Windows Notepad, demonstrating file-based trigger and execution…
 osmancanvural/cve-2026-21436
Proof-of-concept exploit for CVE-2026-21436, demonstrating path traversal in Solus OS eopkg package manager allowing arbitrary file write during…
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 secunnix/cve-2024-27518
SUPERAntiSpyware Professional X <=10.0.1264 LPE Vulnerability PoC
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.