
bdapiutil-bydov
 ull0a/bdapiutil-bydov
C++ Windows research tool for studying the BdApiUtil64.sys vulnerable driver and CVE-2024-51324
binary-exploitationdefensive-toolsexploitation+4
ull0a/bdapiutil-bydovC++ Windows research tool for studying the BdApiUtil64.sys vulnerable driver and CVE-2024-51324
 ektoplasma/ezwinrar
Python tool exploiting CVE-2018-20250 found by CheckPoint folks
 redcrazyghost/cve-2026-42945
Go-based exploit tool for CVE-2026-42945 (nginx HTTP/2) with detection, crash probing, command execution, and reverse shell capabilities for…
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
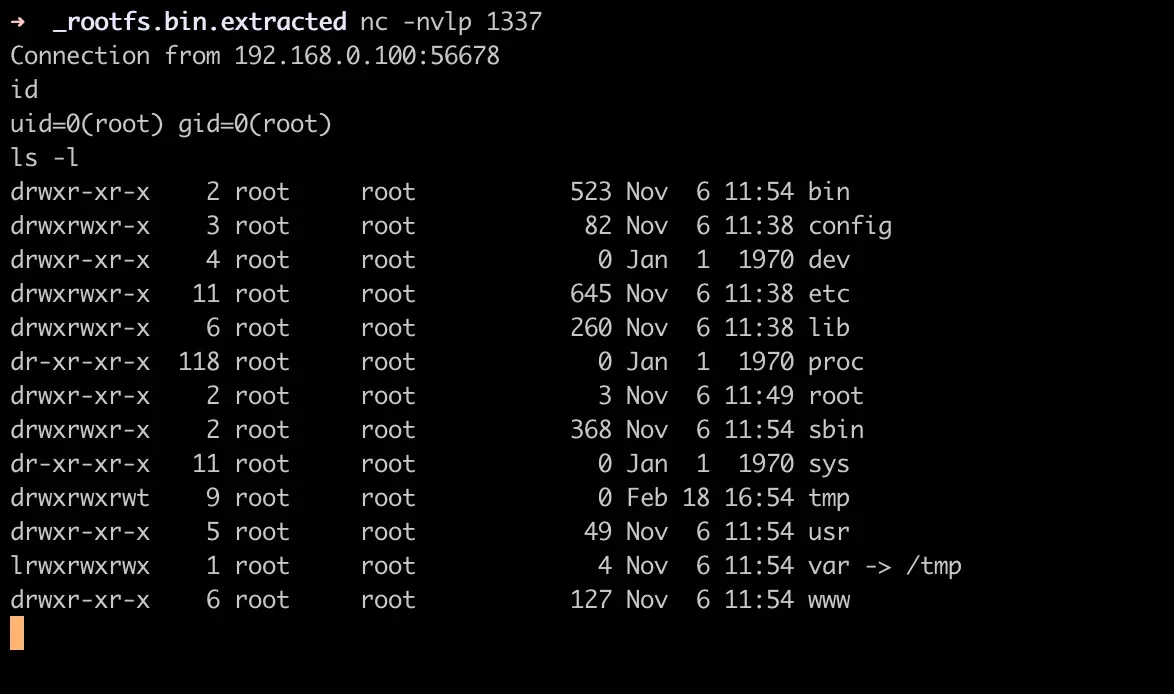 ii4gsp/cve-2026-1457
Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…
 chanbin/cve-2017-11882
Microsoft Equation 3.0/Convert python2 to python3
 timsonner/cve-2025-49144-research
Research tool for CVE-2025-49144, providing vulnerability analysis and exploitation capabilities for security testing and assessment.
 tamagaft/cve-2019-17662
Golang implementation of CVE-2019-17662 TinyVNC Arbitrary File Read leading to Authentication Bypass Exploit
 cyberdesu/remote-buffer-overflow-cve-2003-0172
Python-based remote buffer overflow exploit targeting CVE-2003-0172. Accepts host and port arguments to deliver a payload for penetration testing and…
 imv7/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387, a remote code execution vulnerability. Provides a targeted exploitation tool for security testing and…
 secwiki/linux-kernel-exploits
linux-kernel-exploits Linux平台提权漏洞集合
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 exploits-forsale/prefetch-tool
Windows KASLR bypass using prefetch side-channel
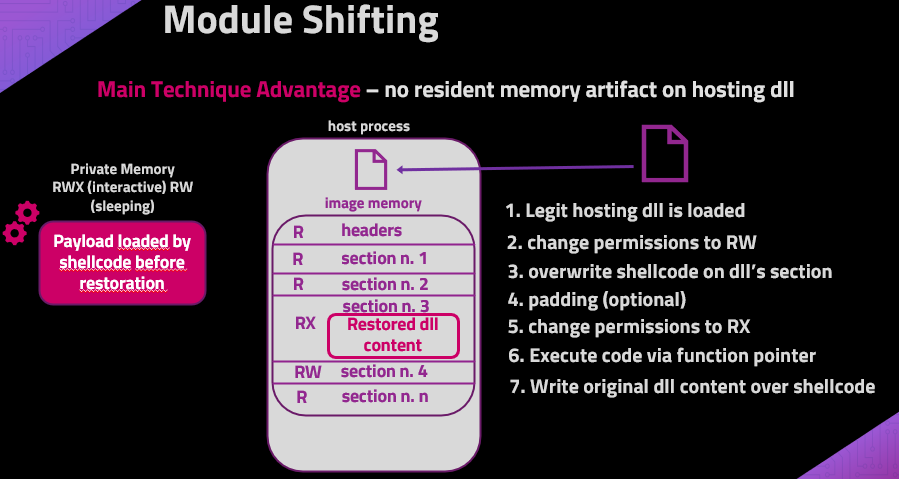 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 bazad/physmem
Local privilege escalation through macOS 10.12.1 via CVE-2016-1825 or CVE-2016-7617.
 obamalaolu/cve-2025-27591
CVE-2025-27591
 wudicainiao/cve-2021-4034
CVE-2021-4034 for single commcand