

CVE-2021-3156
 blasty/cve-2021-3156
Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
binary-exploitationexploitationpayload-development+3
1.0k
blasty/cve-2021-3156Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
 felix-pb/kfd
kfd, short for kernel file descriptor, is a project to read and write kernel memory on Apple devices.
 mcw0/poc
Issues has been disabled for these PoC's, as they are simply PoC, Public Domain and unsupported.
 eugnis/spectre-attack
Example of using revealed "Spectre" exploit (CVE-2017-5753 and CVE-2017-5715)
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
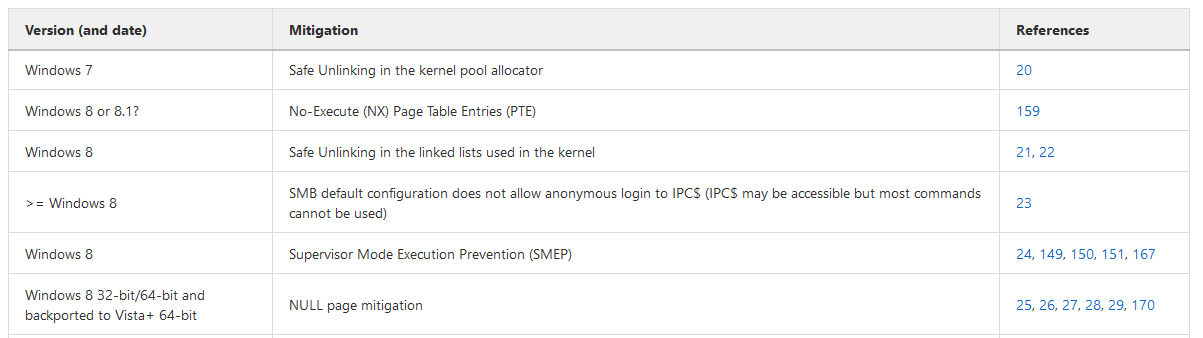 nccgroup/exploit_mitigations
Knowledge base of exploit mitigations available across numerous operating systems, architectures and applications and versions.
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
 laginimaineb/extractkeymaster
Exploit that extracts Qualcomm's KeyMaster keys using CVE-2015-6639 and CVE-2016-2431
 0xdea/exploits
Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…
 alexisahmed/cve-2022-0847-dirtypipe-exploits
A collection of exploits and documentation that can be used to exploit the Linux Dirty Pipe vulnerability.
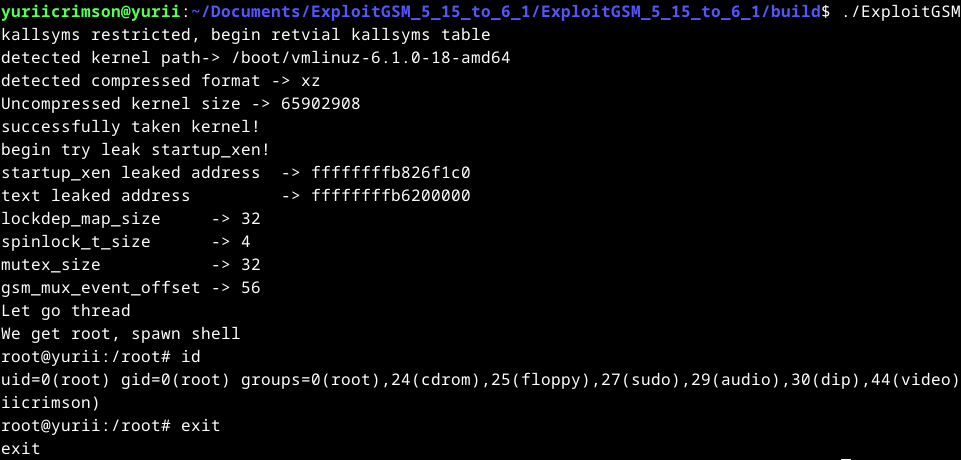 yuriicrimson/exploitgsm
Exploit for 6.4 - 6.5 kernels and another exploit for 5.15 - 6.5
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
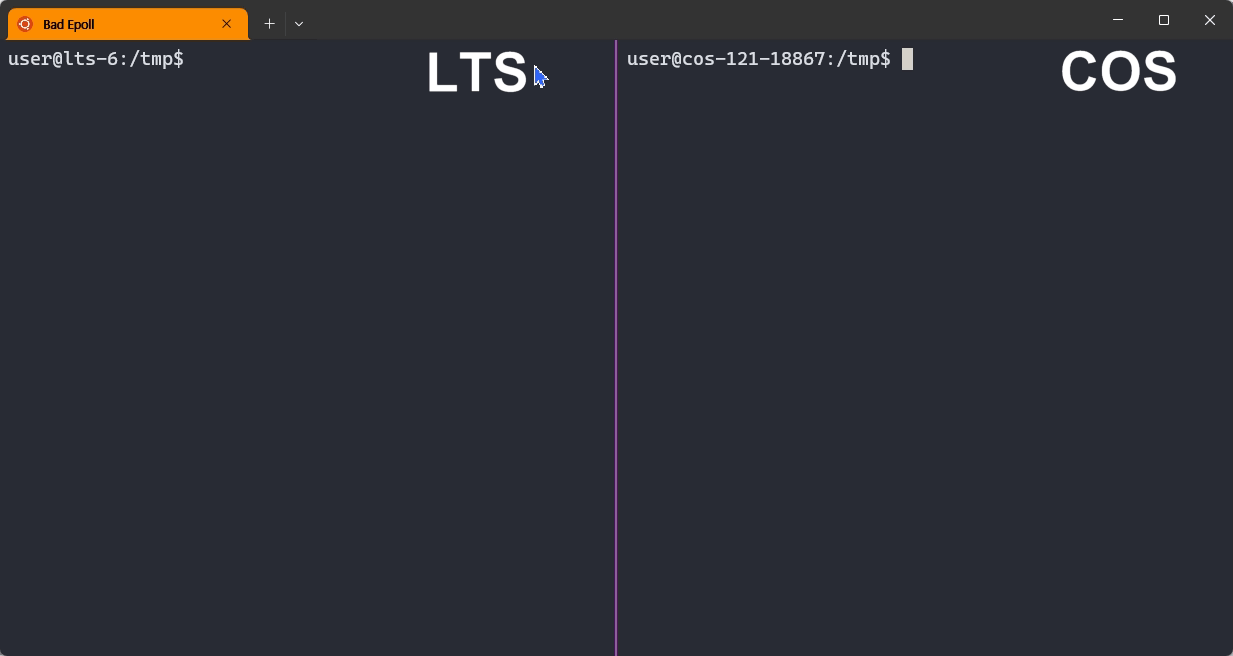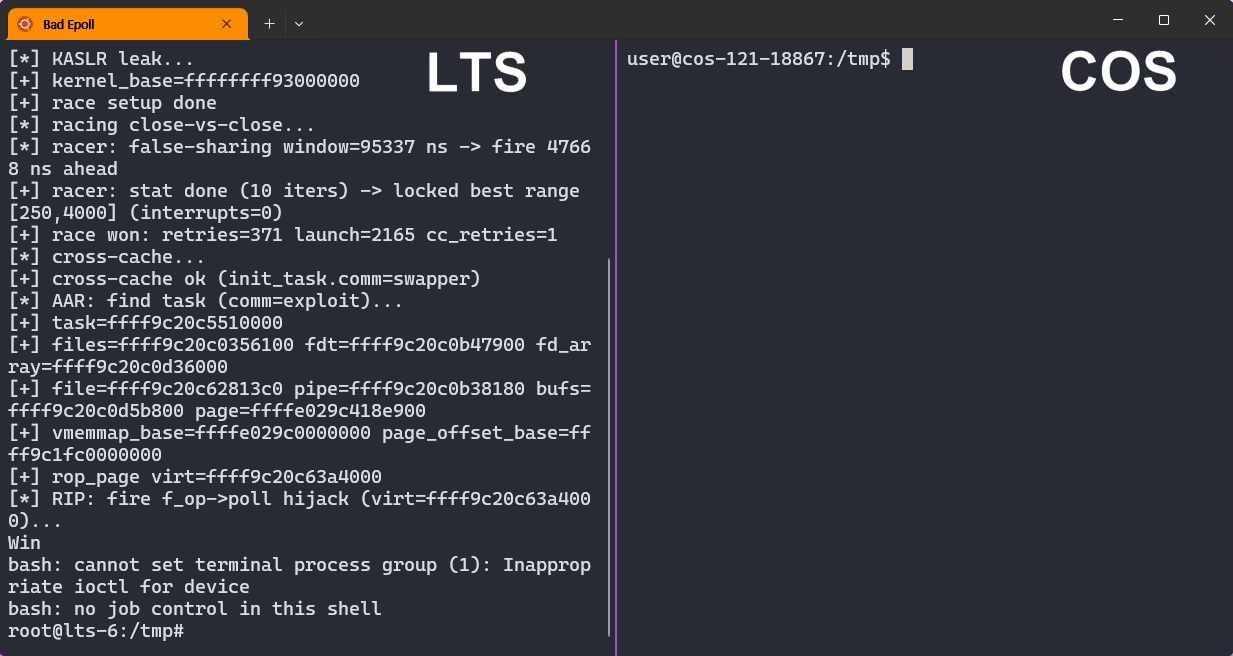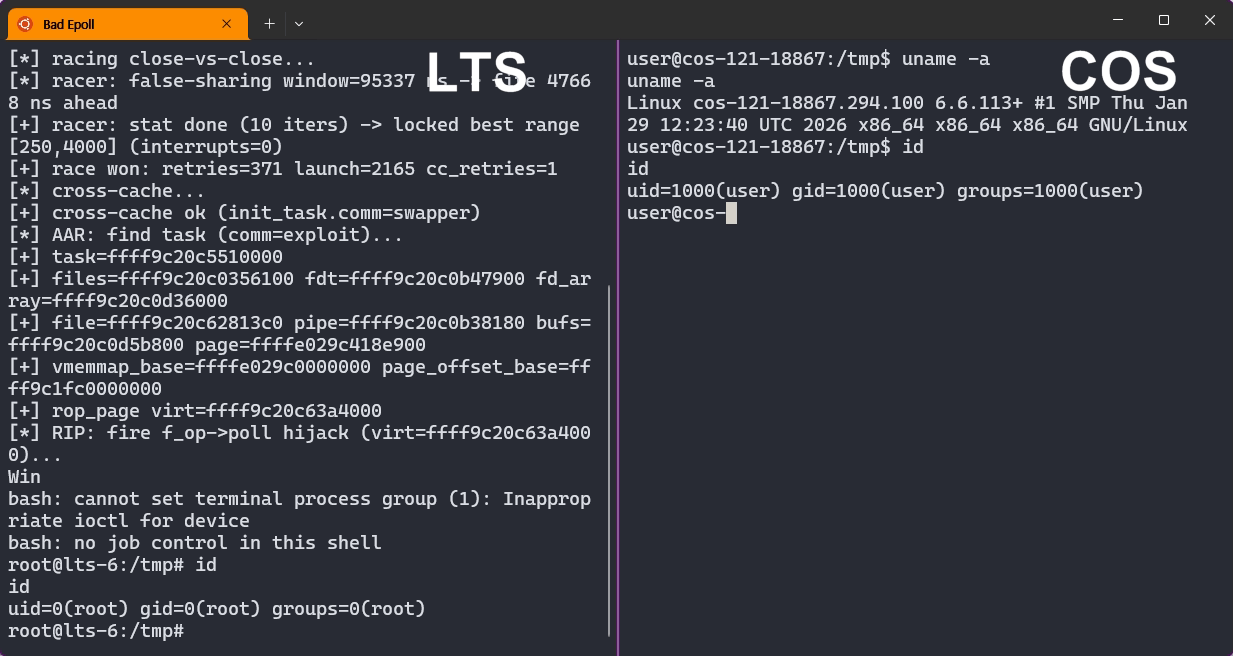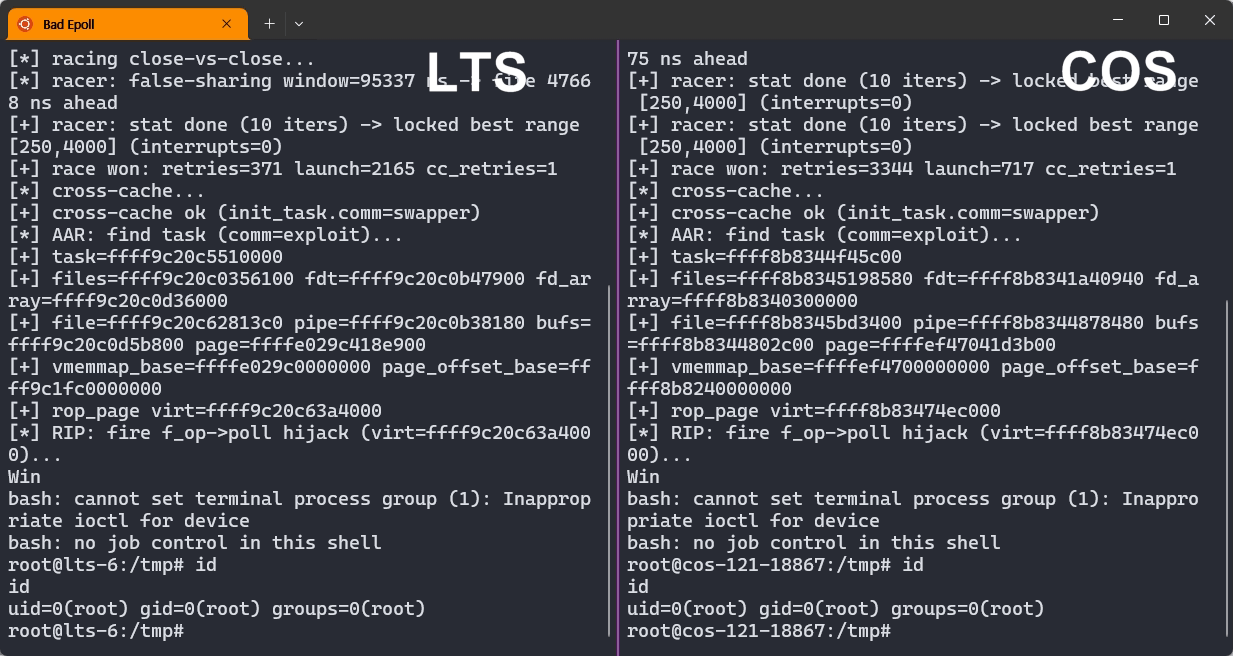 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 nac-l/mergen
Deobfuscation via optimization with usage of LLVM IR and parsing assembly.
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 phoenhex/files
Curated repository of exploits, proof-of-concept code, and vulnerability research presentations from the phoenhex team, focused on binary…