
Koppeling
 monoxgas/koppeling
Adaptive DLL hijacking / dynamic export forwarding
binary-exploitationexploitationpayload-development+1
monoxgas/koppelingAdaptive DLL hijacking / dynamic export forwarding
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
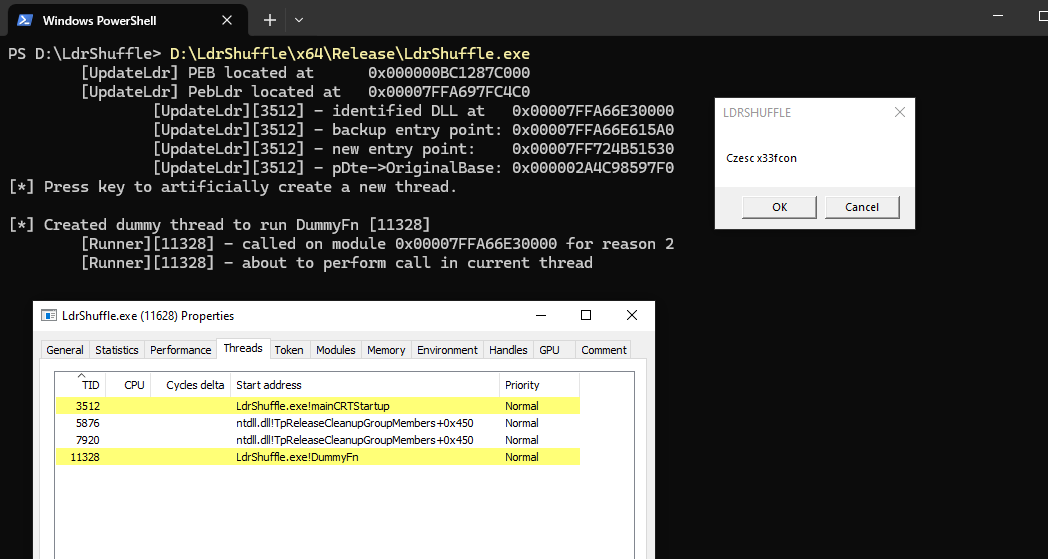 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 klezvirus/koppeling-p
Adaptive DLL hijacking / dynamic export forwarding - EAT preserve
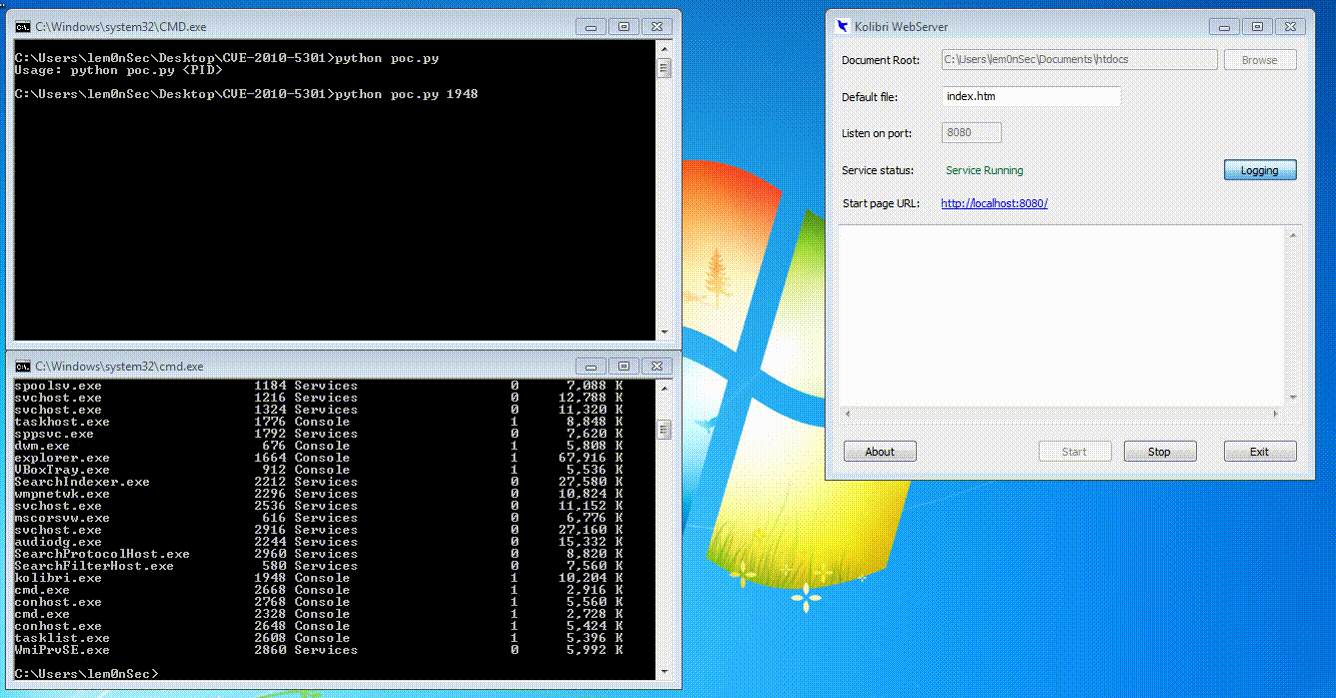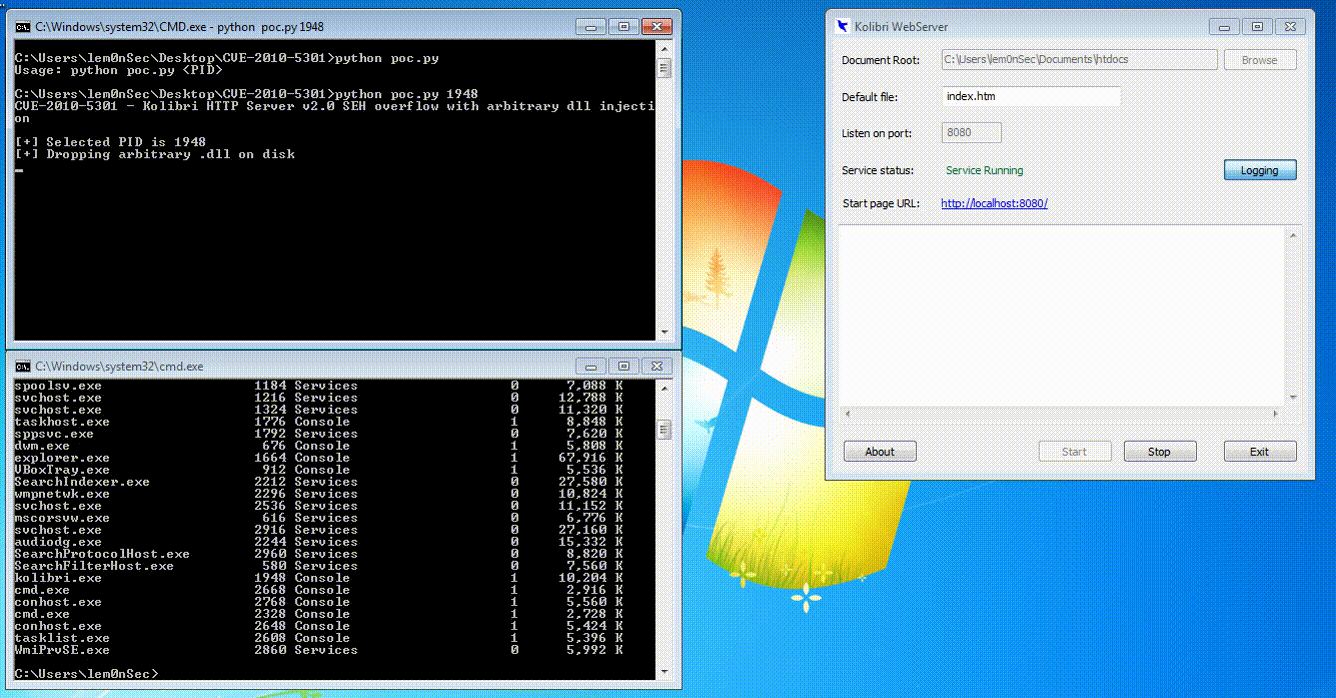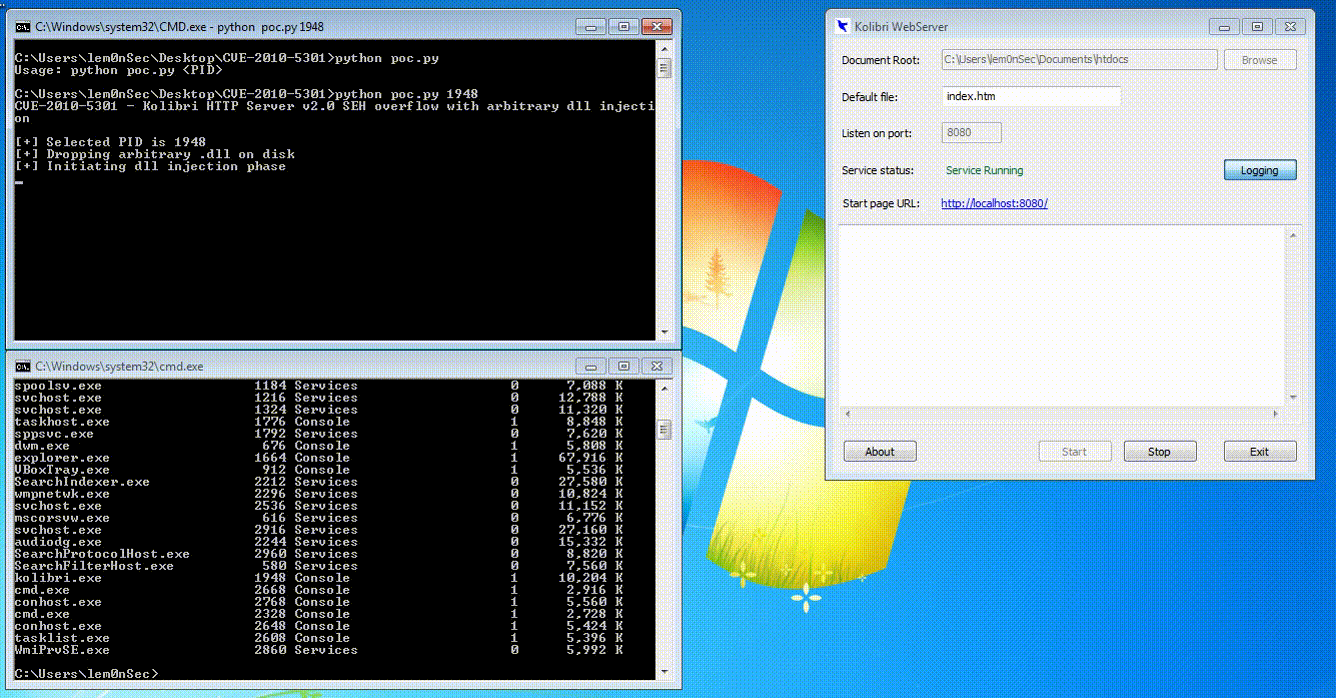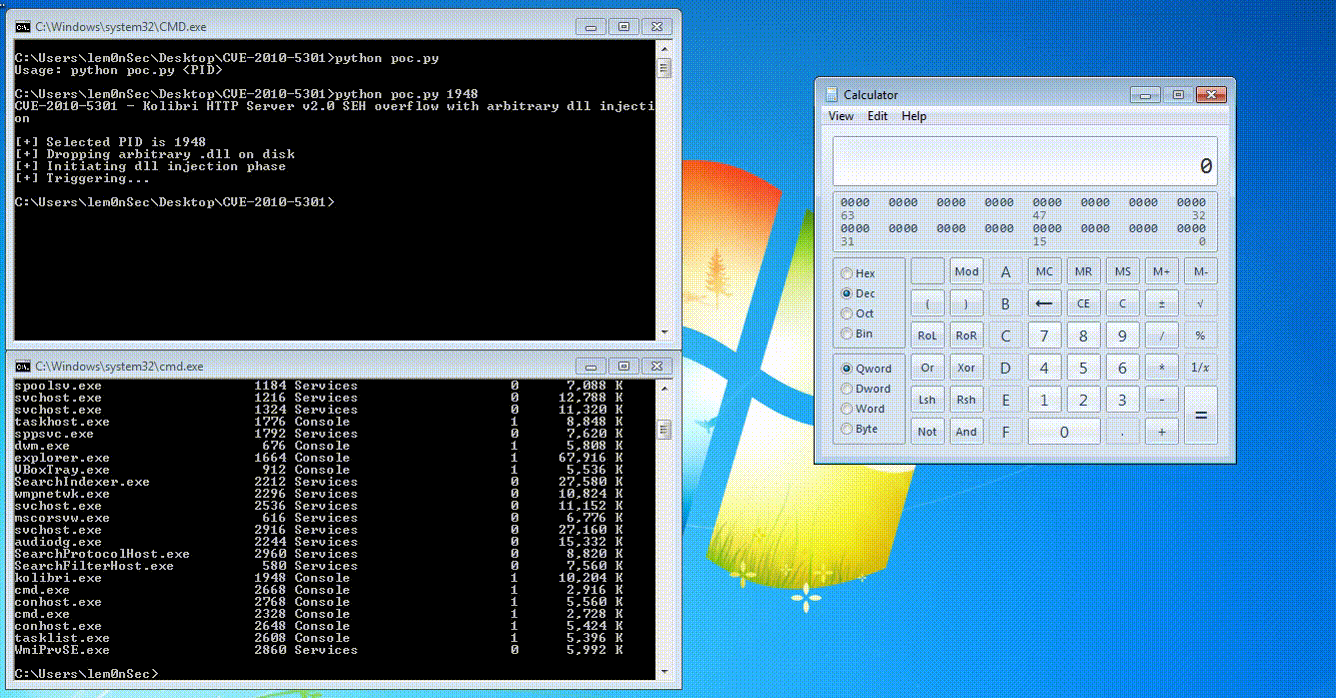 lem0nsec/cve-2010-5301
A proof of concept of an SEH overflow with arbitrary dll injection
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
 evilashz/cve-2021-1675-lpe-exp
PrintNightmare , Local Privilege Escalation of CVE-2021-1675 or CVE-2021-34527
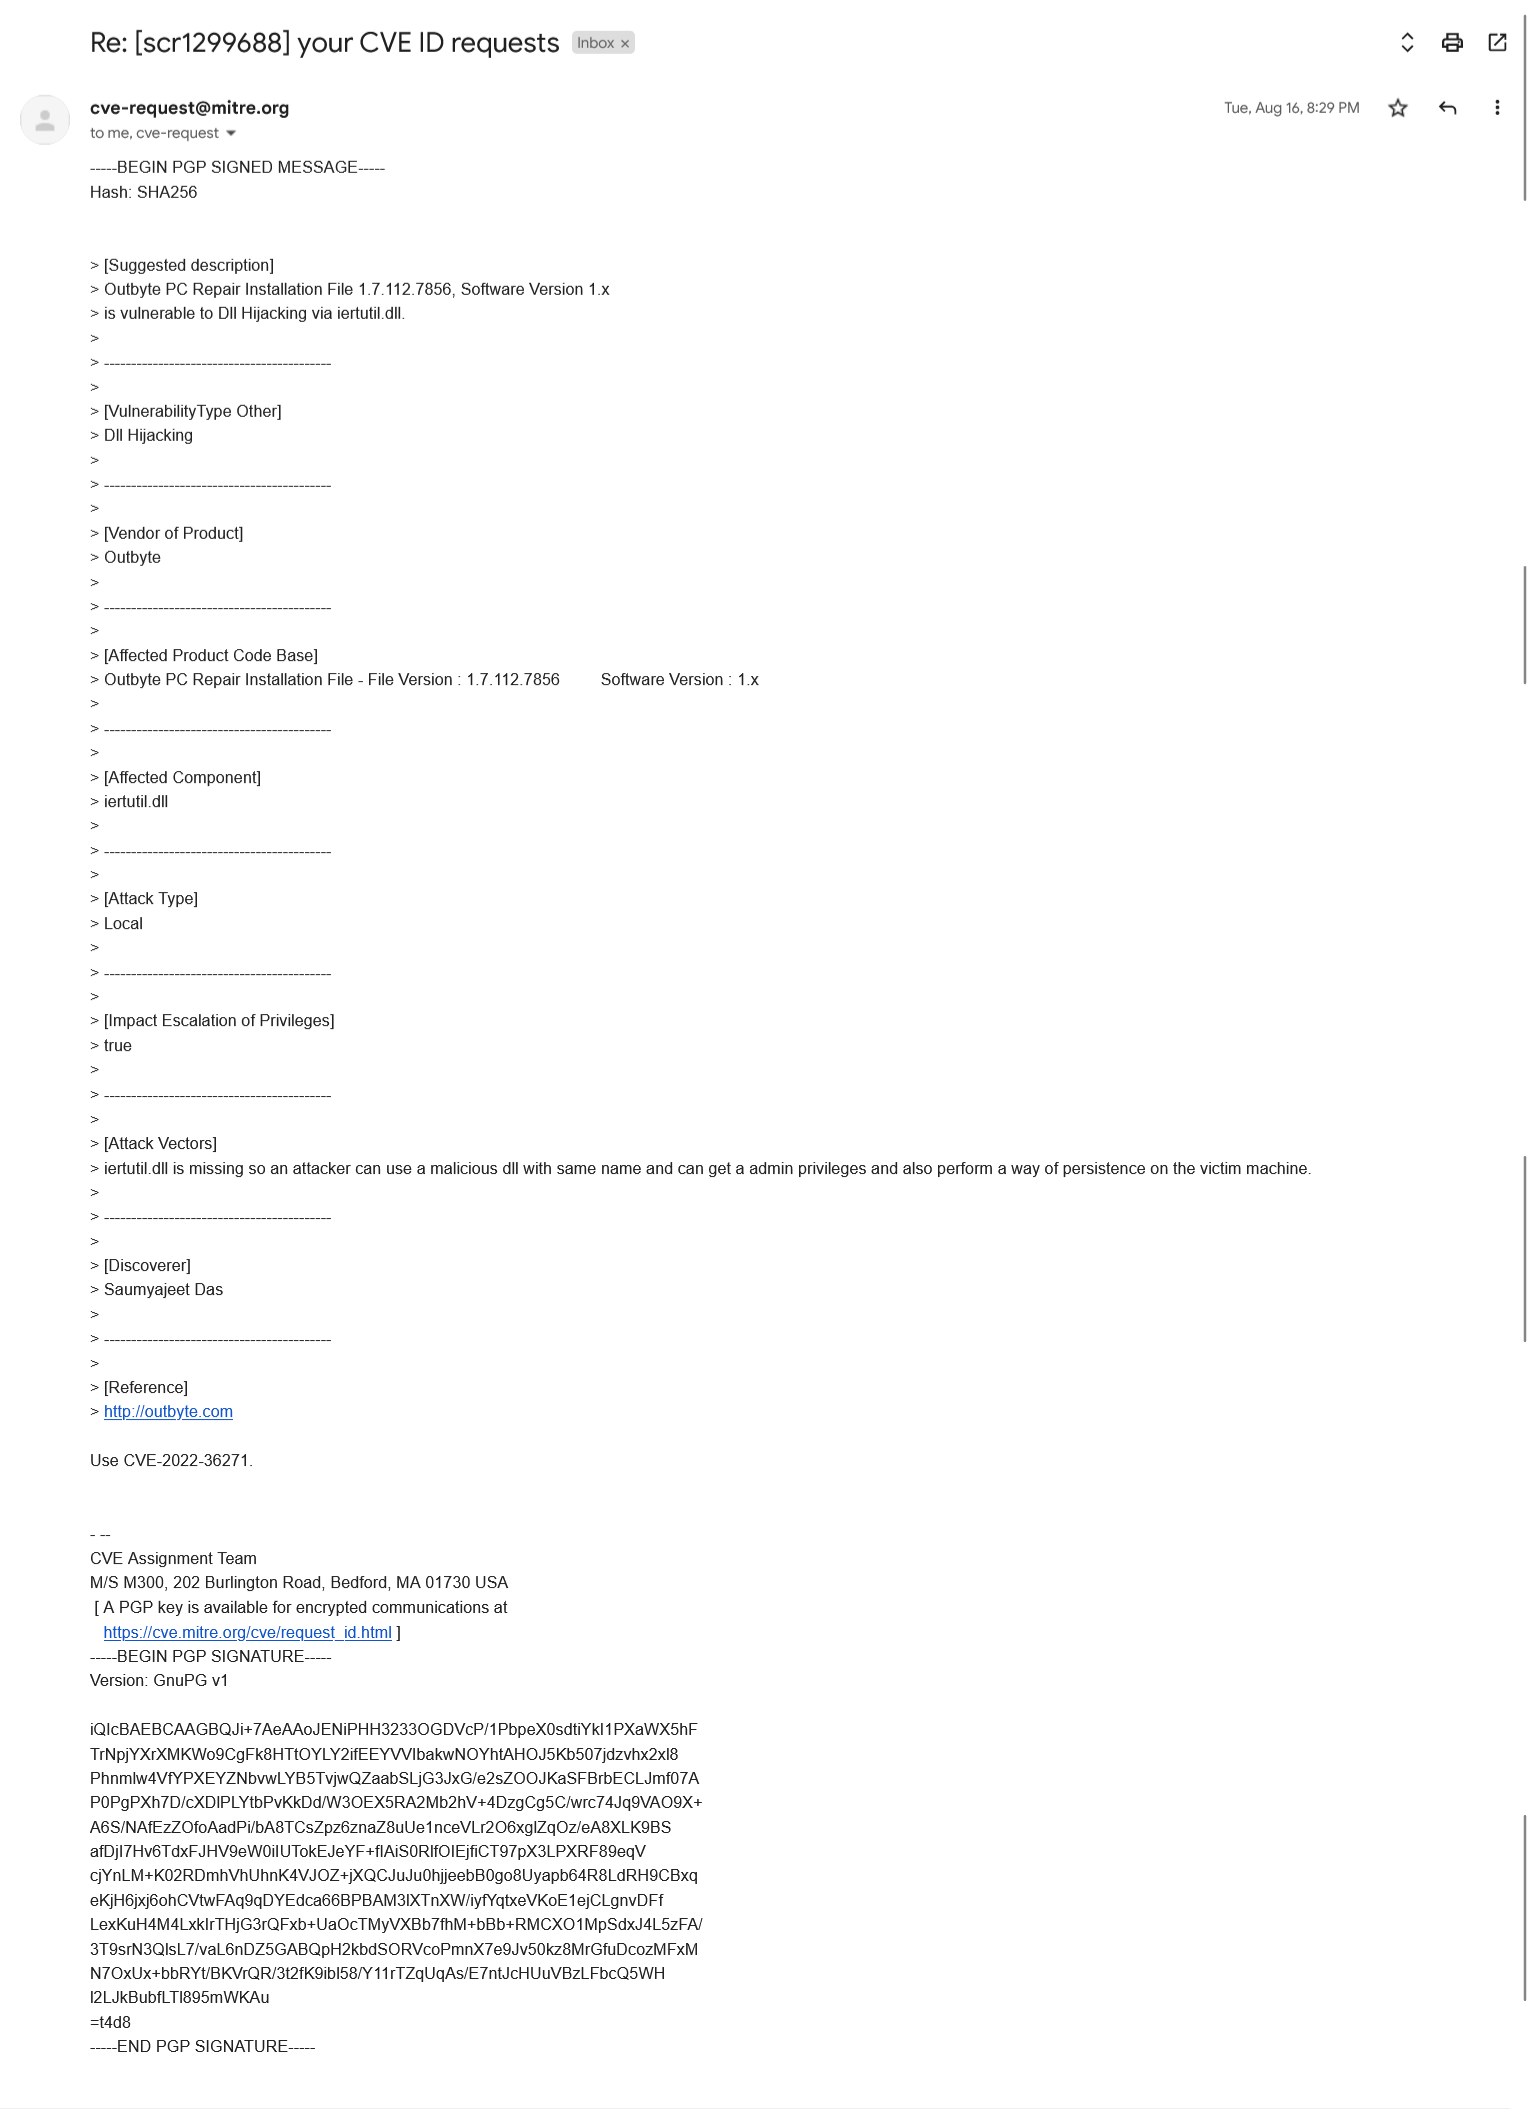 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
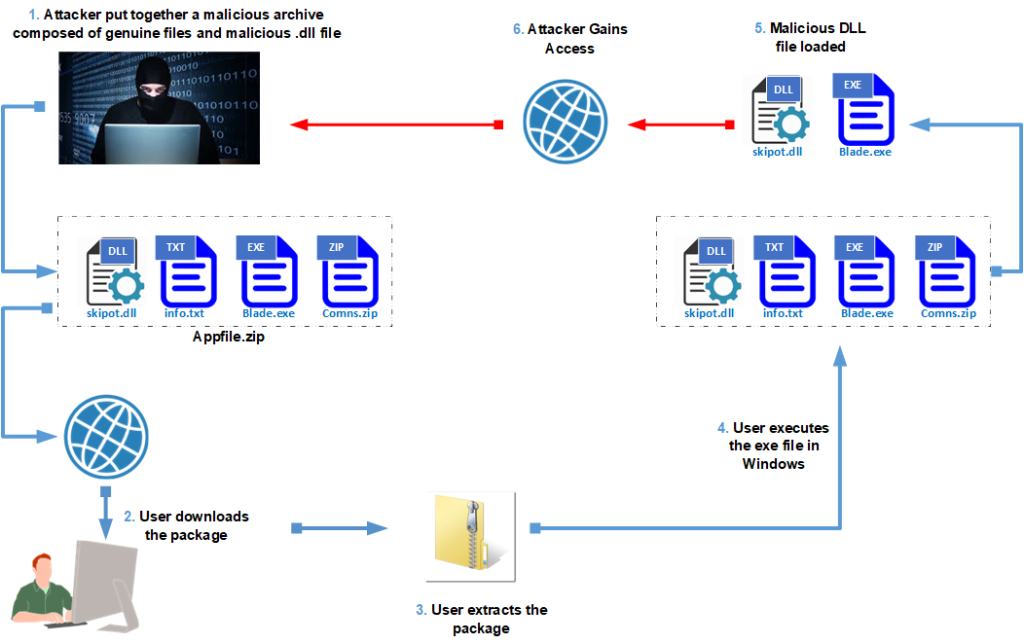 kobukovui/dll_injection_on_vlc
DLL Injection and CVE-2010-3124