
InflativeLoading
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
binary-exploitationexploitationmalware-analysis+3
326
senzee1984/inflativeloadingDynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 thesecretclub/sandboxbootkit
Bootkit for Windows Sandbox to disable DSE/PatchGuard.
 not-matthias/amd_hypervisor
Rust AMD SVM hypervisor framework with customizable vmexit handlers (MSR, CPUID, RDTSC) and NPT hooking for kernel-level monitoring and research.
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 zer0t0/cve-2025-56383-proof-of-concept
CVE-2025-56383-Proof-of-Concept
 mdsecactivebreach/cve-2018-4878
Proof-of-concept exploit for CVE-2018-4878, a Use-After-Free vulnerability in Adobe Flash Player 32-bit, providing a ByteArray object for process…
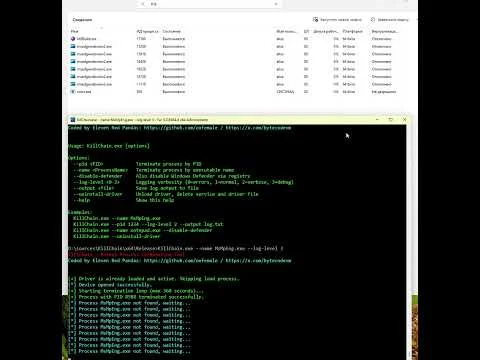 oxfemale/killchain
Kernel Process Termination Tool ( CVE-2026-0828 exploit)
 brianwrf/cve-2017-4878-samples
CVE-2017-4878 Samples - http://blog.talosintelligence.com/2018/02/group-123-goes-wild.html
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
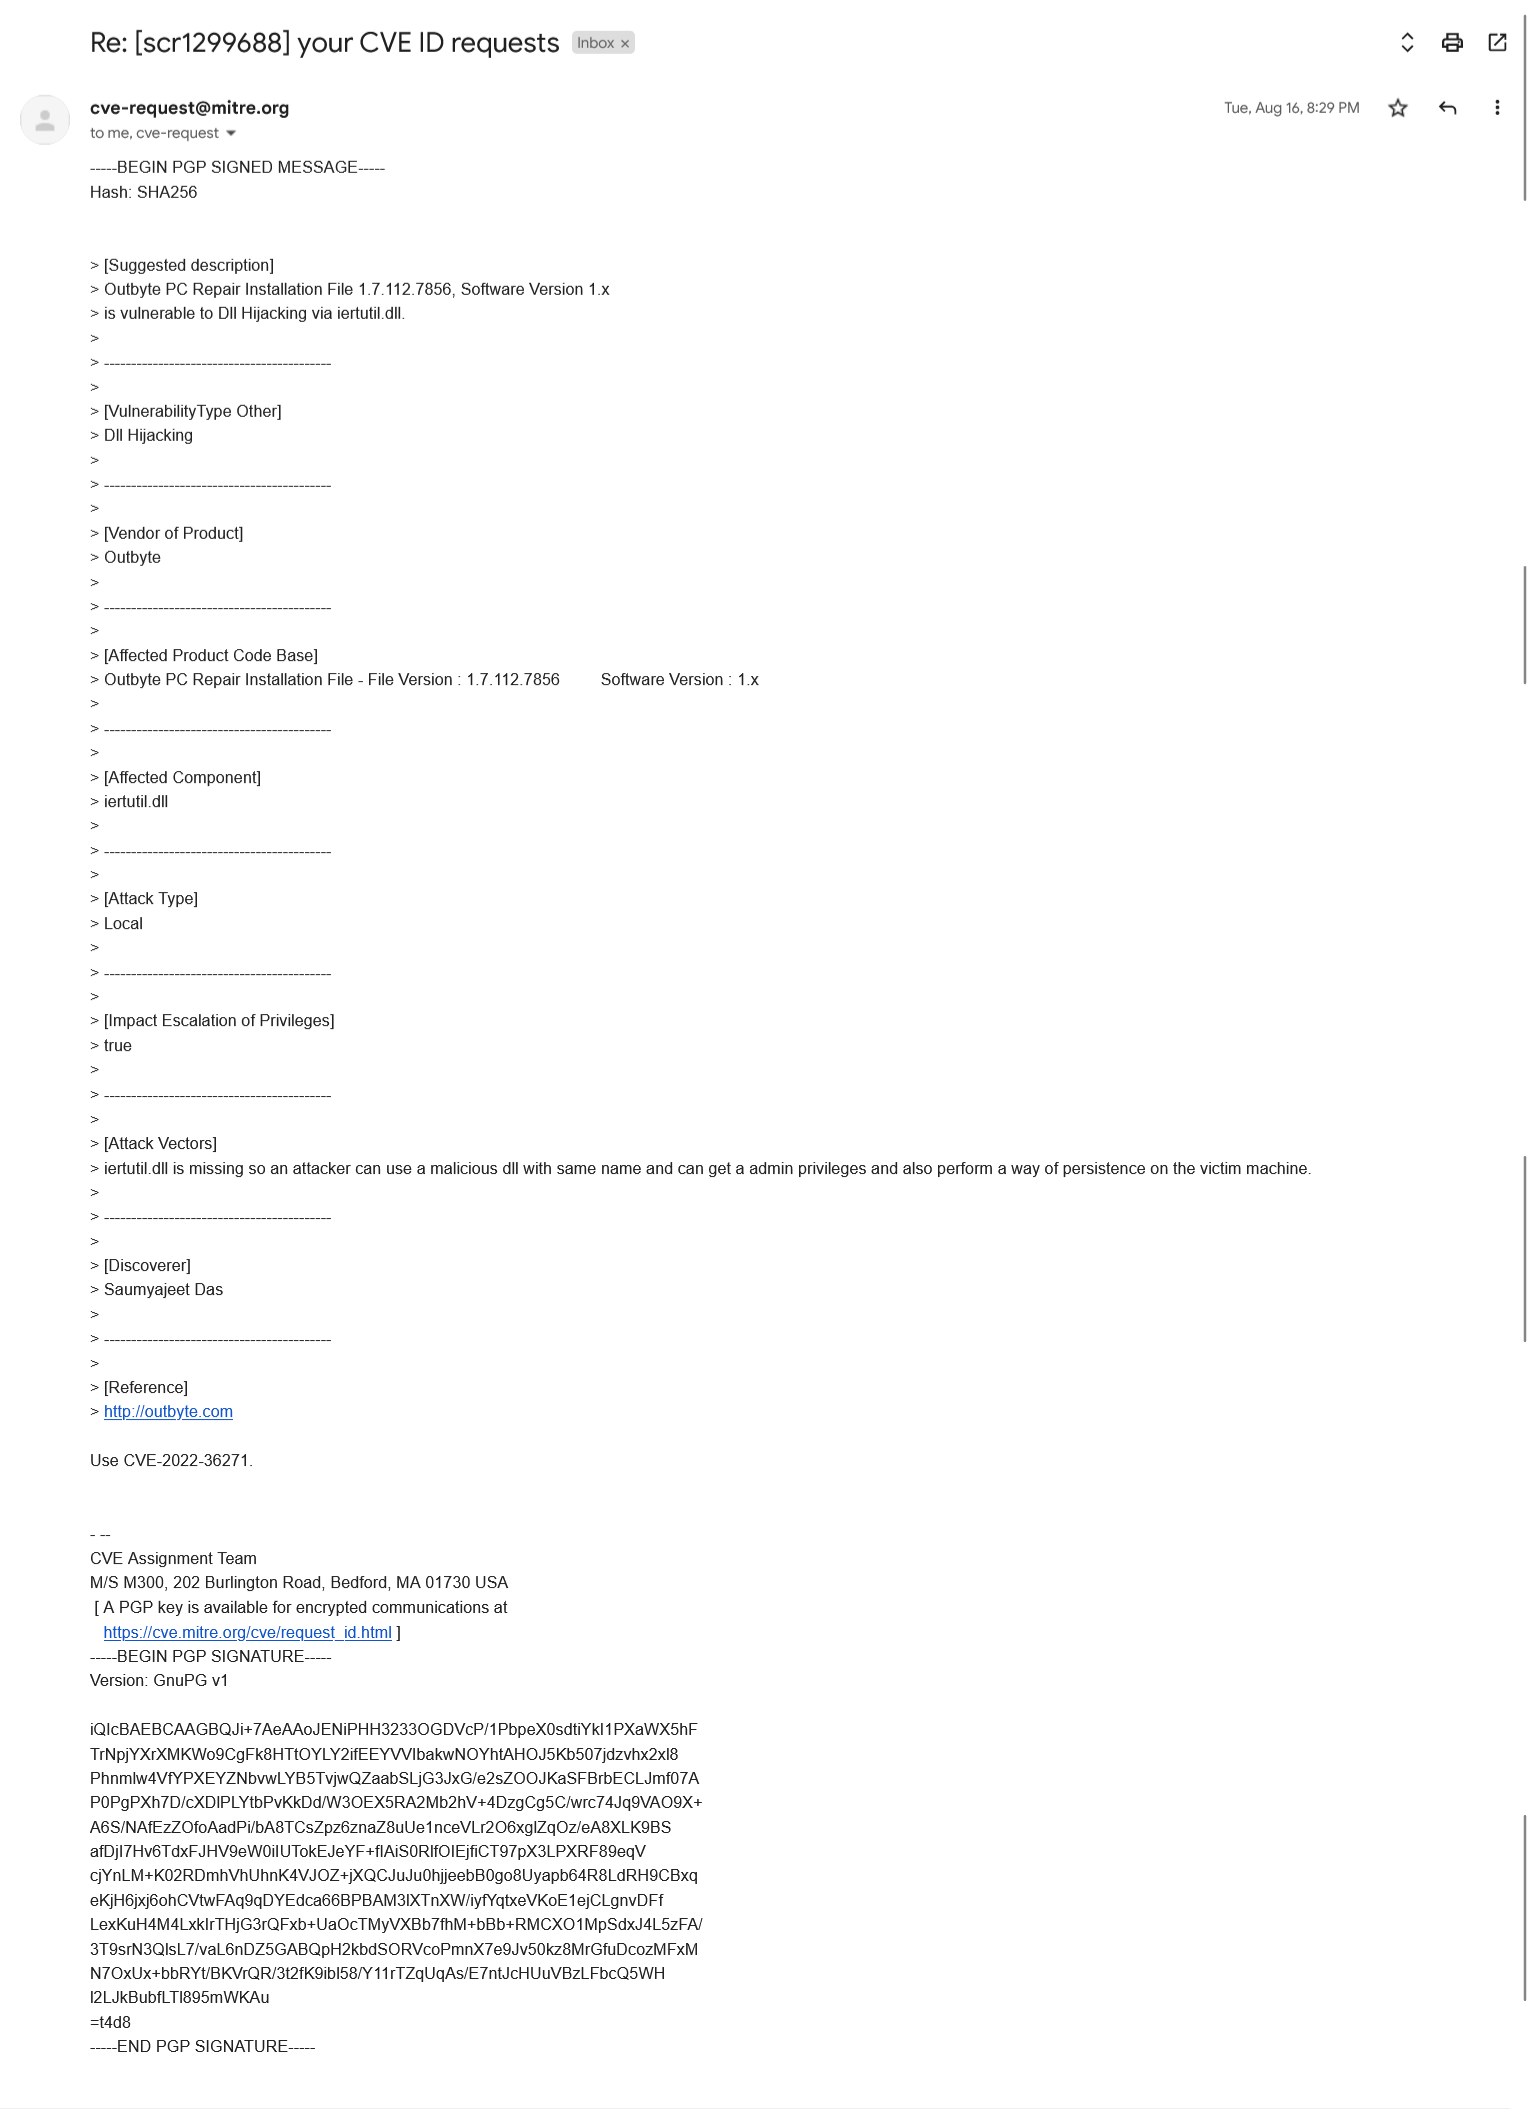 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
 xm0kht4r/cve-2025-7771
A simple PoC demonstrating the vulnerability in the ThrottleStop.sys driver, showcasing arbitrary physical memory read and write capabilities, as…
 lan1oc/cve-2023-34312-exp
Reproduction of CVE-2023-34312 using two malicious DLL files to exploit QQ and TIM messaging applications for security research and testing.
 simoesctt/ctt-microsoft-office-ole-manifold-bypass-cve-2026-21509
Exploit for CVE-2026-21509, a Microsoft Office OLE validation bypass using a speculative race-condition technique to evade AMSI/EDR and achieve code…
 gongchuang1089/edrkiller
Use cve-2026-36425 killer edr,360 can killer
 pexlexity/winrar-cve-2025-8088-path-traversal-poc
Proof-of-Concept for CVE-2025-8088 vulnerability in WinRAR (path traversal via ADS)
 sexyshoelessgodofwar/cve-2025-47256
Stack overflow in LibXMP
 alex-acero-security/cve-2025-20260-poc
Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…