
CVE-2026-23416-POC
 bluedragonsecurity/cve-2026-23416-poc
POC for CVE-2026-23416 (linux kernel 6.17 – linux kernel 7 rc5) - vulnerability discovered by Antonius
binary-exploitationeducationexploitation+2
8
bluedragonsecurity/cve-2026-23416-pocPOC for CVE-2026-23416 (linux kernel 6.17 – linux kernel 7 rc5) - vulnerability discovered by Antonius
 karazajac/charon
CHARON — pre-built PoC for CVE-2026-46333 (Linux ptrace mm==NULL fd theft)
 ysanatomic/cve-2022-32250-lpe
LPE PoC of a user-after-free vulnerability in the Linux netfilter subsystem.
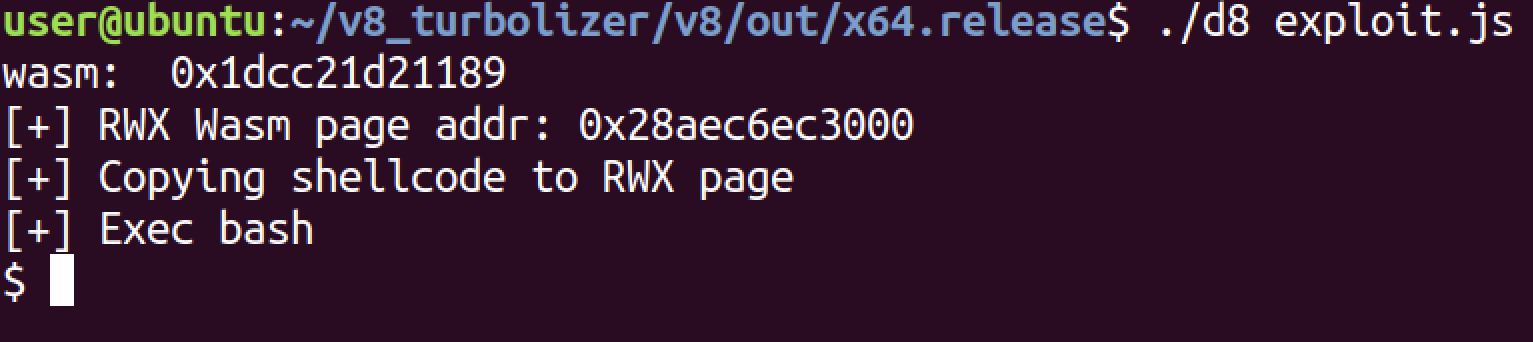 habooblab/cve-2019-13764
Full exploit for CVE-2019-13764 targeting V8 JavaScript engine on Linux, with root cause analysis and proof-of-concept code from Haboob Research Team.
 konoha279/2022-lpe-uaf
Proof-of-concept exploit code for Linux kernel use-after-free vulnerabilities (CVE-2022-2585, CVE-2022-2586, CVE-2022-2588) enabling local privilege…
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 4xura/cve-2026-31431-copy-fail
Research artifacts, PoC scripts, and lab assets for the Copy Fail Linux local privilege escalation writeup on https://4xura.com/binex/kernel/copy-fail
 seadragnol/cve-2023-52927
Local privilege escalation exploit for CVE-2023-52927, a Use-After-Free vulnerability in the Linux kernel netfilter subsystem, with a KASAN trigger…
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
 vudangducminh/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel race condition enabling unprivileged writes to read-only files and privilege…
 0x5068656e6f6c/cve-2017-5123
Exploits Linux kernel CVE-2017-5123 to achieve local privilege escalation; includes C source, static build instructions, and a write-up on the…
 eliot-code/cve-2026-52924
Technical analysis of CVE-2026-52924, a critical use-after-free in Linux kernel SCTP stale cookie handling, including root cause, attack flow, fix,…
 do4choo/cve-2026-53694-nomachine-lpe
Proof-of-concept exploit and write-up for CVE-2026-53694, a local privilege escalation in NoMachine for Linux via argument injection in nxchmod.sh,…
 erdemozgen/copy-fail-cve-2026-31431
Go port of the Copy Fail PoC for CVE-2026-31431, a Linux kernel authencesn flaw enabling a 4-byte write into page cache via AF_ALG and splice.…
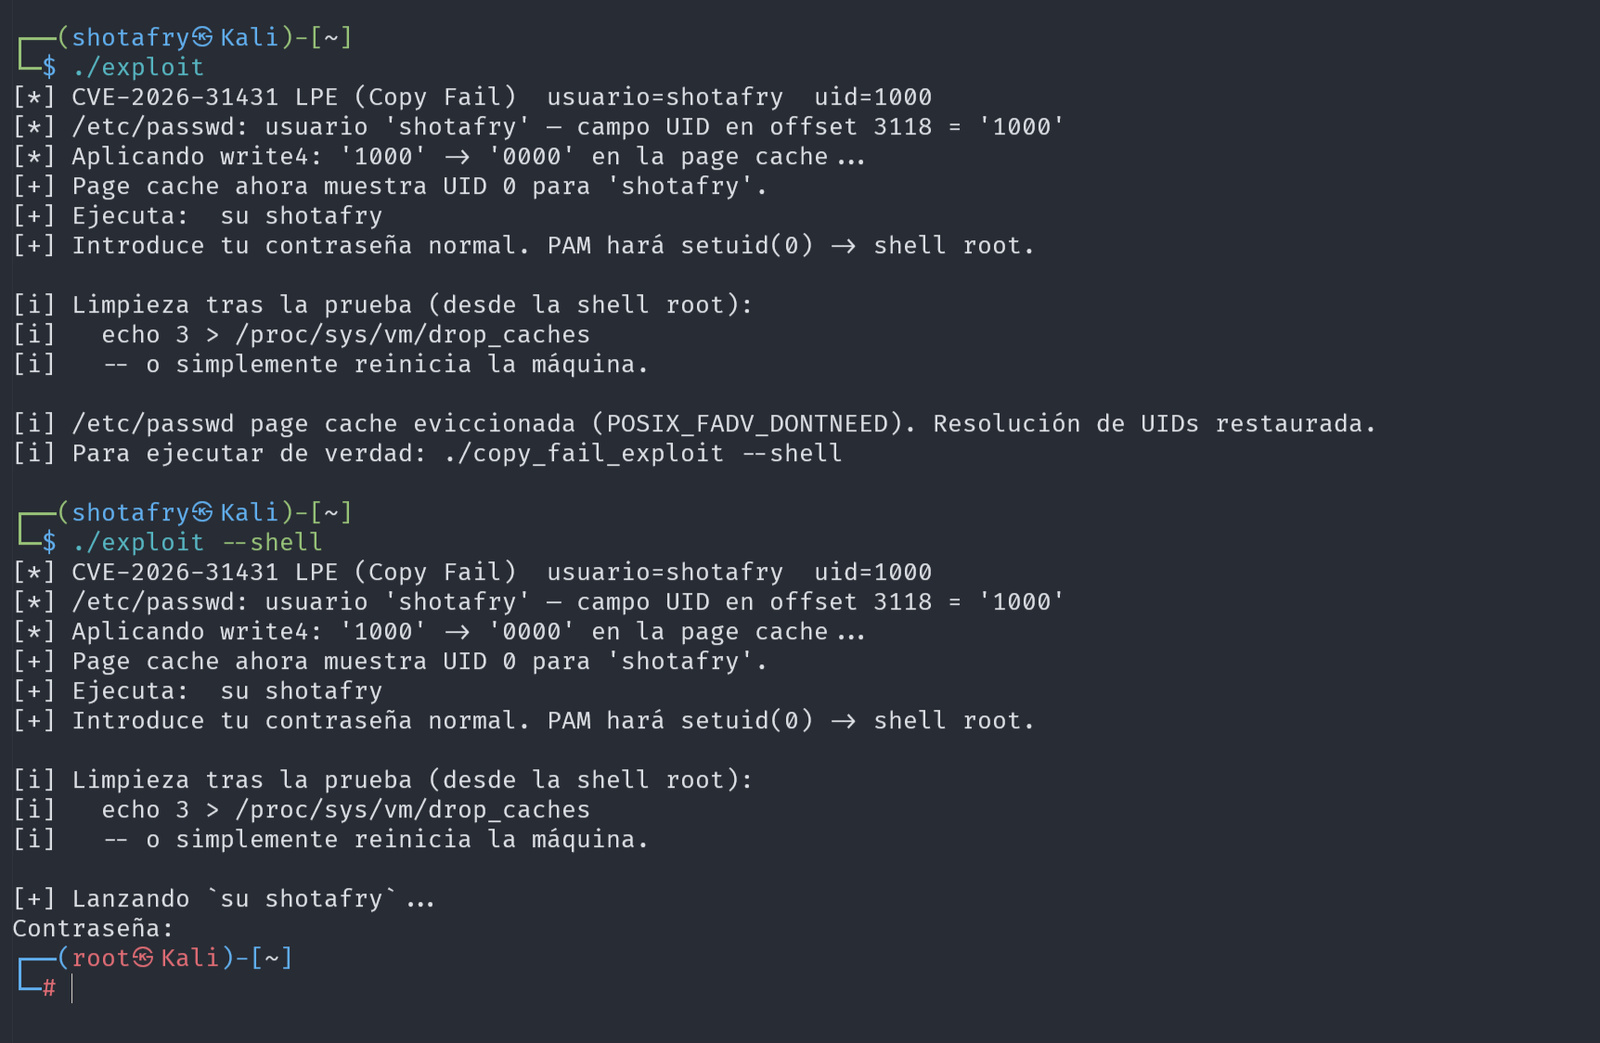 shotafry/copyfail-exploits-cve-2026-31431
Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…
 lutfifakee-project/cve-2026-41651
Local privilege escalation exploit targeting PackageKit's TOCTOU race condition (CVE-2026-41651). Escalates from unprivileged user to root via polkit…
 khoatran107/cve-2025-39682
Linux kernel TLS zero-length record handling exploit for CVE-2025-39682, targeting kernelCTF mitigation instances with a 79% success rate.
 abraxas/cve-2025-38502-linux-lpe
Research repository for CVE-2025-38502, a Linux kernel BPF cgroup local storage out-of-bounds access via tail calls enabling local privilege…