Bypass-PayloadRestrictions.dll-wdeg-rop-mitigation-

C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…

C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…

Oracle VM VirtualBox for Windows prior to 7.0.16 - Elevation of Privileges

Exploit research targeting Windows DWM to achieve local privilege escalation via a theoretical Visual-Field Singularity, bypassing graphics isolation…

Proof of concept exploit of Windows Update Orchestrator Service Elevation of Privilege Vulnerability

Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…

Plex media server local privilige escalation poc - CVE-2021-42835

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…

Proof-of-concept exploit for arbitrary file write in Sysmon 14.14, abusing Windows service tracing to achieve privilege escalation.

Proof-of-concept exploit for CVE-2016-0051 (MS16-016) achieving local privilege escalation to SYSTEM on Windows 7, with compiled binaries and…

Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English

This PoC demonstrates a race condition in the Windows kernel leading to a double-free vulnerability, allowing local privilege escalation to SYSTEM.…

Local privilege escalation exploit for ASUS AsIO3.sys driver (CVE-2025-3464). Chains a TOCTOU authentication bypass with a kernel decrement primitive…

Windows privilege escalation exploit for CVE-2023-41772 (UIFuckUp) that elevates non-admin users to SYSTEM on Windows 10 (1809+) and 11 via a crafted…

The repo contains a precompiled binary which can be run on a Windows machine vulnerable to CVE-2023-28252

Proof-of-concept and root-cause analysis of CVE-2025-60719, a use-after-free vulnerability in Windows afd.sys leading to local privilege escalation,…

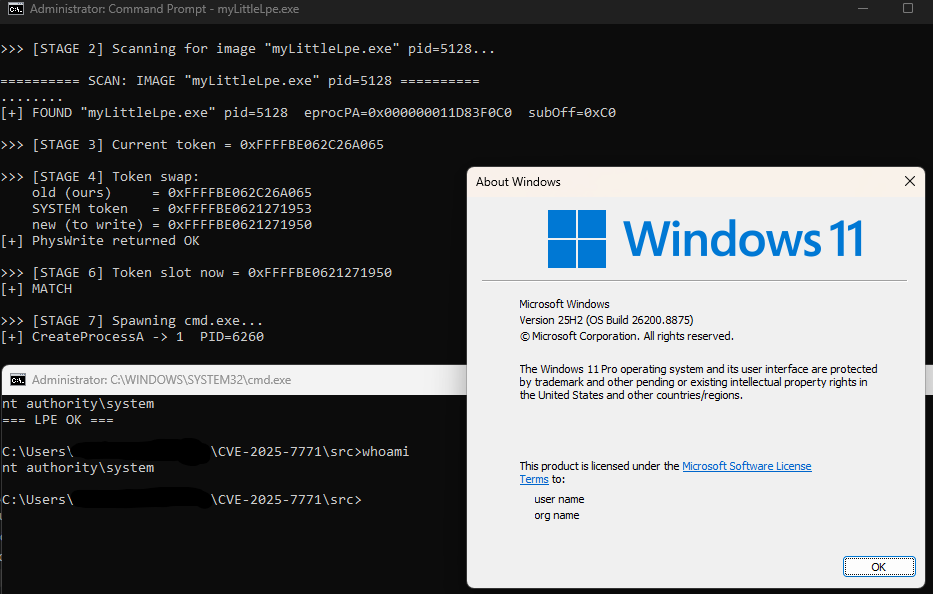
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…

Brute Ratel C4 BOF that exploits a registry symlink race condition in Windows Accessibility ATConfig to escalate privileges to SYSTEM by writing…

Full-chain RCE exploit for CVE-2025-2783, a Chromium Ipcz sandbox escape vulnerability. Implements thread hijacking, V8 hooks, and shellcode…