
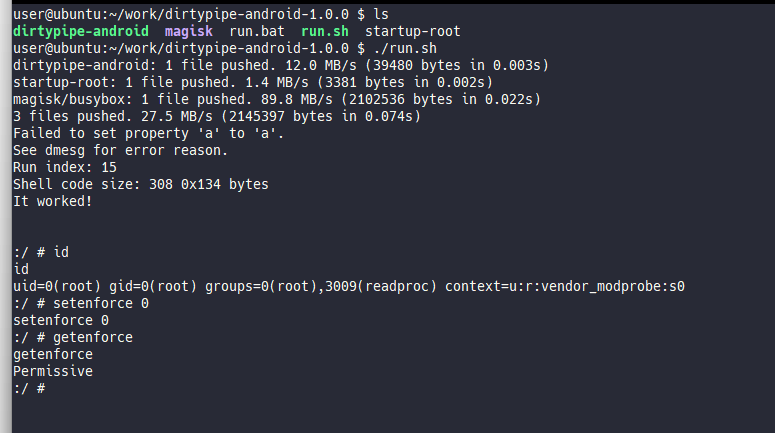
DirtyPipe-Android
 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
android-securitybinary-exploitationexploitation+5
855
polygraphene/dirtypipe-androidDirty Pipe root exploit for Android (Pixel 6)
 grant-h/qu1ckr00t
A PoC application demonstrating the power of an Android kernel arbitrary R/W.
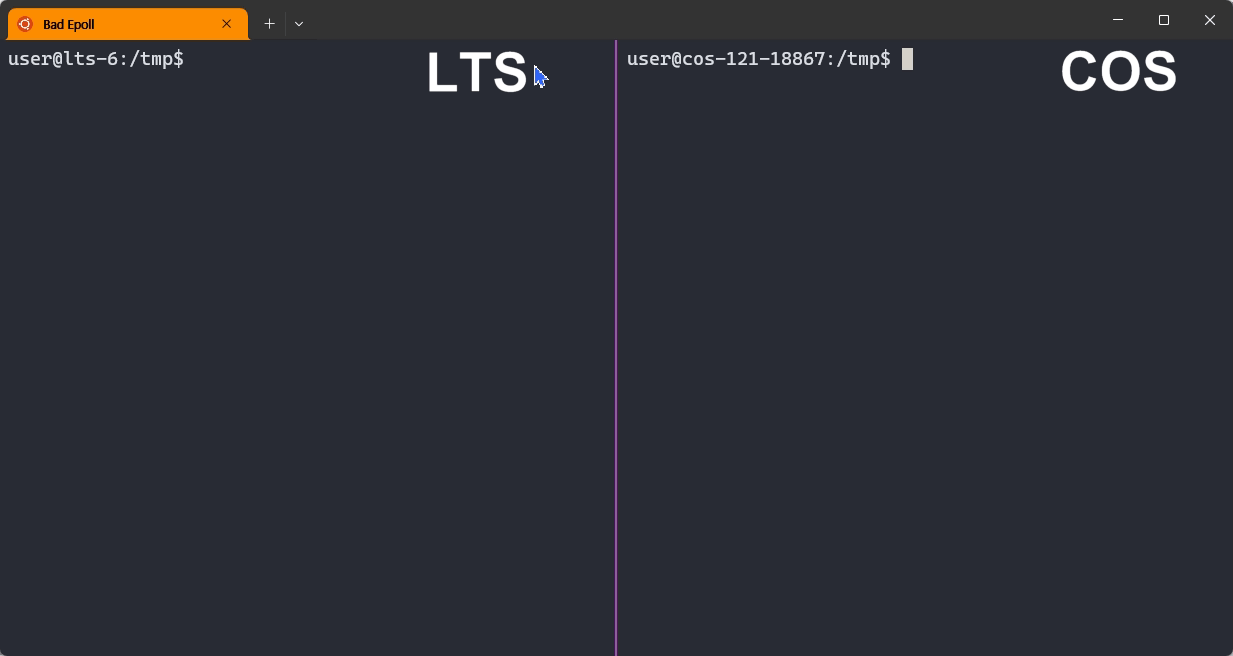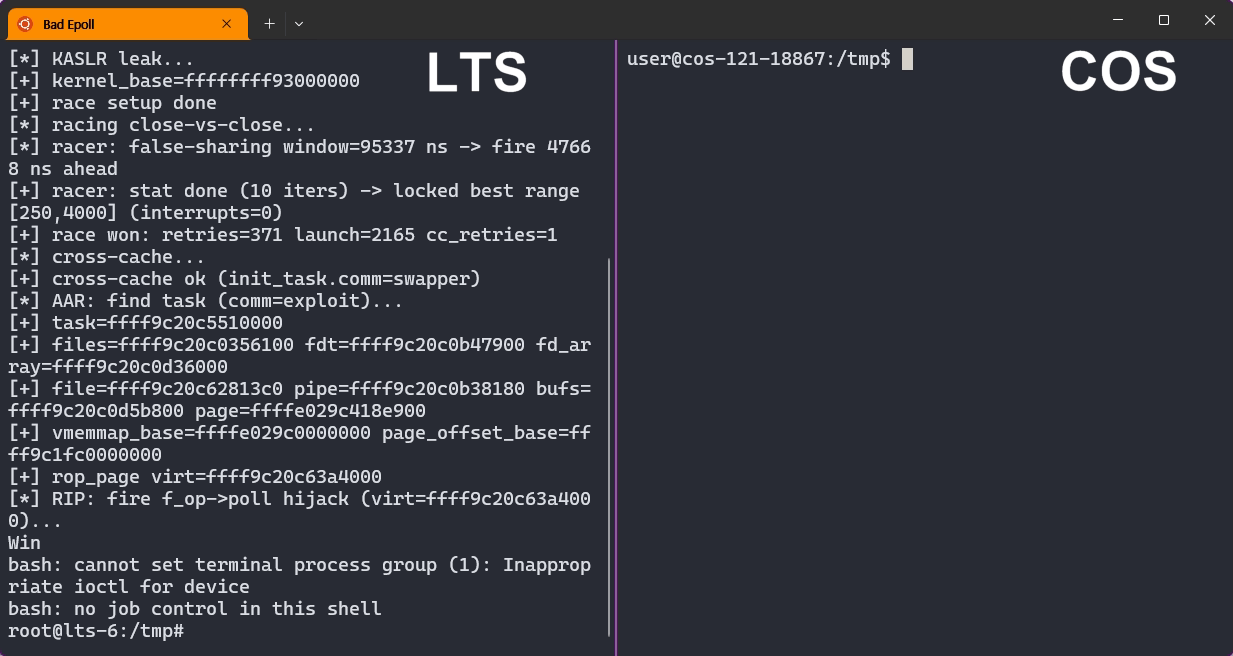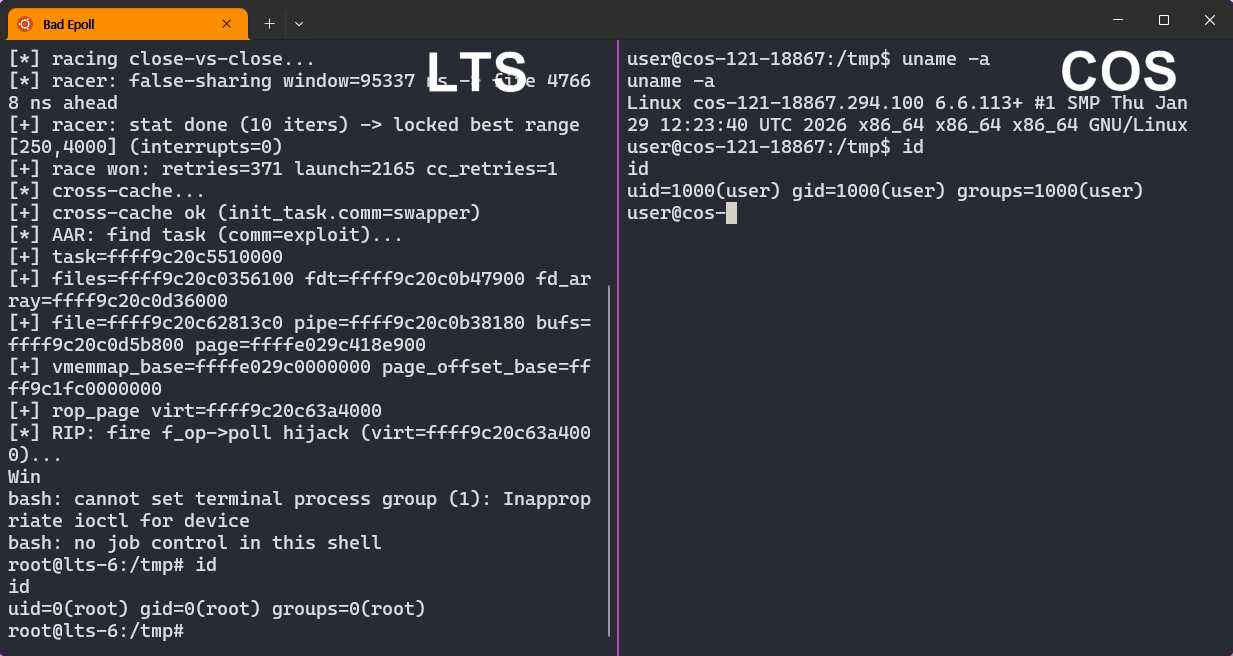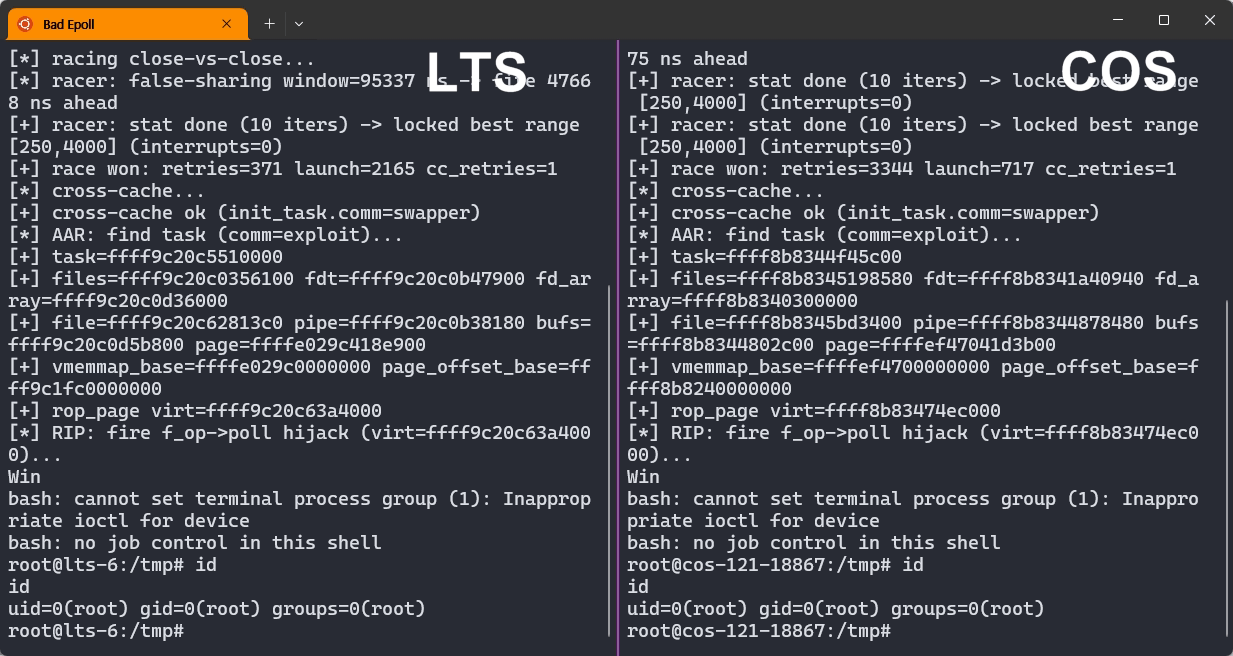 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 x-spy/cve-2026-43499-popsicle
CVE-2026-43499 Implementation for 6.12.23-android16-5-g75e9b1c7ae7c-abogki463945075-4k
 laginimaineb/extractkeymaster
Exploit that extracts Qualcomm's KeyMaster keys using CVE-2015-6639 and CVE-2016-2431
 jduck/cve-2015-1538-1
Python exploit for CVE-2015-1538-1 targeting Stagefright's 'stsc' MP4 atom integer overflow to achieve remote code execution and a reverse shell on…
 northbit/metaphor
Metaphor - Stagefright with ASLR bypass
 michalbednarski/leakvalue
Exploit for CVE-2022-20452, privilege escalation on Android from installed app to system app (or another app) via LazyValue using Parcel after…
 flankerhqd/vendor-android-cves
Collections of my POCs for android vendor CVEs
 bluefrostsecurity/cve-2020-0041
Exploits for Android Binder bug CVE-2020-0041
 0xkol/badspin
Bad Spin: Android Binder Privilege Escalation Exploit (CVE-2022-20421)
 farazsth98/chronomaly
Android kernel exploit for CVE-2025-38352, previously exploited in-the-wild. Targets vulnerable x86_64 Linux kernels v5.10.x.
 zhuowei/cheese
CVE-2025-21479 proof-of-concept, I think
 kpwnz/def1nit3lyn0taja1lbr3aktool
A jailbreak tool for all arm64 devices on iOS 16.0 to iOS 16.6.1
 bazad/blanket
CVE-2018-4280: Mach port replacement vulnerability in launchd on iOS 11.2.6 leading to sandbox escape, privilege escalation, and codesigning bypass.
 potmdehex/multicast_bytecopy
kernel r/w exploit for iOS 15.0 - 15.1.1
 canyie/cve-2024-0044
Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…
 0x36/weightbufs
ANE kernel r/w exploit for iOS 15 and macOS 12