
CVE-2024-6387
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
binary-exploitationexploitationnetwork-security+6
l-urk/cve-2024-6387Proof of concept python script for regreSSHion exploit.
 shreyas-penkar/cve-2025-39965
Proof-of-concept exploit for CVE-2025-39965, a Linux XFRM subsystem vulnerability, demonstrating exploitation in an isolated emulator environment for…
 hycqaq/logitech-g-cloud-ghostlock-cve-2026-43499
罗技云掌机 · GhostLock CVE-2026-43499 root 尝试
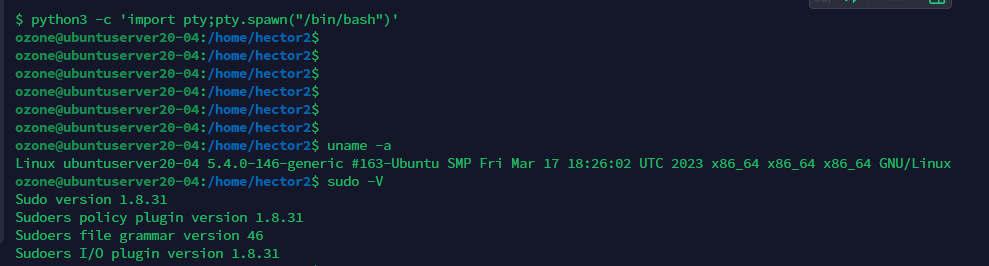 purpleozone/pe_cve-cve-2021-3156
Exploit for Ubuntu 20.04 using CVE-2021-3156 enhanced with post-exploitation scripts
 d0rb/logofail-poc
This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.
 d0rb/cve-2023-42931
The exploit targets a critical privilege escalation vulnerability in macOS versions Monterey, Ventura, and Sonoma.
 sparrow-labz/cve-2020-0423
Researching CVE published originally by longterm.io
 d0rb/cve-2023-49606
Critical use-after-free vulnerability discovered in Tinyproxy
 jackhuyh/cve-2016-3308
Use CVE-2016-3308 corrupt win32k desktop heap
 seqred-s-a/cve-2019-14514
Remote code execution in Microvirt MEmu
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 l1m3syc/cve-2024-4947-poc
Educational proof-of-concept for CVE-2024-4947, a V8 Maglev type confusion, demonstrating a full chain from trigger to arbitrary code execution on a…
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 mk219533/cve-2010-1205
sample exploit of buffer overflow in libpng
 kswzzl/cve-2016-3861
my extended take on Mark Brand's CVE 2016-3861 libutils bug
 ronf98/cve-2023-38831-poc
CVE-2023-38831 is a Zero-day WinRAR vulnerability that lets attackers disguise malicious files in archives, tricking users into executing harmful…
 0xeremus/dirty-pipe-poc
POC Exploit to add user to Sudo for CVE-2022-0847 Dirty Pipe Vulnerability
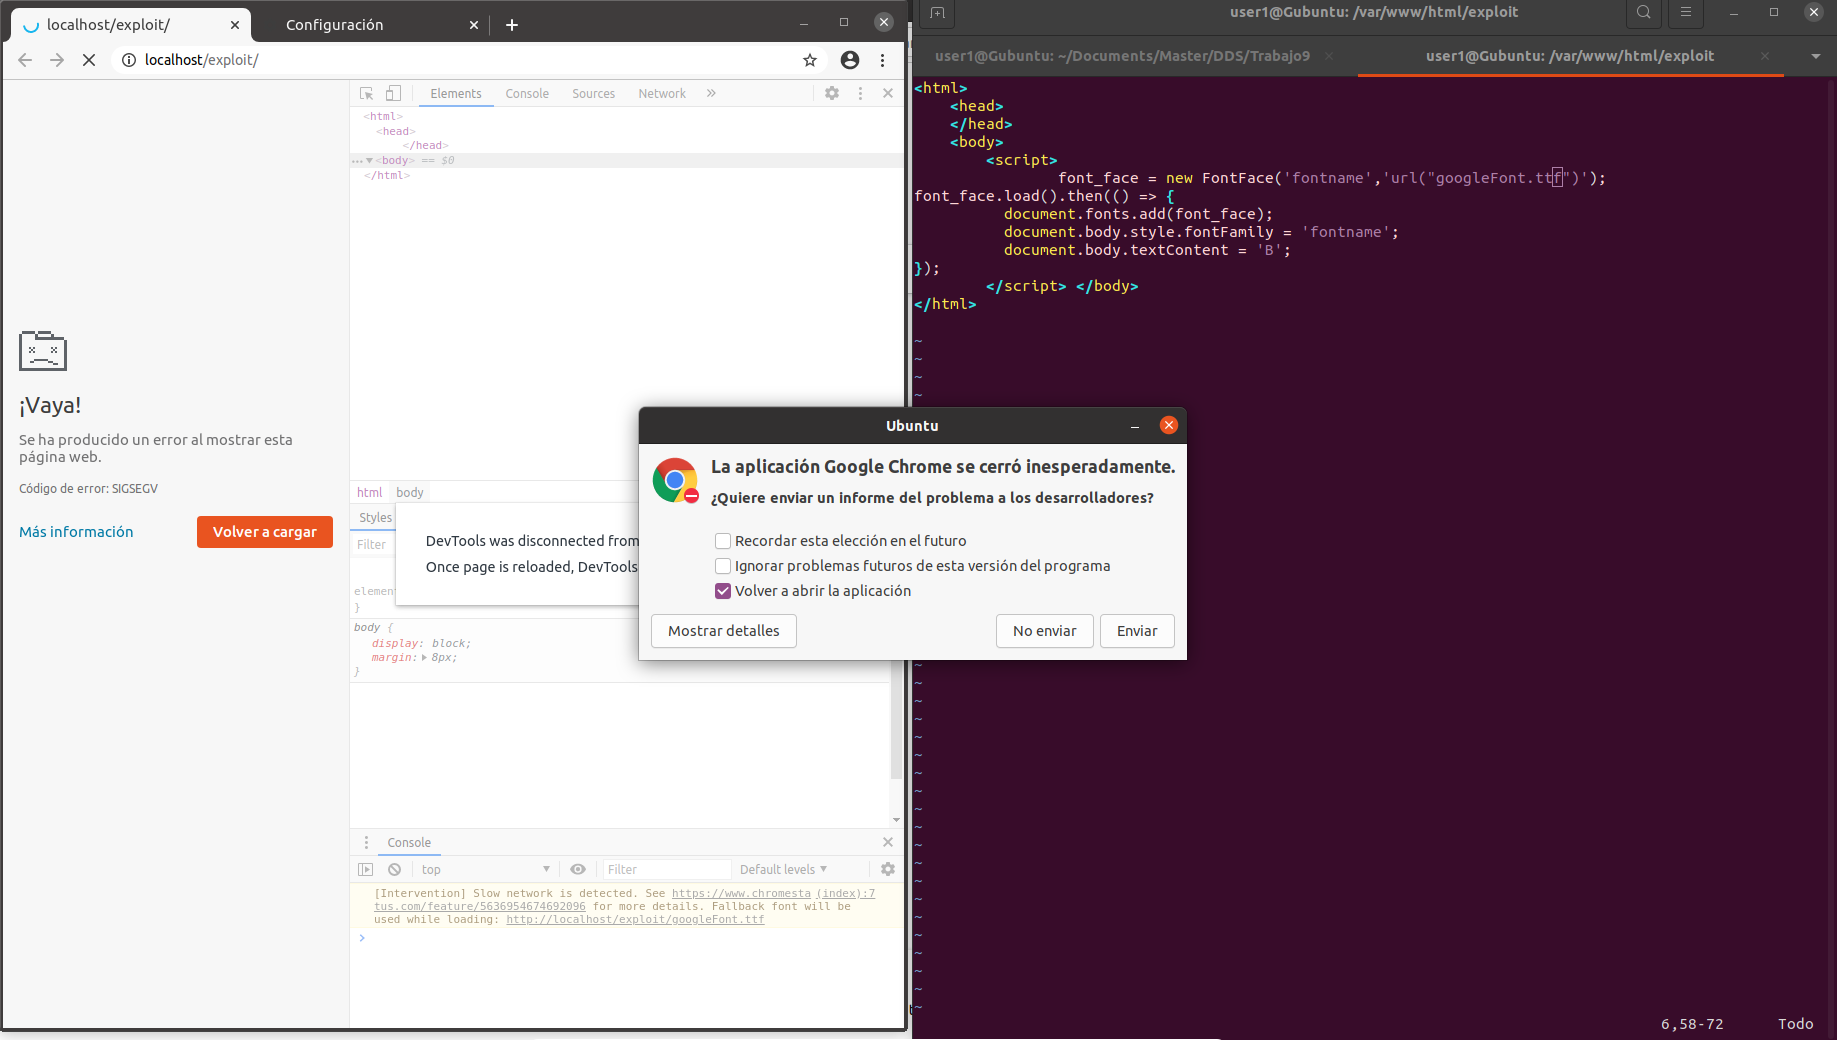 marmeus/cve-2020-15999
Todos los materiales necesarios para la PoC en Chrome y ftview