
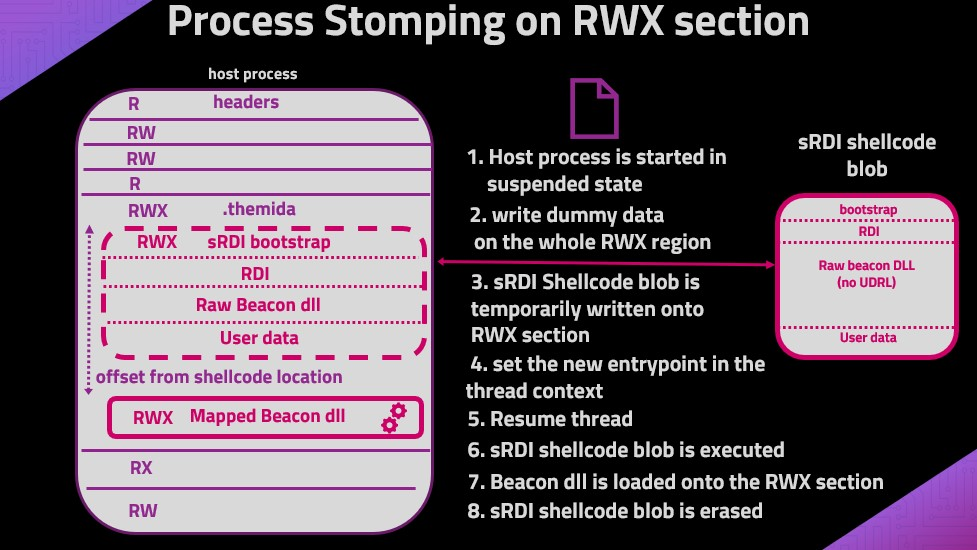
ProcessStomping
 naksyn/processstomping
A variation of ProcessOverwriting to execute shellcode on an executable's section
binary-exploitationeducationpayload-development+3
naksyn/processstompingA variation of ProcessOverwriting to execute shellcode on an executable's section
 4n4s4zi/copyfail-alpine
More portable PoC of copyfail LPE (CVE-2026-31431) that works on Alpine Linux
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
 d4em0n/exrop
Automated ROP chain generator for x86-64 binaries using symbolic execution. Supports register/memory writes, function calls, syscalls, badchar…
 albocoder/cve-2022-27666-exploits
There are 2 exploitation methods that exploit CVE-2022-27666. For more info on how to use these code bases please check my blog.
 ghostn4444/poc-cve-2025-6554
Proof-of-concept exploit for CVE-2025-6554, a V8 JavaScript engine vulnerability allowing unauthorized access to uninitialized 'Hole' values via…
 sakilahamed/linux-kernel-exploit-lab
More specific : Dirty COW (CVE-2016-5195)
 bikini/exploitarium
Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 0xdea/raptor_infiltrate19
#INFILTRATE19 raptor's party pack.
 k3vinlusec/r7000_httpd_bof_cve-2020-15416
Walkthrough of CVE-2020-15416 buffer overflow exploit for Netgear R7000 router, including QEMU user-mode debugging environment setup and detailed…