
copy-fail-CVE-2026-31431
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
binary-exploitationcloud-securitycontainer-security+6
rio128128/copy-fail-cve-2026-31431Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 dinosn/mariadb-13-rce-lab
MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
 minsmiths/cve-2023-34446
Proof-of-concept exploit for CVE-2023-36664, a Ghostscript command injection vulnerability. Includes Docker lab environment, detailed analysis of…
 dinosn/cve-2019-13132-lab
CVE-2019-13132 — libzmq CURVE INITIATE stack overflow → RCE. Working exploit + Docker lab.
 prabeershakya/cve-2022-0185-poc
Proof-of-concept exploit for CVE-2022-0185, a Linux kernel heap buffer overflow enabling local privilege escalation and container escape via FUSE and…
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 trax69/cve-2025-55182-poc
Proof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…
 androidteacher/cve-2026-24061-poc-telnetd
Proof-of-concept exploit for CVE-2026-24061, an unauthenticated remote root privilege escalation in inetutils-telnetd via USER environment variable…
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
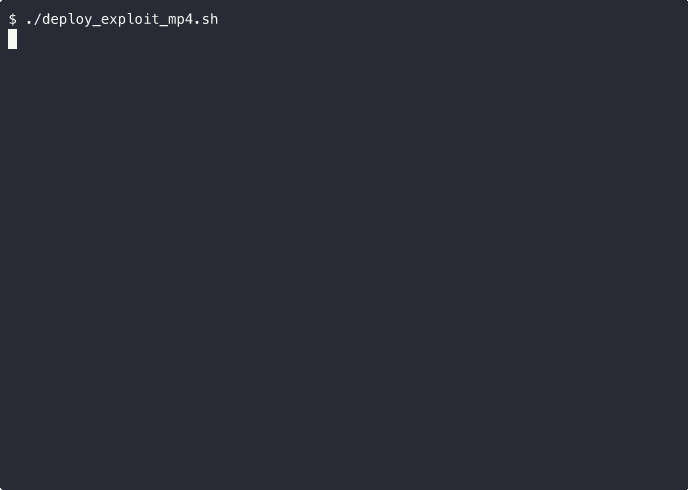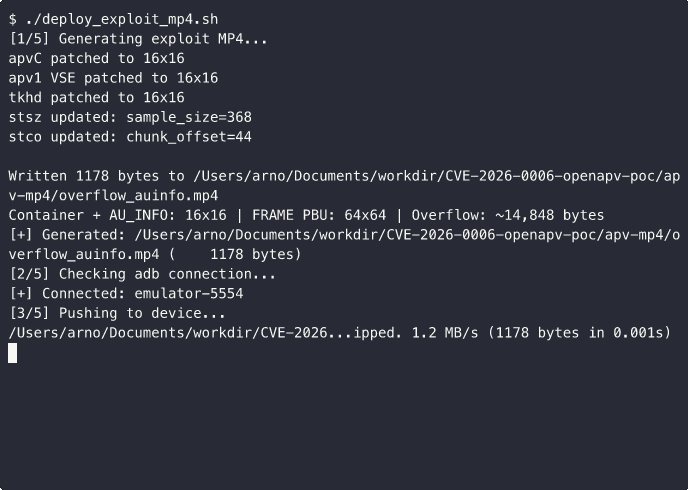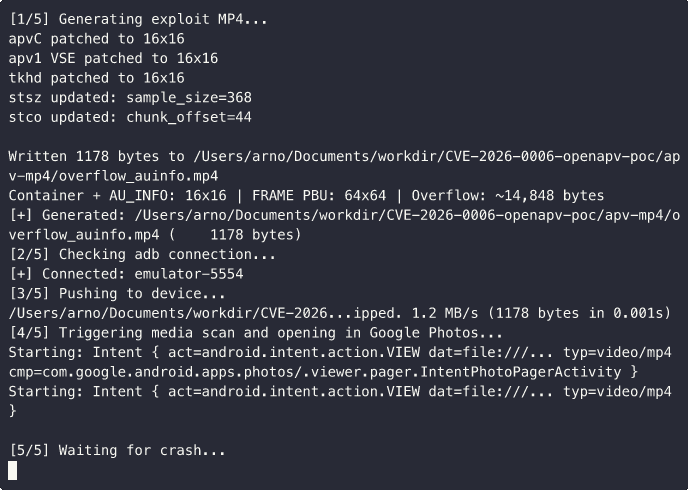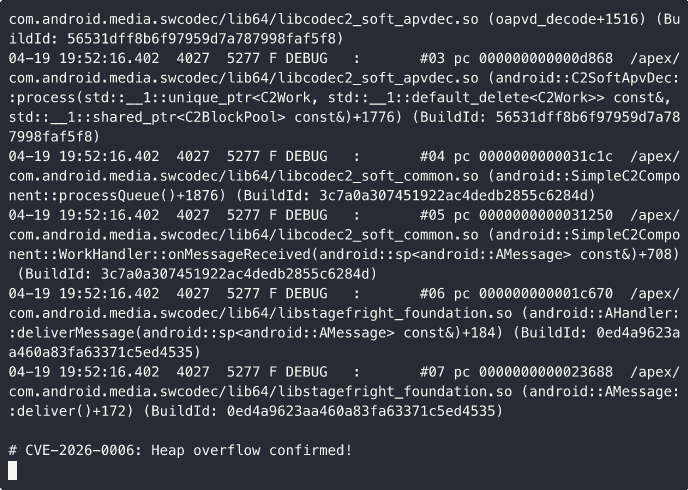 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 rami08448/cve-2021-3656-demo
Demonstration of CVE-2021-3656, a KVM nested virtualization vulnerability allowing L2 guest to bypass VMLOAD/VMSAVE intercepts and read/write host…
 sparshbiswas-ai/cve-2026-0596-reproduction
Research environment and validation scripts for evaluating deserialization behaviors in MLflow and MLServer.
 lane0218/cve-2023-25136-poc
Minimal Docker-based reproduction environment for OpenSSH 9.1p1 pre-auth double-free vulnerability (CVE-2023-25136), demonstrating memory corruption…
 lowercasenumbers/cve-2025-32463_sudo_chroot
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation in sudo's chroot feature via malicious NSS library loading. Includes…
 painoob/cve-2025-32463
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation vulnerability in sudo allowing chroot jail escape via specific sudoers…