
CVE-2025-32463_illdeed
 ill-deed/cve-2025-32463_illdeed
Privilege escalation exploit for CVE-2025-32463 using a malicious NSS module injected via sudo -R. This version creates a stealth payload called…
binary-exploitationeducationexploitation+3
ill-deed/cve-2025-32463_illdeedPrivilege escalation exploit for CVE-2025-32463 using a malicious NSS module injected via sudo -R. This version creates a stealth payload called…
 realatharva15/polkit-cve-2021-3560_writeup
beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 vett3x/smb-linux-cve-2025-37899
Technical analysis of CVE-2025-37899: a use-after-free vulnerability in Linux kernel's ksmbd SMB module enabling remote code execution. Includes…
 homjxi0e/cve-2017-3078
Proof-of-concept exploit for CVE-2017-3078, a memory corruption vulnerability in Adobe Flash Player ATF module enabling arbitrary code execution on…
 0xhuesca/cve-2019-18655
CVE-2019-18655 metasploit module. SEH based buffer overflow in file sharing wizard app v.1.5.0.
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
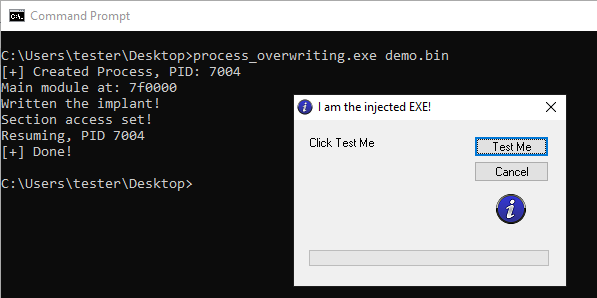 hasherezade/process_overwriting
PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.
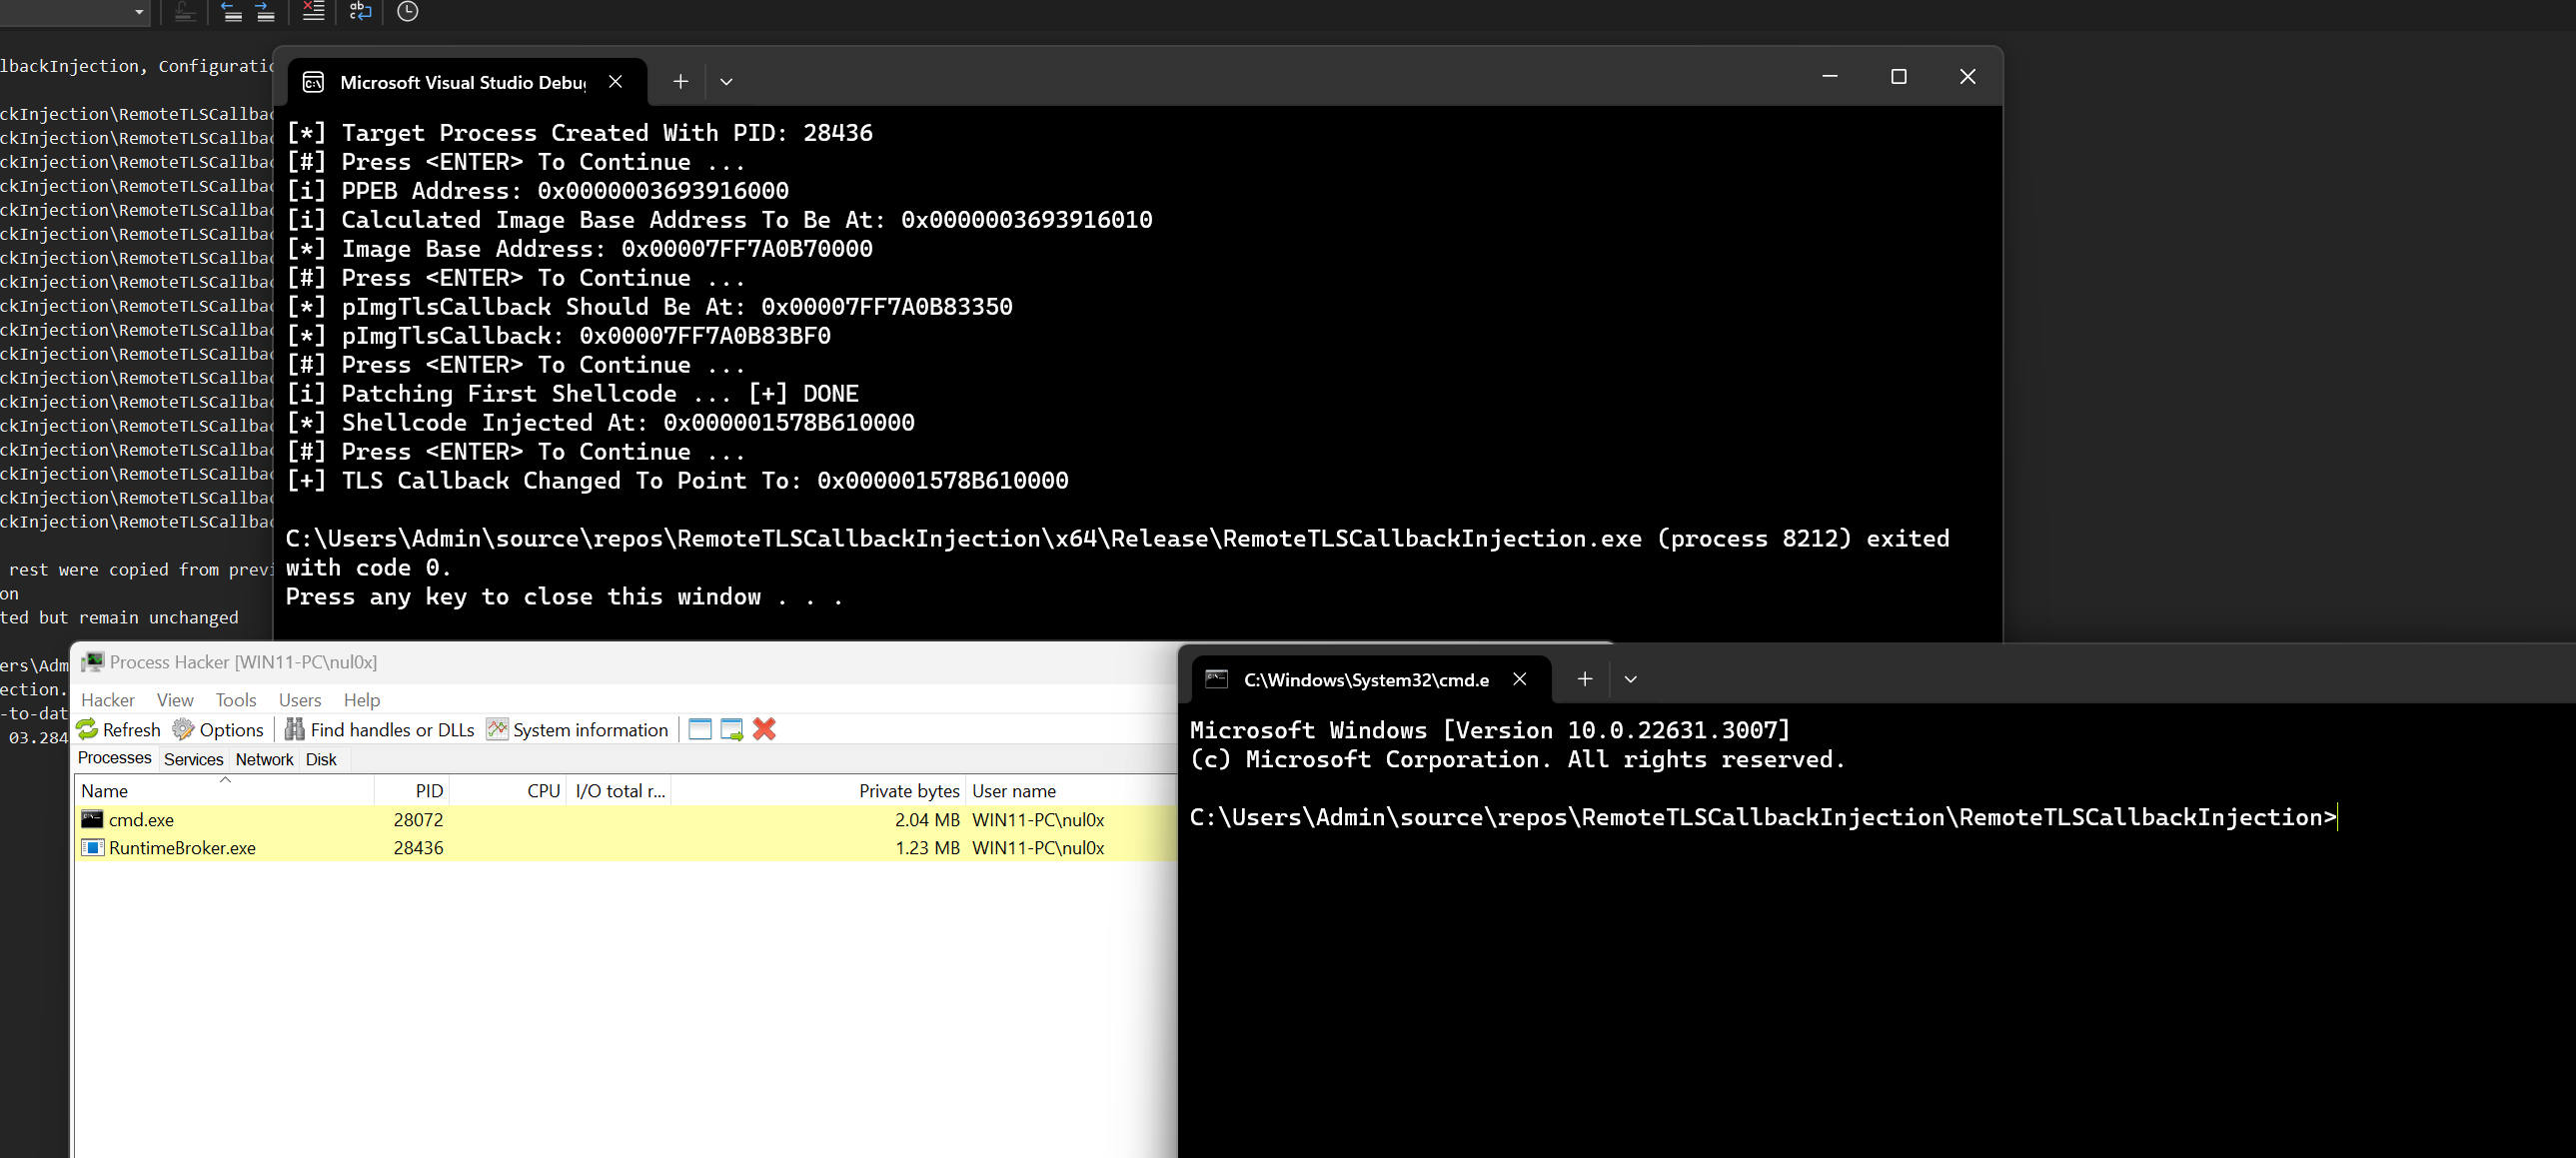 maldev-academy/remotetlscallbackinjection
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process
 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 e-r-butch/f9360-cve43499
SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
 zedeldi/cve-2025-47827
PoC and vulnerability report for CVE-2025-47827.
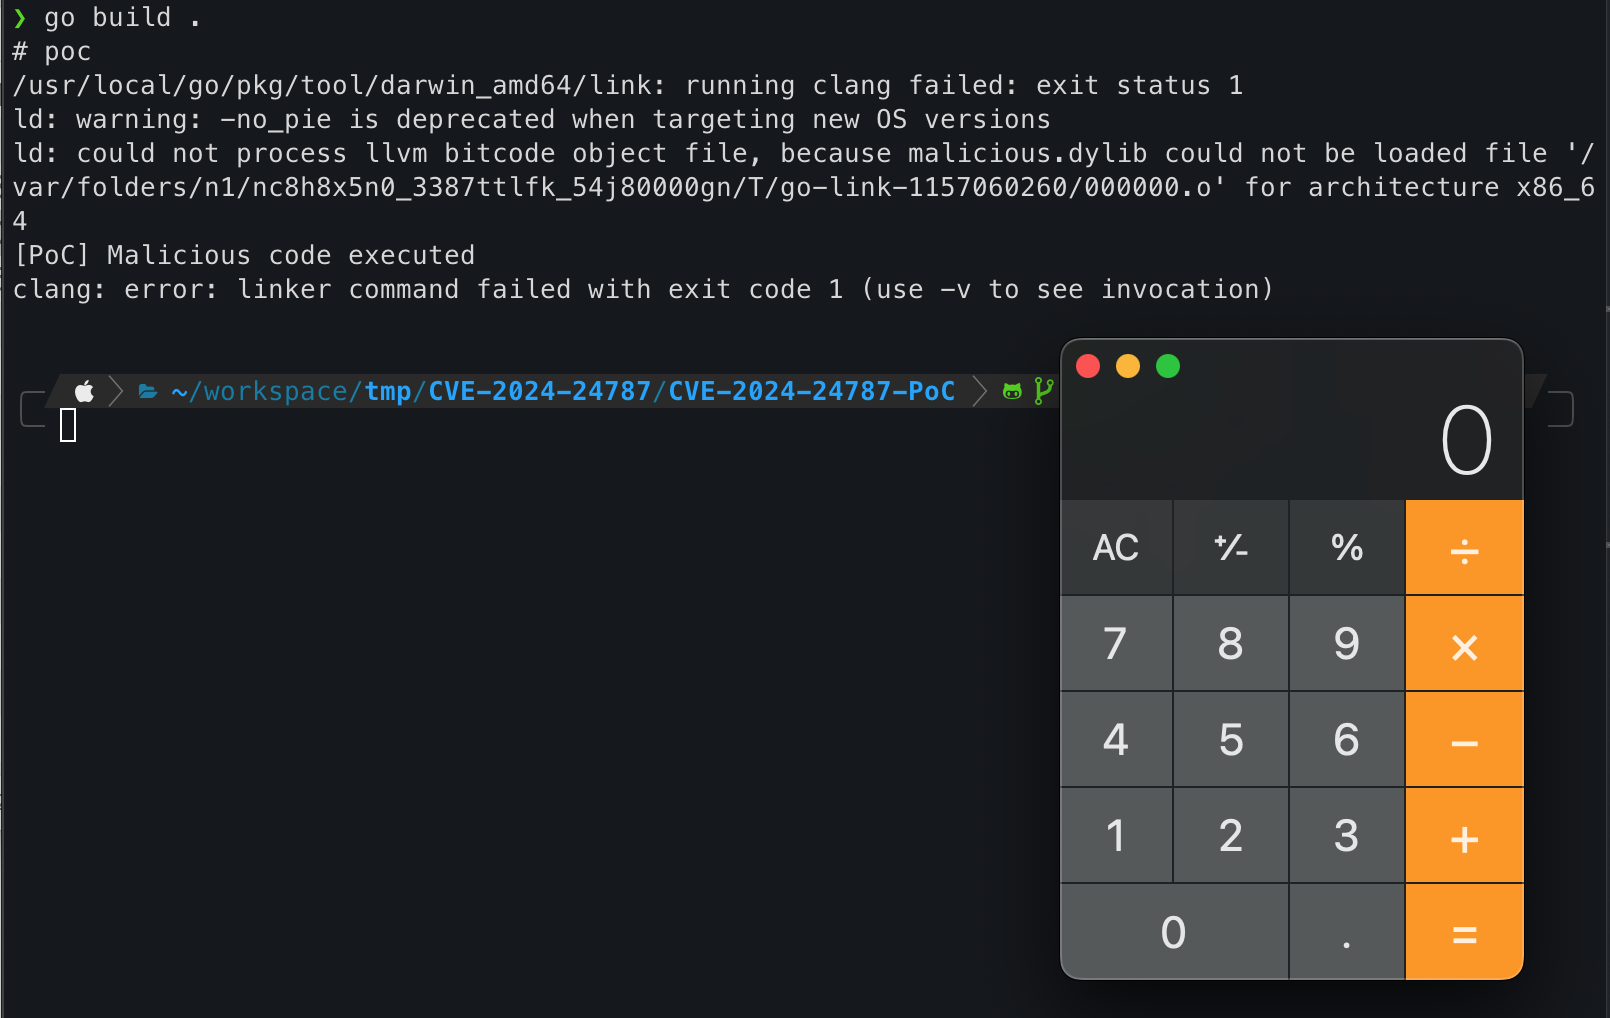 lourc0d3/cve-2024-24787-poc
CVE-2024-24787 Proof of Concept
 3nou9h/cve-2026-9256-poc
Demonstrates CVE-2026-9256 heap buffer overflow in nginx's ngx_http_rewrite_module with PoC scripts for heap/libc leaks and worker crash.
 suominen/cve-2026-9256
Tracking the nginx CVE-2026-9256 rewrite-module heap overflow
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 sexyshoelessgodofwar/cve-2025-47256
Stack overflow in LibXMP