
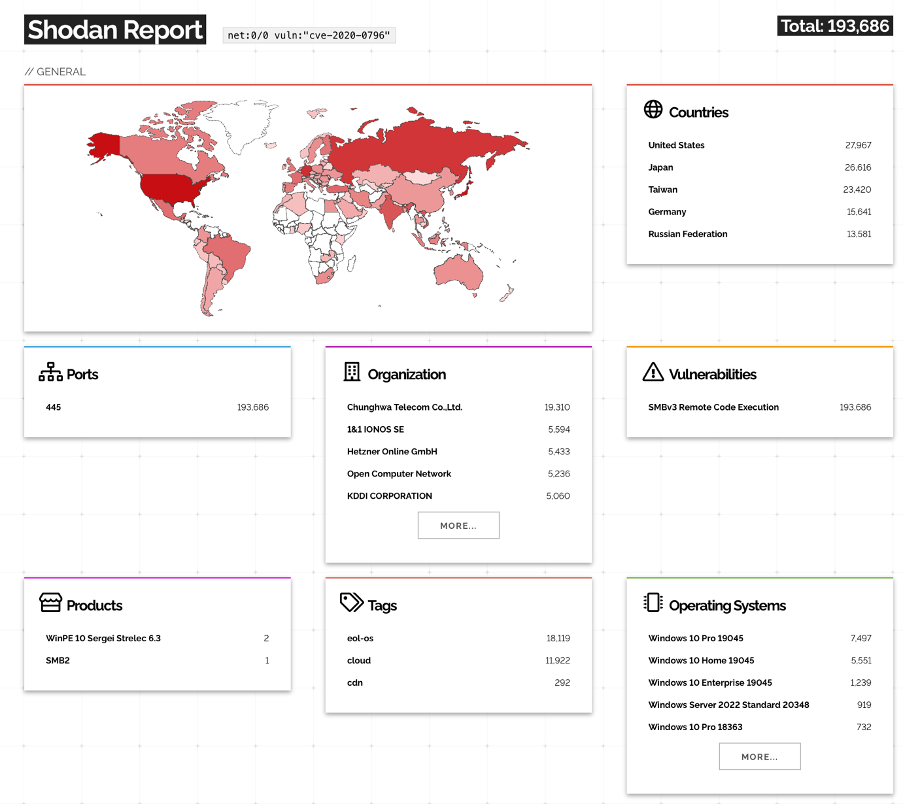
CVE-2020-0796
 maqeel-git/cve-2020-0796
Analysis and ethical exploitation guide for CVE-2020-0796 (SMBGhost) SMBv3 vulnerability with technical details and practical attack plan.
binary-exploitationeducationexploitation+2
maqeel-git/cve-2020-0796Analysis and ethical exploitation guide for CVE-2020-0796 (SMBGhost) SMBv3 vulnerability with technical details and practical attack plan.
 chattopadhyaykittu/cve-2017-0037
Technical analysis of CVE-2017-0037, a Microsoft browser memory corruption vulnerability enabling remote code execution via type confusion in CSS/JS…

 cptgibbon/cve-2021-3156
Root shell PoC for CVE-2021-3156
 fundacion-sadosky/vbox_cve_2017_10235
[CVE-2017-10235] Description and PoC of VirtualBox E1000 device Buffer Overflow
 tamirzb/cve-2019-14040
PoC code for CVE-2019-14040
 tamirzb/cve-2019-14041
PoC code for CVE-2019-14041
 thepwnrip/lehack-analysis-of-cve-2018-8453
Conference talk analyzing CVE-2018-8453, a Windows kernel UAF and double-free vulnerability. Covers binary diffing, exploit reproduction, heap spray,…
 c0d331ng/blackash-cve-2025-48593
CVE-2025-48593
 donghyunlee00/cve-2021-3156
Proof-of-concept exploit for CVE-2021-3156, a heap-based buffer overflow in sudo, providing root shell access without bruteforce. Tested on Ubuntu…
 arvindshima/cve-2021-3156
CVE-2021-3156: Heap-Based Buffer Overflow in Sudo (Baron Samedit)
 sachinthabs/spectre-vulnerability-cve-2017-5753-
Educational proof-of-concept demonstrating the Spectre (CVE-2017-5753) CPU vulnerability with a C-based exploit and detailed report on speculative…
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 0xblackash/cve-2026-80844
Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 wangqian06/cve-2021-3156
Root shell proof-of-concept exploit for CVE-2021-3156 (sudo Baron Samedit) heap-based buffer overflow, enabling local privilege escalation on…